
phpggc
 ambionics/phpggc
PHPGGC is a library of PHP unserialize() payloads along with a tool to generate them, from command line or programmatically.
exploitationexploit-frameworkspayload-generation+1
3.9k
ambionics/phpggcPHPGGC is a library of PHP unserialize() payloads along with a tool to generate them, from command line or programmatically.
 mbechler/marshalsec
Java deserialization vulnerability exploitation tool with payload generators for multiple marshallers (Jackson, XStream, SnakeYAML) and JNDI…
 ignitetechnologies/burpsuite-for-pentester
This cheatsheet is built for the Bug Bounty Hunters and penetration testers in order to help them hunt the vulnerabilities from P4 to P1 solely and…
 mrd0x/bitb
HTML/CSS/JS templates for Browser-In-The-Browser phishing attacks, embedding fake login windows with customizable titles, domains, and phishing links…
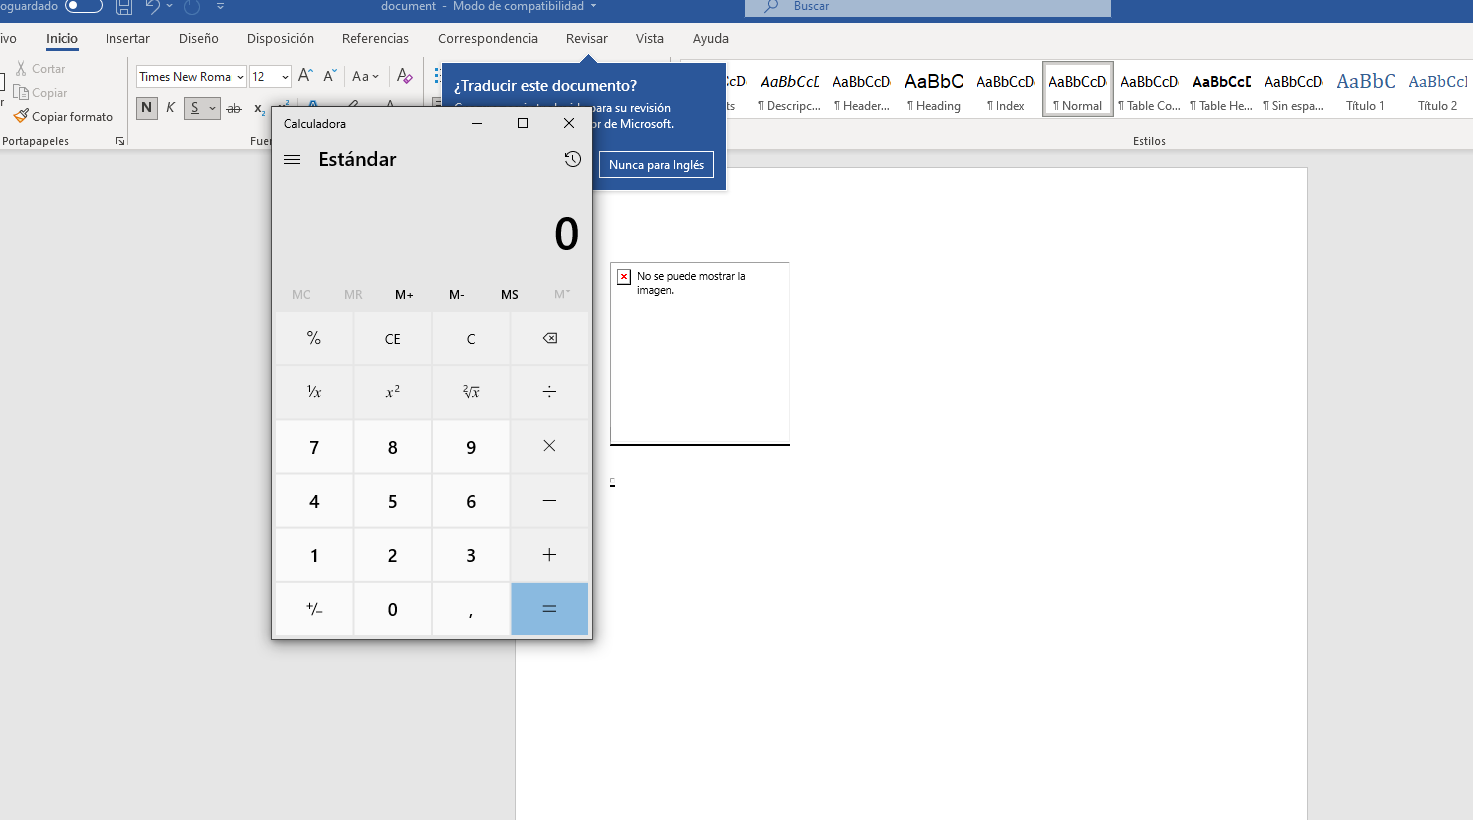 lockedbyte/cve-2021-40444
Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office RCE) with a hosted server for DLL payload delivery, based on…
 b374k/b374k
PHP Webshell with handy features
 portswigger/http-request-smuggler
Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…
 ssl/ezxss
Blind XSS detection and exploitation platform with persistent sessions, reverse proxy, and automated information gathering for penetration testers…
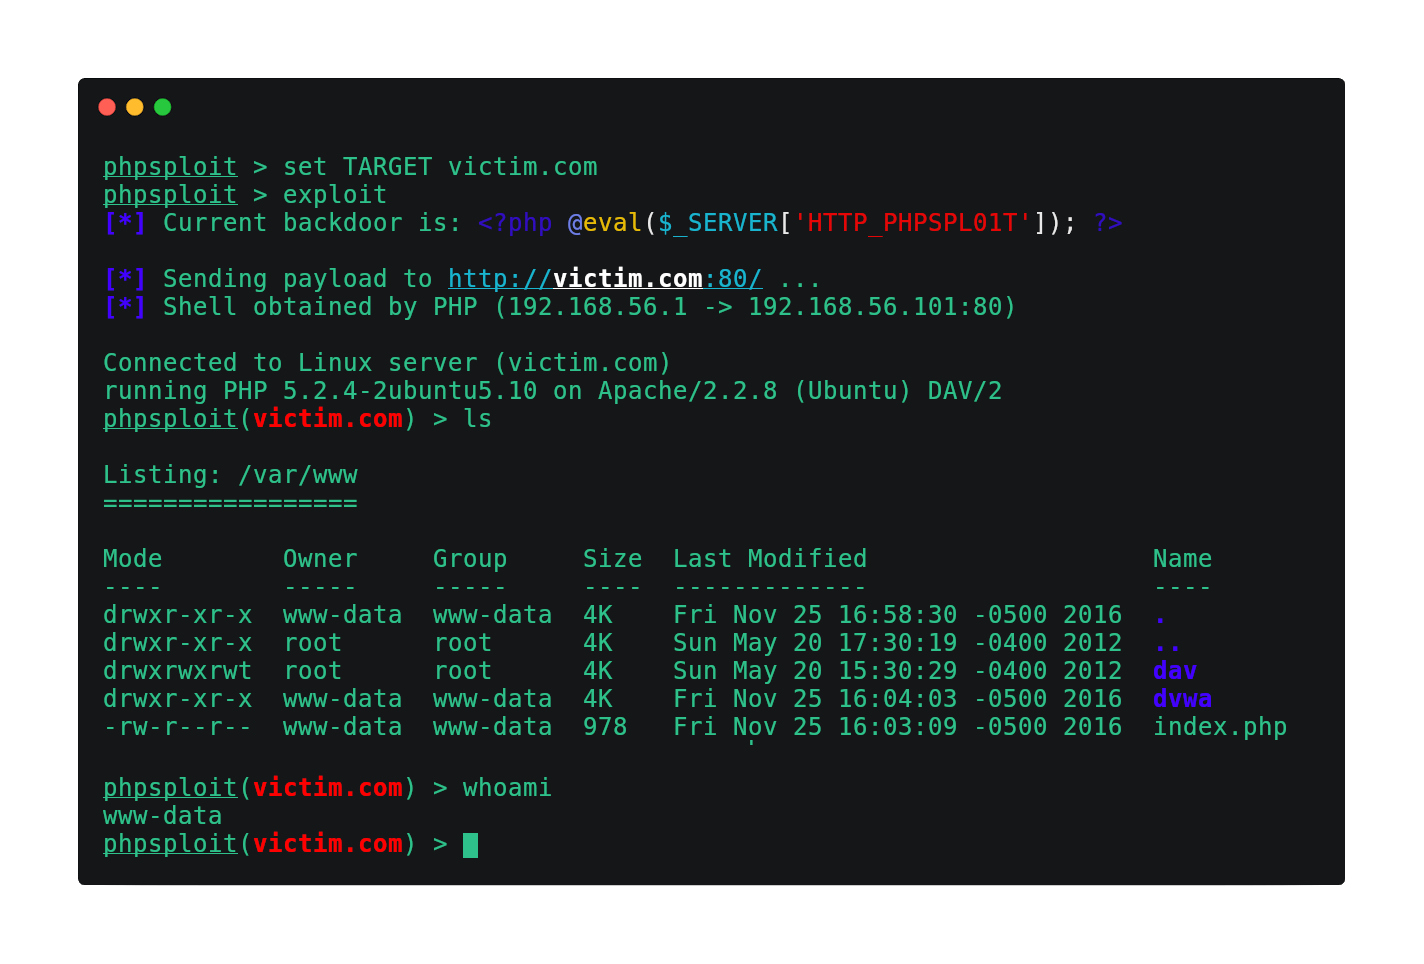 nil0x42/phpsploit
Full-featured C2 framework which silently persists on webserver with a single-line PHP backdoor
 ustayready/credsniper
CredSniper is a phishing framework written with the Python micro-framework Flask and Jinja2 templating which supports capturing 2FA tokens.
 danops-1/gpt-agreement-payment
ChatGPT Plus/Team/Pro 订阅协议端到端重放工具集 · hCaptcha 视觉求解器 · 反欺诈机制实证研究 / End-to-end protocol replay toolkit for ChatGPT Plus/Team/Pro subscription with…
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 albinowax/activescanplusplus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, expression language injection, shellshock and…
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 owasp/joomscan
Perl-based Joomla CMS vulnerability scanner automating version enumeration, component detection, exploit matching, firewall identification, and…
 jas502n/cve-2020-5902
Proof-of-concept exploit for CVE-2020-5902, a directory traversal and remote code execution vulnerability in F5 BIG-IP TMUI. Includes file read,…
 embedi/cve-2017-11882
Proof-of-concept exploit for CVE-2017-11882 with WebDav-based remote execution, generating malicious RTF documents to trigger command execution via…
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)