burpsuite-copy-as-xmlhttprequest

BurpSuite extension that converts HTTP requests into JavaScript XMLHttpRequest code for streamlined XSS proof-of-concept generation and web…

BurpSuite extension that converts HTTP requests into JavaScript XMLHttpRequest code for streamlined XSS proof-of-concept generation and web…

JavaScript beacons and C2 to be used for XSS payload or post exploitation implants on webapp servers or desktop software to monitor users and…

Chrome extension and Shodan scanner for detecting and demonstrating RCE vulnerabilities in React Server Components (RSC) and Next.js applications,…

Browser extension for tracking, inspecting, and exploiting cross-document postMessage vulnerabilities with replay and cross-origin exploit simulation…

Chrome extension that uses vulnerabilities CVE-2021-33044 and CVE-2021-33045 to log in to Dahua cameras without authentication.

A chromium extension exploitation toolkit

PoC for CVE-2026-48907 - Joomla! JCE extension < 2.9.99.5 unauthenticated RCE

Proof-of-concept for CVE-2021-26700: remote code execution in the VSCode npm-script extension via malicious workspace settings.json, with detailed…

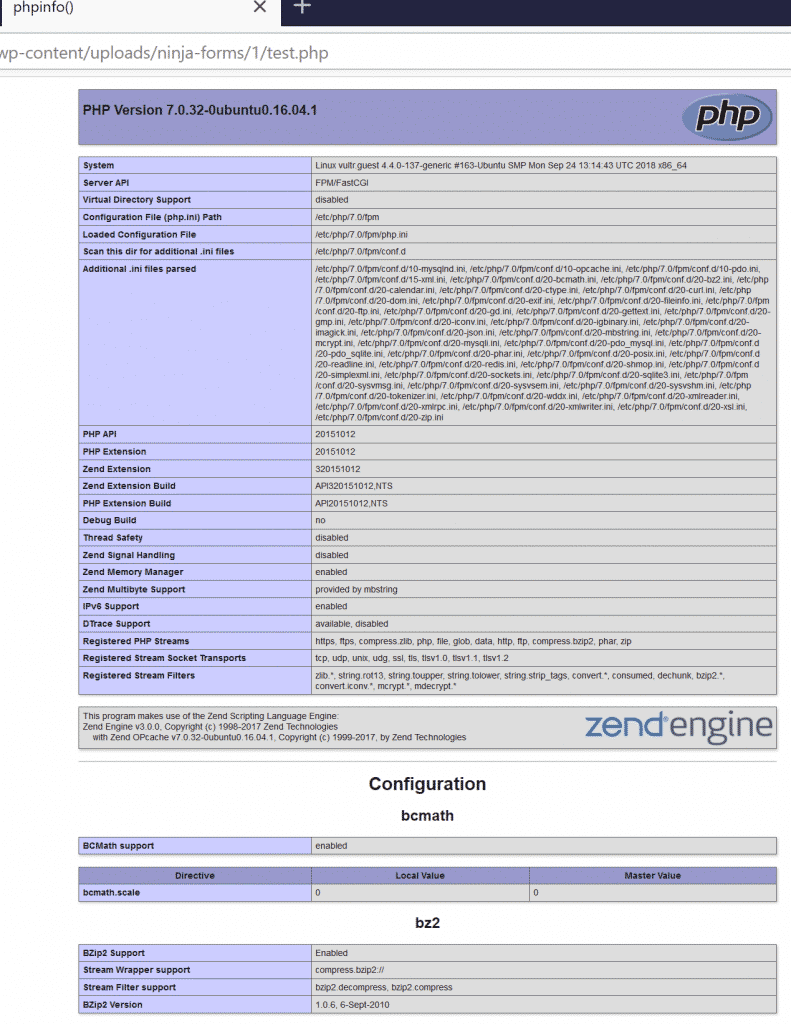
(Wordpress) Ninja Forms File Uploads Extension <= 3.0.22 – Unauthenticated Arbitrary File Upload

CVE-2025-55182 security test kit: CLI scanner + Chrome extension + Nuclei templates + Docker lab.

Proof-of-concept exploit for CVE-2024-6778, a Chromium sandbox escape via a malicious browser extension, achieving code execution on privileged WebUI…

SQL Injection POC for CVE-2024-21514: Divido payment extension for OpenCart

Proof-of-concept exploit for CVE-2024-44902, a deserialization vulnerability in ThinkPHP v6.1.3–v8.0.4 enabling remote code execution via crafted…

Python Interactive Exploit for WP File Manager Vulnerability. The File Manager (wp-file-manager) plugin before 6.9 for WordPress allows remote…

Pre-auth arbitrary file upload RCE exploit for iCagenda Joomla extension < 4.0.8 (CVSS 10.0)

CVE-2025-55182-Exploiter Google Chrome Extension. nextjs vulnerability #nextjscve

CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…

The Joomla extension PhocaCommander is vulnerable to Path Traversal in delete, copy, move actions - CVSS 6.4