CVE-2026-24516-DigitalOcean-RCE.

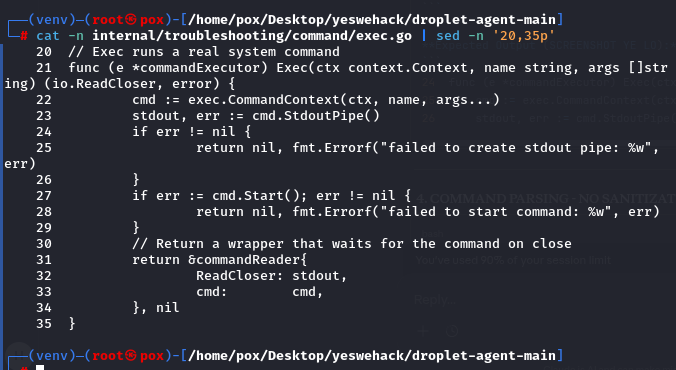
Technical analysis and PoC for CVE-2026-24516: Unauthenticated Root Remote Code Execution in DigitalOcean Droplet Agent (CVSS 10.0).

Technical analysis and PoC for CVE-2026-24516: Unauthenticated Root Remote Code Execution in DigitalOcean Droplet Agent (CVSS 10.0).

ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.

Model Context Protocol server for Firefox DevTools - enables AI assistants to inspect and control Firefox browser through WebDriver BiDi

Proof-of-concept exploit for CVE-2021-38647 (OMIGOD), an unauthenticated remote code execution vulnerability in the OMI agent commonly deployed on…

Mass checks VMware vCenter servers for CVE-2021-22005 RCE by sending telemetry API POST requests and flagging HTTP 201 responses as vulnerable.

Python-based exploit script for Oracle WebLogic CVE-2020-14882 unauthorized bypass RCE. Tests authentication bypass and remote code execution via…

Proof-of-concept for CVE-2026-75898, an SSRF in RAGFlow's Invoke component. Demonstrates the vulnerability with unmodified source, includes E2E…

Proof-of-concept demonstrating a command injection vulnerability in MS-Agent Shell tool, enabling arbitrary command execution and reverse shell via…

Enrolled agent can smuggle arbitrary OpenSearch _bulk operations via DataValue.index. GHSA-ff9g-85jq-r3g3. Draft

Proof-of-concept exploit for SQL injection and authentication bypass in Lodging Reservation Management System 1.0, enabling unauthorized admin access…

Exploit for CVE-2024-43044 enabling arbitrary file read from Jenkins controller to extract and decrypt credentials.xml using secret keys.

PoC for CVE-2020-6207 (Missing Authentication Check in SAP Solution Manager)

🛠 Demonstrate remote code execution in Windows Notepad via markdown links exploiting unsecured URL protocols.

Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.

a unique framework for cybersecurity simulation and red teaming operations, windows auditing for newer vulnerabilities, misconfigurations and…

adaptive agents for dynamic web penetration testing

Agent RCE PoC for CVE-2024-28741, a stored XSS vulnerability in NorthStar C2.

PhantomRecon is a CLI-based, modular, agent-driven red team automation tool designed to demonstrate autonomous offensive security workflows powered…