
rapidscan
 skavngr/rapidscan
:new: The Multi-Tool Web Vulnerability Scanner.
dns-analysisinformation-gatheringpenetration-testing+5
skavngr/rapidscan:new: The Multi-Tool Web Vulnerability Scanner.
 0xinfection/tidos-framework
The Offensive Manual Web Application Penetration Testing Framework.
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF

 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
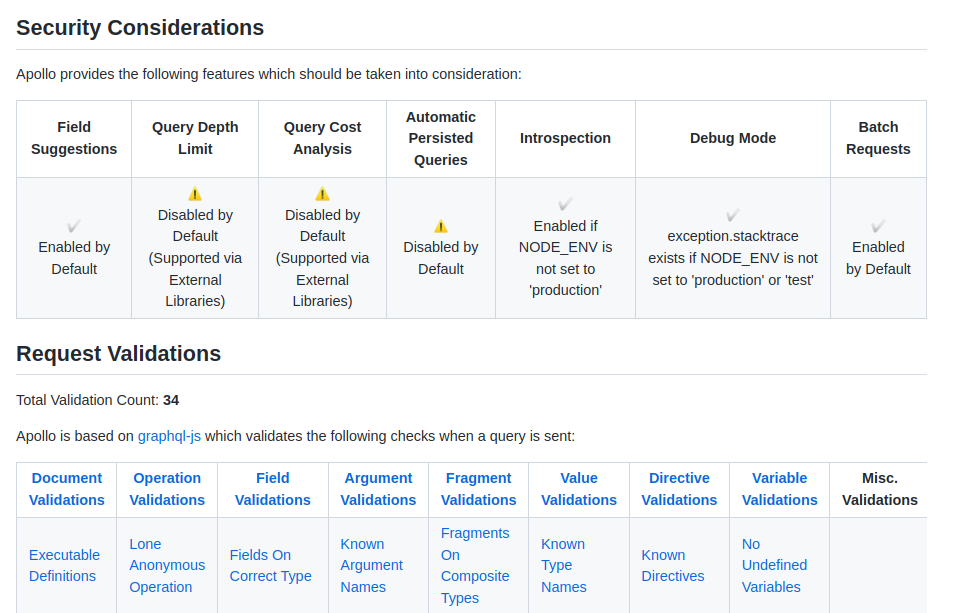 dolevf/graphw00f
GraphQL server engine fingerprinting tool that sends benign and malformed queries to identify backend technology and assess security defenses via the…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 kostas-pa/lfitester
Python3 tool that detects and exploits Local File Inclusion vulnerabilities, with crawling, path traversal and filter bypass payloads, and automated…
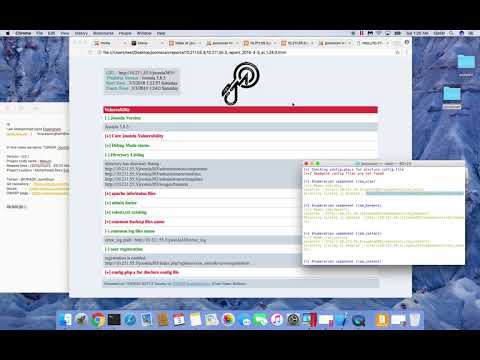 owasp/joomscan
Perl-based Joomla CMS vulnerability scanner automating version enumeration, component detection, exploit matching, firewall identification, and…
 mandatoryprogrammer/sonar.js
A framework for identifying and launching exploits against internal network hosts. Works via WebRTC IP enumeration combined with WebSockets and…
 immunit/drupwn
Drupal enumeration & exploitation tool
 h4x0r-dz/cve-2021-26855
PoC exploit for CVE-2021-26855 (Exchange Server SSRF) with user enumeration, mail header reading, and vulnerability detection. Supports…
 ggolawski/cve-2020-1958
Proof-of-concept exploit for CVE-2020-1958, an LDAP injection vulnerability in Apache Druid 0.17.0, enabling user enumeration and LDAP attribute…
 artemy-ccrsky/cve-2024-39211
User Enumeration vulnerability in Kaiten (workflow management system)
 yairhinkis/cve-2026-56096
Proof of concept and technical write-up for CVE-2026-56096, a blind Solr query injection in TYPO3 EXT:solr enabling unauthenticated field enumeration…
 h4zaz/cve-2026-8794
Username Enumeration via Authentication Timing Side-Channel in PaperCut NG
 elizeuopain/exploit-cve-2024-9513-netadmin-iam-allows-user-enumeration-in-active-directory
Proof-of-concept exploit for CVE-2024-9513 targeting user enumeration in NetAdmin IAM via HTTP POST request to…
 fernandobortotti/cve-2019-9053
Python 3 implementation of a time-based blind SQL injection exploit targeting CVE-2019-9053 in CMS Made Simple 2.2.8, with wordlist-based enumeration.