
Vulnerable-Web-Application
 owasp/vulnerable-web-application
OWASP Vulnerable Web Application Project https://github.com/hummingbirdscyber
educationpenetration-testingweb-application-exploitation
owasp/vulnerable-web-applicationOWASP Vulnerable Web Application Project https://github.com/hummingbirdscyber
 h43z/dns-rebinding-tool
dns rebind tool with custom scripts
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
 eyodav/cve-2025-34159
A critical Remote Code Execution (RCE) vulnerability exists in Coolify's application deployment workflow. This flaw allows a low-privileged member to…
 teycir/burpapisecuritysuite
Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…
 rgkue/mysqli
Time-Based Blind SQL Injection tool for MySQL - CVE-2019-9053
 1h3ll/cve-2025-50364_csrf_add_category-phpgurukul-cve
Proof-of-concept CSRF exploit targeting CVE-2025-50364 in PHPGurukul Maid Hiring Management System v1.0 that adds arbitrary admin categories via a…
 octoberfest7/xll_phishing
XLL Phishing Tradecraft
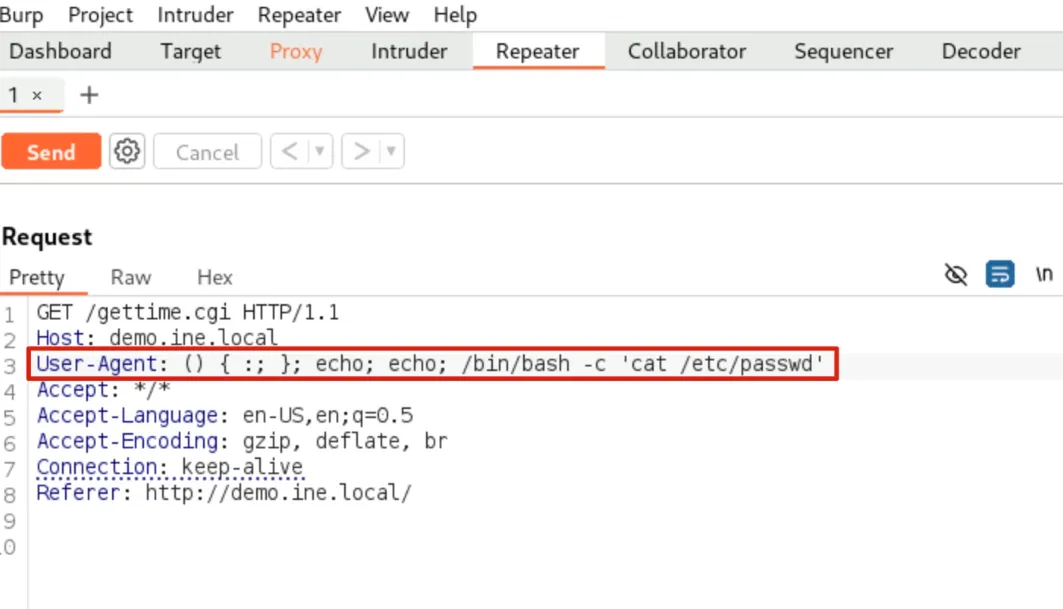 mtaha-sec/bash-apocalypse
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
 dream434/cve-2021-42013-apache
On October 4, 2021, Apache HTTP Server Project released Security advisory on a Path traversal and File disclosure vulnerability in Apache HTTP Server…
 kkc73/weblogic-cve-2020-14882
This is a repository that aims to provide research material on CVE-2020-14882 as part of a project in partial fullfilment of ACS EDU Program.
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
 corvralabs/evilneko
Automated container orchestration tool for Browser-in-the-Browser (BITB) phishing attacks, enabling red teams to scale multi-target infrastructure…
 toperaproject/topera
IPv6 analysis tool: the other side
 geniuszly/cve-2022-46080
it is script that enables Telnet on routers by sending a specially crafted request. The script allows users to specify the router's URL, Telnet port,…
 gagaltotal/cve-2026-10523-ivanti-sentry
Proof-of-concept detection tool for Ivanti Sentry authentication bypass and remote code execution vulnerabilities (CVE-2026-10520, CVE-2026-10523).…
 dhesitheking/localnet_attacker
This is a project about attacking and gathering information of the windows machines which is connected in the same network by using java programs