
CyberhawksLab-telnetCVE
 skyejacobson/cyberhawkslab-telnetcve
Writeup/finding of CVE-2026-24061 within the Cyberhawks lab
educationexploitationpenetration-testing+4
1
skyejacobson/cyberhawkslab-telnetcveWriteup/finding of CVE-2026-24061 within the Cyberhawks lab
 mbadanoiu/cve-2021-46366
CVE-2021-46366: Credential Bruteforce Attack via CSRF + Open Redirect in Magnolia CMS
 tankirat/cve-2017-5638
Educational analysis of Apache Struts 2 RCE vulnerability CVE-2017-5638, including exploit details, Equifax case study, and prevention measures.
 win3zz/cve-2023-25157
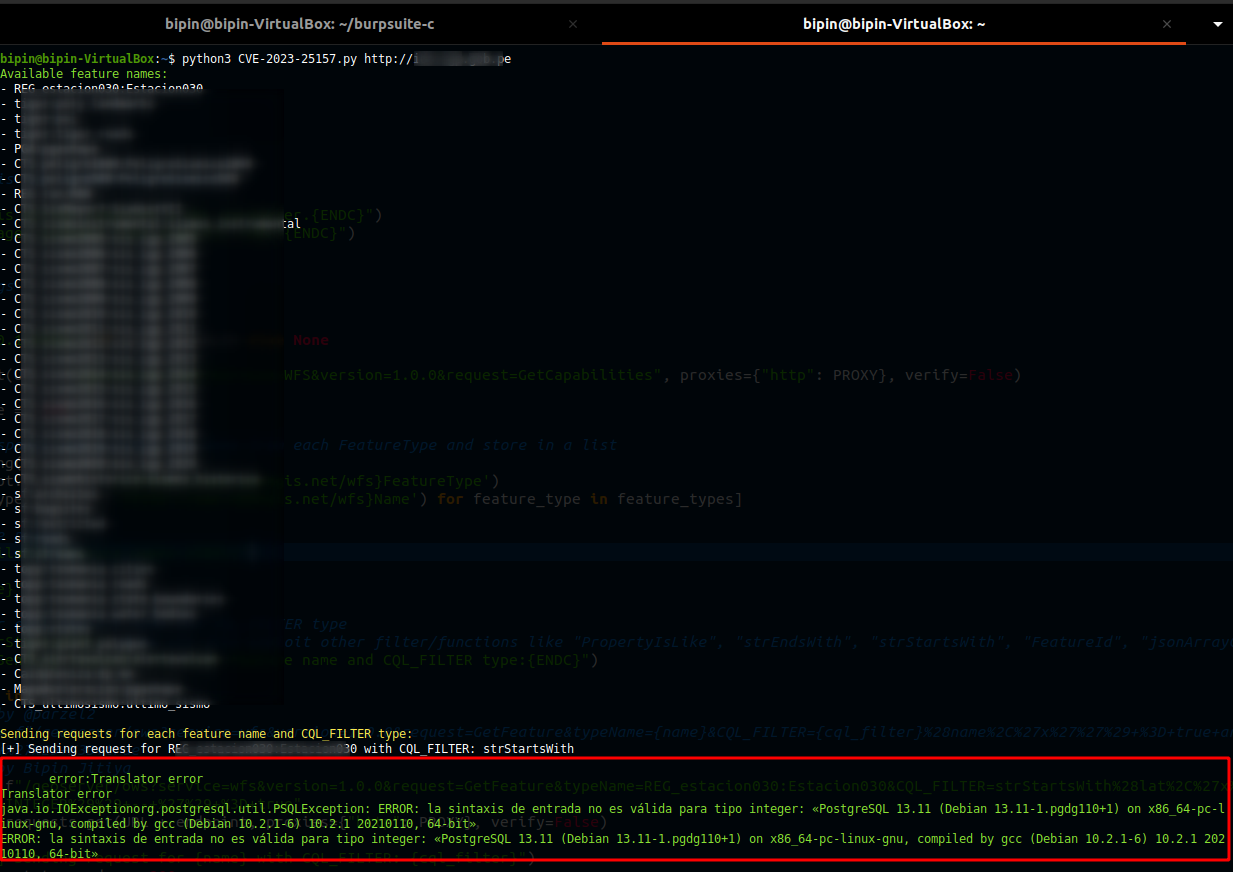
CVE-2023-25157 - GeoServer SQL Injection - PoC
 screetsec/dracos
Dracos Linux ( www.dracos-linux.org ) is the Linux operating system from Indonesian
 hawsec/ginger
A security assessment tool for Hitachi Vantara's Pentaho Business Analytics platform.
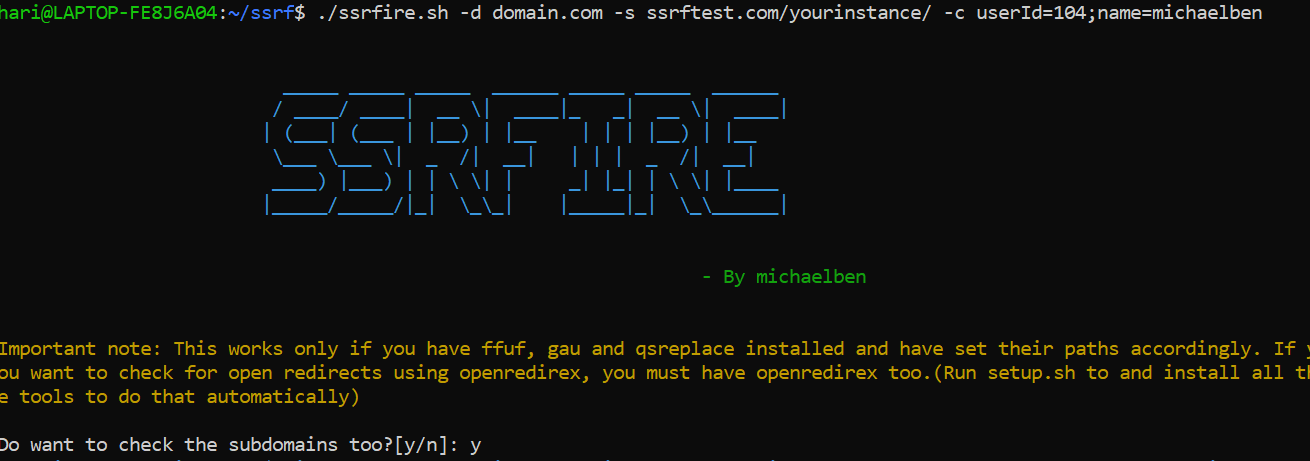 ksharinarayanan/ssrfire
An automated SSRF finder. Just give the domain name and your server and chill! ;) Also has options to find XSS and open redirects
 cappricio-securities/cve-2023-24044
Plesk Obsidian <=18.0.49 - Open Redirect
 dirac231/cve-2024-40498
Blind SQL Injection to RCE in a PHP open source application
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 signorrayan/redteam_toolkit
Red Team Toolkit is an Open-Source Django Offensive Web-App which is keeping the useful offensive tools used in the red-teaming together.
 matank001/moxy
Moxy is an open-source DAST tool designed for modern web application security testing. It provides an easy-to-use interface with agentic capabilities…
 spider12223/penscope
Passive recon & attack surface mapper — zero requests sent
 649/pingpon-exploit
Exploit for Mass Remote Code Execution on GPON home routers (CVE-2018-10562) obtained from Shodan.
 abraxas/forgejo-restore-file-open
Forgejo 16.0.5 - High - Remote - File read - restore-repo follows dump-side file:// into attachments
 gh-ost00/cve-2024-24809-proof-of-concept
Critical Flaws in Traccar GPS System Expose Users to Remote Attacks