
 mcipekci/wp2shell
Pre-auth RCE PoC for WordPress core — chains CVE-2026-63030 (REST /batch/v1 route-confusion desync) with CVE-2026-60137 (author__not_in SQLi) into an…
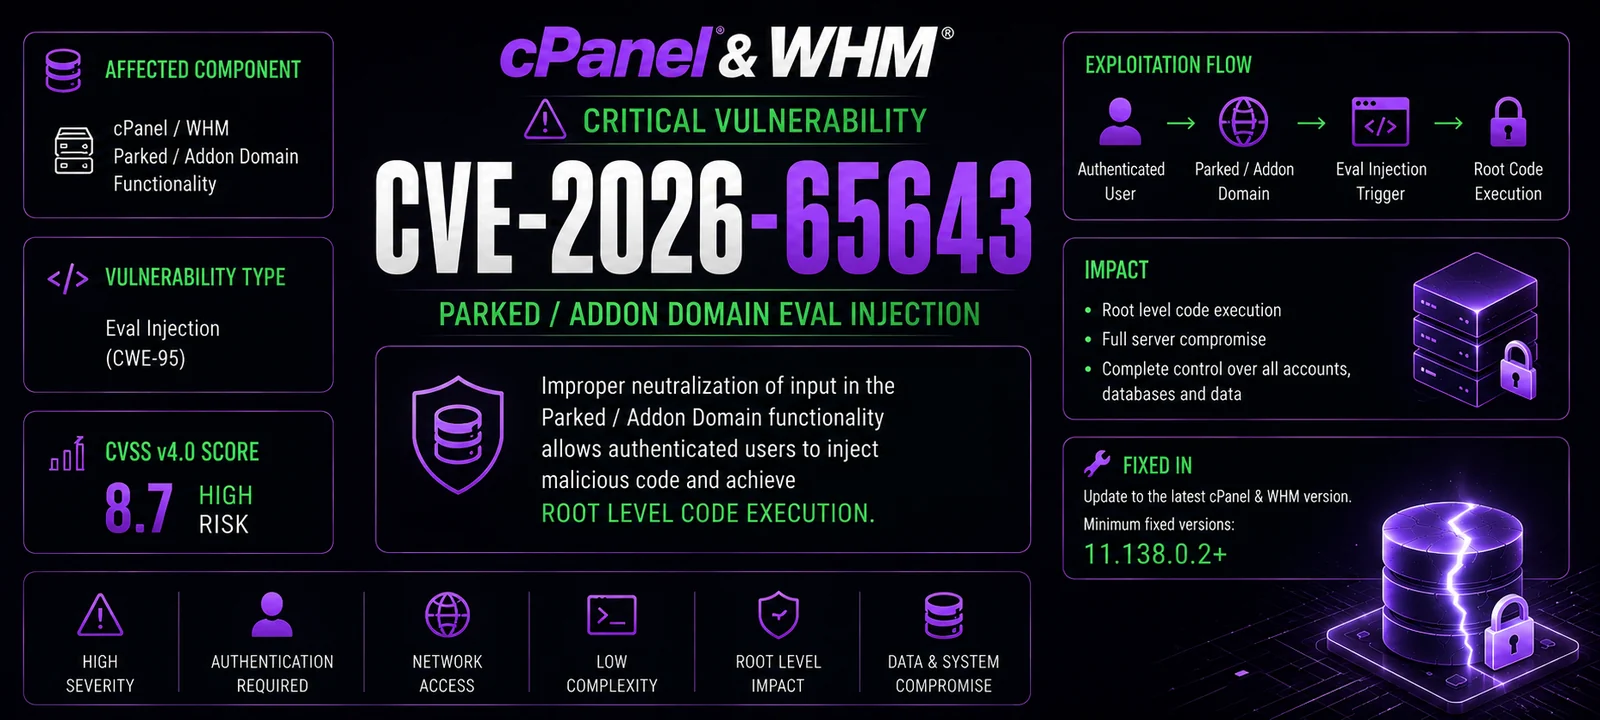 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 rbowes-r7/refreshing-soap-exploit
A PoC exploit for CVE-2022-41622 - a CSRF in F5 BIG-IP control plane that leads to remote root
 v1k1ngfr/exploits-rconfig
Exploit codes for rconfig <= 3.9.4
 ivanitlearning/cve-2017-17562
Standalone Python 3 exploit for CVE-2017-17562 targeting GoAhead web server 2.5–3.6.5 with automated CGI endpoint discovery and reverse shell payload…
 momika233/cve-2024-3400
Proof-of-concept exploit for CVE-2024-3400, demonstrating command injection in Palo Alto PAN-OS with a Python-based backdoor, persistence via…
 c411e/cve-2024-53691
CVE-2024-53691
 geffner/cve-2020-8289
Proof-of-concept exploit for CVE-2020-8289 demonstrating remote code execution as SYSTEM/root via Backblaze backup client's SSL verification bypass…
 itzsh4dowxz/cve-2024-37032-poc
CVE-2024-37032 (Probllama) PoC for Ollama ≤0.1.33: path traversal and arbitrary file write via model digest handling, leading to automated privilege…
 deadexpl0it/cve-2026-78006-poc
POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution
 richard-tang/sscms-pluginshell
CVE-2022-28118
 mbadanoiu/cve-2023-34468
CVE-2023-34468: Remote Code Execution via DB Components in Apache NiFi
 secforce/wptimecapsulepoc
An authentication bypass was recently discovered (https://www.webarxsecurity.com/vulnerability-infinitewp-client-wp-time-capsule/) on WP Time Capsule…
 ianxtianxt/bypass_disablefunc_via_ld_preload
解决php提权的时候因系统禁用函数导致无法执行命令的情况
 r2qa/cve-2026-17544
Exploit for CVE-2026-17544: PHP bcmath OOB write converted into memory-only RCE, bypassing disable_functions and open_basedir with a runtime…
 katransefa/cve-2026-13714
Unauthenticated RCE exploit for Realtyna WPL < 5.3.0 that uploads a PHP webshell via hardcoded API key and executes arbitrary system commands.
 bridgeralderson/cve-2025-81110-poc
Improper Symbolic link handling in the PutContents API in Gogs allows Local Execution of Code.