
CVE-2023-7028
 randomrobbiebf/cve-2023-7028
CVE-2023-7028
authentication-authorizationexploitationpenetration-testing+3
582 years ago
randomrobbiebf/cve-2023-7028CVE-2023-7028
 emerinohdz/facebrute
Facebook brute forcer script
 0z09e/cve-2020-35846
Cockpit CMS 0.11.1 NoSQL Injection to Remote Code Execution
 s3bap3/pmp-exploit
Password Manager Pro Exploit
 redteampentesting/cve-2023-33243
PoC for login with password hash in STARFACE
 groshi215/cve-2024-48887-exploit
Unverified Password Change (CWE-620)
 fimtow/cve-2021-24750
Demonstration of the WP Visitor Statistics plugin exploit
 7megaumka7/foskiller
FOSSBilling CVE-2026-53647 & CVE-2026-53646 PoC — Unauthenticated API key disclosure & password reset token reuse
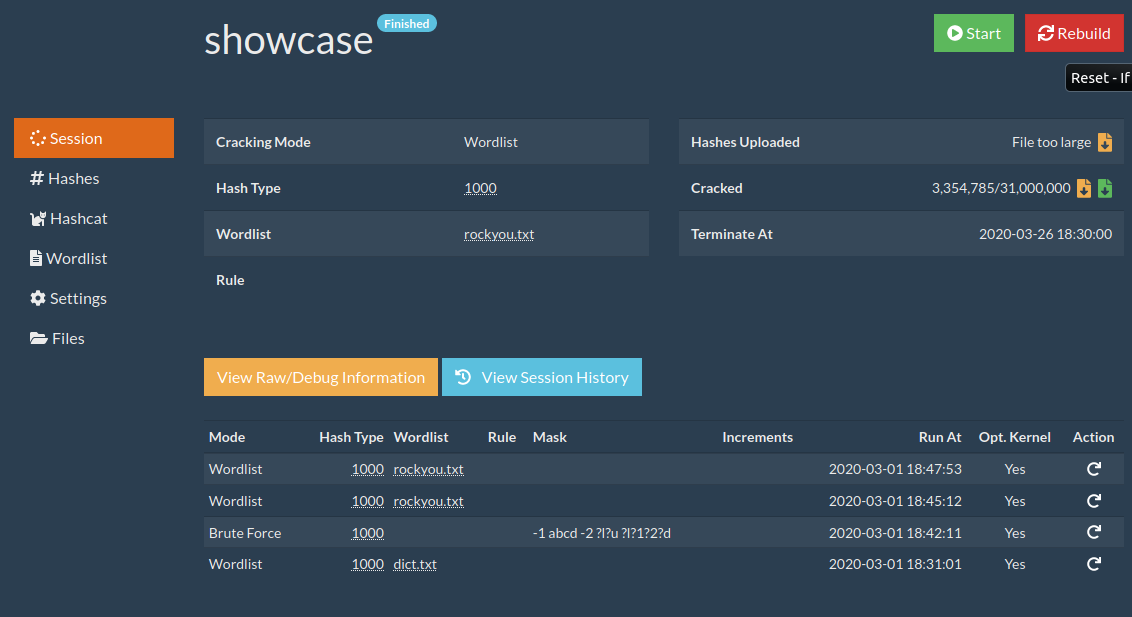 ctxis/crackerjack
CrackerJack / Hashcat Web Interface / Context Information Security
 jbaines-r7/hook
Proof of Concept for WatchGuard Authenticated Arbitrary File Read (CVE-2022-31749)
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
 mahamedm/cve-2019-9053-exploit-python-3
The exploit is edited to work with different text encodings and Python 3 and is compatible with CMSMS version 2.2.9 and below.
 zhairiazzeddine/exploit-cve-2023-6063-poc-vuln
Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…
 elizeuopain/cve-2019-9053-cms-made-simple-2.2.10---sql-injection-exploit
Python exploit for CVE-2019-9053 SQL injection in CMS Made Simple 2.2.10 with password hash cracking and user enumeration capabilities.
 dh4nuj4/simplectf-updatedexploit
This script is a modified version of the original exploit by Daniele Scanu which exploits an unauthenticated SQL injection vulnerability in CMS Made…
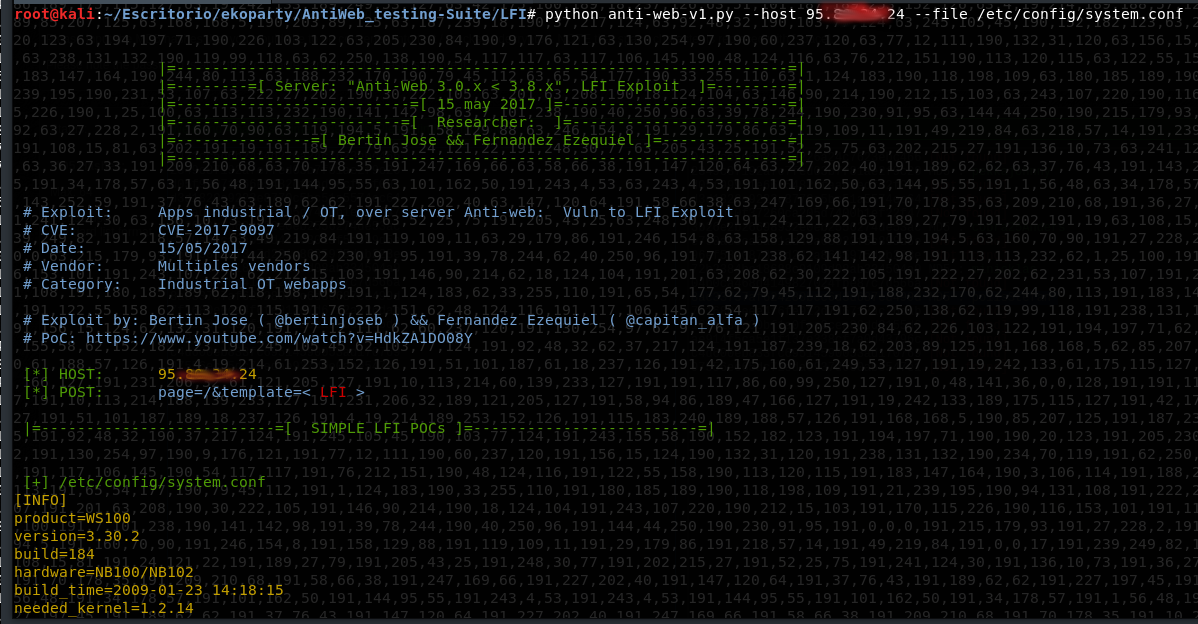 mdudek-ics/antiweb_testing-suite
Suite de herramientas que sacan partido del CVE-2017-9097 (+RCE)
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…