

CVE-2021-45232
 dskho/cve-2021-45232
Proof-of-concept scanner for CVE-2021-45232, targeting unauthenticated API access and default credentials in Apache APISIX Dashboard.
api-securityexploitationmisconfiguration+2
dskho/cve-2021-45232Proof-of-concept scanner for CVE-2021-45232, targeting unauthenticated API access and default credentials in Apache APISIX Dashboard.
 abrewer251/cve-2024-38475_sonicboom_apache_url_traversal_poc
Proof-of-concept scanner for CVE-2024-38475 (SonicBoom) Apache URL traversal. Automates TLS negotiation, directory scanning, traversal verification,…
 mostafaanouarghorab/microservicecve-2021-39156
 imthecopilotnow/cve-2025-492030
Proof-of-concept for CVE-2025-492030: account takeover via session token validation bypass in SecureVPN API endpoint /api/v1/authenticate.
 cyberharsh/mini_httpd-cve-2018-18778
PoC exploit for CVE-2018-18778: arbitrary file read in mini_httpd 1.29 via empty Host header, affecting IoT devices from Huawei, Zyxel, and others.
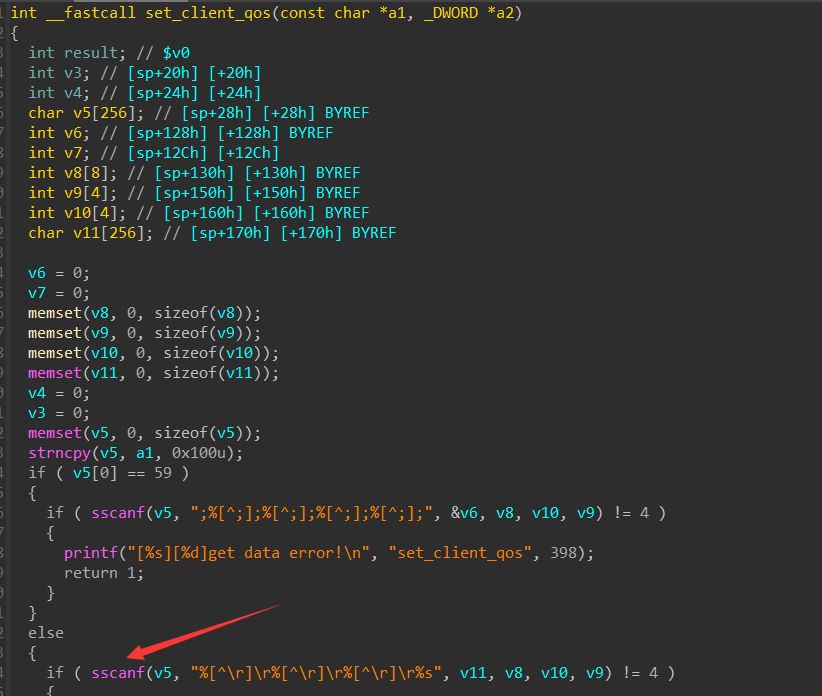 zt20xx/cve-2023-48194
Proof-of-concept exploit for a buffer overflow vulnerability in Tenda AC8v4 router firmware (V16.03.34.09) via the SetNetControlList endpoint,…
 hupe1980/cve-2021-3129
Laravel debug mode - Remote Code Execution (RCE)
 wing-song/cve-2021-37580
Apache ShenYu 管理员认证绕过
 tibrn/cve-2025-30144
Proof-of-concept for CVE-2025-30144: JWT issuer validation bypass in fast-jwt library allowing attackers to forge tokens with array-based iss claims.
 vanlam2001/netis-n5vn-ac1200-dos
Proof-of-concept exploit for a buffer overflow vulnerability (CVE-2024-44596) in Netis N5VN AC1200 routers, causing a denial of service by crashing…
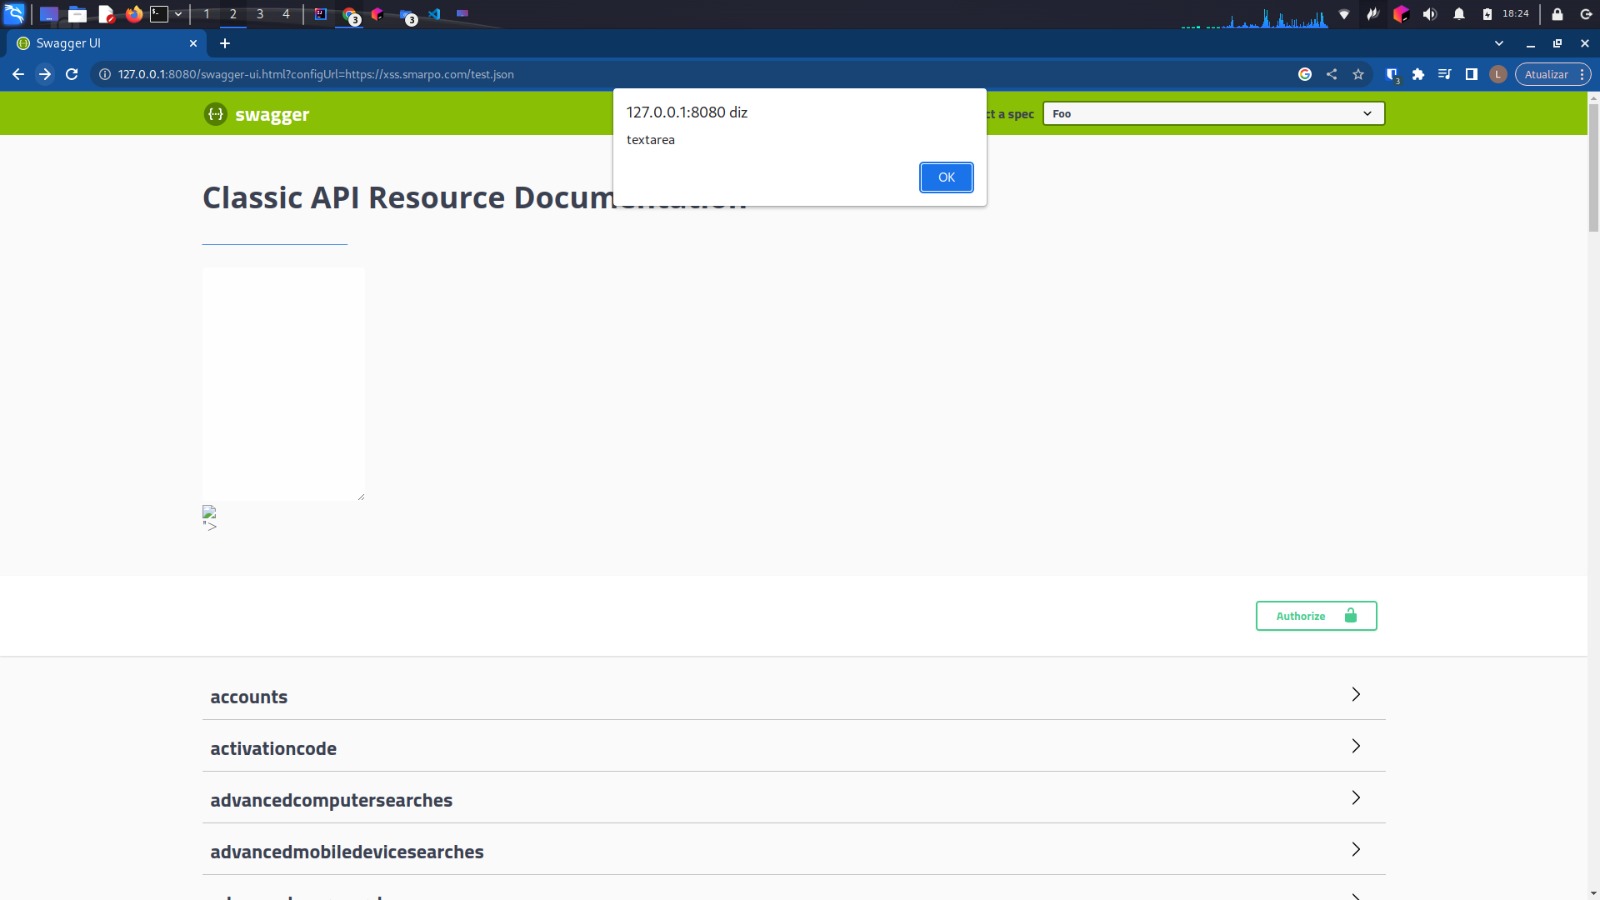 lucasrenaa/cve-2018-25031
Python-based proof-of-concept script demonstrating CVE-2018-25031 XSS vulnerability in Swagger UI using Selenium for automated detection across…
 ubuntustrike/cve-2017-9805-apache-struts-fuzz-n-sploit
A script to Fuzz and and exploit Apache struts CVE-2017-9805
 cainiao159357/cve-2025-51495
Proof-of-concept exploit for CVE-2025-51495, an integer overflow in Mongoose WebSocket's mg_ws_cb function leading to out-of-bounds memory access and…
 hantwister/fakedellom
A fake host that can be "managed" by Dell OMSA, getting you past the login screen.
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 anonmoty/xxstrike
XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.
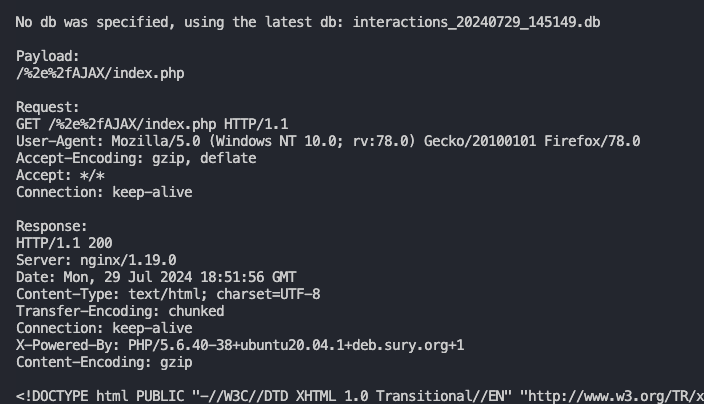 intrudir/bypassfuzzer
Fuzz 401/403/404 pages for bypasses
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…