
CVE-2026-30945-PoC
 filipegaudard/cve-2026-30945-poc
Proof-of-concept exploit for CVE-2026-30945, an IDOR in StudioCMS allowing arbitrary API token revocation and denial of service. Includes manual and…
api-securityeducationexploitation+3
filipegaudard/cve-2026-30945-pocProof-of-concept exploit for CVE-2026-30945, an IDOR in StudioCMS allowing arbitrary API token revocation and denial of service. Includes manual and…
 randomrobbiebf/cve-2025-67923
JetEngine <= 3.7.7 — Unauthenticated Stored Cross-Site Scripting via CCT REST API
 0xmid00/cve-2022-46364-poc
CVE-2022-46364 Apache CXF XOP:Include SSRF / LFI
 faccimatteo/cve-2022-4361
Proof-of-concept exploit for CVE-2022-4361, a reflected XSS vulnerability in Keycloak's OIDC authentication flow, with Docker-based test environment…
 mohitsinghpapola/cve-2023-20052
Fixed Docker build for CVE-2023-20052 ClamAV XXE exploit. Resolves OpenSSL 3.0 compilation errors using Ubuntu 18.04 with OpenSSL 1.0 for…
 kylvgoi/cve-2019-1663
Educational exploit for CVE-2019-1663 targeting a stack-based buffer overflow in Cisco RV routers. Includes a Python exploit script, reverse shell…
 ltidi2000/cve-2021-45232
Proof-of-concept exploit for CVE-2021-45232, an unauthorized access vulnerability in Apache APISIX Dashboard allowing export/import of admin…
 5qu1n7/cve-2025-55817
ChilliCream Nitro GraphQL version 28.0.13 is vulnerable to multiple Stored Cross Site Scripting (XSS) Vulnerabilities
 ubuntustrike/struts_rest_rce_fuzz-cve-2017-9805-
Simple python script to fuzz site for CVE-2017-9805
 shoucheng3/vert-x3__vertx-web_cve-2018-12542_3-5-3-cr1
Exploit for CVE-2018-12542 in Vert.x-Web, a Java web framework. Demonstrates a path traversal vulnerability allowing unauthorized access to static…
 novem13th/cve-2026-23745-via-graphql-demo
Proof-of-concept exploit for CVE-2026-23745 targeting GraphQL endpoints, demonstrating the vulnerability and potential impact for security testing…
 shoucheng3/apache__dubbo_cve-2021-30180_2-7-9
Exploit for CVE-2021-30180 targeting Apache Dubbo RPC framework, enabling remote code execution via crafted RPC requests in vulnerable versions.
 s3mpr1linux/cve-2011-0762
Um script automatizado melhorando o exploit do cve-2011-0762 postado no exploit-db
 shoucheng3/x-stream__xstream_cve-2021-21345_1-4-15
Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.
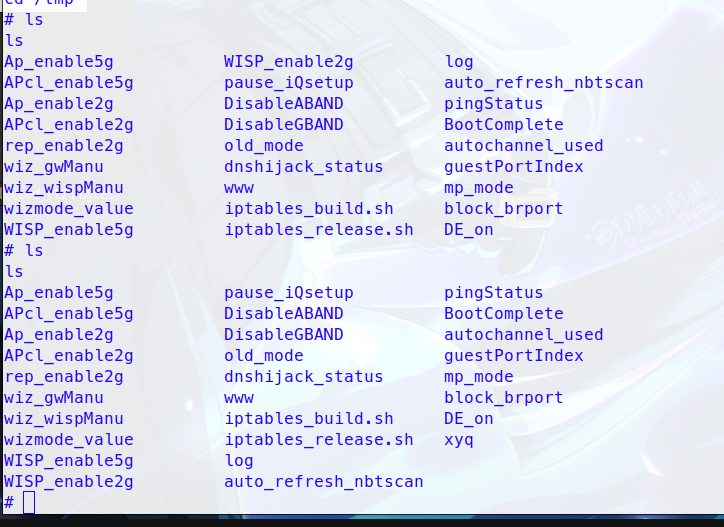 passwa11/re11s_1.11-formaccept-commandinjection
CVE-2025-22912
 freefv/cve-2020-6308-mass-exploiter
Mass exploiter for CVE-2020-6308 with multi-worker support, enabling automated exploitation of vulnerable SAP NetWeaver systems.
 0xsu3ks/cve-2025-29557
Documents a high-severity ExaGrid EX10 MailConfiguration API access control flaw that leaks plaintext SMTP credentials to authenticated operators,…