
CVE-2026-33439-PoC
 ibonok/cve-2026-33439-poc
Exploit for OpenAM pre-auth RCE (CVE-2026-33439) using a Java deserialization gadget chain to execute commands and return output directly in the HTTP…
exploitationpayload-developmentpenetration-testing+3
ibonok/cve-2026-33439-pocExploit for OpenAM pre-auth RCE (CVE-2026-33439) using a Java deserialization gadget chain to execute commands and return output directly in the HTTP…
 ianxtianxt/apache-flink-dashboard-rec
Apache Flink Dashboard未授权访问-远程代码命令执行
 secforce/cve-2008-5416
Microsoft SQL Server sp_replwritetovarbin Memory Corruption via SQL Injection
 kevin-mizu/werkzeug-cve-2022-29361-poc
Proof-of-concept exploit for CVE-2022-29361, demonstrating remote code execution via Werkzeug debugger console in Python web applications.
 sh0ckfr/cve-2024-4577
Fixed and minimalist PoC of the CVE-2024-4577
 devzspy/cve-2019-7214
Collection of PoCs created for SmarterMail < Build 6985 RCE
 ctlyz123/cve-2020-8193
Proof-of-concept exploit for CVE-2020-8193, a pre-authentication remote code execution vulnerability in Citrix ADC/NetScaler. Enables security…
 0xc4t/cve-2022-29455
Proof-of-concept exploit for CVE-2022-29455, a cross-site scripting vulnerability in the Elementor WordPress plugin (<=3.5.5) via crafted lightbox…
 motoyasu-saburi/cve-2019-12086-jackson-databind-file-read
Proof-of-concept exploit for CVE-2019-12086: Jackson databind deserialization vulnerability enabling arbitrary file read via rogue MySQL server when…
 mesh3l911/cve-2021-31760
Exploiting a Cross-site request forgery (CSRF) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 abraxas/pfsense-igmp-type
pfSense CE 2.9.0-DEVELOPMENT - Medium - Remote - Config injection - IGMP type newline
 isee857/cleo-cve-2024-50623-poc
Cleo 远程代码执行漏洞批量检测脚本(CVE-2024-50623)
 houmanpashaei/cve-2025-29927
This is a CVE-2025-29927 Scanner.
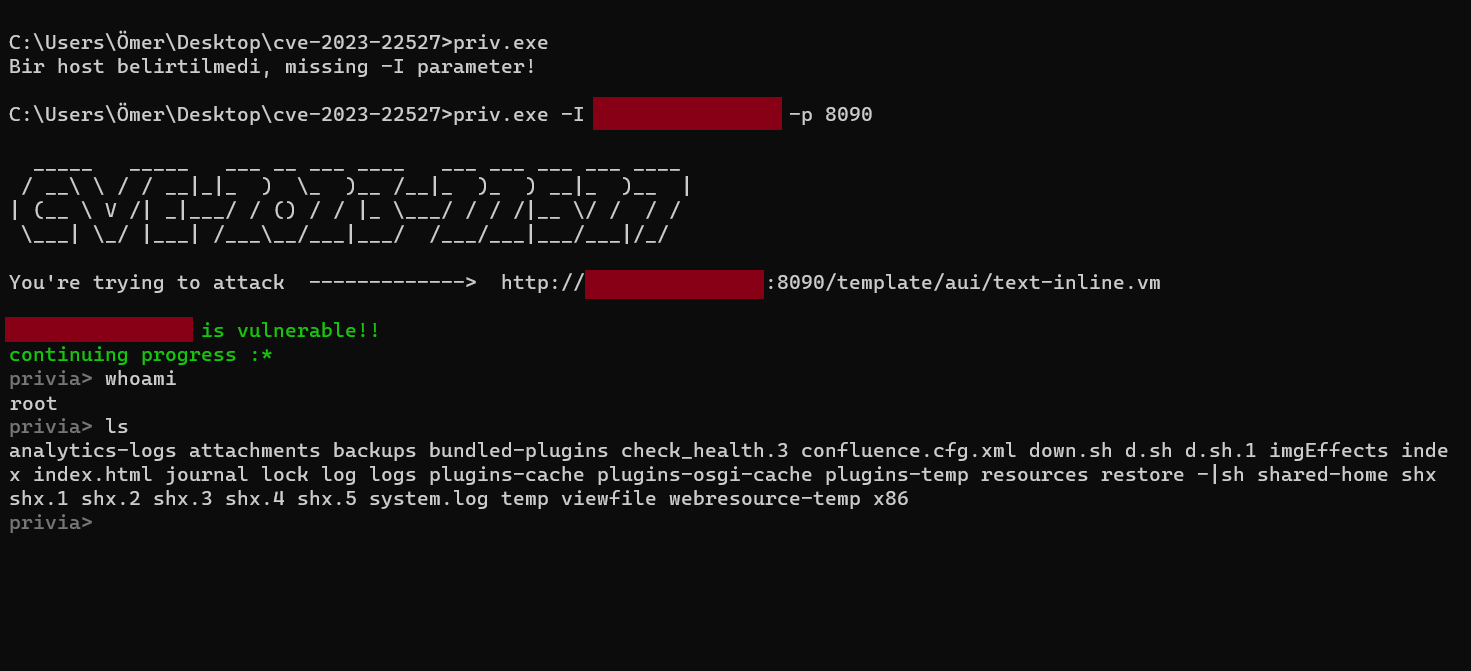 privia-security/cve-2023-22527
CVE-2023-22527
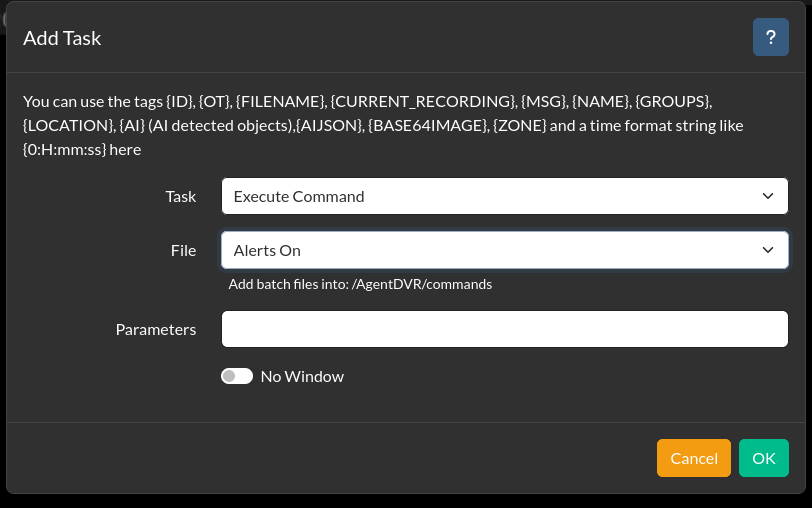 orange-418/agentdvr-5.1.6.0-file-upload-and-remote-code-execution
CVE-2024-22515 arbitrary file upload and CVE-2024-22514 remote code execution for AgentDVR 5.1.6.0 (Authenticated)
 guilhem7/cve-2025-46816
POC for exploit of goshs
 h4md153v63n/cve-2022-40348_intern-record-system-cross-site-scripting-v1.0-vulnerability-unauthenticated
CVE-2022-40348: Intern Record System - 'name' and 'email' Cross-site Scripting (Unauthenticated)
 huskyhacks/cve-2021-38699-reflected-xss
Multiple Reflected XSS in TastyIgniter v3.0.7 Restaurtant CMS