

r2s
 mxm0z/r2s
A web-based vulnerability scanner for CVE-2025-55182, a critical Remote Code Execution (RCE) vulnerability in React Server Components.
api-security-testingcloud-securityexploitation+3
mxm0z/r2sA web-based vulnerability scanner for CVE-2025-55182, a critical Remote Code Execution (RCE) vulnerability in React Server Components.
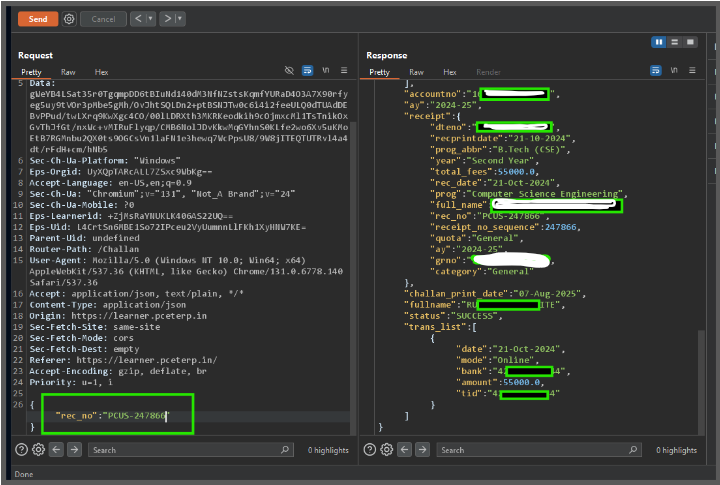 sharma19d/cve-2025-61148
The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…
 filipegaudard/cve-2026-30944-poc
Python proof-of-concept for CVE-2026-30944, exploiting a BOLA vulnerability in StudioCMS to escalate privileges via insecure API token generation.
 d0n601/cve-2025-12720
g-FFL Cockpit <= 1.7.1 - Improper Authorization to Unauthenticated Product Deletion
 fuyuooumi1027/cve-2023-45857-demo
Interactive demo for CVE-2023-45857 (axios XSRF token bypass). Step-by-step guide to reproduce the vulnerability in a controlled dev container…
 clemfavre/cve-2023-45612_exploit
Reproduction of a high severty security problem that allows XXE (XML eXternal Entity) attacks on Ktor's XML serialization.
 0xsu3ks/cve-2025-29556
PoC for CVE-2025-29556 creating Security Officer accounts on ExaGrid EX10 backup appliances via a low-privilege API session, enabling privilege…
 crackercat/cve-2022-24112
Apache APISIX apisix/batch-requests RCE
 skysliently/cve-2022-22947-pb-ai
一个由AI生成的漏洞验证应用
 secsys-fdu/cve-2025-51862
Demonstrates an IDOR vulnerability in TelegAI's chat API allowing unauthorized conversation tampering, leading to phishing and XSS-based account…
 secsys-fdu/cve-2025-51867
Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Deepfiction AI's chat API, allowing attackers to consume other users'…
 mindpatch/simple-maven
Deliberately vulnerable C# API application for practicing web application exploitation and security testing. Includes Docker setup and documentation…
 randomrobbiebf/cve-2023-45828
RumbleTalk Live Group Chat <= 6.1.9 - Missing Authorization via handleRequest
 nxploited/cve-2024-9707-poc
he Hunk Companion Plugin for WordPress: Vulnerable to Unauthorized Plugin Installation/Activation (Versions Up to and Including 1.8.4)
 blueowl-overlord/burp_cve-2025-31324
Python-based Burp Suite extension is designed to detect the presence of CVE-2025-31324
 aureum01/cve-2023-23752
A bash automation that exploits the vulnerable endpoints for the Joomla! API 4.0 - 4.2.7
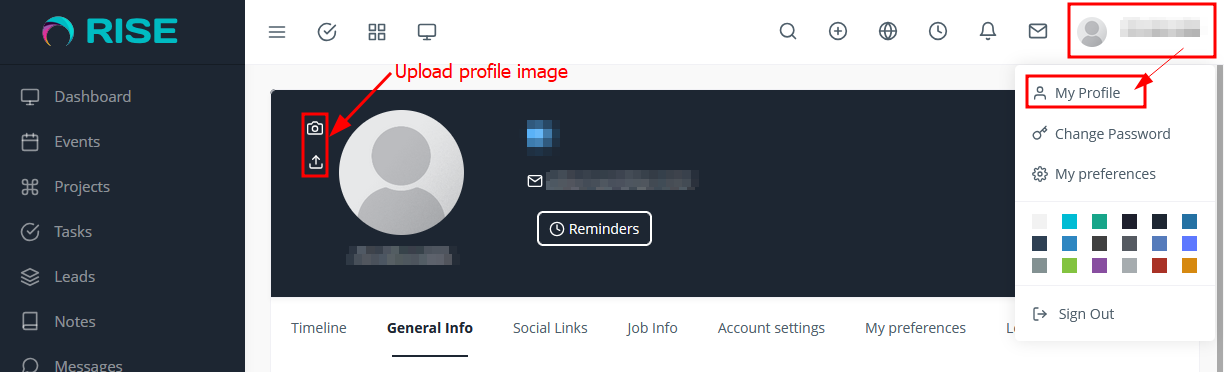 l4zyfox/rise-ultimate_project_manager_e_crm
CVE-2025-3855 - RISE Ultimate Project Manager - IDOR
 palmtreeforest/codepath_week_7-8
CodePath Assignment for Weeks 7 & 8: CVE-2017-14719, CVE-2019-9787 & Unauthenticated Page/Post Content Modification via REST API