

feroxbuster
 epi052/feroxbuster
A fast, simple, recursive content discovery tool written in Rust.
api-securityapi-security-testingcrawler+8
epi052/feroxbusterA fast, simple, recursive content discovery tool written in Rust.
 dmontgomery40/pentest-mcp
NOT for educational purposes: An MCP server for professional penetration testers including STDIO/HTTP/SSE support, nmap, go/dirbuster, nikto, JtR,…
 abraxas/forgejo-openid-discovery-ssrf
Forgejo 16.0.5 - High - Remote - SSRF - OpenID discovery fetches attacker-controlled URLs
 shenril/sitadel
Web Application Security Scanner
 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
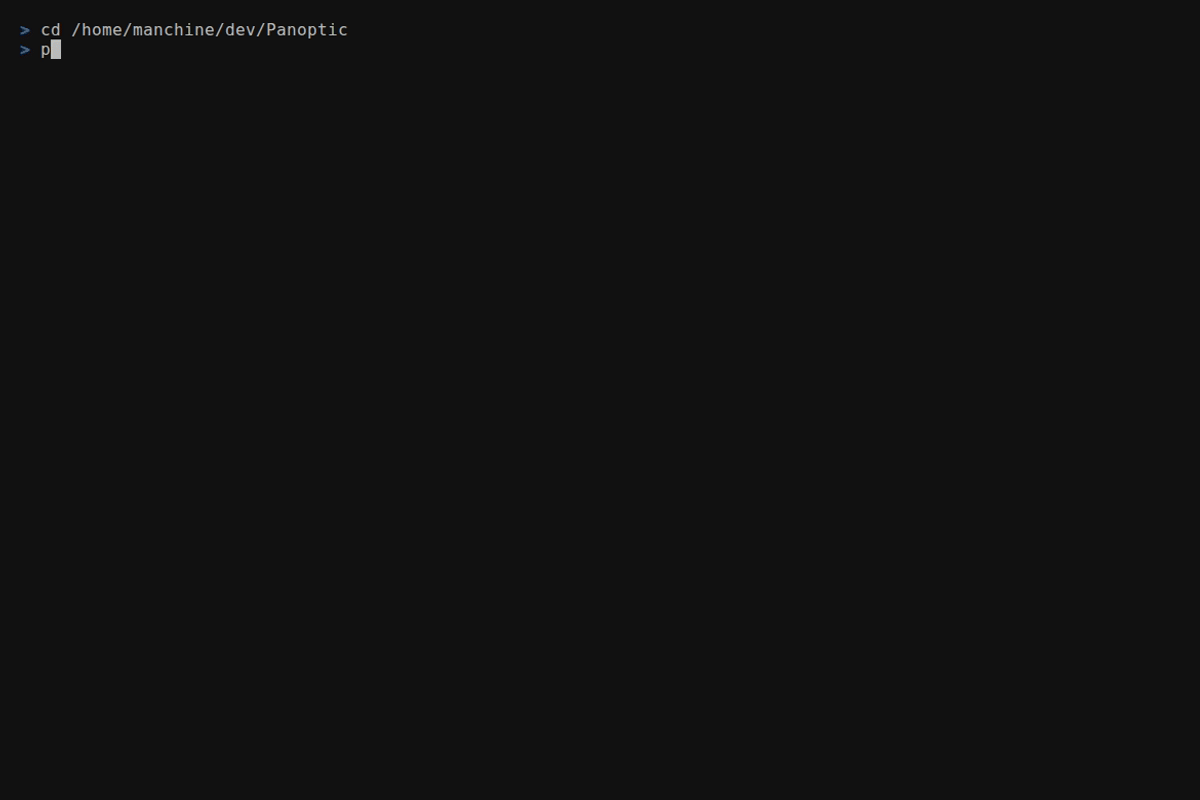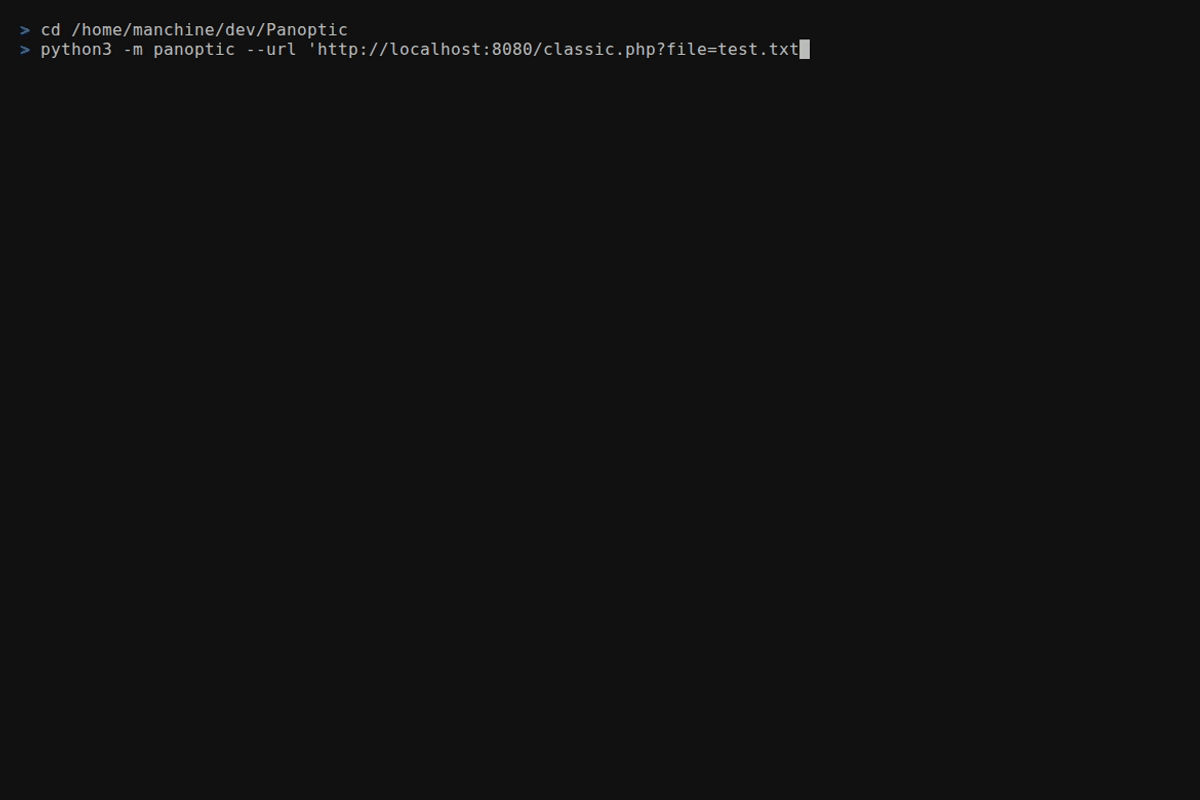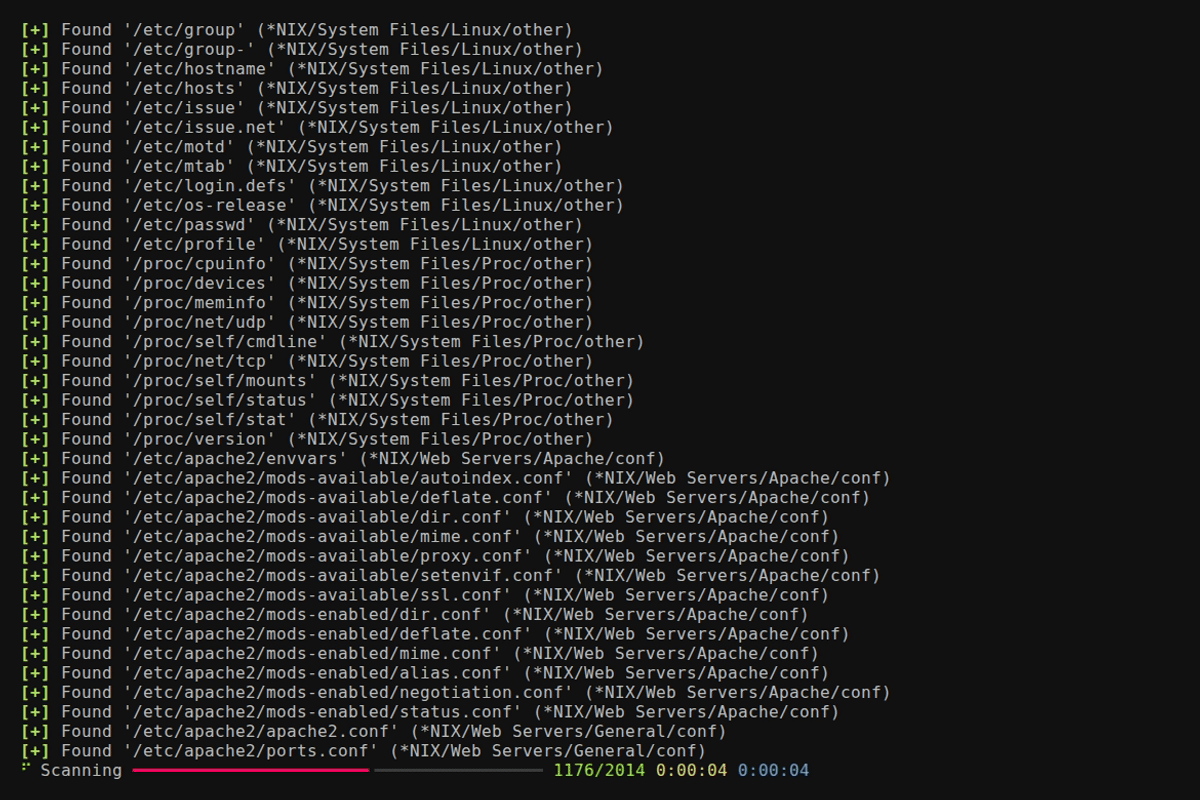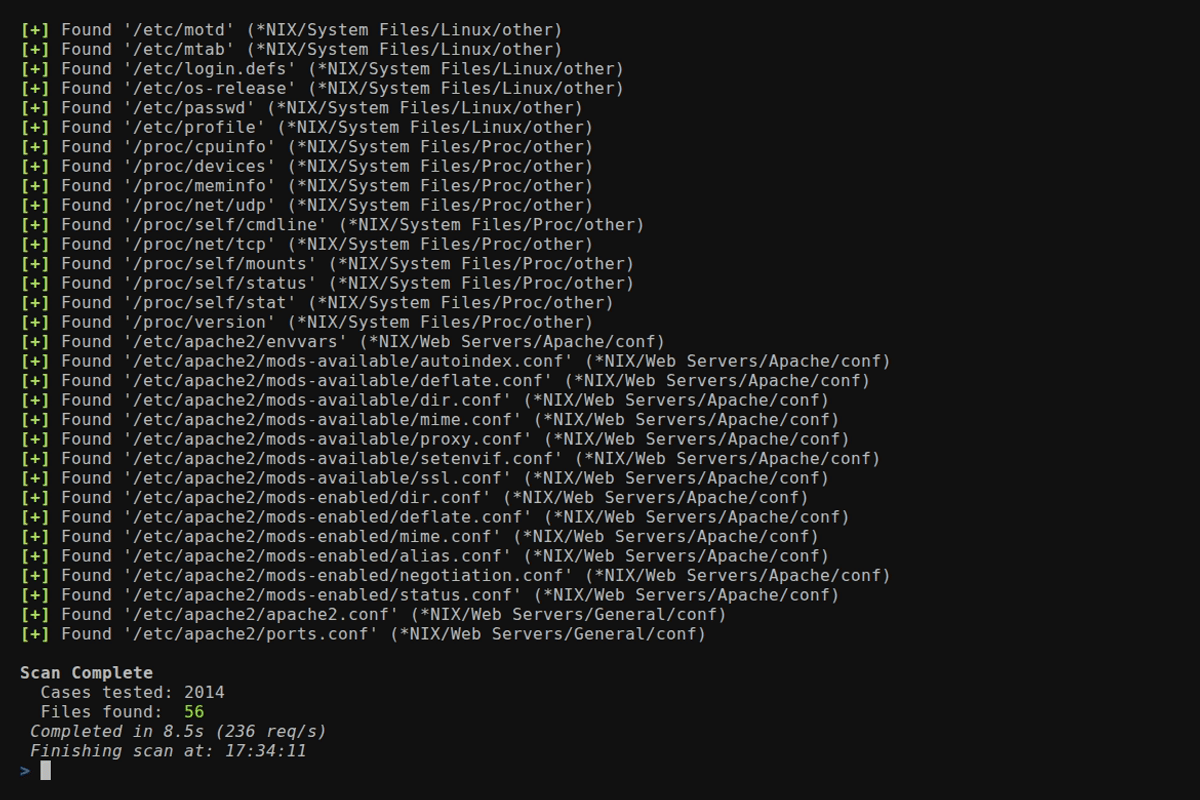 lightos/panoptic
Panoptic is an open source penetration testing tool that automates the process of search and retrieval of content for common log and config files…

 murrez/cve-2026-19658
Python 3 checker and exploit helper for CVE-2026-19658, a WordPress Give Tributes PHP object injection flaw, with FOFA target discovery and legacy…
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
 azmisyahrul/prismsec
Secure, modular MCP server wrapping nmap, nuclei, gobuster, subfinder, httpx, nikto, sqlmap for AI-powered pentesting
 sylhetyhackvenger/hikraven
HIKRAVEN - Advanced Hikvision Security Assessment Platform for professional penetration testing. Detects 12+ CVEs including CVE-2021-36260…
 nxploited/cve-2026-13714
Realtyna Organic IDX plugin + WPL Real Estate < 5.3.0 - Unauthenticated Arbitrary File Upload to Remote Code Execution
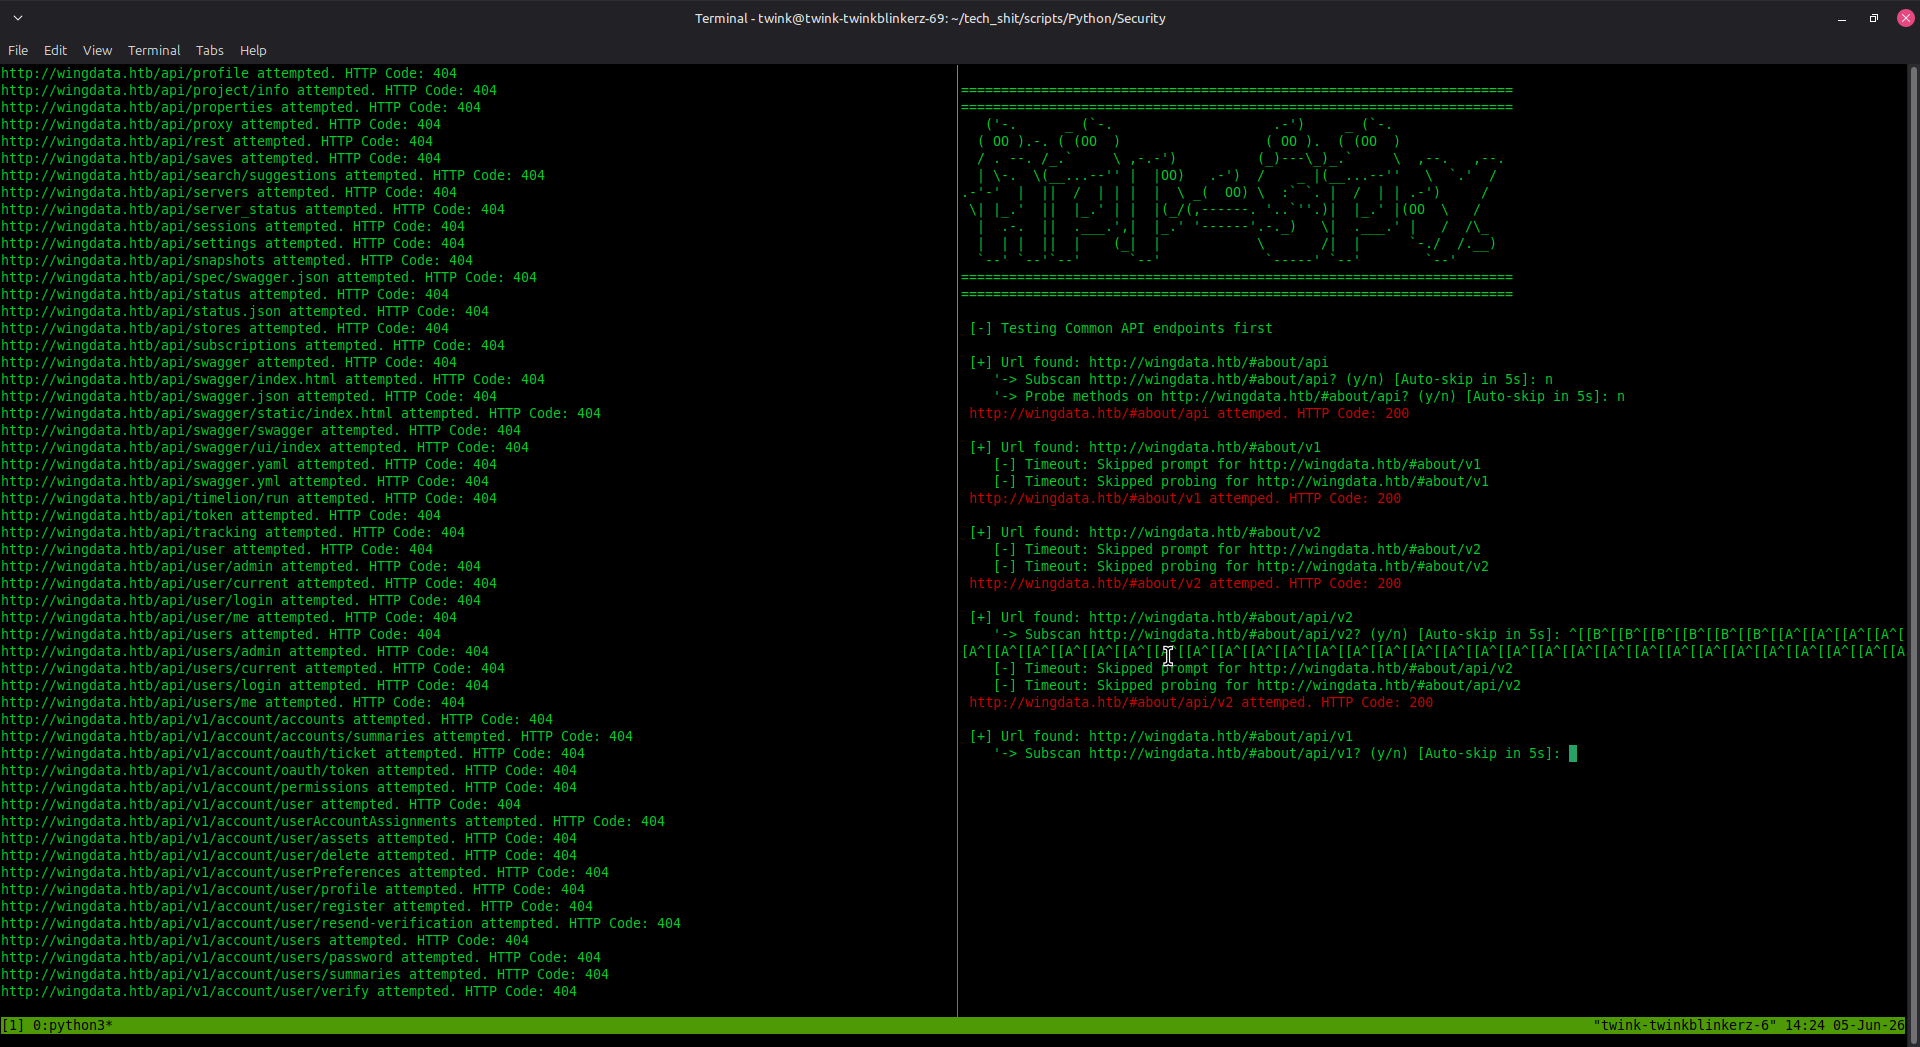 austinjump-sec/api-spy-api-probe
A powerful directory brute-force tool that's tailored for recursive/multiplex operations, API discovery and enumeration, JS file scraping, and lists…
 itstarsec/cve-2025-48703
Proof-of-concept exploit for CVE-2025-48703, an unauthenticated remote code execution vulnerability in CentOS Web Panel (CWP) versions prior to…
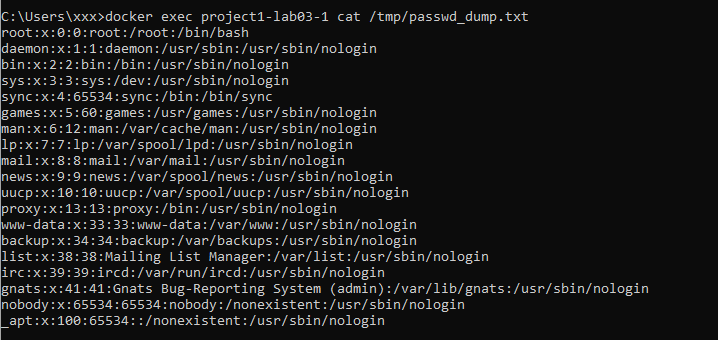 dungsocool/cve-2017-11610
Step-by-step exploit writeup for CVE-2017-11610 (Supervisord XML-RPC RCE) with attack surface analysis, namespace traversal discovery, and…
 synacktiv/cve-2025-59213
Unauthenticated SQL injection exploit for Microsoft Configuration Manager (SCCM) 2503, enabling arbitrary SQL execution on the site database via the…
 renison-gohel/cve-2026-42945-nginx-rift
Python exploit for CVE-2026-42945 (NGINX Rift) with reverse shell capability and Shodan-based target discovery for penetration testing.
 jeanback1/cve-2023-27163-exploit
SSRF exploit for CVE-2023-27163 in request-baskets, enabling internal port scanning, cloud metadata probing, and service discovery via malicious…