
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
37 results
HackTheBox-Facts preview

HackTheBox-Facts

GitHubsuriyaboon/hackthebox-facts

HTB Facts is a Easy Linux box featuring Camaleon CMS and MinIO. Gain admin access via open registration and a mass assignment vulnerability, then…
cloud-securityctfeducation+7
26 days ago
metasploitable3-pentest-writeup preview

metasploitable3-pentest-writeup

GitHubadfortunato/metasploitable3-pentest-writeup

Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
ctfeducationexploitation+8
1 month ago
CVE-2026-42945_NginxRift preview

CVE-2026-42945_NginxRift

GitHubkentox493/cve-2026-42945_nginxrift

Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…

binary-exploitationcontainer-securityctf+5
12 months ago
Sudo-Agent-CTF- preview

Sudo-Agent-CTF-

GitHubnyxrecon/sudo-agent-ctf-

Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.
ctfeducationexploitation+7
2 months ago
Room-Walkthrough-Billing preview

Room-Walkthrough-Billing

GitHubadityabhatt3010/room-walkthrough-billing

A detailed walkthrough of Billing room exploiting CVE-2023-30258 and escalating via fail2ban misconfig
ctfeducationexploitation+6
143 months ago
traveller-htb preview

traveller-htb

GitHubsharma01672/traveller-htb

Traveller is an Easy Linux machine featuring a Joomla 4.2.7 travel booking website vulnerable to CVE-2023-23752, an unauthenticated REST API…
educationexploitationinformation-gathering+6
4 months ago
Shocker-TJNULL-OSCP- preview

Shocker-TJNULL-OSCP-

GitHubr3fr4kt/shocker-tjnull-oscp-

Structured HTB walkthrough demonstrating Shellshock (CVE-2014-6271) exploitation via CGI directory fuzzing and privilege escalation through…
educationexploitationlabs-practice+6
5 months ago
CVE-2025-24071-POC preview

CVE-2025-24071-POC

GitHubbuffertrychar/cve-2025-24071-poc

Proof-of-concept exploit for CVE-2025-24071, generating a malicious ZIP file that triggers NTLM hash disclosure via Windows Explorer, used with an…
exploitationpayload-generationpenetration-testing+2
5 months ago
SimpleCTF-THM-Walkthrough preview

SimpleCTF-THM-Walkthrough

GitHubpaulameg/simplectf-thm-walkthrough

First CTF successfully completed! This repo documents my walkthrough of TryHackMe's Simple CTF. It covers network reconnaissance (Nmap), web…
ctfeducationpassword-cracking+5
15 months ago
CVE-2026-23918-Apache-HTTP-Server-DoubleFree-PoC preview

CVE-2026-23918-Apache-HTTP-Server-DoubleFree-PoC

GitHubcyfare/cve-2026-23918-apache-http-server-doublefree-poc

Proof-of-concept exploit for CVE-2026-23918, a double-free vulnerability in Apache HTTP Server, demonstrating remote crash via crafted requests.
exploitationpenetration-testingvulnerability-analysis+2
5 months ago
Penetration-Testing-Walkthrough-Hacksudo-Thor preview

Penetration-Testing-Walkthrough-Hacksudo-Thor

GitHubheventafese/penetration-testing-walkthrough-hacksudo-thor

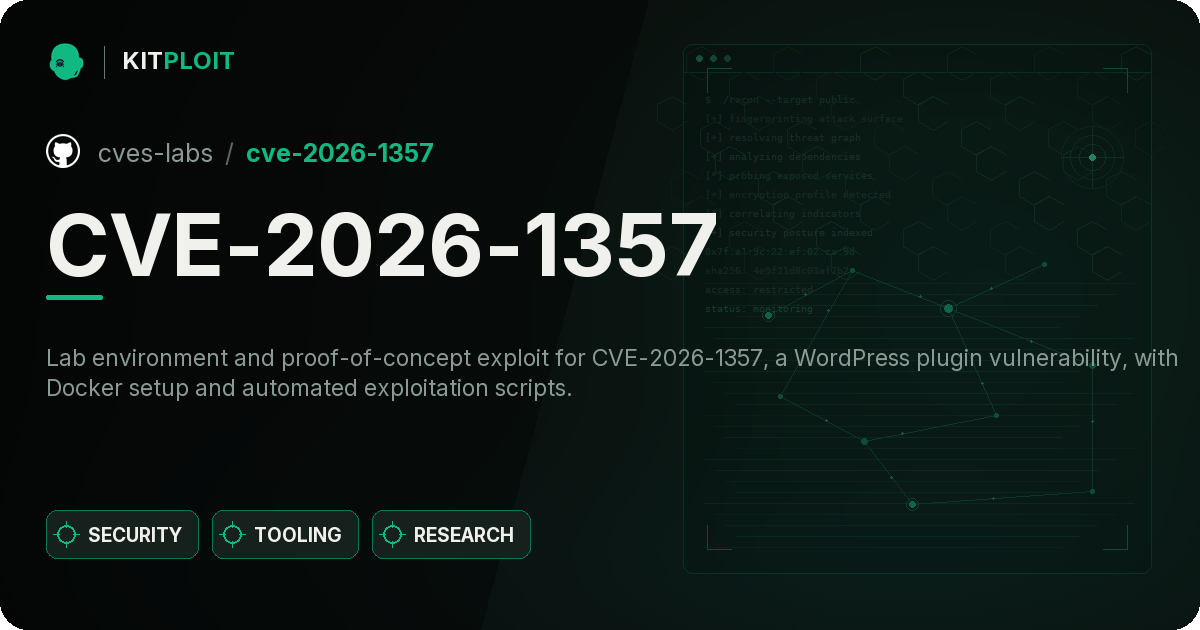
Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…
ctfeducationexploitation+8
6 months ago
CVE-2026-1357 preview

CVE-2026-1357

GitHubcves-labs/cve-2026-1357

Lab environment and proof-of-concept exploit for CVE-2026-1357, a WordPress plugin vulnerability, with Docker setup and automated exploitation…
educationexploitationlabs-practice+3
6 months ago
CVE-2021-43857-Gerapy-v0.9.7 preview

CVE-2021-43857-Gerapy-v0.9.7

GitHubafifudinmtop/cve-2021-43857-gerapy-v0.9.7

Exploit for CVE-2021-43857 in Gerapy v0.9.7, providing a reverse shell via authenticated project creation and command injection.
exploitationpenetration-testingremote-access-tool+2
9 months ago
CVE-2009-3103 preview

CVE-2009-3103

GitHubafifudinmtop/cve-2009-3103

Exploit for CVE-2009-3103, a Windows SMB remote code execution vulnerability, with a Python script and Metasploit handler for reverse shell.
command-and-controlexploitationpayload-generation+3
9 months ago
CVE-2021-21425 preview

CVE-2021-21425

GitHubafifudinmtop/cve-2021-21425

Python exploit for CVE-2021-21425 that executes a reverse shell payload against a target IP, with instructions for setting up a netcat listener.
command-and-controlexploitationpayload-generation+2
9 months ago
Helpdesk-Telecom-CVE-2025-64459 preview

Helpdesk-Telecom-CVE-2025-64459

GitHubalxsourin/helpdesk-telecom-cve-2025-64459

Sets up a vulnerable Django web application and provides a PDF detailing exploitation of CVE-2025-64459 for security training and lab practice.
educationexploitationpenetration-testing+2
9 months ago
CVE-2024-23897 preview

CVE-2024-23897

GitHubhybinn/cve-2024-23897

Step-by-step lab environment setup for exploiting CVE-2024-23897 in Jenkins, including Java installation, WAR file download, and execution on port…
educationexploitationlabs-practice+3
1 year ago
cve-2023-3824 preview

cve-2023-3824

GitHubdadosneurais/cve-2023-3824

Proof-of-concept exploit for CVE-2023-3824 (PHP phar deserialization) enabling remote code execution via crafted phar archive and reverse shell…

command-and-controlexploitationpayload-generation+3
1 year ago
Previous123Next