

httpx
 projectdiscovery/httpx
Fast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
api-securityapi-security-testingcrawler+18
10.5k
projectdiscovery/httpxFast, multi-probe HTTP toolkit for reconnaissance and information gathering. Probes TLS, CSP, headers, tech stack, and CDN. Supports matchers,…
 lightos/panoptic
Panoptic is an open source penetration testing tool that automates the process of search and retrieval of content for common log and config files…
 shinthink/blitzstrike
MCP server packaging a three-tier penetration-testing methodology: attack-surface reconnaissance, source-to-sink static analysis, and live finding…
 candisexterior171/cve-2026-57827
Demonstrate the unauthenticated remote code execution vulnerability in the RSFiles! Joomla component through an arbitrary file upload.
 shenril/sitadel
Web Application Security Scanner
 abraxas/cve-2026-87902
Proof-of-concept and disclosure pack for CVE-2026-87902, an unauthenticated local file inclusion in WordPress Core via locate_template(), with a…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
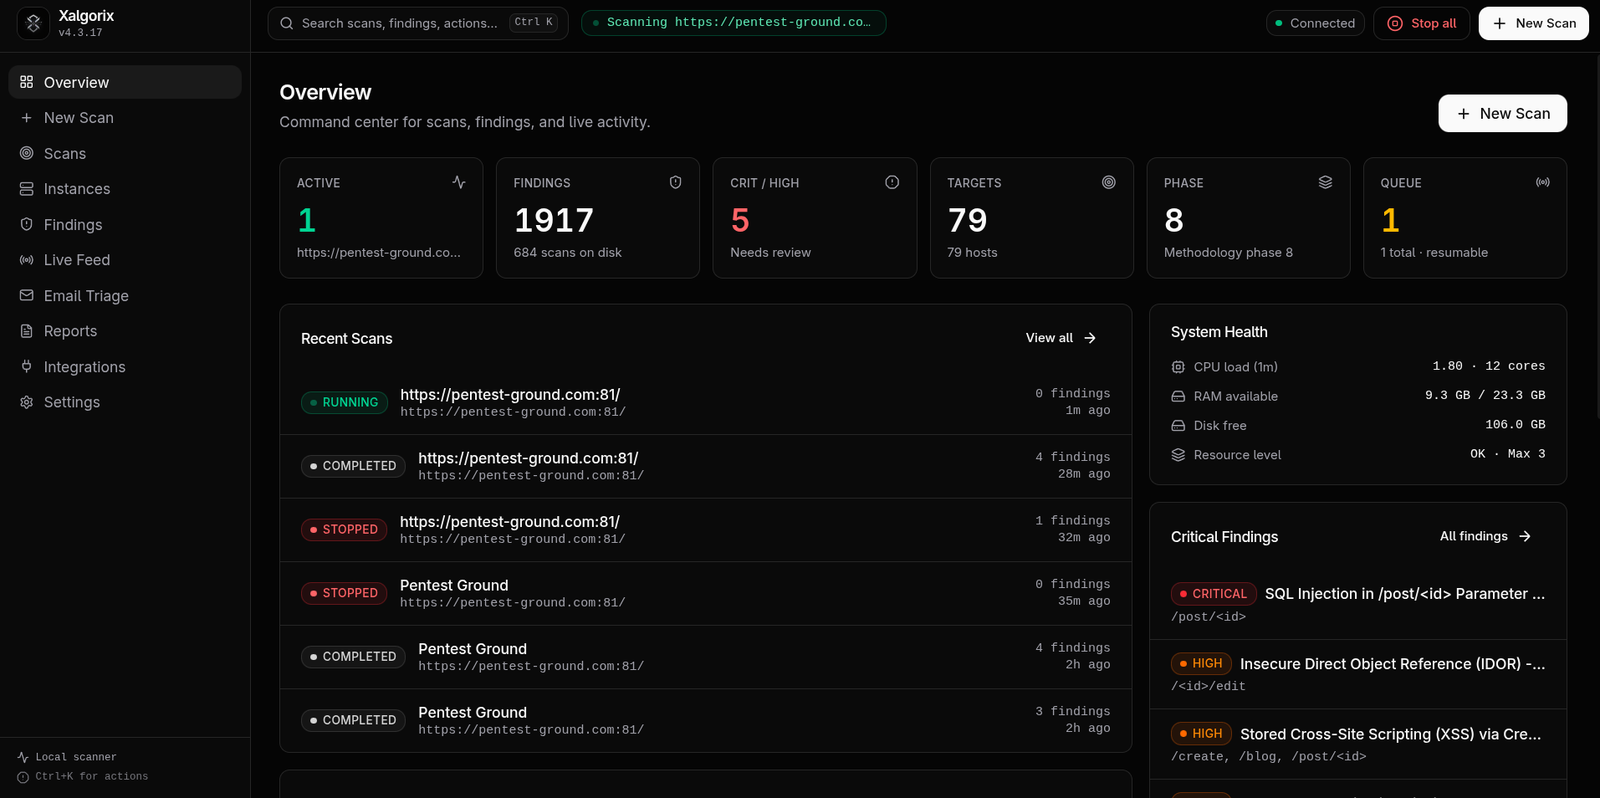 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 qyvora/qyvora-anansi
Terminal-first attack surface intelligence engine. Built for speed, portability, and raw technical signal.
 kiwknr/cve-2026-103978
Proof-of-concept and writeup for CVE-2026-103978, an unauthenticated path traversal in OPNMGR's snyk_scan_progress.php allowing arbitrary .json file…
 elvira-alec/fracture
FragAttacks WiFi penetration framework — CVE-2020-24586/87/88
 abraxas/cve-2026-52782
Reproduction pack and PoC script for CVE-2026-52782, an authenticated IDOR in OpenProject project storage settings that hijacks Nextcloud/OneDrive…
 bombobombone/cve-2026-103445
Report summary and local proof-of-concept for CVE-2026-103445, a stored XSS in MediaWiki PageForms #autoedit via javascript: redirect URLs.
 mrdark-ops/cve-2026-12227
Proof-of-concept and technical analysis for CVE-2026-12227, an unauthenticated LFI/RCE in the WordPress Visual Composer plugin via the vcv-template…
 murrez/cve-2026-102425
Python PoC for CVE-2026-102425: unauthenticated RCE in Joomla Balbooa Forms (com_baforms) via field shortcode injection in post-submission PHP…
 murrez/cve-2026-101894
Python PoC for CVE-2026-101894: symlink-chain path traversal in @xhmikosr/decompress. Includes local Node lab, lockfile version scan, and mass…
 murrez/cve-2026-101110
Python 3 PoC and mass exploit for CVE-2026-101110, an unauthenticated ORDER BY SQL injection in OrdaSoft Joomla Book Library <=6.4.6 via…
 murrez/cve-2026-101108
Python 3 PoC and mass scanner for CVE-2026-101108, an unauthenticated ORDER BY SQL injection in OrdaSoft Joomla Vehicle Manager <=6.5.7…