
cve-2024-38819-lab
 trevorputbrese/cve-2024-38819-lab
Hands-on lab demonstrating CVE-2024-38819 Spring Framework path traversal vulnerability with vulnerable and patched Spring Boot deployments for…
educationlabs-practicemisconfiguration+3
trevorputbrese/cve-2024-38819-labHands-on lab demonstrating CVE-2024-38819 Spring Framework path traversal vulnerability with vulnerable and patched Spring Boot deployments for…
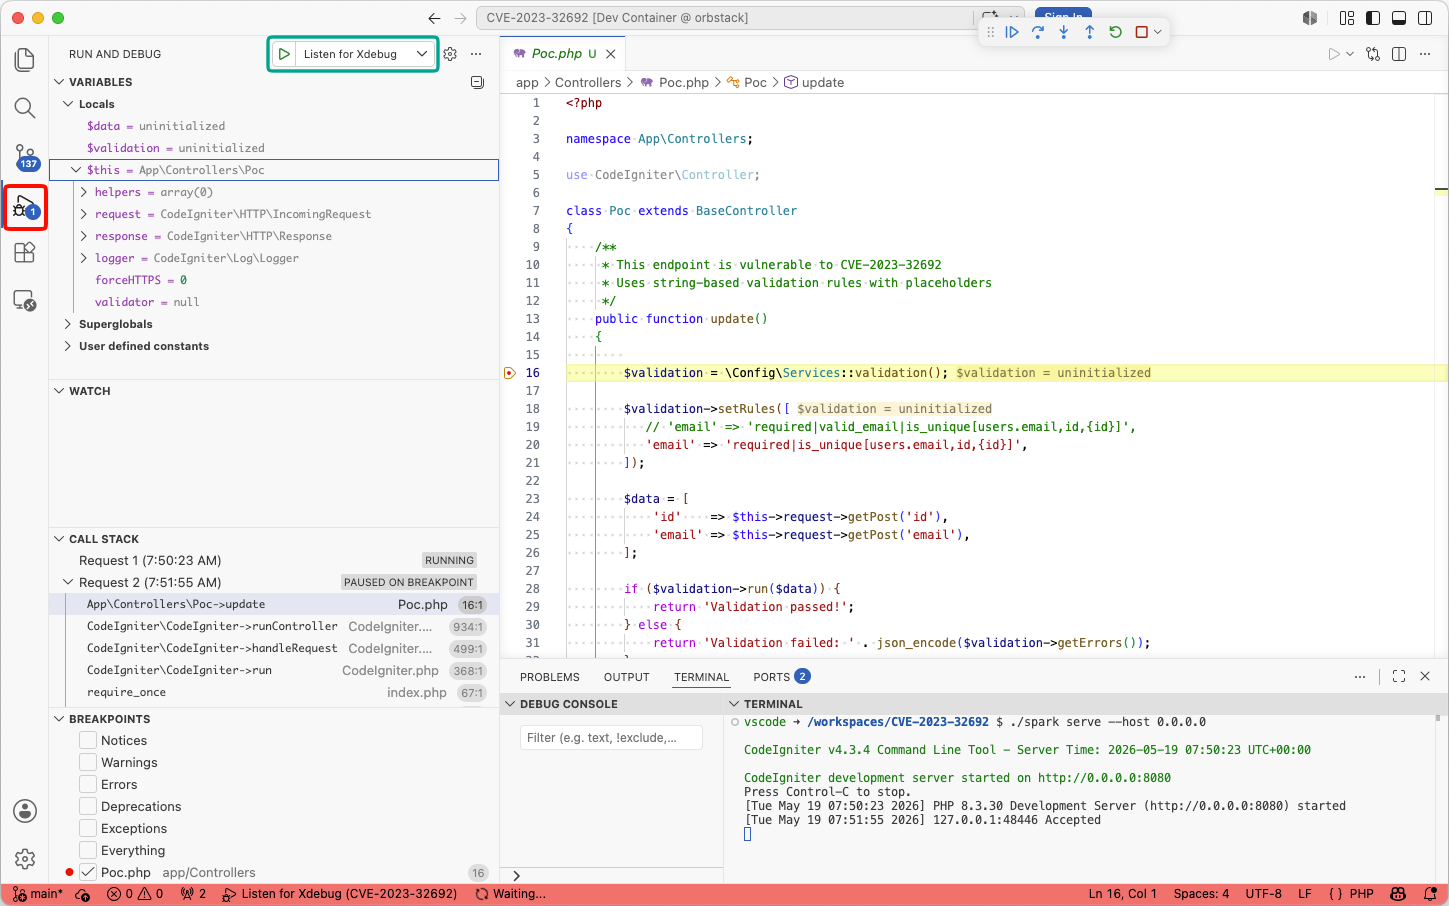 mogwailabs/cve-2023-32692-codeigniter4
Example application, vulnerable to CVE-2023-32692 (Validation Rule Injection in the PHP Framework CodeIgniter)
 kishorbal/deep-c
Android deeplink misconfiguration detector and exploitation tool
 ak-cybe/cve-2025-68664-langgrinch-poc
A testing framework to identify and demonstrate deserialization vulnerabilities in LangChain Core (<0.3.81). Educational use only
 theori-io/reactguard
ReactGuard provides framework- and vulnerability-detection tooling for CVE-2025-55182 (React2Shell)
 niokagi/react-cve-2025-55182
Test & Analyze the CVE-2025-55182 vulnerability within Next.js Server Actions
 shoucheng3/apache__myfaces_cve-2011-4367_2-0-11
Exploit for CVE-2011-4367 targeting Apache MyFaces JSF implementation, demonstrating a remote code execution vulnerability in the Jakarta Faces…
 zr0n/react2shell
A complete framework for exploiting the vulnerability CVE-2025-55182
 lachlan2k/react2shell-cve-2025-55182-original-poc
Original proof-of-concept exploits for React2Shell (CVE-2025-55182), demonstrating remote code execution in Next.js applications via Webpack chunk…
 drackyjr/cve-2025-3248-exploit
A comprehensive Python exploitation framework for testing and demonstrating CVE-2025-3248, a critical unauthenticated remote code execution…
 kadamnayan/poc-cve-2024-38820
Proof-of-concept exploit for CVE-2024-38820, demonstrating locale-dependent case conversion bypass of Spring Framework DataBinder disallowedFields…
 shoucheng3/spring-projects__spring-framework_cve-2022-22965_5-2-19-release
Exploit for CVE-2022-22965 (Spring4Shell) targeting Spring Framework versions vulnerable to remote code execution via classLoader manipulation.
 shoucheng3/vert-x3__vertx-web_cve-2018-12542_3-5-3-cr1
Exploit for CVE-2018-12542 in Vert.x-Web, a Java web framework. Demonstrates a path traversal vulnerability allowing unauthorized access to static…
 kai-one001/letta-cve-2025-51482-rce
Proof-of-concept exploit for CVE-2025-51482, demonstrating remote code execution via unsafe exec() usage and sandbox bypass in the Letta AI agent…
 syfi/cve-2023-46818
Metasploit Modules
 seanpesce/cve-2024-22243
Example exploitable scenarios for CVE-2024-22243 affecting the Spring framework (open redirect & SSRF).
 abdurahmon3236/cve-2024-6366
Metasploit exploit module for CVE-2024-6366, an unauthenticated file upload remote code execution in WordPress User Profile Builder before 3.11.8,…
 abdurahmon3236/-cve-2024-31211
Metasploit module that exploits a WordPress unserialization vulnerability (CVE-2024-31211) in WP_HTML_Token to achieve remote code execution.