

openfire-ssrf-cve-2019-18394
 l0lsec/openfire-ssrf-cve-2019-18394
PoC for CVE-2019-18394: unauthenticated full-read SSRF in Openfire <= 4.4.2 FaviconServlet
exploitationpenetration-testingreconnaissance+4
l0lsec/openfire-ssrf-cve-2019-18394PoC for CVE-2019-18394: unauthenticated full-read SSRF in Openfire <= 4.4.2 FaviconServlet
 clayofgilgamesh/cve-2026-29000
CTF lab and exploit toolkit for CVE-2026-29000, a pac4j-jwt JWE authentication bypass. Includes vulnerable Flask target, token forging library,…
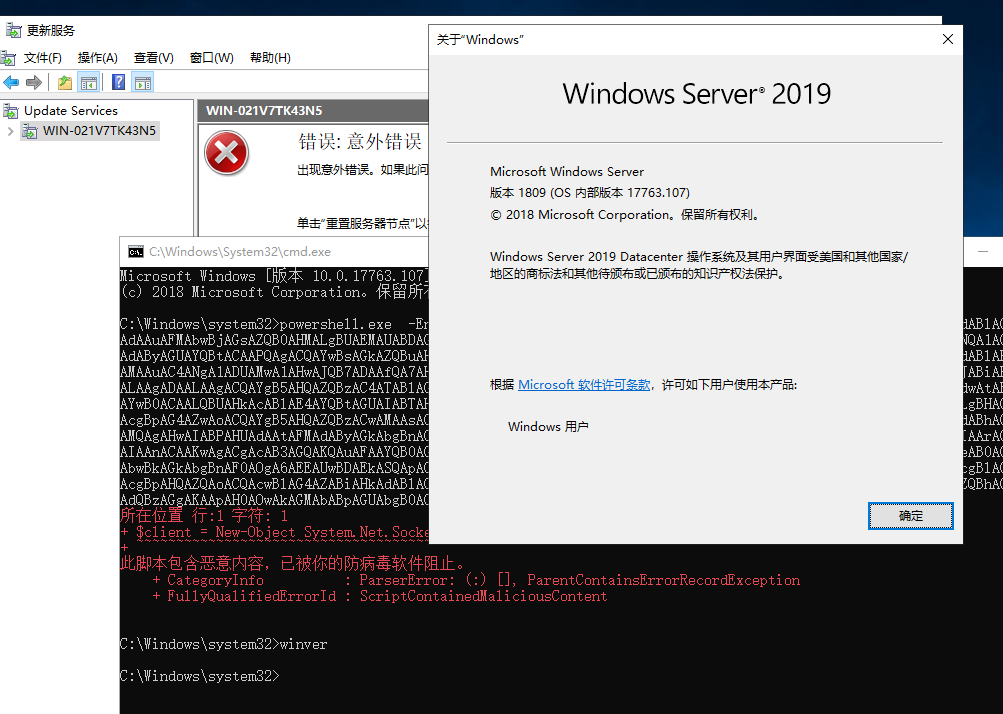 0x7556/cve-2025-59287
Exploit for CVE-2025-59287, injecting WolfShell memory webshell into WSUS servers to achieve remote code execution when the admin console is opened.
 k0nnect/halo-cve-2026-67919
halo cms plugin 1-request rce from a url, PoC + exploit chain
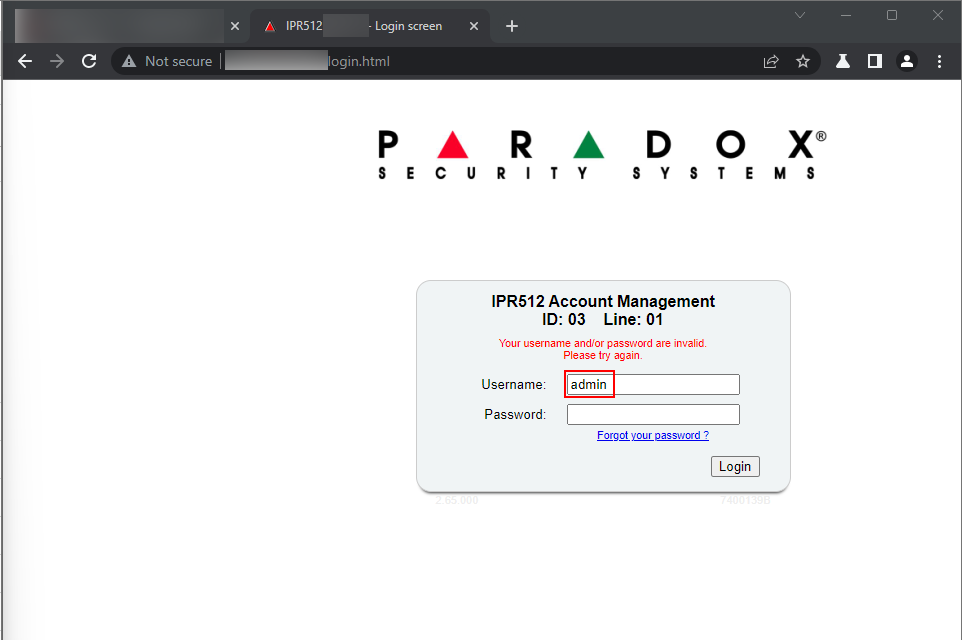 darknesschieftain/injection-vulnerability-in-paradox-security-systems-ipr512-cve-2023-24709-poc
In Paradox Security System IPR512 Web console login form page, attacker can input JavaScript string, such as "</script>" that will overwrite…
 nxploited/cve-2024-50498
Exploit script for CVE-2024-50498 code injection in WordPress WP Query Console that checks vulnerability and delivers a reverse shell.
 mbadanoiu/mal-012
MAL-012: Reflected Cross-Site Scripting in Admin Console leading to Remote Code Execution in Payara Server
 mbadanoiu/wso2-2021-1258
WSO2-2021-1258: Zip Slip vulnerability in WSO2 ESB
 rdincel1/craft-cms-3.0.25---cross-site-scripting
Craft CMS 3.0.25 - Cross-Site Scripting Vulnerability
 gabrielha12/glassfish-research
CVE-2026-2586 — Eclipse GlassFish EL injection to RCE
 maxmnml/majordomo-cve-2026-27174-poc
CVE-2026-27174 - An unauthenticated remote code execution via the admin panel's PHP console feature
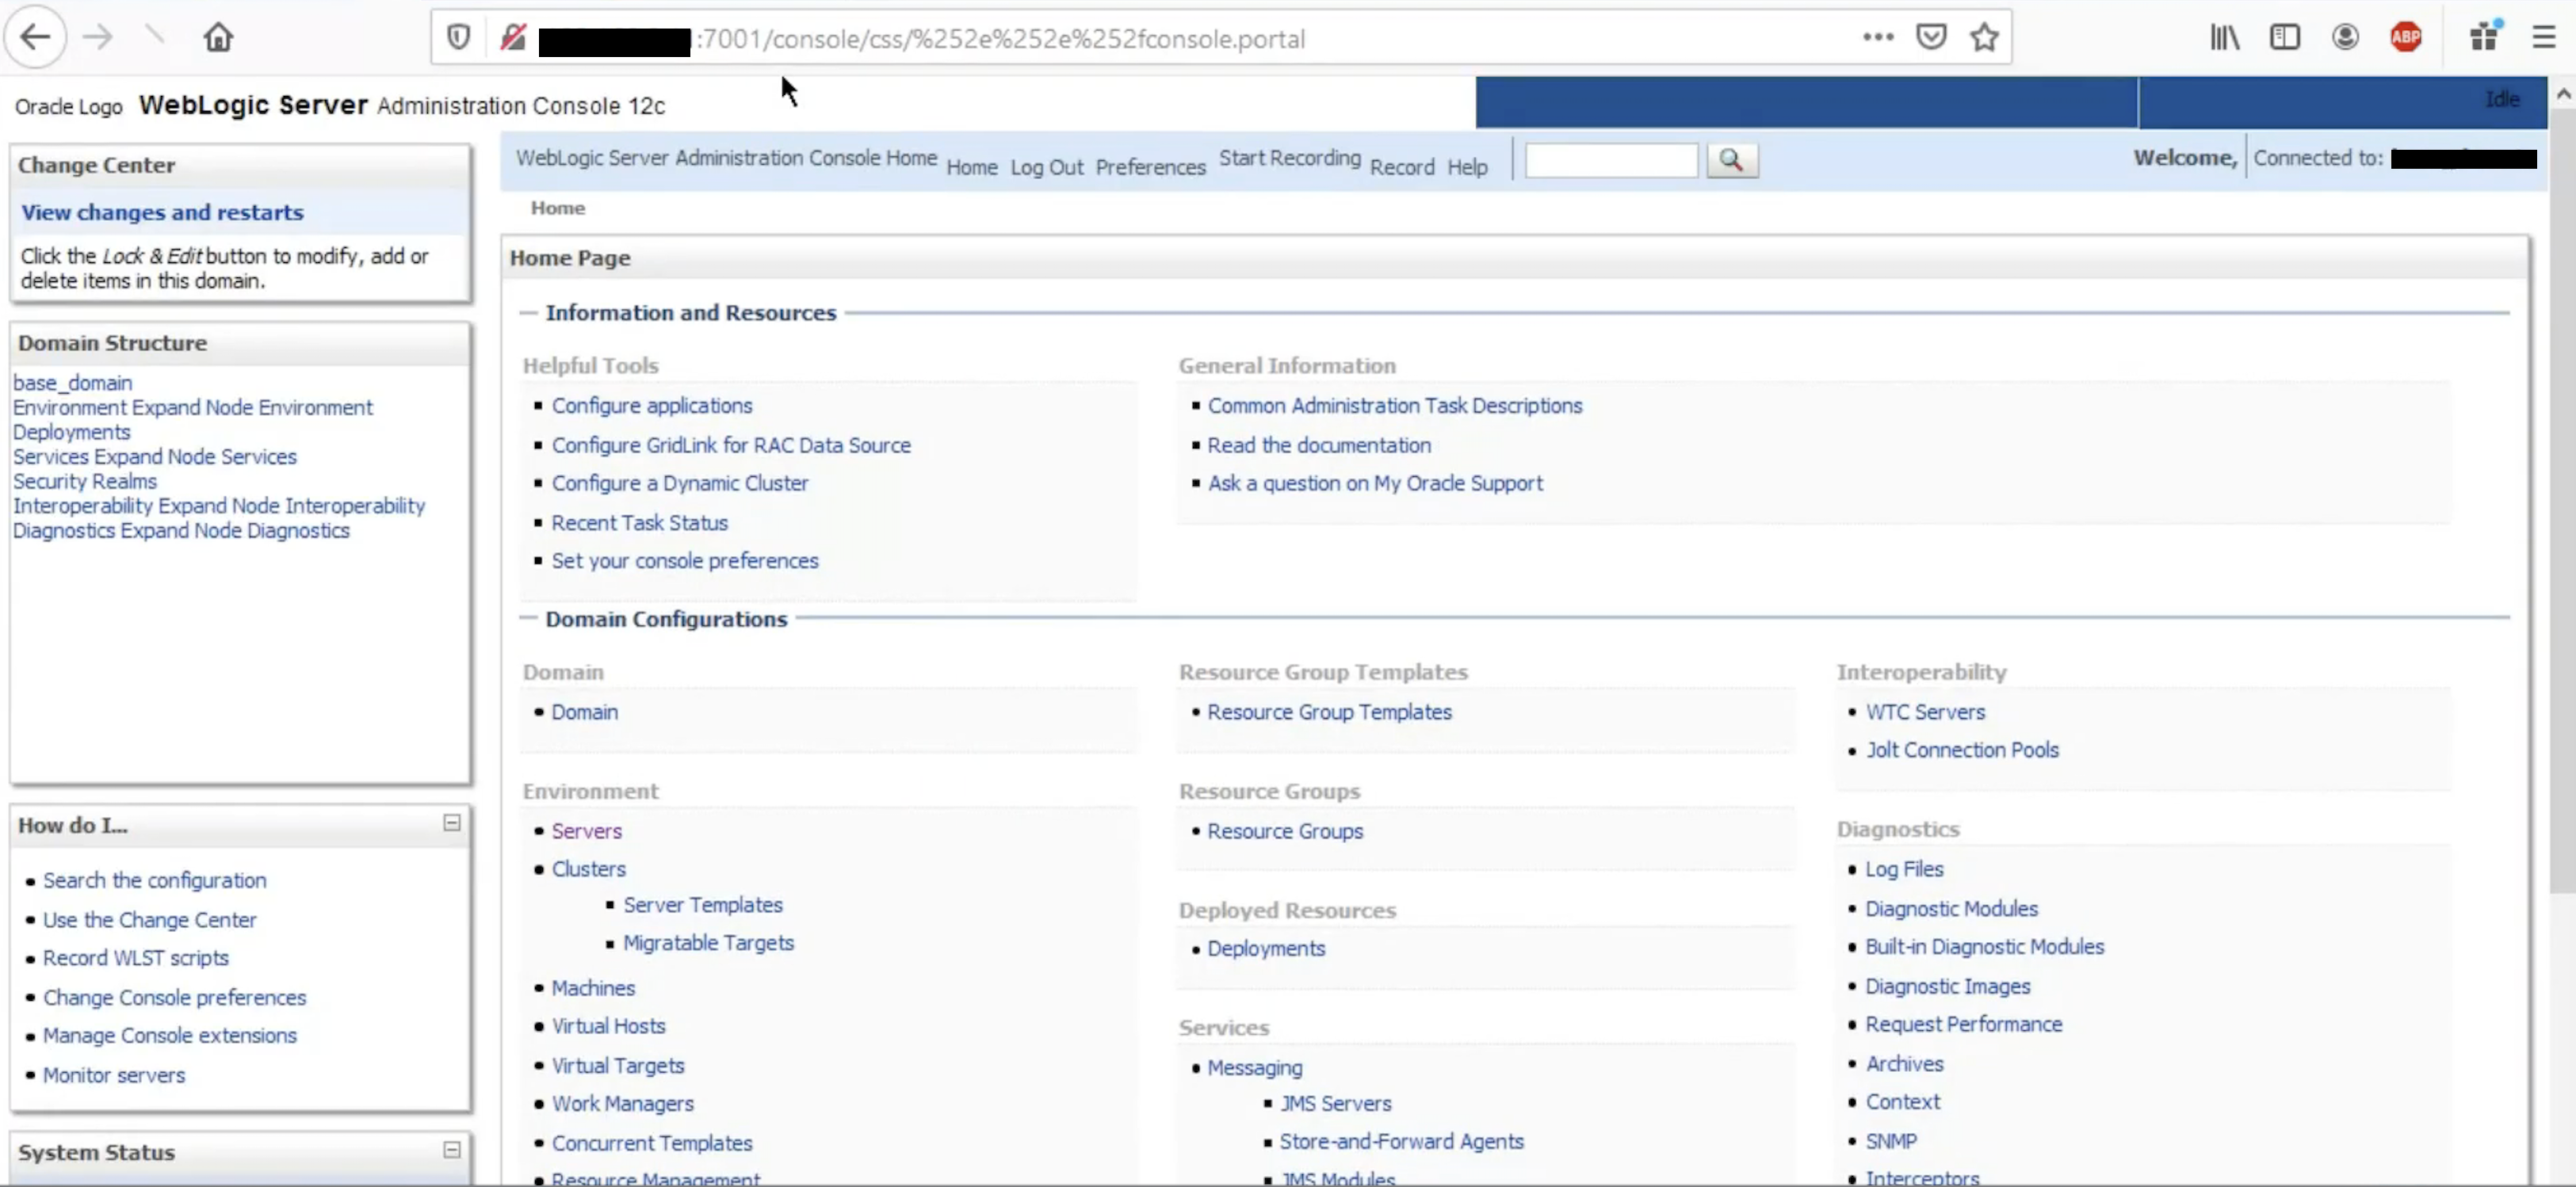 murataydemir/cve-2020-14882
[CVE-2020-14882] Oracle WebLogic Server Authentication Bypass
 voidsshadows/hikvision-city-hunter
This tool is a modern evolution of older PoCs like those for CVE-2017-7921 and ICSA-17-124-01, updated for 2025 with live console output, threading…
 wrathfuldiety/cve-2025-52357
Proof of Concept and Security Advisory for XSS vulnerability in the FD602GW-DX-R410 fiber router’s admin console (firmware V2.2.14). Includes…
 ydycjz6j/cve-2020-17453-poc
PoC (Proof of Concept) - CVE-2020-17453
 edgarloyola/cve-2021-36563
Proof-of-concept for stored and reflected XSS vulnerabilities in CheckMK Management Web Console versions 1.5.0 to 2.0.0p9, with detailed disclosure…
 edgarloyola/cve-2021-40904
Proof-of-concept for remote code execution in CheckMK Raw Edition 1.5.0–1.5.0p25 via misconfigured Dokuwiki embedded application allowing PHP code…
 edgarloyola/cve-2021-40906
Proof-of-concept for a reflected XSS vulnerability in CheckMK Management Web Console (versions 1.5.0 to 1.6.0), enabling session theft or backdoor…