IBM-Langflow-CVE-2026-48519-poc

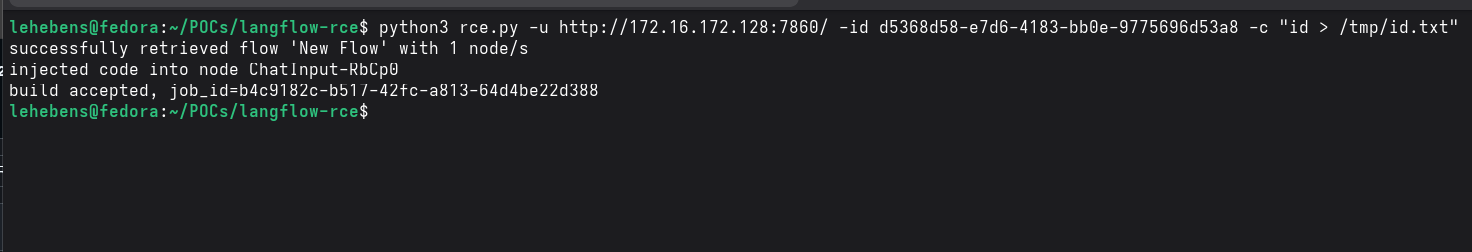
Proof-of-concept exploit for CVE-2026-48519, a pre-auth RCE in IBM Langflow <= 1.9.1 via the Shareable Playground /api/v1/build_public_tmp endpoint.

Proof-of-concept exploit for CVE-2026-48519, a pre-auth RCE in IBM Langflow <= 1.9.1 via the Shareable Playground /api/v1/build_public_tmp endpoint.

PoC for CVE-2026-17633 — Authenticated RCE in IBM Langflow OSS 1.0.0–1.10.3 via custom_component endpoint. Includes CVE-2026-17632 AST scanner bypass…

Proof-of-concept exploit for CVE-2026-9198, an unauthenticated RCE in IBM Langflow OSS, chaining auto_login and validate/code endpoints. Includes a…

CVE-2026-9198利用代码

Exploit script for CVE-2026-9198 targeting IBM Langflow, providing proof-of-concept code to validate vulnerabilities and support authorized security…

IBM Langflow Unauthenticated RCE via Auto-Login Bypass

Proof of Concept for CVE-2026-9198 - IBM Langflow Unauthenticated RCE via Auto-Login Bypass

Unauthenticated RCE exploit for Langflow OSS chaining auto_login JWT bypass with validate/code exec() to achieve remote command execution and reverse…

CVE-2020-4464 / CVE-2020-4450

Proof-of-concept exploit for CVE-2022-26377, an AJP smuggling vulnerability that poisons the HTTP response queue of IBM QRadar with a stored redirect.

CVE-2023-30990 exploits

CVE-2022-47986: Python, Ruby, NMAP and Metasploit modules to exploit the vulnerability.

IBM Maximo Asset Management is vulnerable to Information Disclosure via XXE Vulnerability (CVE-2020-4463)

CVE-2018-8021 Proof-Of-Concept and Exploit

Proof-of-concept exploit for CVE-2017-1635, a use-after-free vulnerability in IBM Tivoli Monitoring's KDH web server component enabling remote code…

A POC for IBM Datapower Authenticated Redis RCE Exploit abusing the Test Message Function (CVE-2020-5014)

IBM Proventia Sensor Appliance - Multiple Input Validation Vulnerabilities

IBM i Access Client Solutions < 1.1.9.4 - Remote code execution via insecure deserialisation