

joomla-bruteforce
 ajnik/joomla-bruteforce
Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
authenticationpassword-attackspassword-cracking+4
138
ajnik/joomla-bruteforcePython script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
 zhairiazzeddine/exploit-cve-2023-6063-poc-vuln
Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…
 boreas37/cve-2026-43914-poc
PoC for CVE-2026-43914: Vaultwarden <1.35.4 email-2FA brute-force bypass password oracle. Stdlib-only Python.
 paradoxis/flask-unsign
Command line tool to fetch, decode, brute-force and craft session cookies of a Flask application by guessing secret keys.
 randomrobbiebf/wordpress-bf
Brute Force Wordpress Blogs.
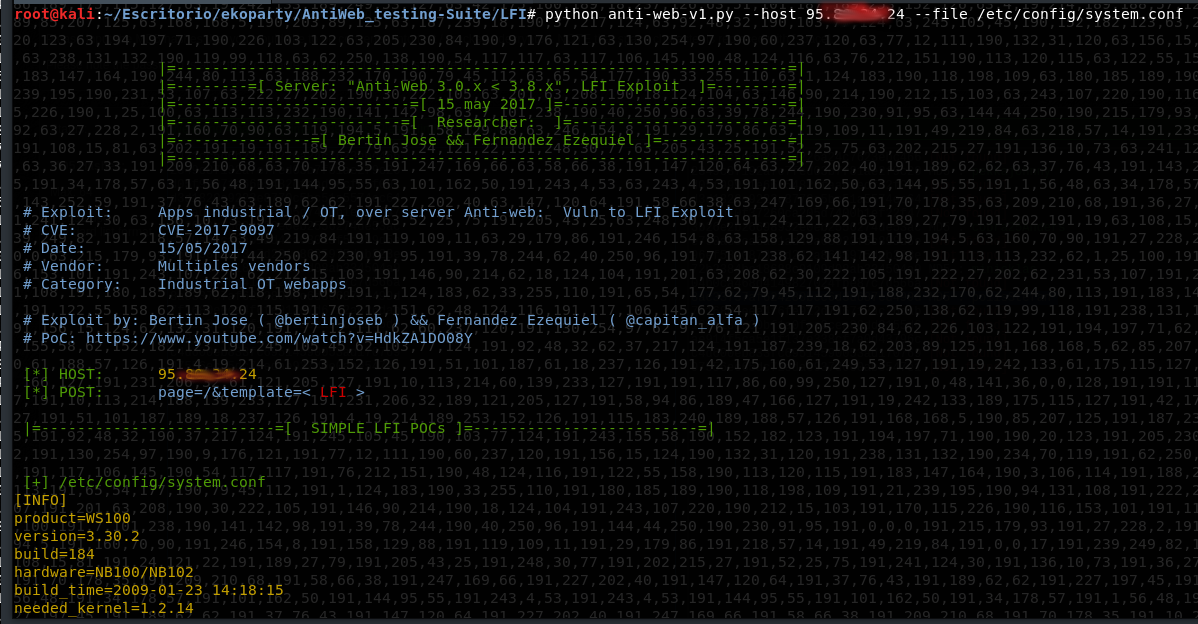 mdudek-ics/antiweb_testing-suite
Suite de herramientas que sacan partido del CVE-2017-9097 (+RCE)
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
 1n3/wordpress-xmlrpc-brute-force-exploit
Wordpress XMLRPC System Multicall Brute Force Exploit (0day) by 1N3 @ CrowdShield
 coalfire-research/doozer
Password cracking utility
 emerinohdz/facebrute
Facebook brute forcer script
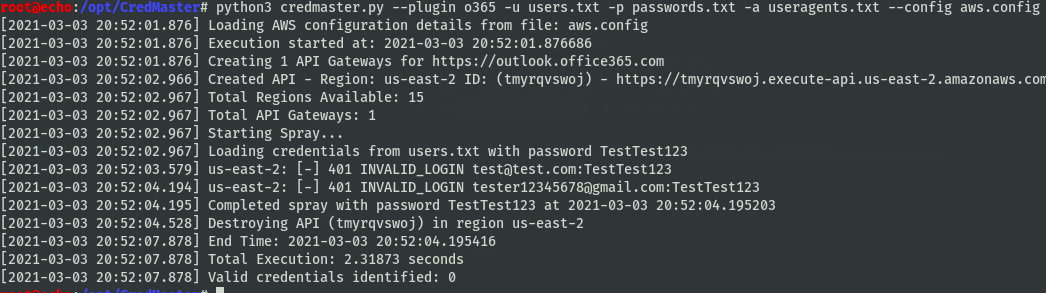 knavesec/credmaster
Refactored & improved CredKing password spraying tool, uses FireProx APIs to rotate IP addresses, stay anonymous, and beat throttling
 coldfusionx/cve-2019-17240_bludit-bf-bypass
Bludit <= 3.9.2 - Authentication Bruteforce Mitigation Bypass Exploit/PoC
 cybersecuritist/cve-2024-21754-forti-rce
Exploit for CVE-2024-21754 targeting insufficient password hashing in FortiOS and FortiProxy, enabling privileged attackers to decrypt backup files…
 fathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…
 dh4nuj4/simplectf-updatedexploit
This script is a modified version of the original exploit by Daniele Scanu which exploits an unauthenticated SQL injection vulnerability in CMS Made…