
CVE-2026-77276-PoC
 morzan6/cve-2026-77276-poc
CVE-2026-77276 pre-auth macro RCE via convert-to on Collabora Online
exploitationpenetration-testingred-teaming+2
morzan6/cve-2026-77276-pocCVE-2026-77276 pre-auth macro RCE via convert-to on Collabora Online
 theexploiters/cve-2024-27115-exploit
Exploit For SOPlanning 1.52.01 (Simple Online Planning Tool) - Remote Code Execution (RCE) (Authenticated)
 quetuan03/cve-2025-54677
WordPress Online Booking & Scheduling Calendar for WordPress by vcita Plugin <= 4.5.3 is vulnerable to a medium priority Arbitrary File Upload
 nawed20002/cve-2021-46005
Proof-of-concept for stored XSS in Online Car Rental System 1.0, demonstrating session hijacking and credential theft via the vehicalorcview…
 aaryan-11-x/cve-2024-57487-and-cve-2024-57488
Proof-of-concept and detailed writeups for CVE-2024-57487 (authenticated RCE via file upload) and CVE-2024-57488 (stored XSS) in Online Car Rental…
 xmyronn/cve-2026-7028-sqli
Proof-of-concept exploit for SQL injection in CodeAstro Online Job Portal allowing authenticated deletion of all job records via crafted GET request.
 xmyronn/cve-2026-6201-idor
Proof-of-concept demonstrating an IDOR vulnerability in CodeAstro Online Job Portal allowing authenticated employers to delete arbitrary job postings…
 nxvh1337/cve-2025-60736
code-projects Online Medicine Guide 1.0 is vulnerable to SQL Injection
 error-inside/cve-2025-10897
WooCommerce Designer Pro <= 1.9.28 - Unauthenticated Arbitrary File Read
 1337-l3v1ath0n/exploit_development
Learning Exploit Development for Web. POCs for CVEs which was assigned to me.
 jonathanrey87/cve-2020-25273
Online Bus Booking System 1.0, there is Authentication bypass on the Admin Login screen in admin.php via username or password SQL injection.
 bootstrapbool/xerteonlinetoolkits-rce
Unauthenticated Xerte Online Toolkits exploit. Requires knowing a valid username.
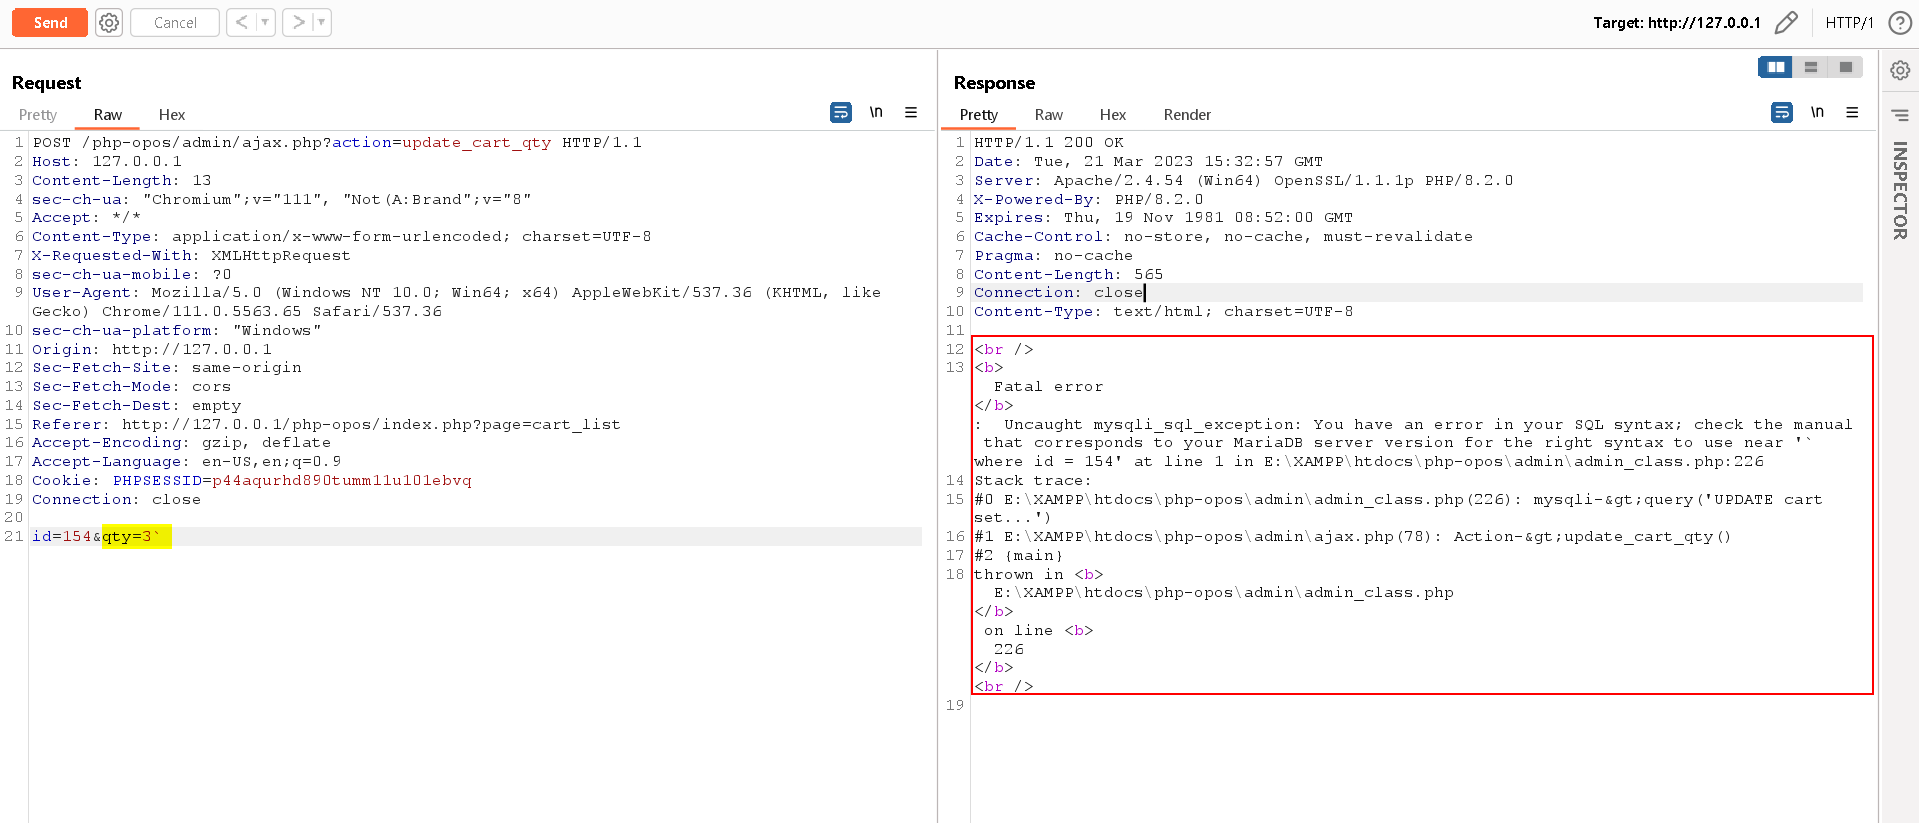 nawed20002/cve-2023-30092
Proof-of-concept exploit for SQL injection in Sourcecodester Online Pizza Ordering System 1.0. Demonstrates remote code execution and denial of…
 p0et08/dwrwq
This is a EXP For CVE-2025-57576. PHPGurukul Online Shopping Portal 2.1 is vulnerable to Cross Site > Scripting (XSS) in /admin/updateorder.php
 yasinyilmaz/vuln-chm-hijack
Potential malicious code execution via CHM hijacking (CVE-2019-9896)
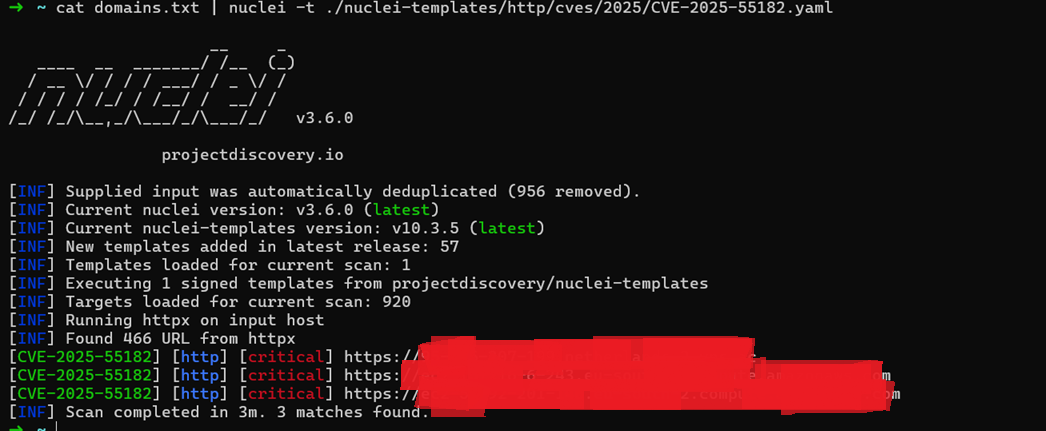 jaycelation/cve-2025-55182
PoC, Hunting React2Shell about CVE-2025-55182