

SafeLine
 chaitin/safeline
Self-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
anti-botapi-securityapi-security-testing+8
22.6k
chaitin/safelineSelf-hosted WAF and reverse proxy that filters malicious HTTP traffic, blocks SQL injection, XSS, and bot attacks, with rate limiting and dynamic…
 funnywolf/pystinger
Bypass firewall for traffic forwarding using webshell
 bishopfox/h2csmuggler
HTTP Request Smuggling over HTTP/2 Cleartext (h2c)
 sumitpathania03/log4j-cve-2021-44228
Proof-of-concept for Log4Shell (CVE-2021-44228) demonstrating remote code execution via JNDI injection, including vulnerable server setup, exploit…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 magentabear/cve-2019-11043-vulnerability
Hands-on lab reproducing CVE-2019-11043 PHP-FPM RCE behind nginx, demonstrating reverse-tunnel persistence, memory forensics, and network traffic…
 benrich127n/react2shell_analyzer
a dart package to analyze CVE-2025-55182 react2shell
 husam212/mitmer
Automated man-in-the-middle attack tool.
 d3n14ld15k/cve-2024-7593_poc_exploit
CVE-2024-7593 Ivanti Virtual Traffic Manager 22.2R1 / 22.7R2 Admin Panel Authentication Bypass PoC [EXPLOIT]
 zwclose/cve-2021-26258
Files and tools for CVE-2021-26258
 murataydemir/cve-2020-5902
[CVE-2020-5902] F5 BIG-IP Remote Code Execution (RCE)
 imbas007/cve-2025-53770-vulnerable-scanner
Python script to scan SharePoint hosts for CVE-2025-53770 using custom payloads, with optional Burp Suite proxy interception for traffic analysis and…
 yassineaboukir/cve-2020-5902
Proof of concept for CVE-2020-5902
 nsflabs/cve-2020-5902
Python scanner to detect CVE-2020-5902 RCE vulnerability in F5 BIG-IP TMUI. Tests unauthenticated remote systems for arbitrary command execution via…
 rwincey/cve-2020-5902-nse
Nmap NSE script for detecting and exploiting CVE-2020-5902, a remote code execution vulnerability in F5 BIG-IP traffic management user interface.
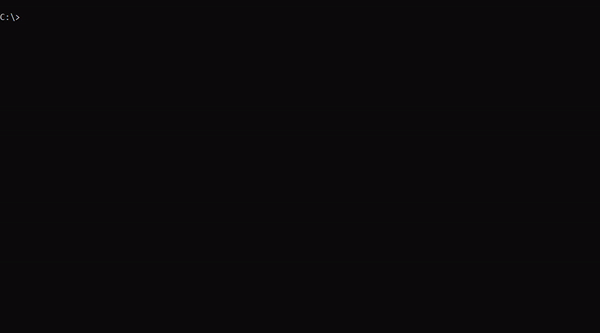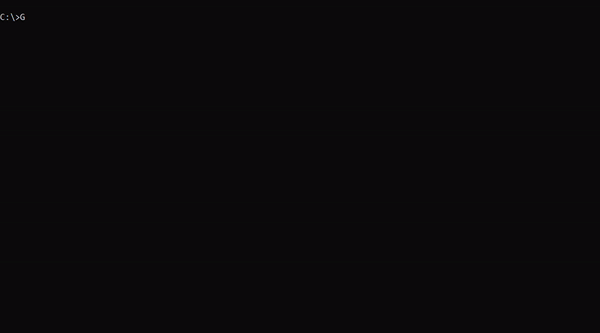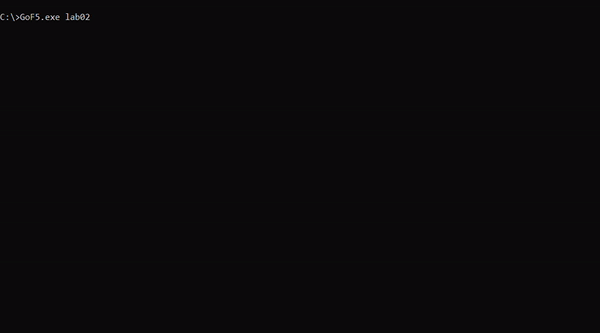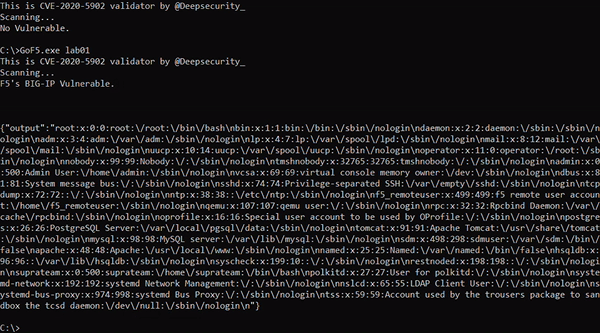 deepsecurity-pe/gof5-cve-2020-5902
Script para validar CVE-2020-5902 hecho en Go.
 0xblackash/cve-2020-5902
CVE-2020-5902
 boreas37/cve-2026-33267-poc
CVE-2026-33267 — Apache Traffic Server @ header internal-metadata spoof (CVSS 10.0). Verified: @ headers leak to plugins on 10.1.2, stripped on 10.1.4