CVE-2018-12633-TPLink-Auth-Bypass

A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).

A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).

TP-Link TL-WR1043ND - Authenticated Remote Code Execution

PoC exploit chain for TP-Link Tapo C260 camera — CVE-2026-0651/0652/0653. Research by @spaceraccoon.

CVE-2023-33538 - TP-Link Command Injection Ruby module for Metasploit Framework

Provides a detailed analysis and proof-of-concept for CVE-2026-1457, an authenticated buffer overflow in TP-Link VIGI C385 web API leading to remote…

Exploiting TP-Link Archer CR-700 Router. (Responsibly Disclosed to TP-Link)

Proof-of-concept exploit for TP-Link TDDP authentication bypass (CVE-2026-0834) that sends crafted packets to execute administrative commands like…

CVE-2018-19537

Proof-of-concept exploits for TP-Link routers, including remote command execution and authentication bypass vulnerabilities.

TP-Link Router Authenticated RCE Exploit (CVE-2022-30075) Bu araç, TP-Link Archer AX50 ve bazı diğer TP-Link router modellerinde bulunan…

Proof-of-concept exploit for authenticated OS command injection in TP-Link Archer C20 v6 web management interface, executing root commands via BPA…

Tp-Link Archer AX50 Authenticated RCE (CVE-2022-30075)

Proof of Concept for the CVE-2026-22226

Weaponized exploit script for CVE-2020-35575, a password-disclosure vulnerability in TP-Link router web interfaces, granting remote administrative…

TP-Link Tapo c200 ver <1.1.15 - Remote Code Execution (RCE)

TypeScript PoC for CVE-2024-54887 (TP-Link TL-WR940N authenticated RCE)

TP-Link Archer AXE75 Authenticated Command Injection

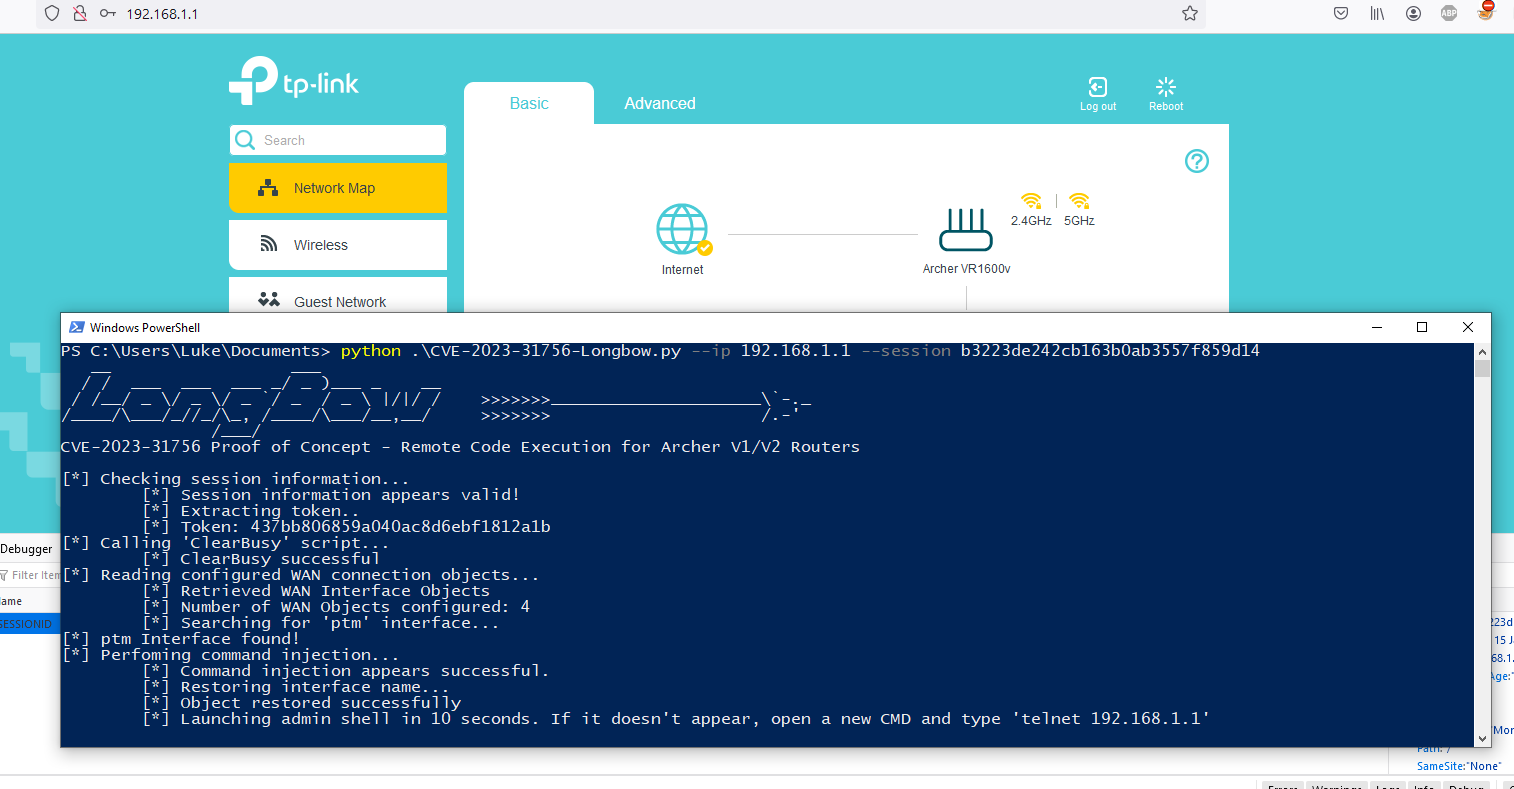
CVE-2023-31756 Proof of Concept - Remote Code Execution for Archer V1/V2 Routers