

strix
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
ai-securityapi-security-testingcode-analysis+9
usestrix/strixOpen-source AI penetration testing tool to find and fix your app’s vulnerabilities.

 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 seanrickerd/cve-2024-53677
Vulnerable Environment and Exploit for CVE-2024-53677
 snailsploit/claude-red
Curated library of 78 offensive security SKILL.md modules that prime Claude with expert red team methodology across web, AD, wireless, cloud, and…
 bugbasesecurity/pentest-copilot
AI-driven penetration testing agent that connects to a Kali box, autonomously runs security tools, analyzes results, and iterates through…
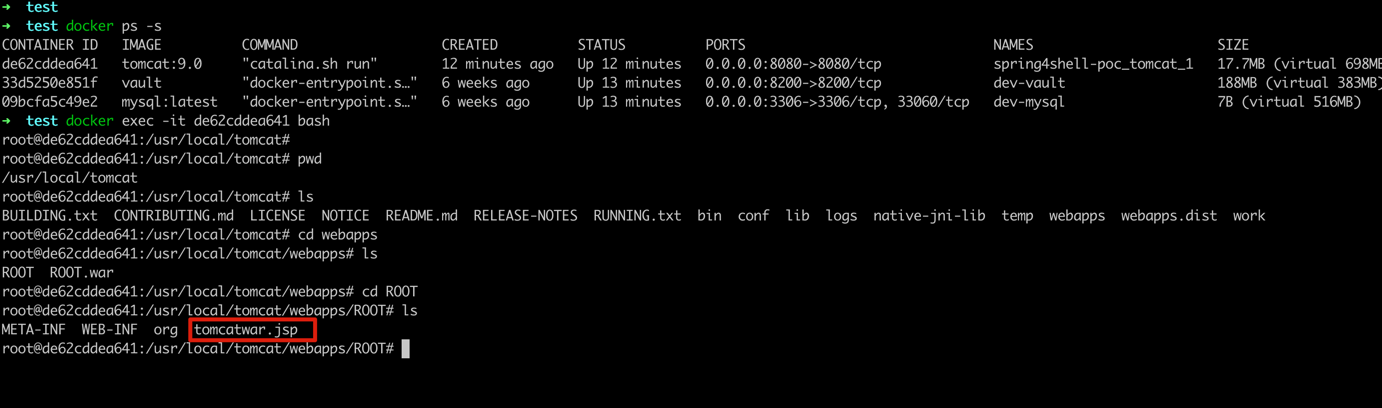 weijilab/spring4shell-poc
Reproduces the Spring4Shell (CVE-2022-22965) remote code execution vulnerability with a Python exploit script, deploying a JSP webshell on Apache…
 nabhan-mohy/cve-2026-27483-lab
A containerized enterprise-style lab for researching and defending against CVE-2026-27483.
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 dnr6419/cve-2021-24145
WordPress File Upload Vulnerability, Modern Events Calendar Lite WordPress plugin before 5.16.5
 jrrdev/cve-2017-5638
Docker-based vulnerable environment and Python exploit script demonstrating CVE-2017-5638 (Apache Struts2 RCE) for educational security testing.
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 abhinavagarwal07/mirth-connect-security-poc
Working PoCs for three NextGen Connect 4.5.2 vulnerabilities.
 alihzsec/cve-2024-28000
Hands-on exploit lab for CVE-2024-28000 — unauthenticated privilege escalation in LiteSpeed Cache (WordPress plugin, <=6.3.0.1). Spins up a…
 laliea/cve-2021-46398
A Proof of Concept for the CVE-2021-46398 flaw exploitation
 zer0sumgam3/cve-2026-66066-poc
PoC for CVE-2026-66066 in Ruby on Rails
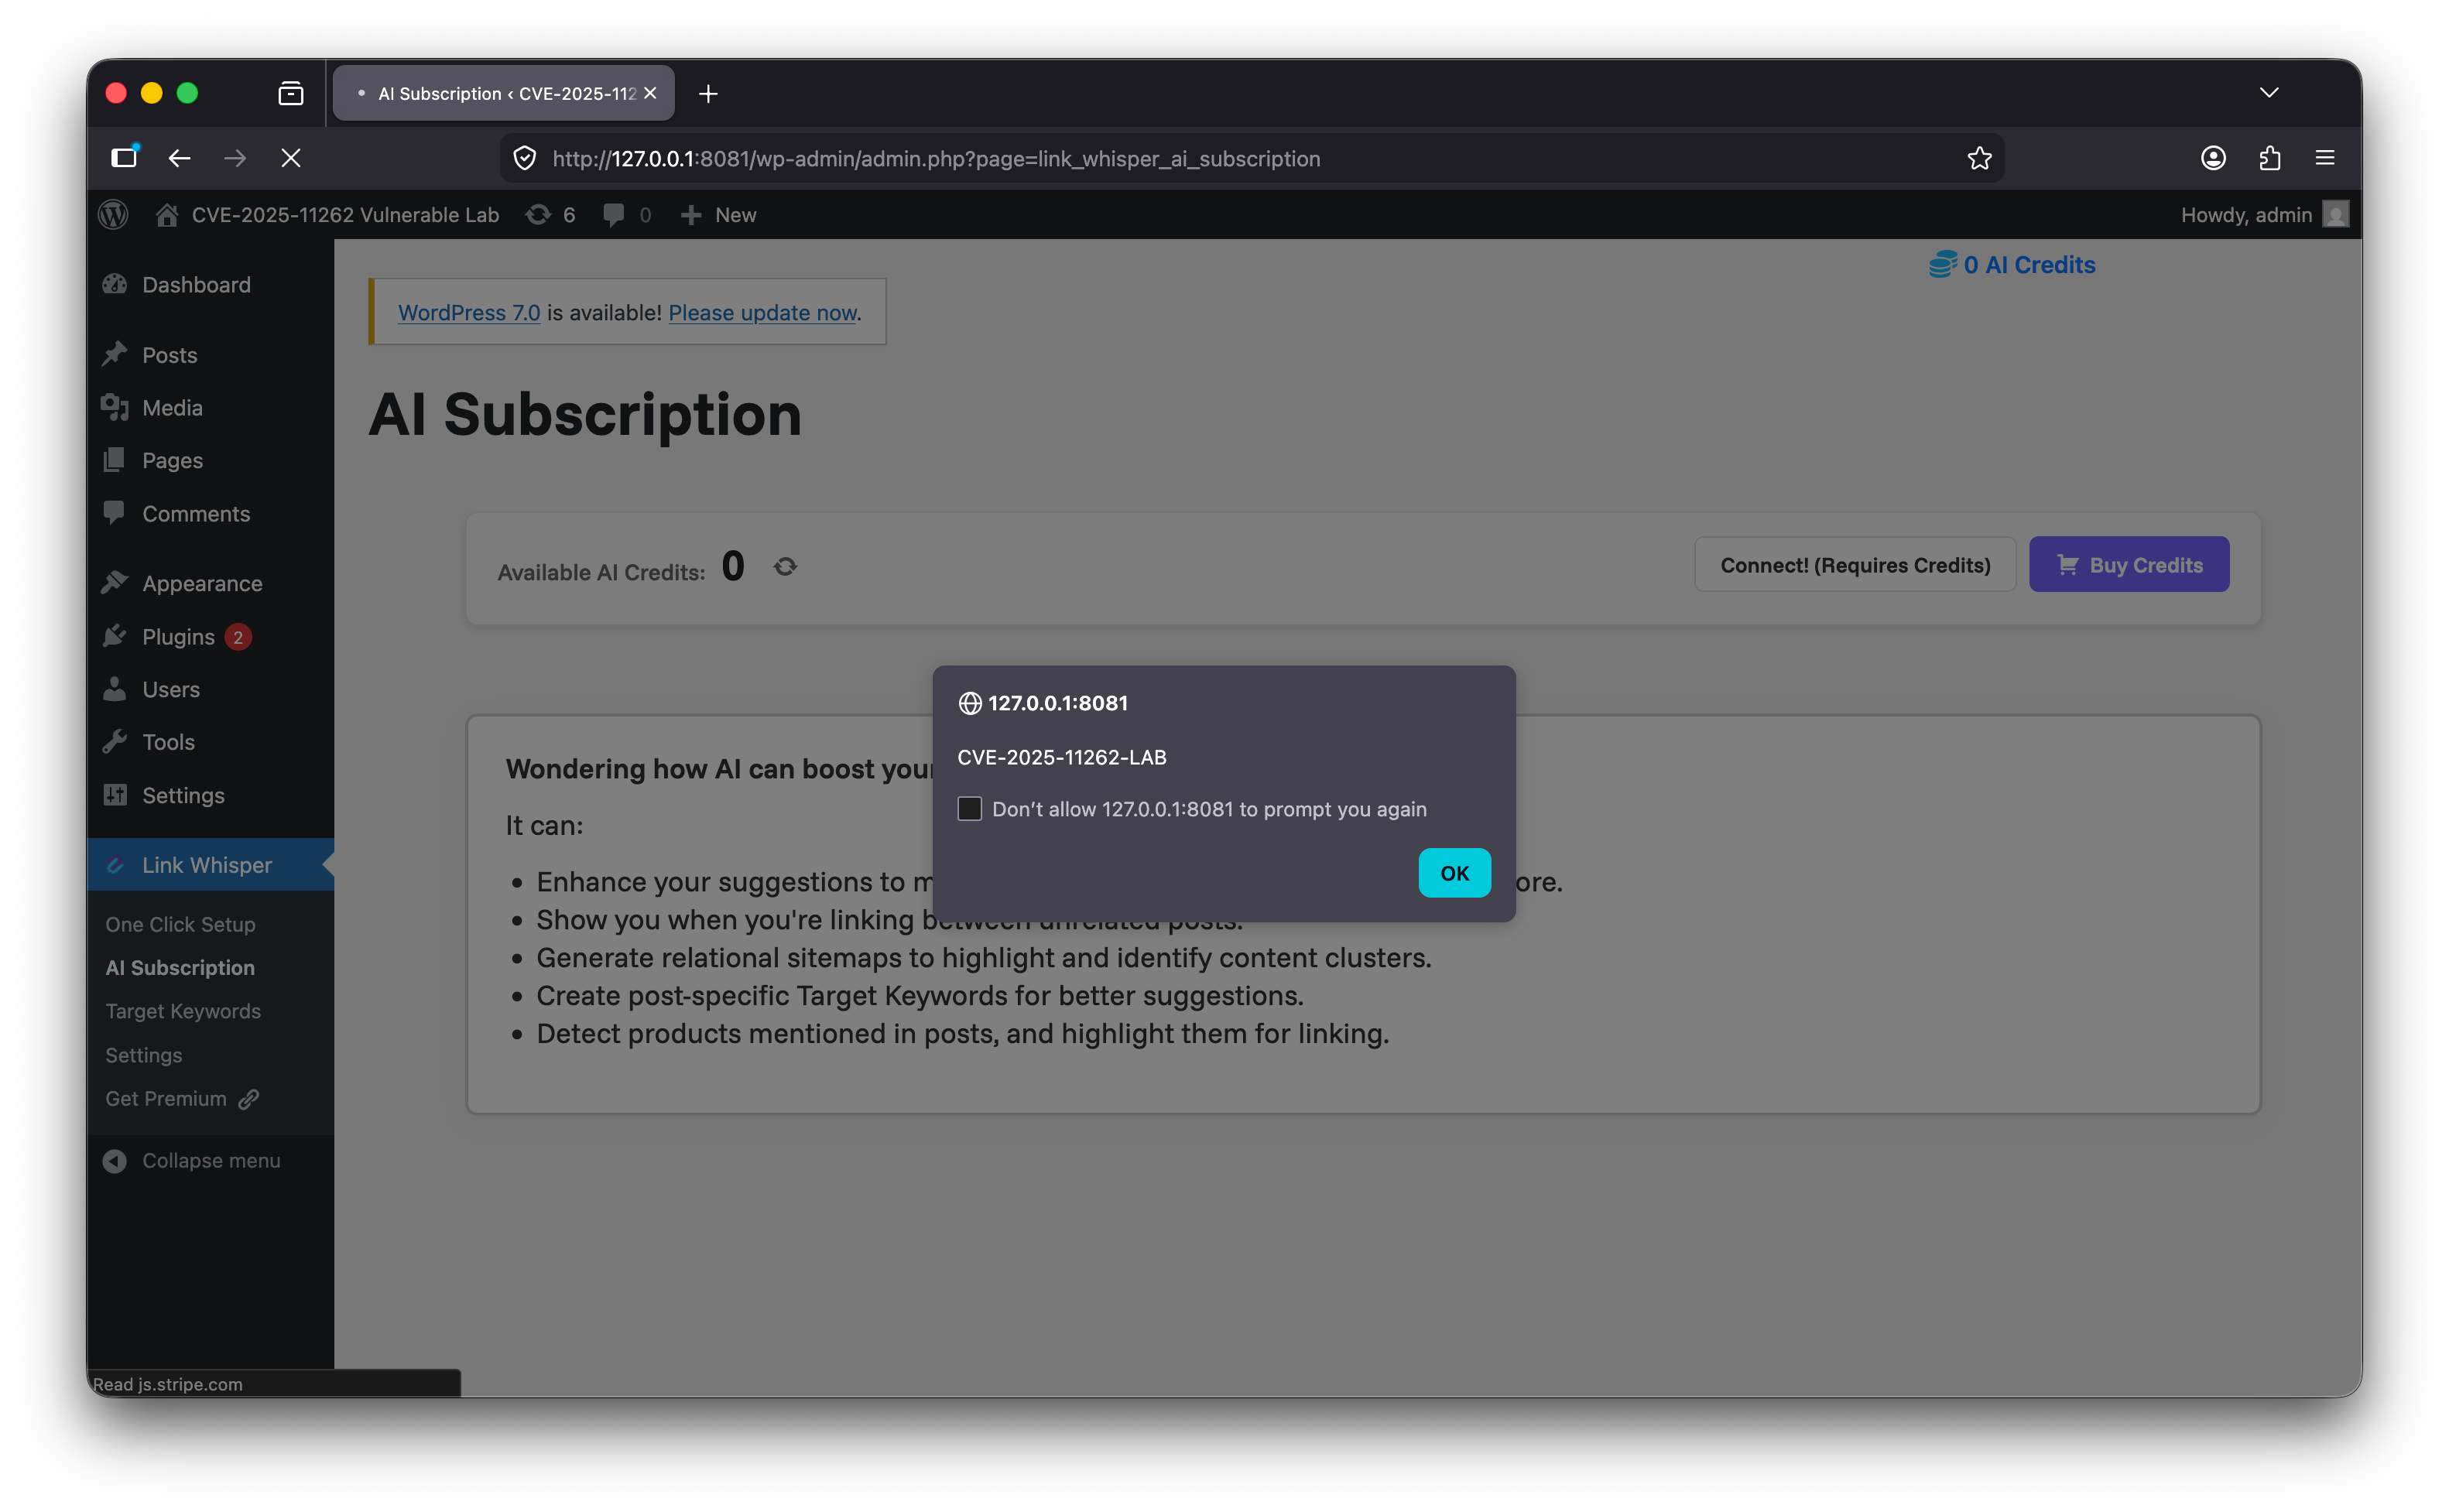 rootdirective-sec/cve-2025-11262-lab
Docker lab for reproducing CVE-2025-11262, an unauthenticated stored blind XSS in Link Whisper Free WordPress plugin. Includes vulnerable and patched…