
CVE-2026-66066-POC
 zer0sumgam3/cve-2026-66066-poc
PoC for CVE-2026-66066 in Ruby on Rails
educationexploitationlabs-practice+3
232 months ago
zer0sumgam3/cve-2026-66066-pocPoC for CVE-2026-66066 in Ruby on Rails
 0x00-0x00/cve-2015-3224
Modification of Metasploit module for RCE in Ruby-On-Rails Console CVE-2015-3224
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…
 3rg1s/cve-2016-2098
Proof-of-concept exploit for CVE-2016-2098, demonstrating remote Ruby code execution through Rails render method abuse; intended for security testing…
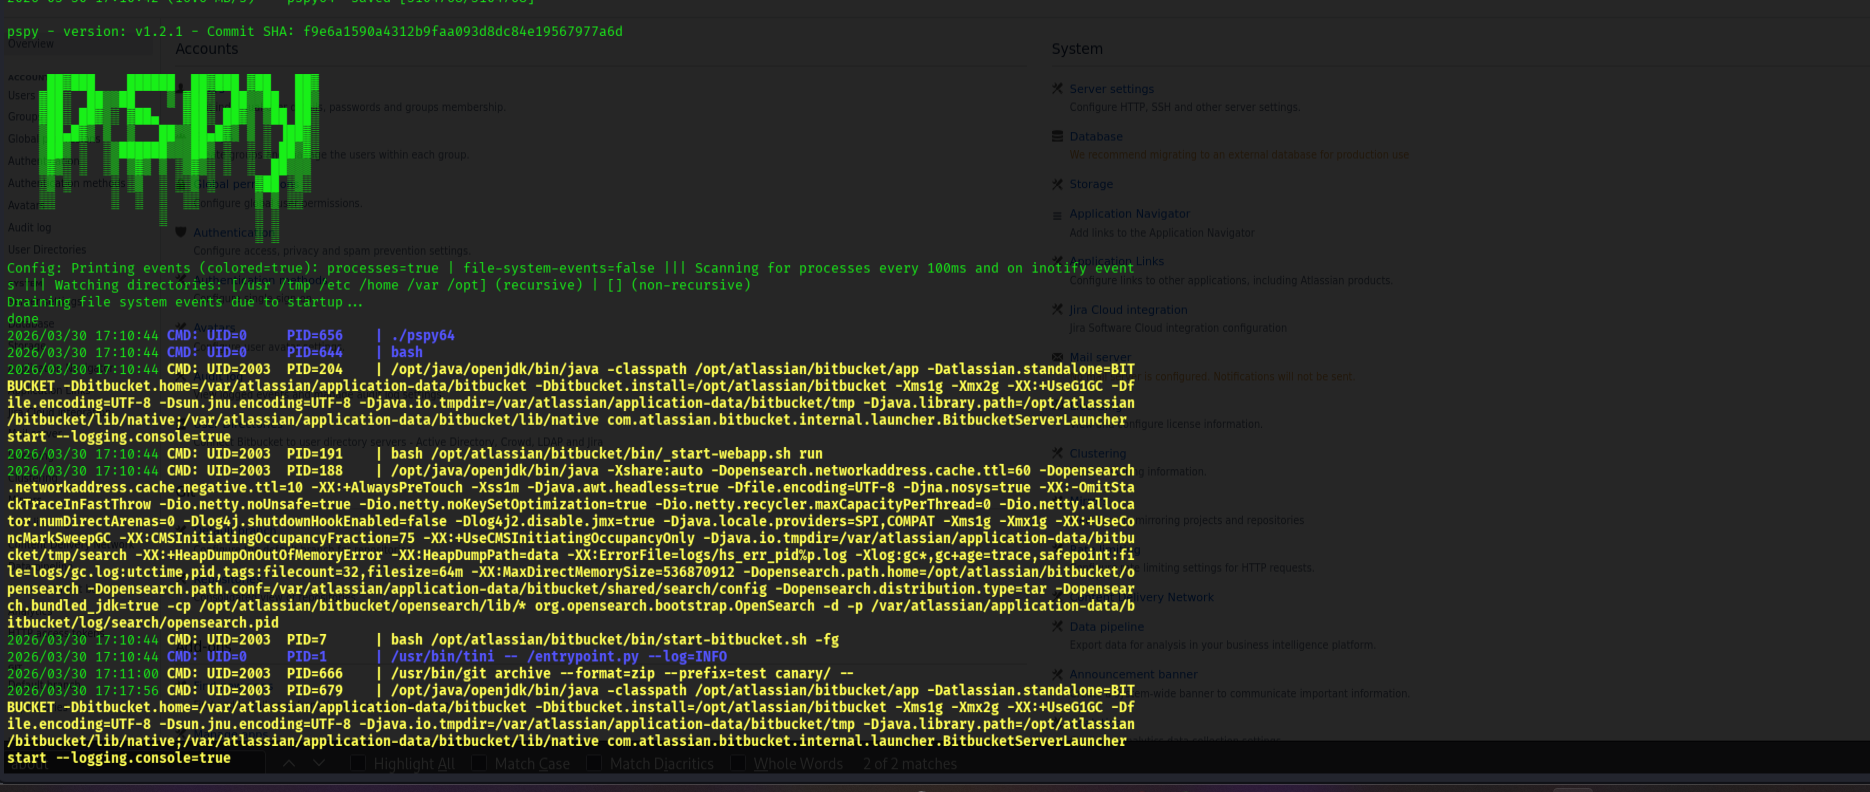 johangabrielson/bitbucket-test
Investigating CVE-2022-36804
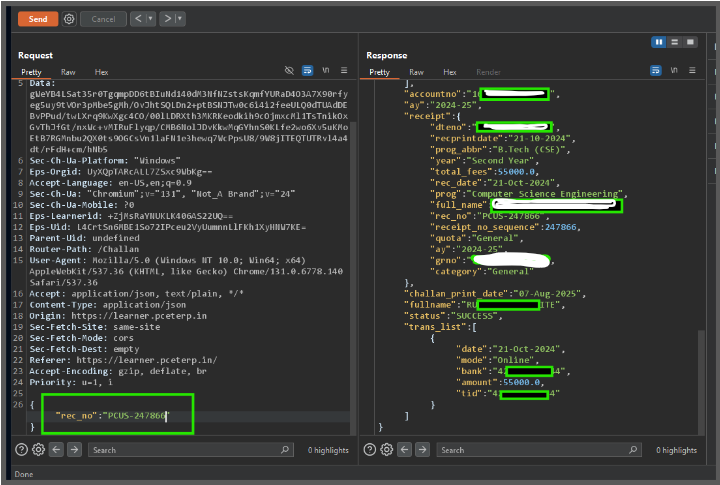 sharma19d/cve-2025-61148
The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…
 hackspeak/cve-2026-66066
CVE-2026-66066 (KindaRails2Shell) PoC - Rails Active Storage/libvips arbitrary file read to RCE; for authorized security testing
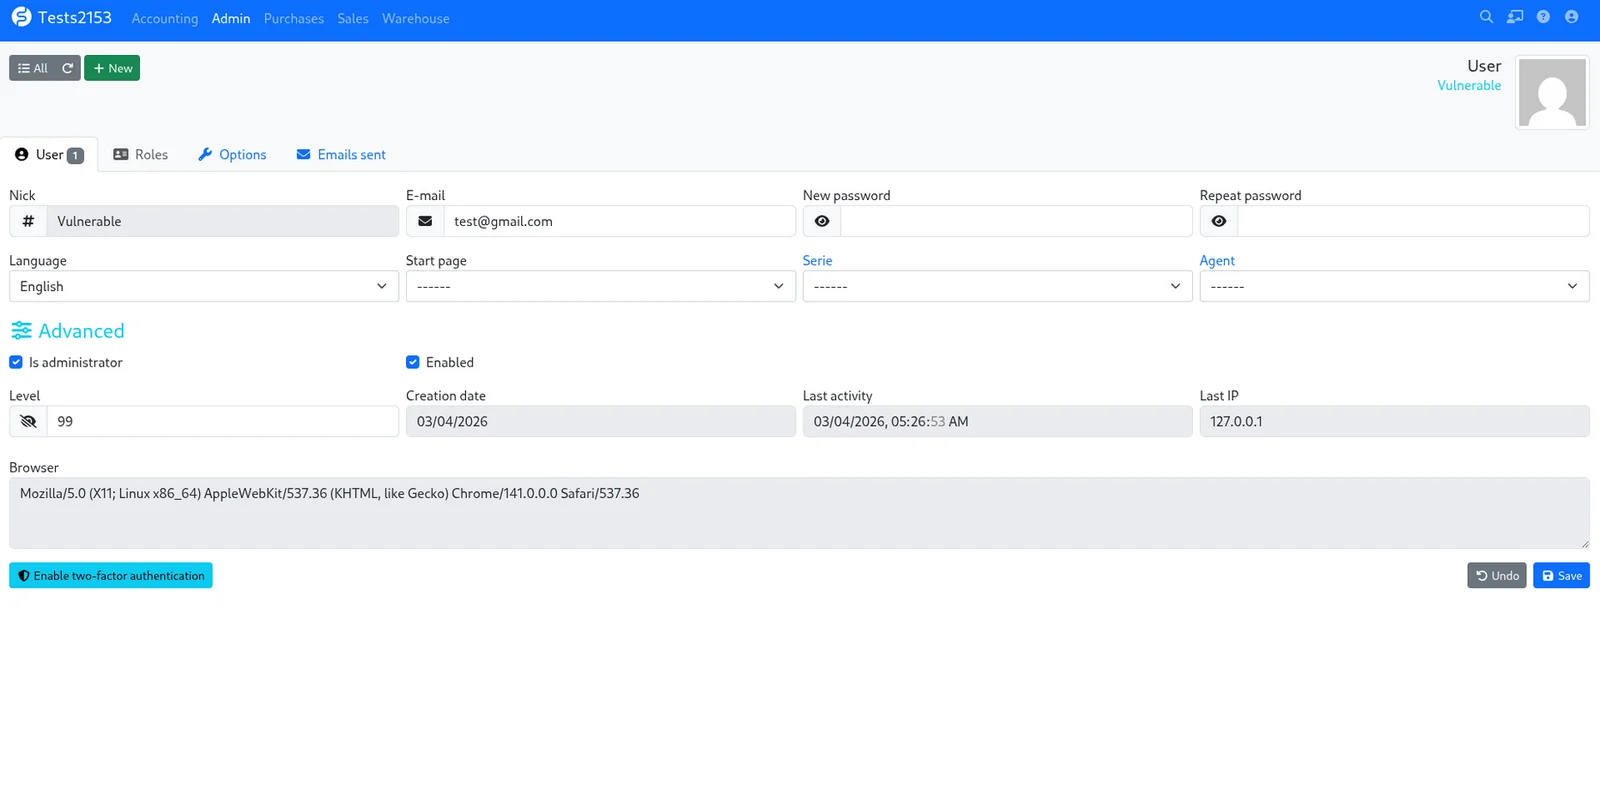 turkios/cve-2026-32699-facturascripts-nick-bypass
Broken Access Control in FacturaScripts EditUser controller allows authenticated users to rename any account (including admin) by modifying the…
 its-arun/cve-2016-2098
Bash-based proof-of-concept exploit for CVE-2016-2098, targeting Ruby on Rails Action Pack remote code execution via unrestricted render method.
 simoesctt/sctt-2026-33-0004-forticloud-sso-identity-singularity
While Fortinet's January 27, 2026 mitigation for **CVE-2026-24858** focuses on blocking specific accounts like `[email protected]`, it fails to…
 debalinax64/cve-2016-2098
CVE-2016-2098 - POC of RCE Ruby on Rails: Improper Input Validation (CVE-2016-2098) in bash. Remote attackers can execute arbitrary Ruby code by…
 forced-request/rails-rce-cve-2016-0752
Proof-of-concept exploit for CVE-2016-0752, a remote code execution vulnerability in Ruby on Rails via dynamic render paths. Includes vulnerable app,…
 bombobombone/cve-2026-73314
Proof-of-concept exploit for CVE-2026-73314, a PayPal REST webhook signature verification bypass in XenForo before 2.3.13, allowing unauthorized…
 eremiel/cve-2019-5420
Python exploit script for CVE-2019-5420, targeting Ruby on Rails signed-session AES GCM key brute-forcing to achieve remote code execution in…
 oscerd/cve-2026-53913
PoC reproducer for CVE-2026-53913 (Apache Camel camel-keycloak): KeycloakSecurityPolicy fails open in the Basic Setup — with no required…
 dhmosfunk/http3onsteroids
PoC and lab environment for CVE-2023-25950: HTTP request smuggling via malformed header fields in HAProxy's HTTP/3 implementation, enabling DoS and…
 hybryx/cve-2020-8165
Python exploit for CVE-2020-8165 targeting Rails MemCacheStore and RedisCacheStore. Enables remote command execution via user-provided object…
 theopaid/cve-2026-67184-unauthenticated-null-pointer-dereference-crashes-the-server-tinyweb-
Security Advisory: Unauthenticated NULL Pointer Dereference Crashes the Server (TinyWeb)