

nuclei
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
anti-botapi-securityapi-security-testing+21
32.4k
projectdiscovery/nucleiFast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 botesjuan/burp-suite-certified-practitioner-exam-study
Practical study notes and walkthroughs for PortSwigger Academy labs, covering web vulnerabilities, payloads, enumeration, and BSCP exam strategies.
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 swisskyrepo/payloadsallthethings
A list of useful payloads and bypass for Web Application Security and Pentest/CTF
 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 zaproxy/zaproxy
Open-source web application security scanner for automated vulnerability detection, manual penetration testing, and API security testing with a…
 osyanina/westone-cve-2020-14883-scanner
A vulnerability scanner that detects CVE-2020-14883 vulnerabilities.
 xaanziu/cve-2026-5513
CVE-2026-5513: Bookly <= 27.2 Stored XSS via Cookie (Unauthenticated)
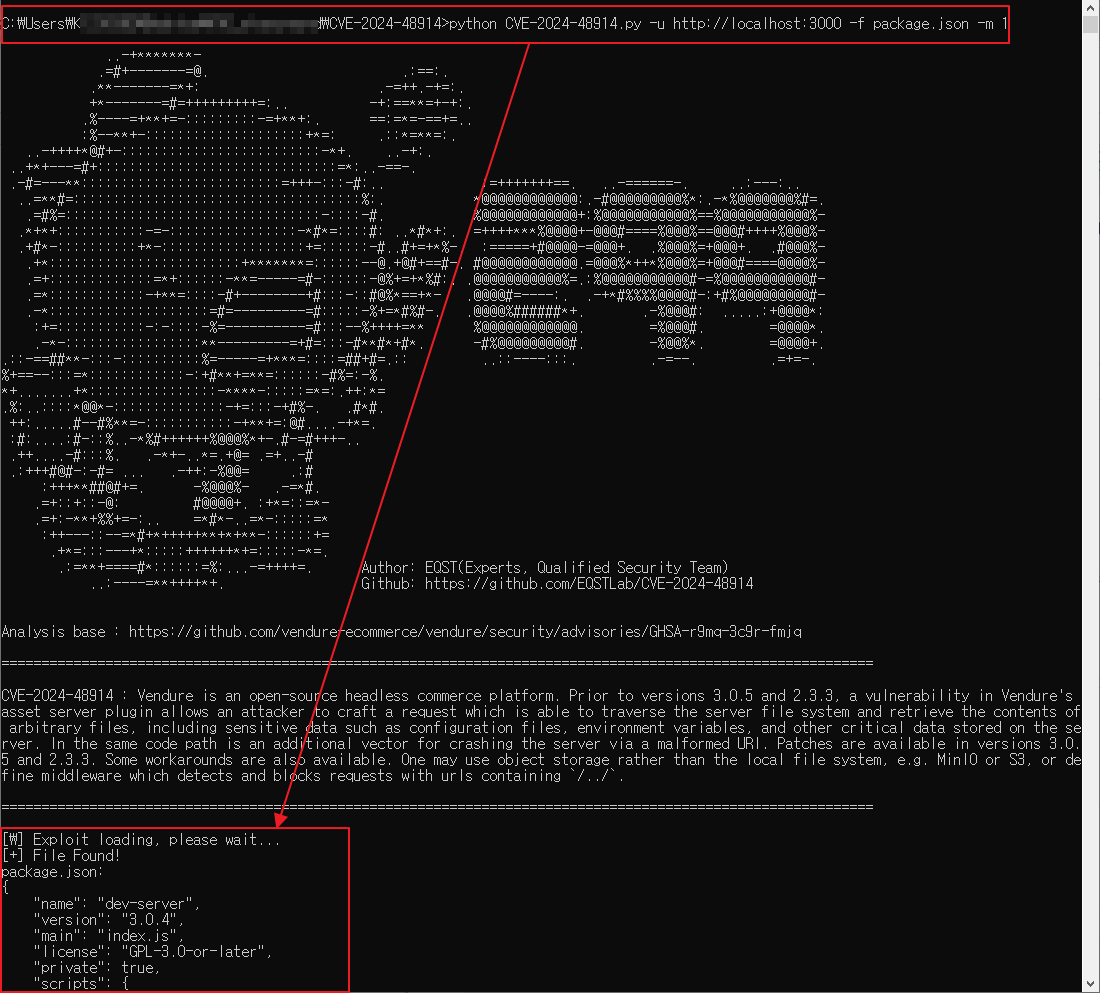 eqstlab/cve-2024-48914
Arbitrary File Read and DoS in vendure-ecommerce exploit
 osyanina/westone-cve-2021-21980-scanner
A vulnerability scanner that detects CVE-2021-21980 vulnerabilities.
 caybermods/cve-2026-22812-poc
Python tool to check and exploit CVE-2026-22812 in OpenCode, supporting command execution, file read, and multi-target scanning on ports 4095-4100.
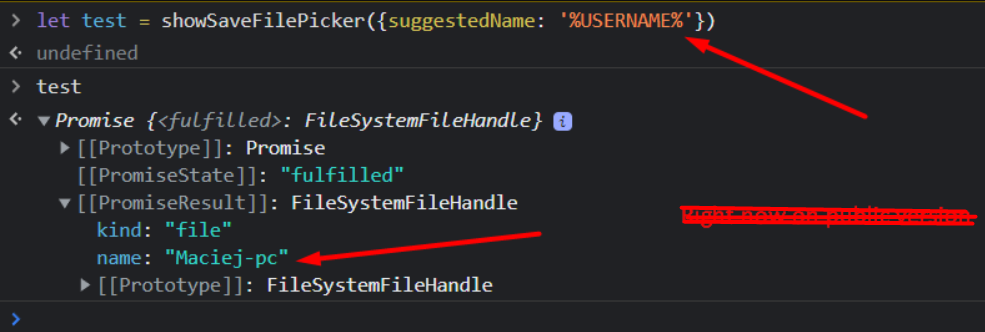 puliczek/cve-2022-0337-poc-google-chrome-microsoft-edge-opera
🎩 🤟🏻 [P1-$10,000] Google Chrome, Microsoft Edge and Opera - vulnerability reported by Maciej Pulikowski - System environment variables leak -…
 a0yami/cve-2025-50505
Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
 rafabd1/vectorfreed
Documents the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
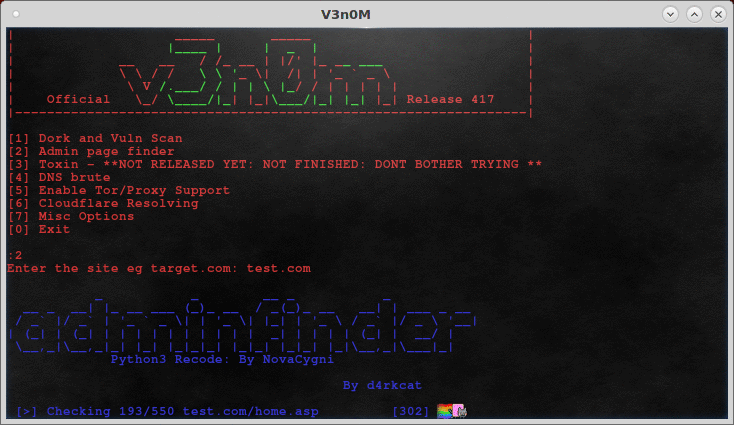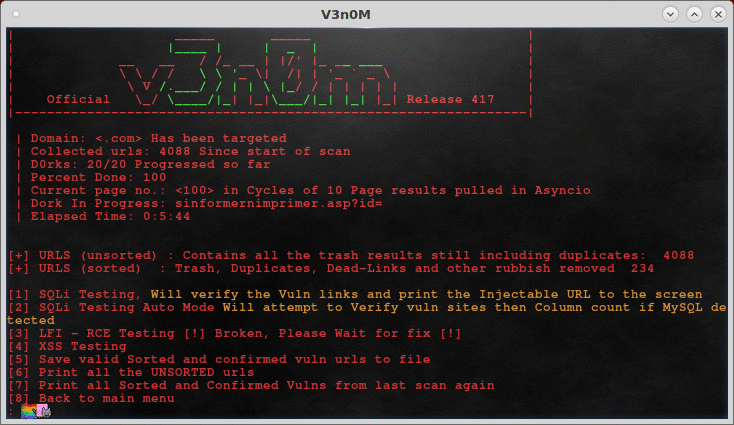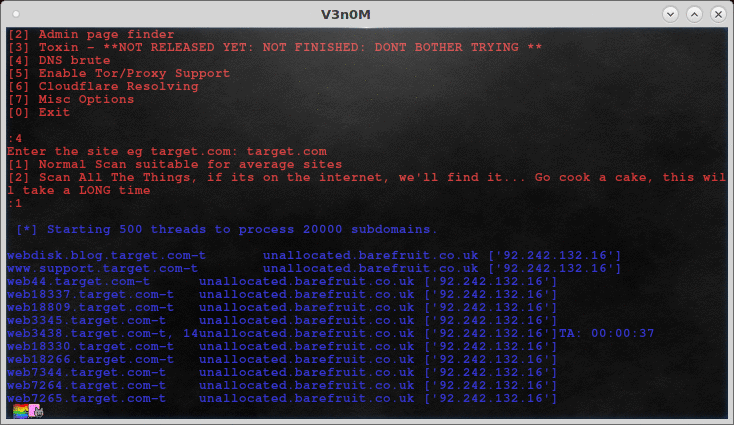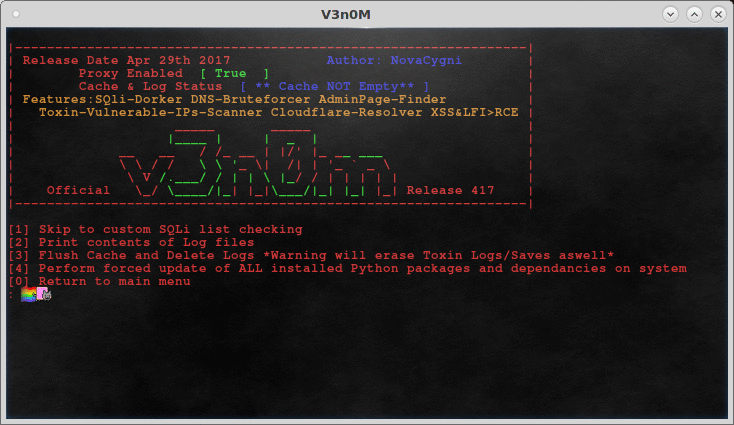 v3n0m-scanner/v3n0m-scanner
Popular Pentesting scanner in Python3.6 for SQLi/XSS/LFI/RFI and other Vulns
 exfil0/cve-2024-55591-poc
A comprehensive all-in-one Python-based Proof of Concept script to discover and exploit a critical authentication bypass vulnerability…
 xthalach/cve-2024-11318
This repository details an IDOR vulnerability in AbsysNet 2.3.1, which allows a remote attacker to brute-force session IDs via the /cgi-bin/ocap/…