cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

Automatic SSTI detection tool with interactive interface

Vulnerable Environment and Exploit for CVE-2024-53677


XWiki 15.10.11, 16.4.1 and 16.5.0RC1 Unauthenticated Remote code execution POC

Next generation web scanner


WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…

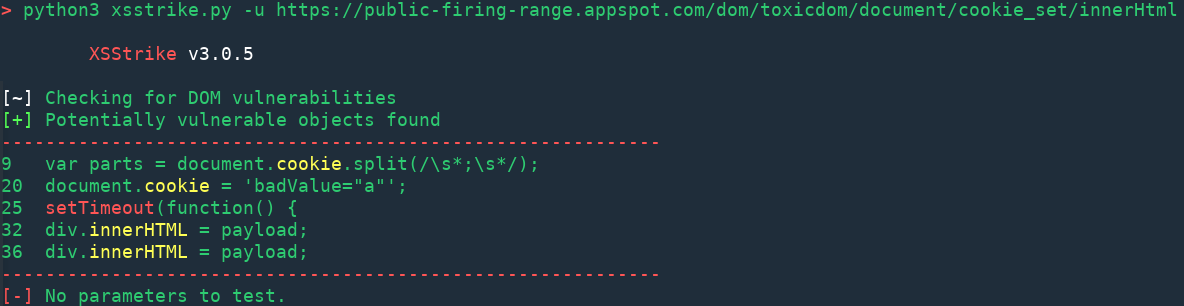
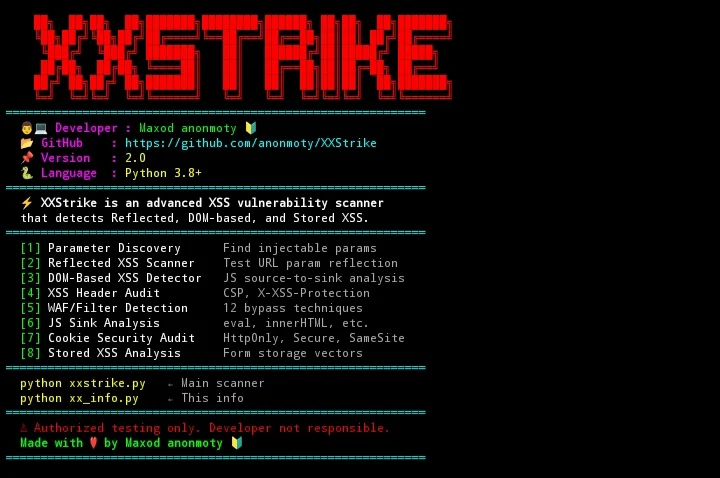
Fast XSS scanner with parameter analysis, WAF fingerprinting, and DOM/AST verification. Supports reflected, stored, and DOM-based XSS detection via…

XSStrike based XSS scanner with custom features. Detects XSS vulnerabilities in web applications.

Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…

A wrapper around grep, to help you grep for things

A collection of useful resources for hacking WordPress and it's plugins and themes

TInjA is a CLI tool for testing web pages for template injection vulnerabilities and supports 44 of the most relevant template engines for eight…

Generates five .NET deserialization payload formats for CVE-2026-56158, delivers them over HTTP/SOAP/JSON endpoints, includes mock server, scanner,…

Proof-of-concept reproducers for Apache Camel path traversal vulnerability (CVE-2026-60093) in camel-azure-storage-datalake, demonstrating arbitrary…

Unified Security Research Tool

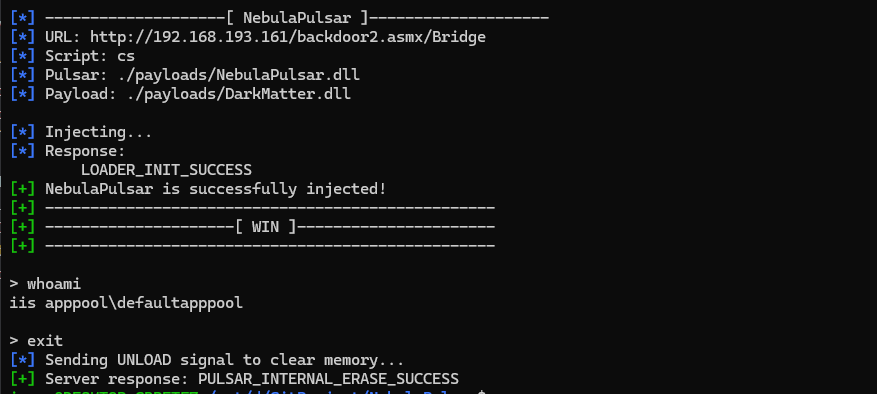
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…