
AllHackingTools
 mishakorzik/allhackingtools
All-in-One Hacking Tools For Hackers! And more hacking tools! For termux.
crawlerexploitationhash-analysis+8
6.4k1 month ago
mishakorzik/allhackingtoolsAll-in-One Hacking Tools For Hackers! And more hacking tools! For termux.
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 tegal1337/pocketpentester
Offline-first Android offensive security toolkit with 21 modules for recon, port scanning, subdomain enumeration, SQLi/XSS/JWT exploitation, payload…
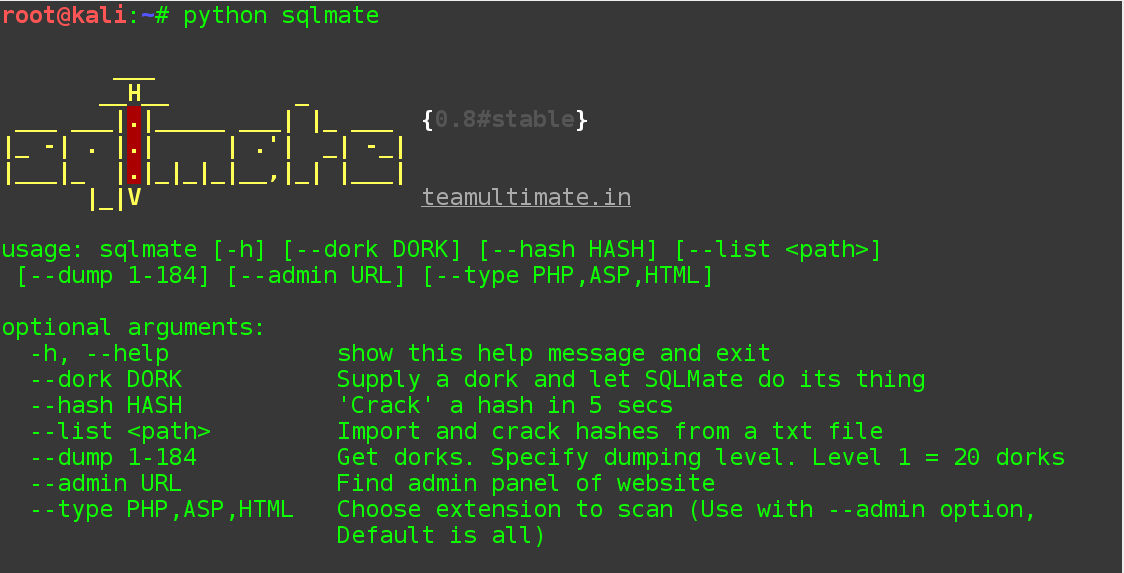 s0md3v/sqlmate
A friend of SQLmap which will do what you always expected from SQLmap.
 alihzsec/cve-2024-28000
Hands-on exploit lab for CVE-2024-28000 — unauthenticated privilege escalation in LiteSpeed Cache (WordPress plugin, <=6.3.0.1). Spins up a…
 jeanback1/cve-2019-9053-exploit
Automated exploit for CVE-2019-9053, a time-based blind SQL injection in CMS Made Simple ≤2.2.9. Extracts admin credentials (username, email,…
 chinesespeople/cve-2026-52614
There is a SQL injection vulnerability in the backend of Ruoyi v4.8.3
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 tghook/cve-2024-4295-poc
CVE-2024-4295 Email Subscribers by Icegram Express <= 5.7.20 - Unauthenticated SQL Injection via hash
 okymi-x/cve-2021-43798
Python toolkit for authorized testing of CVE-2021-43798 Grafana path traversal, with arbitrary file read PoC, secret decryption, and user hash export…
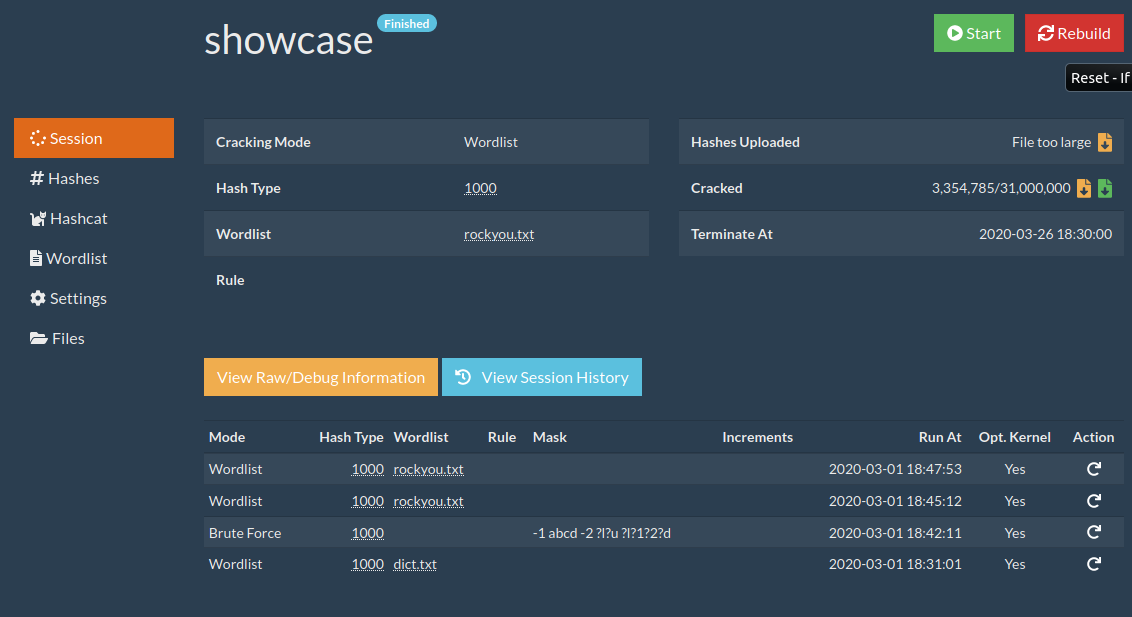 ctxis/crackerjack
CrackerJack / Hashcat Web Interface / Context Information Security
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
 jbaines-r7/hook
Proof of Concept for WatchGuard Authenticated Arbitrary File Read (CVE-2022-31749)
 fin3ss3g0d/cve-2024-4956
Python utility for automating CVE-2024-4956 path traversal exploitation with mass file extraction, plus custom Hashcat module for cracking Apache…
 zzz66686/cve-2017-14262
Exploit for CVE-2017-14262 targeting Samsung NVR devices: extracts admin MD5 password hash via unauthenticated CGI request and logs in with the hash…
 valencenavy/isolatedanarchy-public
Proof-of-concept exploit for CVE-2026-87492, a Chromium site isolation bypass using a patched renderer and MojoJS to demonstrate cross-origin data…
 coalfire-research/doozer
Password cracking utility
 zhairiazzeddine/exploit-cve-2023-6063-poc-vuln
Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…