

wpscan
 wpscanteam/wpscan
WordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
crawlerdynamic-code-analysisinformation-gathering+7
9.8k
wpscanteam/wpscanWordPress security scanner that detects vulnerabilities, enumerates plugins/themes/users, and checks for weak passwords. Integrates with the WPScan…
 bypazs/cve-2023-26984
An issue in the password reset function of Peppermint v0.2.4 allows attackers to access the emails and passwords of the Tickets page via a crafted…
 emerinohdz/facebrute
Facebook brute forcer script
 jas502n/grafana-cve-2021-43798
Grafana Unauthorized arbitrary file reading vulnerability
 iqbalx7/wp2shell
unauthenticated RCE in WordPress core (CVE-2026-63030 + CVE-2026-60137)
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
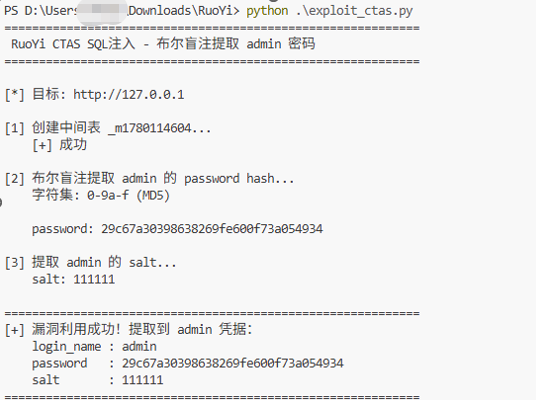 chinesespeople/cve-2026-52614
There is a SQL injection vulnerability in the backend of Ruoyi v4.8.3
 unpredictable21/halo-cors-csrf-cve-2026-67921
Proof-of-concept demonstrating a combined CORS misconfiguration and CSRF protection bypass in Halo CMS, enabling cross-site request forgery attacks…
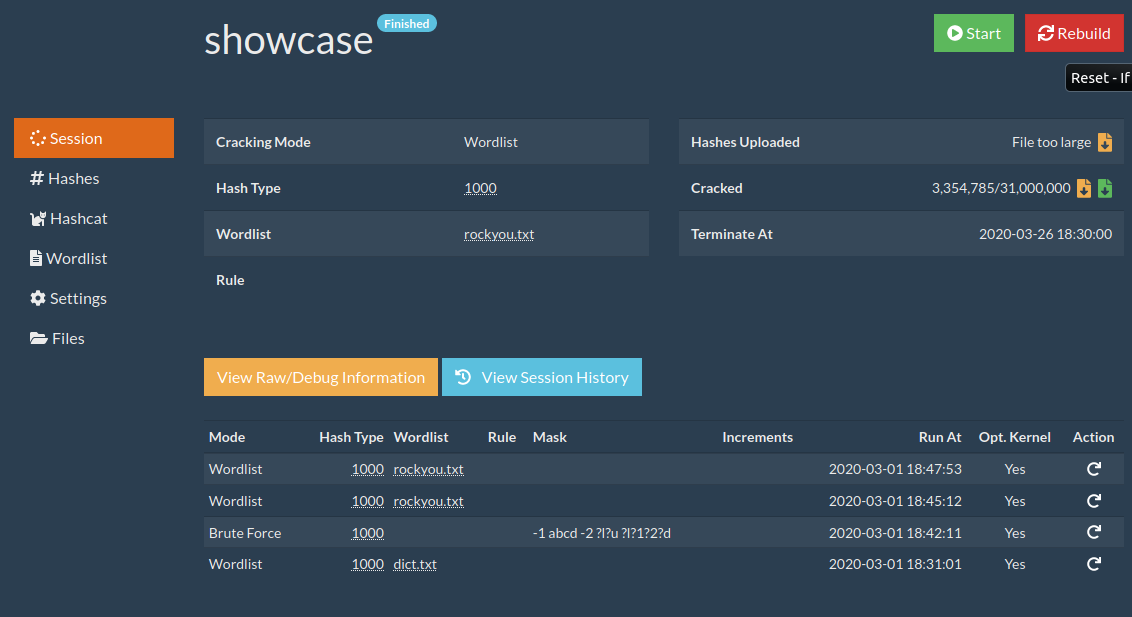 ctxis/crackerjack
CrackerJack / Hashcat Web Interface / Context Information Security
 jbaines-r7/hook
Proof of Concept for WatchGuard Authenticated Arbitrary File Read (CVE-2022-31749)
 zhairiazzeddine/exploit-cve-2023-6063-poc-vuln
Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…
 byrek/cve-2019-9053
Improved code of Daniele Scanu SQL Injection exploit
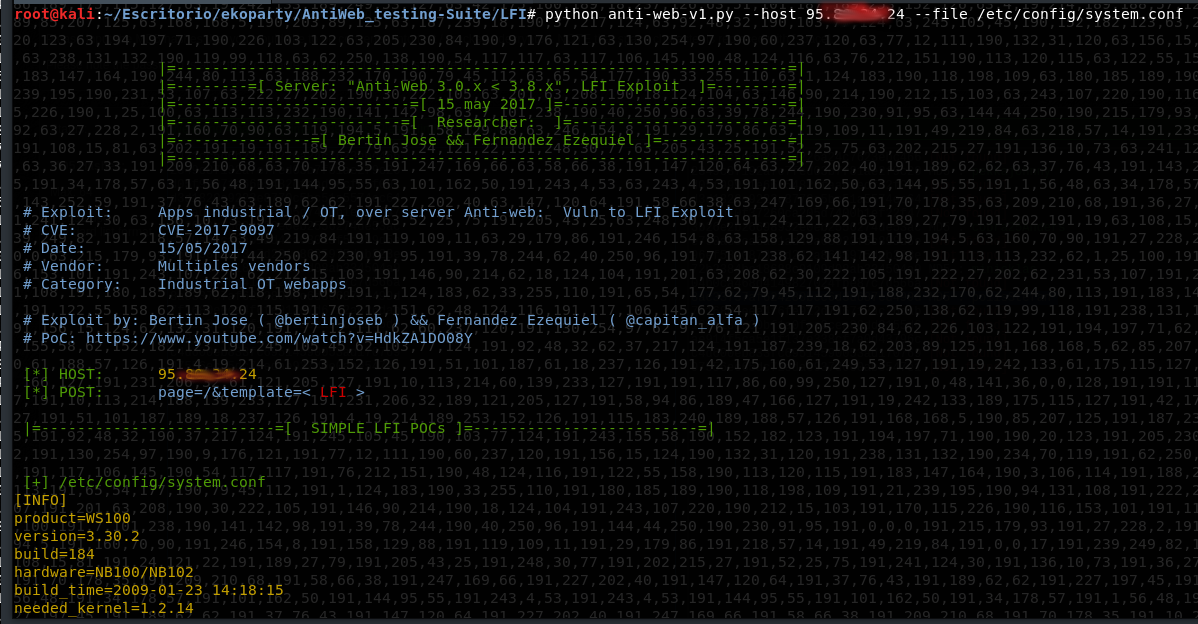 mdudek-ics/antiweb_testing-suite
Suite de herramientas que sacan partido del CVE-2017-9097 (+RCE)
 cerberusmrxi/wp-contest-gallery-28.1.4-exploit
Complete exploitation toolkit for CVE-2026-3180 - WordPress Contest Gallery SQL Injection vulnerability. Features automated data extraction, WAF…
 s3bap3/pmp-exploit
Password Manager Pro Exploit
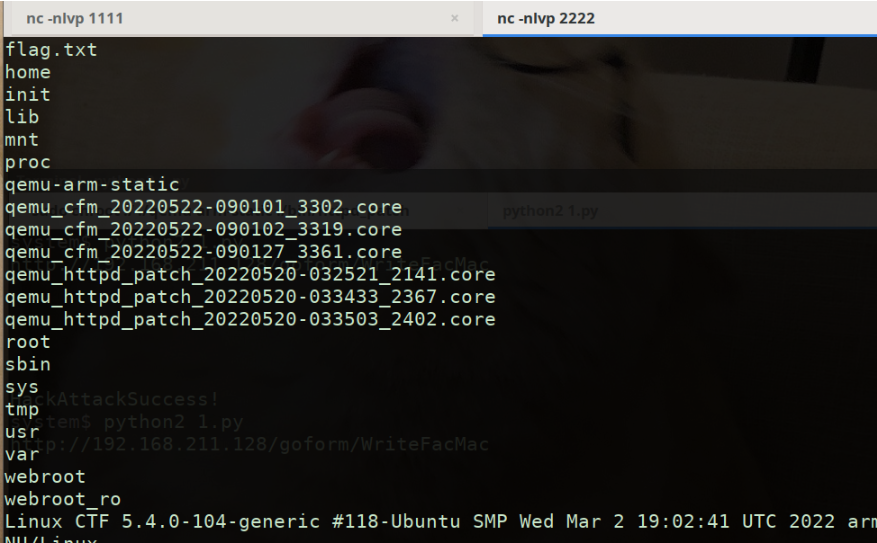 cybersecuritist/cve-2024-21754-forti-rce
Exploit for CVE-2024-21754 targeting insufficient password hashing in FortiOS and FortiProxy, enabling privileged attackers to decrypt backup files…
 fathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…
 tim-karov/cmsms-sqli
Python3 exploit for CVE-2019-9053 (CMS Made Simple <= 2.2.9 SQLi). No deps, time-based blind SQLi → admin creds dump. HTB Writeup owned.